hi
I reopened it, You can continue to leave messages.
Your current question credit has been refunded.
hi
You can try to remove the app.UseDynamicClaims from the ASP NET Core pipeline.
https://docs.abp.io/en/abp/latest/Dynamic-Claims
[auth-server_9fe7f5b1-5]: [21:50:00 ERR] ---------- RemoteServiceErrorInfo ----------
[auth-server_9fe7f5b1-5]: {
[auth-server_9fe7f5b1-5]: "code": null,
[auth-server_9fe7f5b1-5]: "message": "An internal error occurred during your request!",
[auth-server_9fe7f5b1-5]: "details": null,
[auth-server_9fe7f5b1-5]: "data": {},
[auth-server_9fe7f5b1-5]: "validationErrors": null
[auth-server_9fe7f5b1-5]: }
[auth-server_9fe7f5b1-5]:
[auth-server_9fe7f5b1-5]: [21:50:00 ERR] Nullable object must have a value.
[auth-server_9fe7f5b1-5]: System.InvalidOperationException: Nullable object must have a value.
[auth-server_9fe7f5b1-5]: at System.Nullable`1.get_Value()
[auth-server_9fe7f5b1-5]: at Volo.Abp.Users.CurrentUserExtensions.GetId(ICurrentUser currentUser)
[auth-server_9fe7f5b1-5]: at Volo.Abp.Account.DynamicClaimsAppService.RefreshAsync()```
hi
Problem is that when a token expire abp redirect me to login page. How can i remove/override that abp behavior?
I think the behavior comes from: https://github.com/abpframework/abp/blob/dev/npm/ng-packs/packages/oauth/src/lib/strategies/auth-flow-strategy.ts#L76-L78
devpayoff:
I used: builder.SetAccessTokenLifetime(TimeSpan.FromMinutes(20)); for making the token expire after 20 minutes.

In angular i subscribed to the token refresh expiration event so when the token expire a modal appear this.oAuthService.events .pipe(filter(event => event.type === 'token_refresh_error')) .subscribe(() => { this.modalVisible = true; });

Problem is that when a token expire abp redirect me to login page. How can i remove/override that abp behavior?
hi
Which page source code and js files do you need?
Your question credit has been refunded.
hi
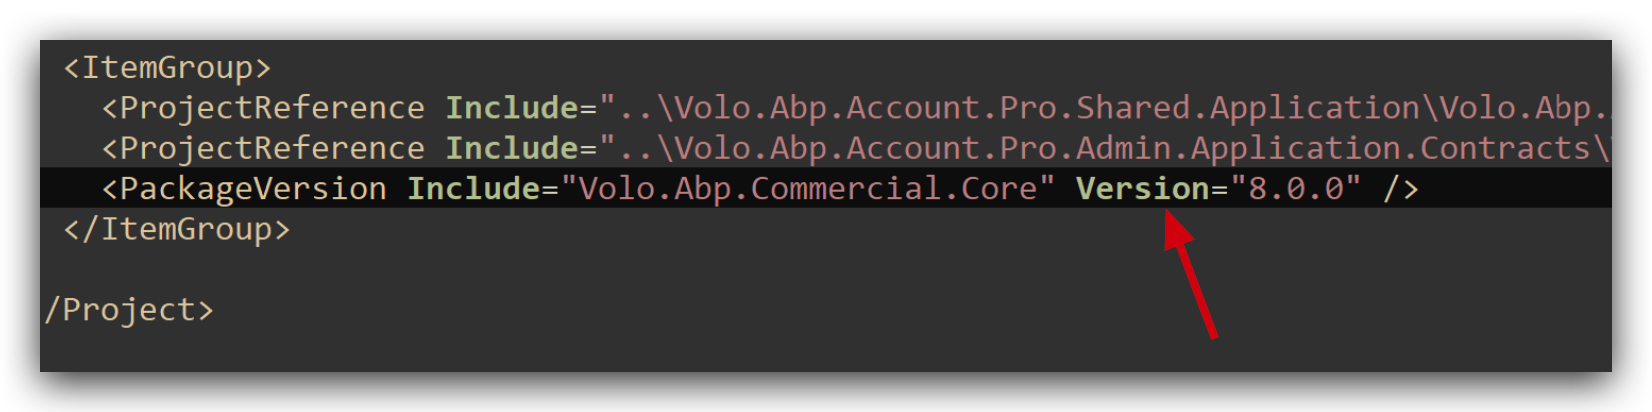
We fixed this in 8.0.1
You can use VersionOverride to replace the Version.
https://github.com/abpframework/abp/pull/18566
hi
There is an angular method to clear the login state.
https://github.com/abpframework/abp/blob/dev/npm/ng-packs/packages/oauth/src/lib/utils/clear-o-auth-storage.ts#L4
hi
When I try it on my local, everything works fine but it does not work for the docker containers.
Is the running environment of your docker application Development?
If so, please Configure the DataProtection to use same keys.
private void ConfigureDataProtection(
    ServiceConfigurationContext context,
    IConfiguration configuration,
    IWebHostEnvironment hostingEnvironment)
{
    var dataProtectionBuilder = context.Services.AddDataProtection().SetApplicationName("MyProjectName");
    //if (!hostingEnvironment.IsDevelopment())
    var redis = ConnectionMultiplexer.Connect(configuration["Redis:Configuration"]!);
    dataProtectionBuilder.PersistKeysToStackExchangeRedis(redis, "MyProjectName-Protection-Keys");
}
hi
Can you share the full logs? liming.ma@volosoft.com
Have you tested this case in a new microservice template project?




