- ABP Framework version: V5.0 commercial
- UI type: Angular
- DB provider: EF Core
- Tiered (MVC) or Identity Server Separated (Angular): yes
I publish the three sites on IIS Identity Server Host: https://mabuhamad.mowe.gov.sa:12345/ API Host: https://mabuhamad.mowe.gov.sa:12346/swagger/index.html Angular Host: https://mabuhamad.mowe.gov.sa:4400/ everything working ok
but I want to publish the three sites on IIS on port 443 with a subdirectory Identity Server Host: https://mabuhamad.mowe.gov.sa/NaamaIdentityServer API Host: https://mabuhamad.mowe.gov.sa/NaamaAPI Angular Host: https://mabuhamad.mowe.gov.sa/NaamaAngular after these settings, the Identity Server not working
Internal Server Error - UNAUTHORIZED_CLIENT invalid issuer in discovery document expected: https://mabuhamad.mowe.gov.sa/NaamaIdentityServer current: https://mabuhamad.mowe.gov.sa/naamaidentityserver
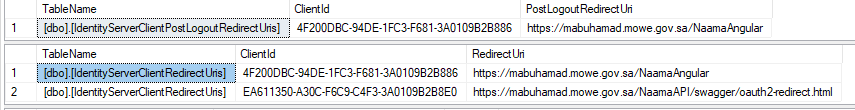
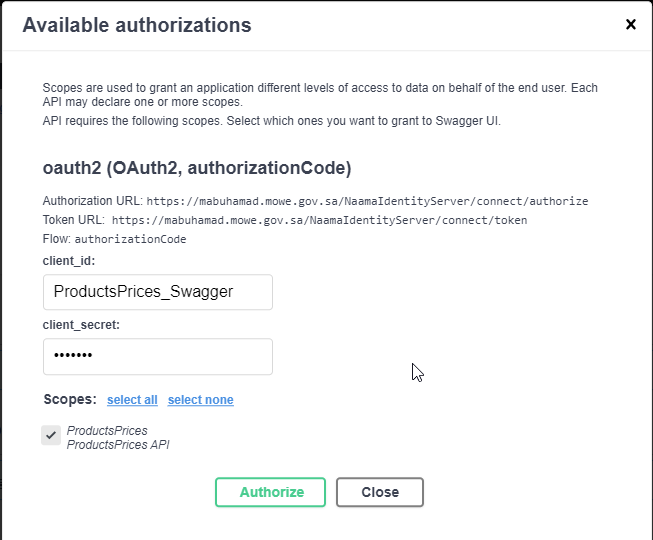
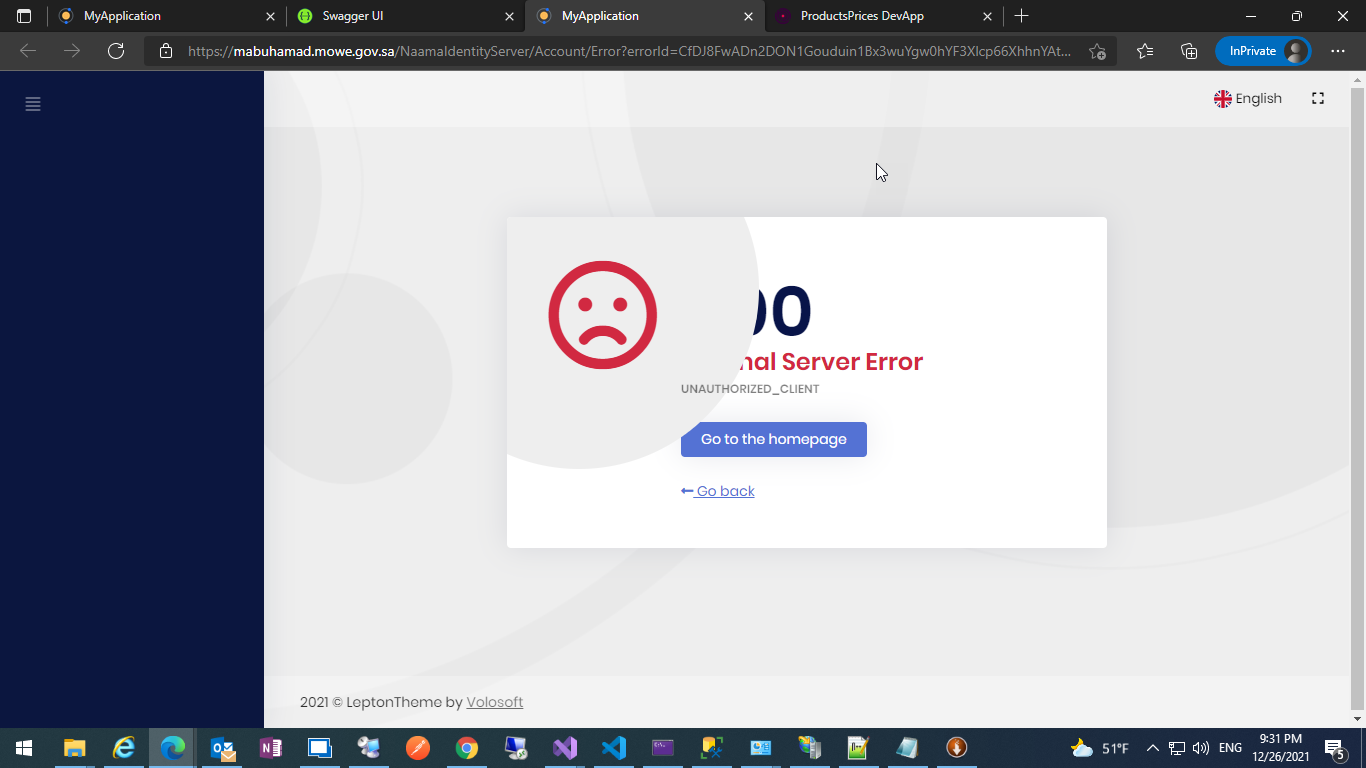
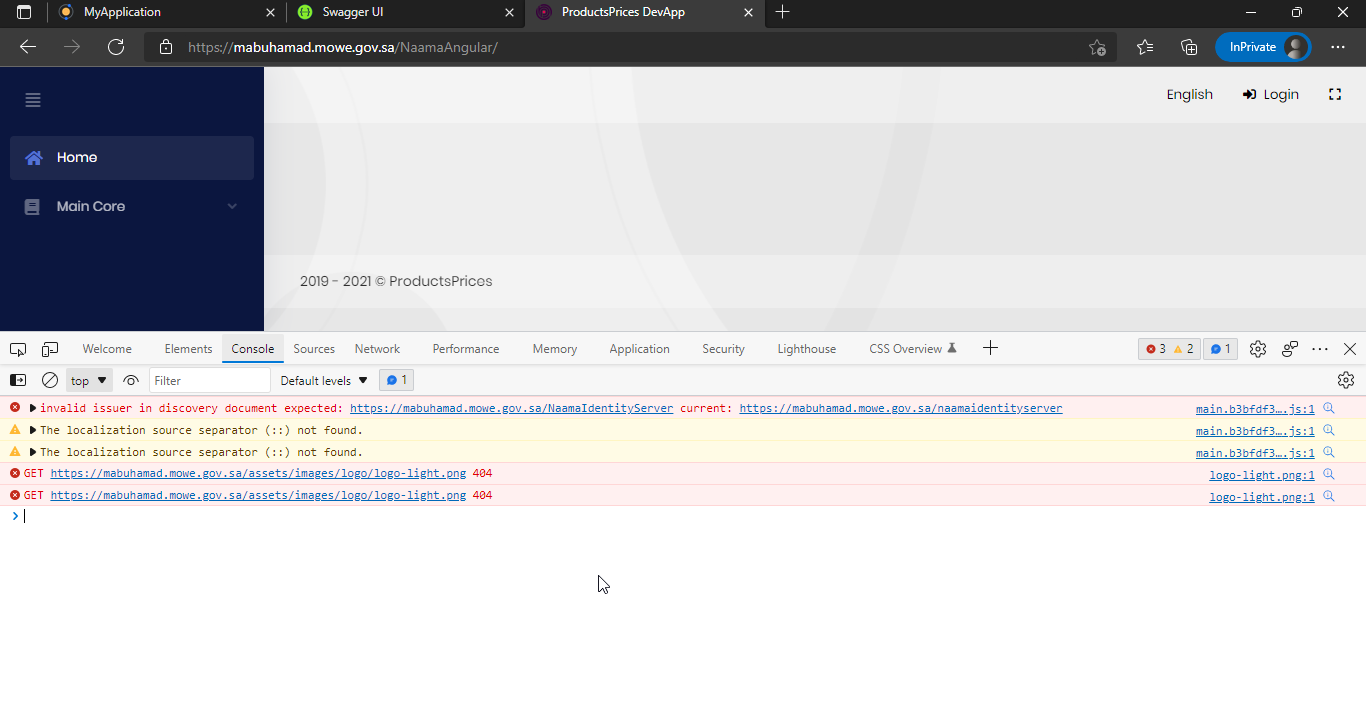
and some resources not found 404
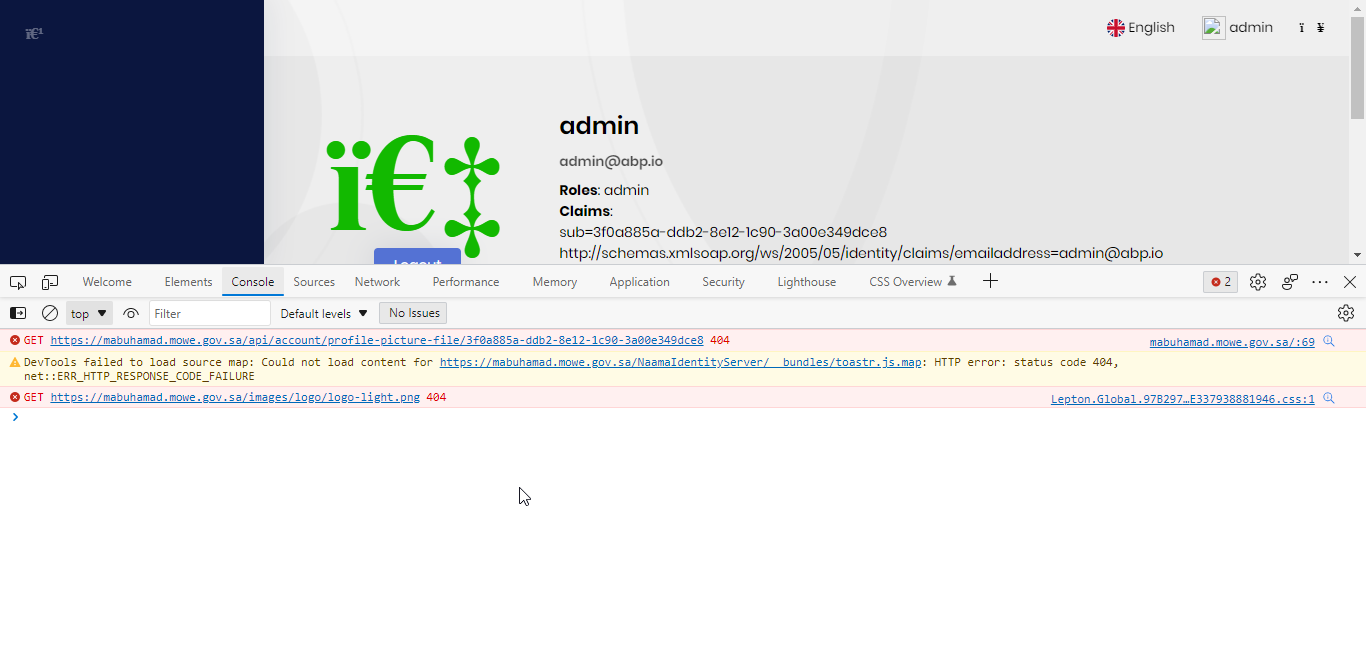
22 Answer(s)
-
0
hi
but I want to publish the three sites on IIS on port 443 with a subdirectory
You should update your url in
appsettingsand re-seed it to databaseMarkdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi,
I updated all URLs in appsettings, you can show images in above
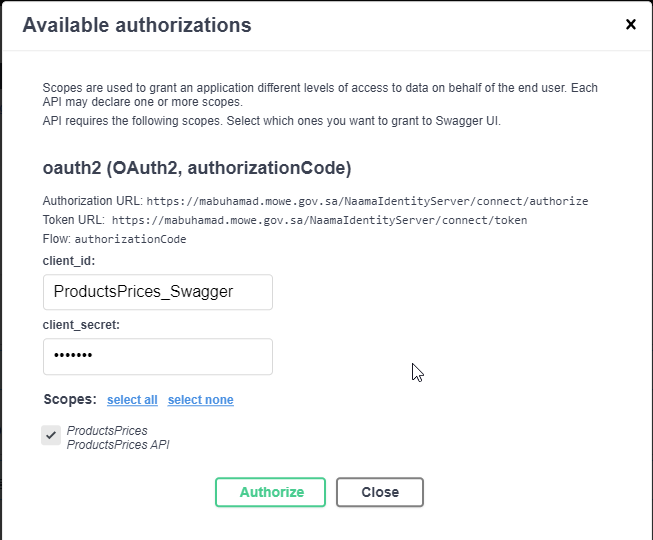 for test
{
  "App": {
    "SelfUrl": "https://mabuhamad.mowe.gov.sa/naamaidentityserver/",
	"CorsOrigins": "https://mabuhamad.mowe.gov.sa/naamaangular,https://mabuhamad.mowe.gov.sa/naamaapi"
  },
  "AppSelfUrl": "https://mabuhamad.mowe.gov.sa/naamaidentityserver/",
  "ConnectionStrings": {
    "Default": "Server=localhost;Database=NaamaMainUnder443;User Id=sa;Password=P@ssw0rd"
  },
  "Redis": {
    "Configuration": "127.0.0.1",
    "IsEnabled": false
  },
  "AuthServer": {
    "Authority": "https://mabuhamad.mowe.gov.sa/naamaidentityserver/",
    "RequirehttpMetadata": "false",
    "ApiName": "ProductsPrices"
  },
  "IdentityServer": {
    "Clients": {
      "ProductsPrices_App": {
        "ClientId": "ProductsPrices_App",
        "ClientSecret": "1q2w3e*",
        "RootUrl": "https://mabuhamad.mowe.gov.sa/naamaangular"
      },
      "ProductsPrices_Swagger": {
        "ClientId": "ProductsPrices_Swagger",
        "ClientSecret": "1q2w3e*",
        "RootUrl": "https://mabuhamad.mowe.gov.sa/naamaapi"
      }
    }
  }
}


{
  "App": {
    "CorsOrigins": "https://mabuhamad.mowe.gov.sa/naamaangular,https://mabuhamad.mowe.gov.sa/naamaidentityserver"
  },
  "ConnectionStrings": {
    "Default": "Server=localhost;Database=NaamaMainUnder443;;User Id=sa;Password=P@ssw0rd",
    "ProductsPrices": "Server=localhost;Database=ProductsPrices_Module;;User Id=sa;Password=P@ssw0rd",
    "MainCore": "Server=localhost;Database=MainCore_Module;;User Id=sa;Password=P@ssw0rd"
  },
  "Redis": {
    "Configuration": "127.0.0.1",
    "IsEnabled": false
  },
  "AuthServer": {
    "Authority": "https://mabuhamad.mowe.gov.sa/naamaidentityserver/",
    "RequirehttpMetadata": "false",
    "SwaggerClientId": "ProductsPrices_Swagger",
    "SwaggerClientSecret": "1q2w3e*"
  }
}
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
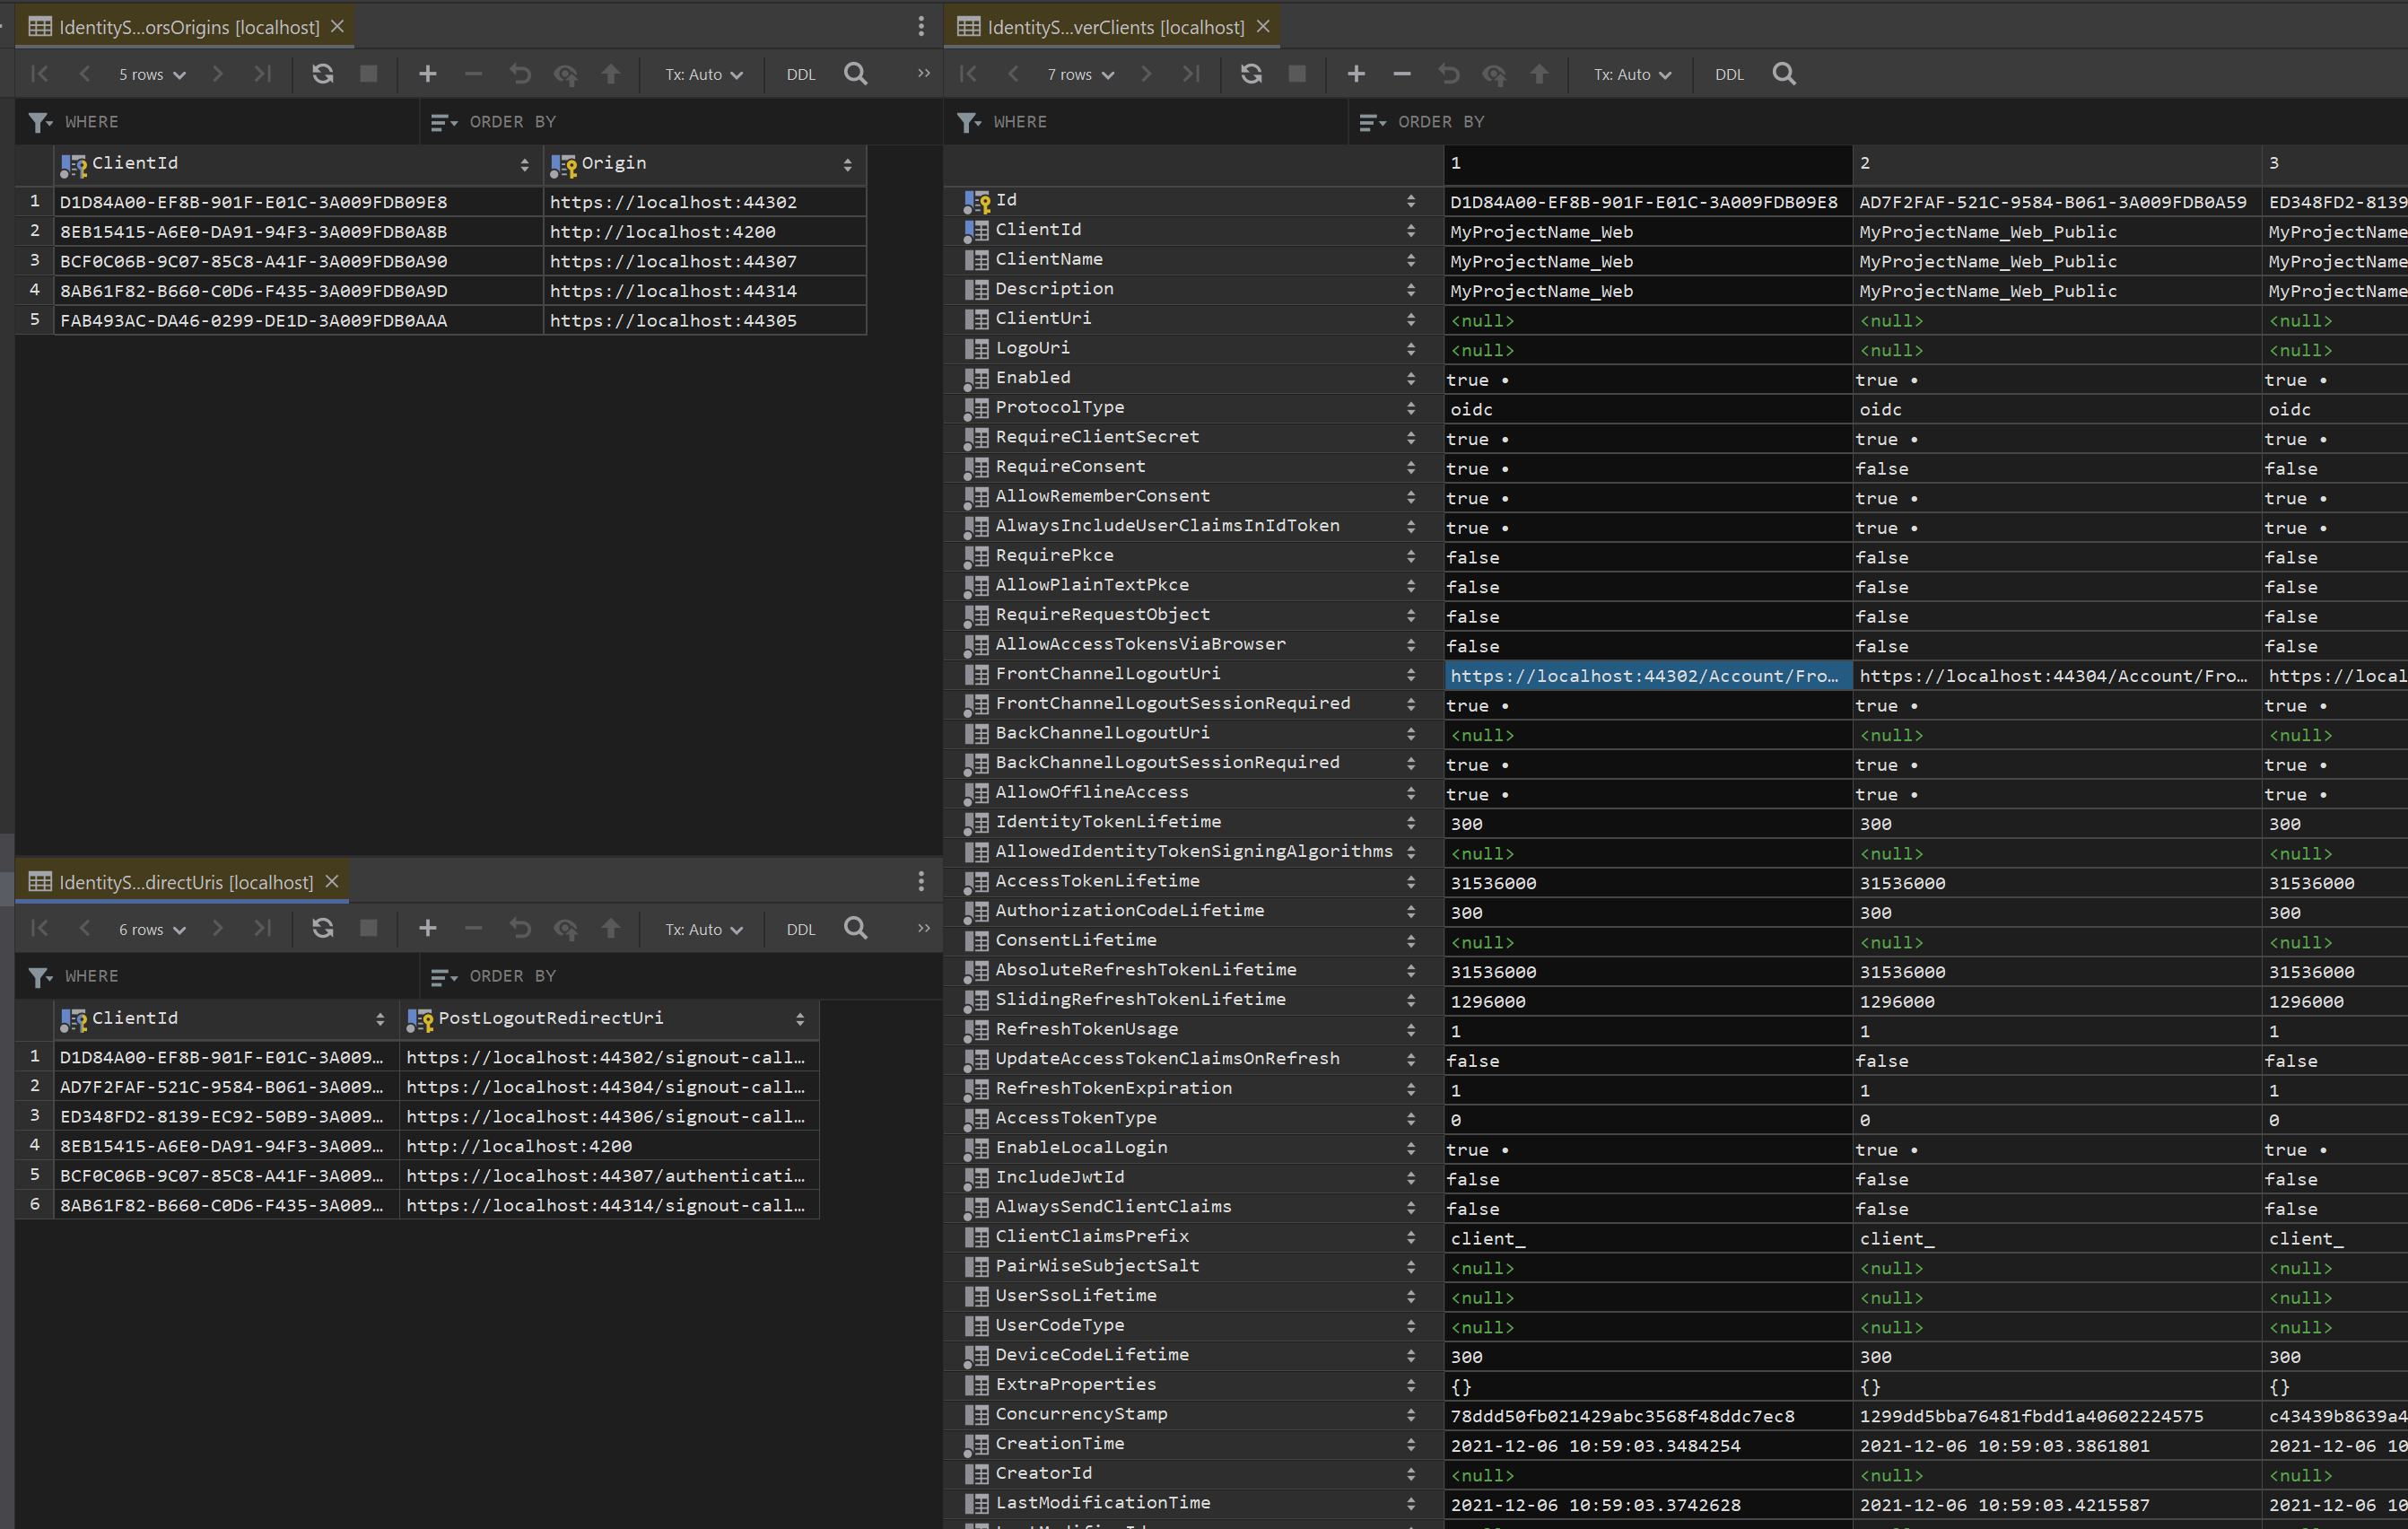
hi, i used angular project, I think FrontChannelUri and BackChannelUri are not used with angular and API, it's only used in web mvc
Kindly please review DB and appsettings :
DB and appsettings : https://app.box.com/s/xj9g2ai2r07tok54sq1l2qscg5vg1hqy
and you can try these on local iis
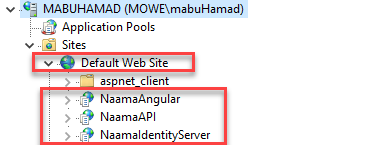 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)
-
0
Hi Logs : https://app.box.com/s/xj9g2ai2r07tok54sq1l2qscg5vg1hqy
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Kindly any update
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
AllowedCorsOrigins contains invalid origin: https://mabuhamad.mowe.gov.sa/naamaapi
Can you try to update the URL in
AllowedCorsOrigins?https://mabuhamad.mowe.gov.sa/naamaapitohttps://mabuhamad.mowe.gov.sa2021-12-28 16:52:44.346 +03:00 [ERR] Invalid client configuration for client ProductsPrices_Swagger: AllowedCorsOrigins contains invalid origin: https://mabuhamad.mowe.gov.sa/naamaapi 2021-12-28 16:52:44.354 +03:00 [INF] {"ClientId":"ProductsPrices_Swagger","ClientName":"ProductsPrices_Swagger","Category":"Error","Name":"Invalid Client Configuration","EventType":"Error","Id":3001,"Message":"AllowedCorsOrigins contains invalid origin: https://mabuhamad.mowe.gov.sa/naamaapi","ActivityId":"80000249-0006-fb00-b63f-84710c7967bb","TimeStamp":"2021-12-28T13:52:44.0000000Z","ProcessId":36476,"LocalIpAddress":"10.210.28.124:443","RemoteIpAddress":"10.210.28.124","$type":"InvalidClientConfigurationEvent"} 2021-12-28 16:52:44.364 +03:00 [ERR] Unknown client or not enabled: ProductsPrices_Swagger {"ClientId":null,"ClientName":null,"RedirectUri":null,"AllowedRedirectUris":null,"SubjectId":"anonymous","ResponseType":null,"ResponseMode":null,"GrantType":null,"RequestedScopes":"","State":null,"UiLocales":null,"Nonce":null,"AuthenticationContextReferenceClasses":null,"DisplayMode":null,"PromptMode":"","MaxAge":null,"LoginHint":null,"SessionId":null,"Raw":{"response_type":"code","client_id":"ProductsPrices_Swagger","redirect_uri":"https://mabuhamad.mowe.gov.sa/naamaapi/swagger/oauth2-redirect.html","scope":"ProductsPrices","state":"VHVlIERlYyAyOCAyMDIxIDE2OjUyOjQ0IEdNVCswMzAwIChBcmFiaWFuIFN0YW5kYXJkIFRpbWUp"},"$type":"AuthorizeRequestValidationLog"} 2021-12-28 16:52:44.367 +03:00 [ERR] Request validation failedMarkdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi,
I Updated only in app.setting in NaamaIdentityServer and NaamaAPI "App": { "CorsOrigins": "https://mabuhamad.mowe.gov.sa" },
2021-12-30 07:49:04.233 +03:00 [ERR] Invalid client configuration for client ProductsPrices_Swagger: AllowedCorsOrigins contains invalid origin: https://mabuhamad.mowe.gov.sa/naamaapi 2021-12-30 07:49:04.238 +03:00 [INF] {"ClientId":"ProductsPrices_Swagger","ClientName":"ProductsPrices_Swagger","Category":"Error","Name":"Invalid Client Configuration","EventType":"Error","Id":3001,"Message":"AllowedCorsOrigins contains invalid origin: https://mabuhamad.mowe.gov.sa/naamaapi","ActivityId":"800004b5-0000-f100-b63f-84710c7967bb","TimeStamp":"2021-12-30T04:49:04.0000000Z","ProcessId":28292,"LocalIpAddress":"10.210.28.124:443","RemoteIpAddress":"10.210.28.124","$type":"InvalidClientConfigurationEvent"} 2021-12-30 07:49:04.245 +03:00 [ERR] Unknown client or not enabled: ProductsPrices_Swagger {"ClientId":null,"ClientName":null,"RedirectUri":null,"AllowedRedirectUris":null,"SubjectId":"anonymous","ResponseType":null,"ResponseMode":null,"GrantType":null,"RequestedScopes":"","State":null,"UiLocales":null,"Nonce":null,"AuthenticationContextReferenceClasses":null,"DisplayMode":null,"PromptMode":"","MaxAge":null,"LoginHint":null,"SessionId":null,"Raw":{"response_type":"code","client_id":"ProductsPrices_Swagger","redirect_uri":"https://localhost/NaamaAPI/swagger/oauth2-redirect.html","scope":"ProductsPrices","state":"VGh1IERlYyAzMCAyMDIxIDA3OjQ5OjA0IEdNVCswMzAwIChBcmFiaWFuIFN0YW5kYXJkIFRpbWUp"},"$type":"AuthorizeRequestValidationLog"} 2021-12-30 07:49:04.247 +03:00 [ERR] Request validation failed
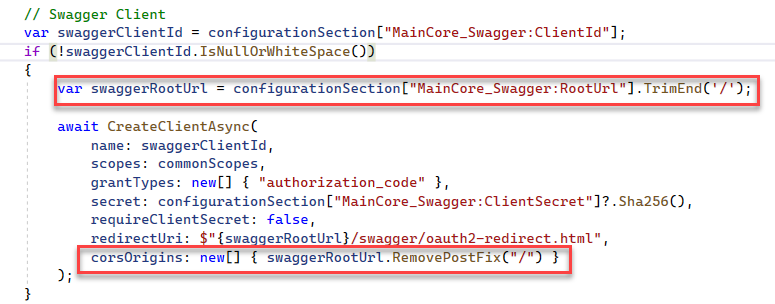 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)
-
0
https://github.com/IdentityServer/IdentityServer4/blob/main/src/IdentityServer4/src/Validation/Default/DefaultClientConfigurationValidator.cs
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi,
Identity server it's ok but show other problems.
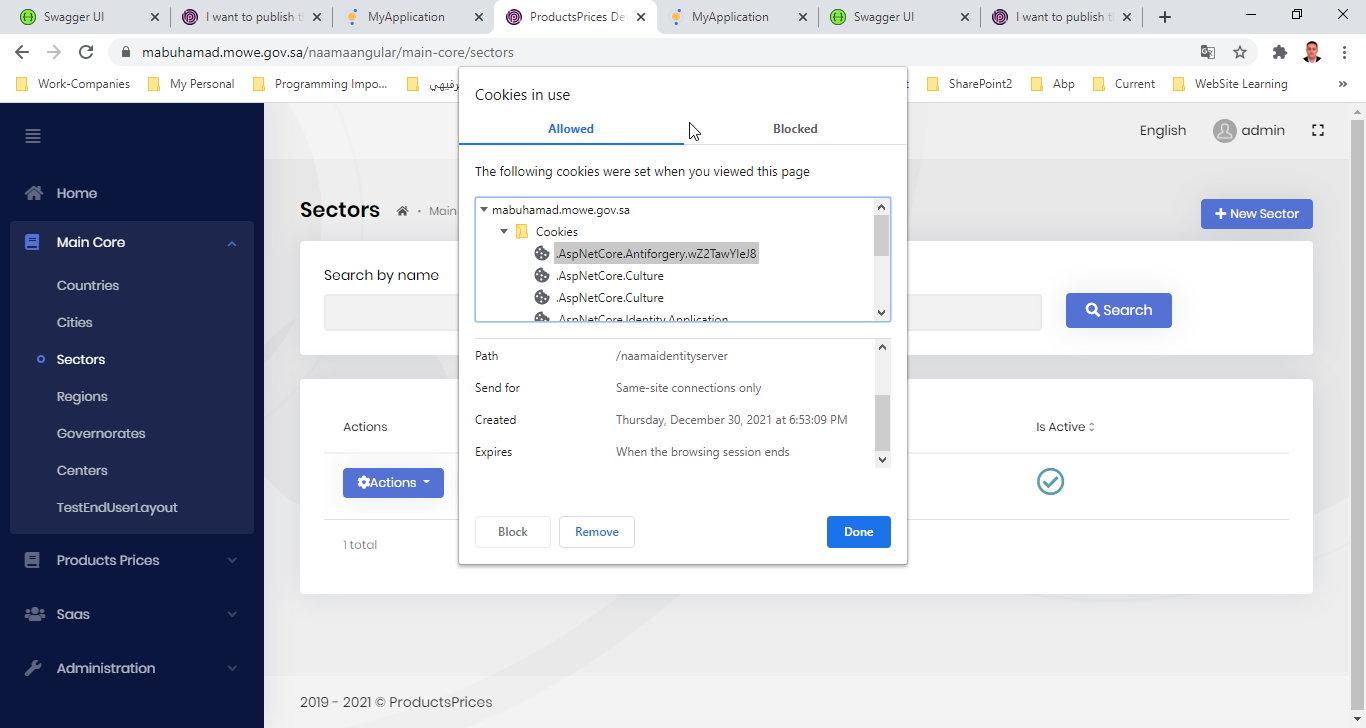
2021-12-30 20:04:20.567 +03:00 [INF] Request starting HTTP/2 POST https://mabuhamad.mowe.gov.sa/naamaapi/api/main-core/sector application/json 83 2021-12-30 20:04:20.567 +03:00 [INF] CORS policy execution successful. 2021-12-30 20:04:20.571 +03:00 [INF] Executing endpoint 'Naama.MainCore.Lookups.Sectors.SectorController.CreateAsync (Naama.MainCore.HttpApi)' 2021-12-30 20:04:20.573 +03:00 [INF] Route matched with {area = "mainCore", action = "Create", controller = "Sector", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Naama.MainCore.Lookups.Sectors.SectorDto] CreateAsync(Naama.MainCore.Lookups.Sectors.CreateUpdateSectorDto) on controller Naama.MainCore.Lookups.Sectors.SectorController (Naama.MainCore.HttpApi). 2021-12-30 20:04:20.573 +03:00 [ERR] The required antiforgery cookie ".AspNetCore.Antiforgery.wZ2TawYIeJ8" is not present. 2021-12-30 20:04:20.573 +03:00 [INF] Authorization failed for the request at filter 'Volo.Abp.AspNetCore.Mvc.AntiForgery.AbpAutoValidateAntiforgeryTokenAuthorizationFilter'. 2021-12-30 20:04:20.573 +03:00 [INF] Executing StatusCodeResult, setting HTTP status code 400 2021-12-30 20:04:20.573 +03:00 [INF] Executed action Naama.MainCore.Lookups.Sectors.SectorController.CreateAsync (Naama.MainCore.HttpApi) in 0.24
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi Kindly any update
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Hi Kindly your support
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
The cookies of these 3 websites should be isolated, and now they are sharing cookies.
Identity Server Host:     https://mabuhamad.mowe.gov.sa/NaamaIdentityServer
API Host:                 https://mabuhamad.mowe.gov.sa/NaamaAPI
Angular Host:             https://mabuhamad.mowe.gov.sa/NaamaAngular
Please configure path on the 3 websites(NaamaIdentityServer, NaamaAPI, NaamaAngular).
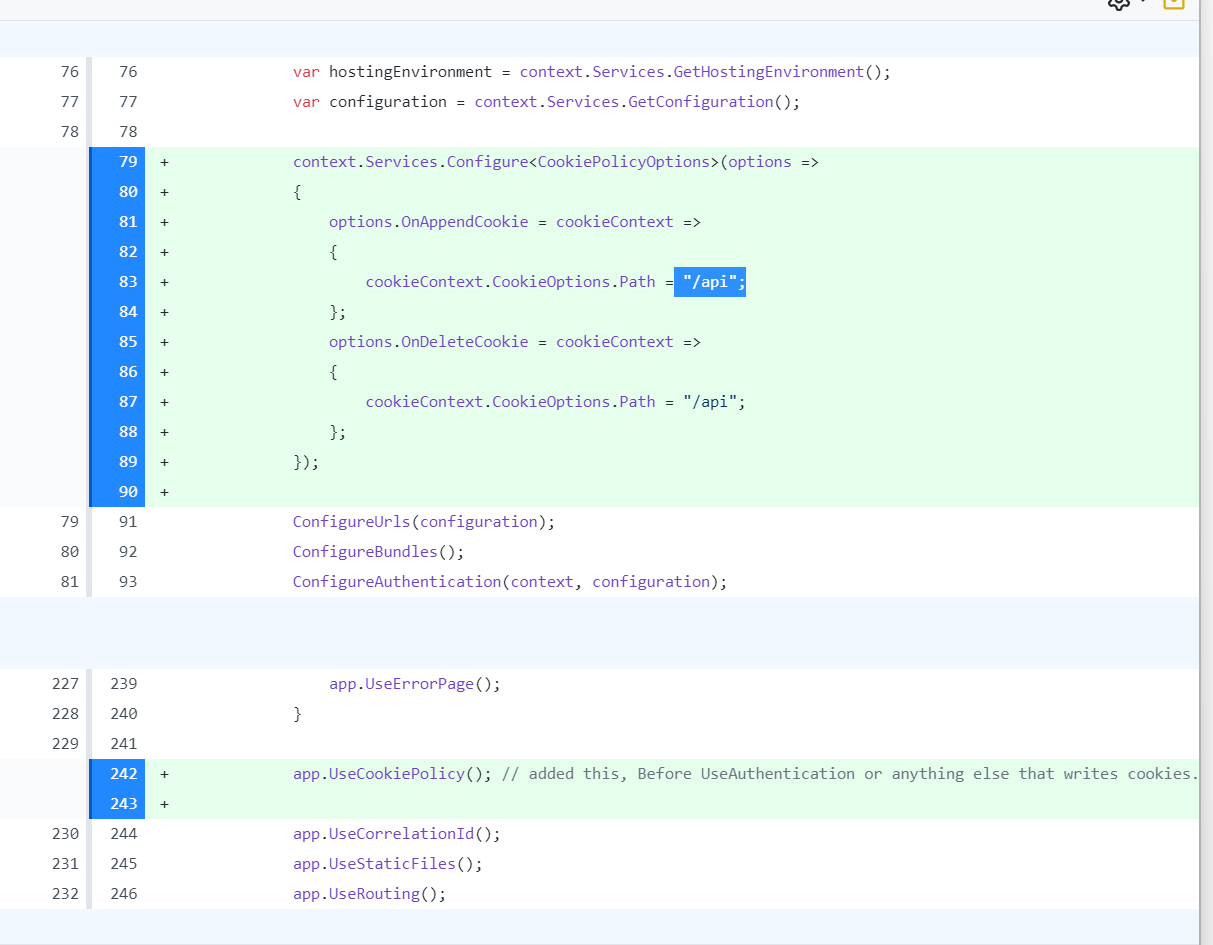 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)
-
0
Kindly, please support me with the right solution in such cases.
I want to share all cookie paths with "/" Because the cookie path is case-sensitive the cookie is not sent by the browser if the case changes. Thereby, the user is not authenticated.
I want only set names of cookies and paths like these, how to make these in ABP
services.AddAntiforgery(options =>
{
    options.Cookie.Name = "API_AntiforgeryCookie";
    options.Cookie.Path = "/";
});
services.AddAntiforgery(options => { options.Cookie.Name = "IdSrv_AntiforgeryCookie"; options.Cookie.Path = "/"; });
app.AddAuthentication()
    .AddCookie(options =>
    {
        options.Cookie.Name = "API_AuthCookie";
        options.Cookie.Path = "/";
    });
app.AddAuthentication() .AddCookie(options => { options.Cookie.Name = "IdSrv_AuthCookie"; options.Cookie.Path = "/"; });
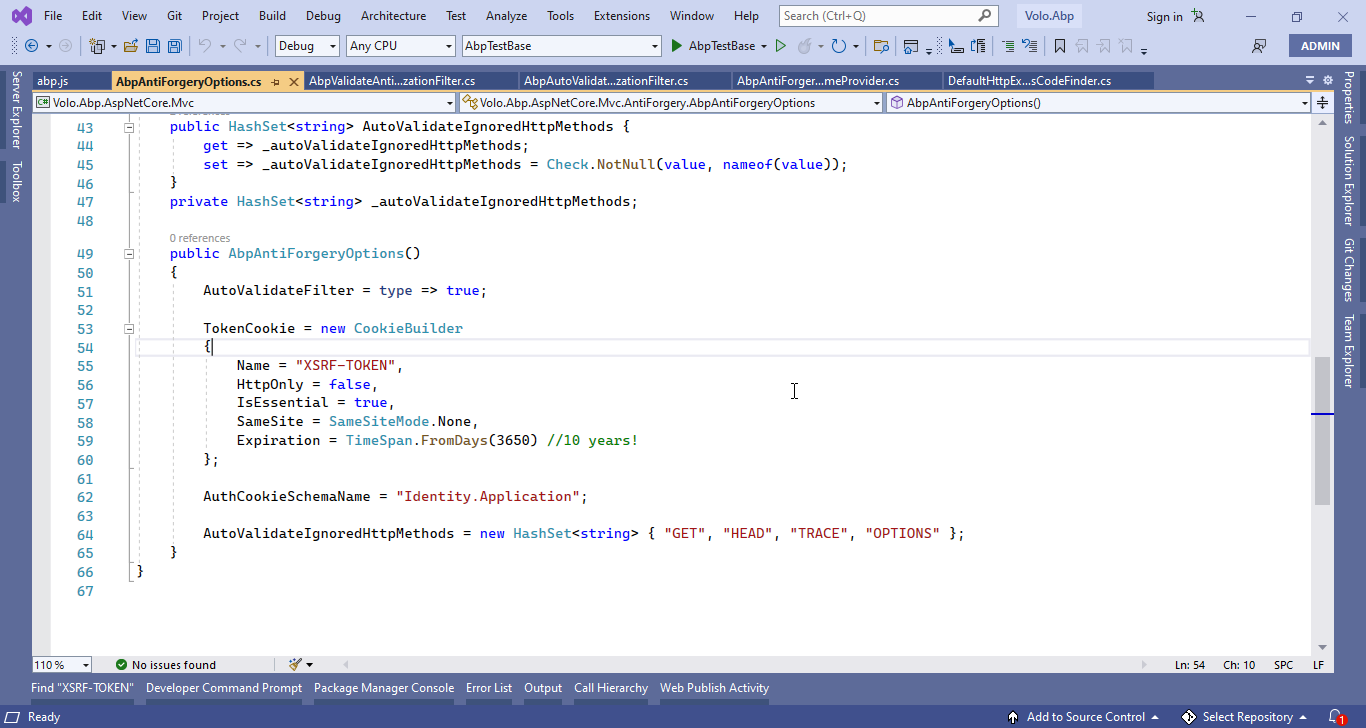
and in the ABP framework, how changed the Expiration date
- there is another problem in an angular application for the first call after authenticated from SSO, but i click for any authenticated page redirect on SSO and return on angular app to store new cookies
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) - there is another problem in an angular application for the first call after authenticated from SSO, but i click for any authenticated page redirect on SSO and return on angular app to store new cookies
-
0
Kindly, please support me with the right solution in such cases.
I try the above solution and the error anti-forgery cookie are fixed, but cookie path is case-sensitive the cookie is not sent by the browser if the case changes. Thereby, the user is not authenticated.and I Have other problem angular for first time, the angular appear as authenticated user, but actual not authenticated, and after click or any link to nagivate authenticated url, angular redirect on sso, and return to angular app after authenticated
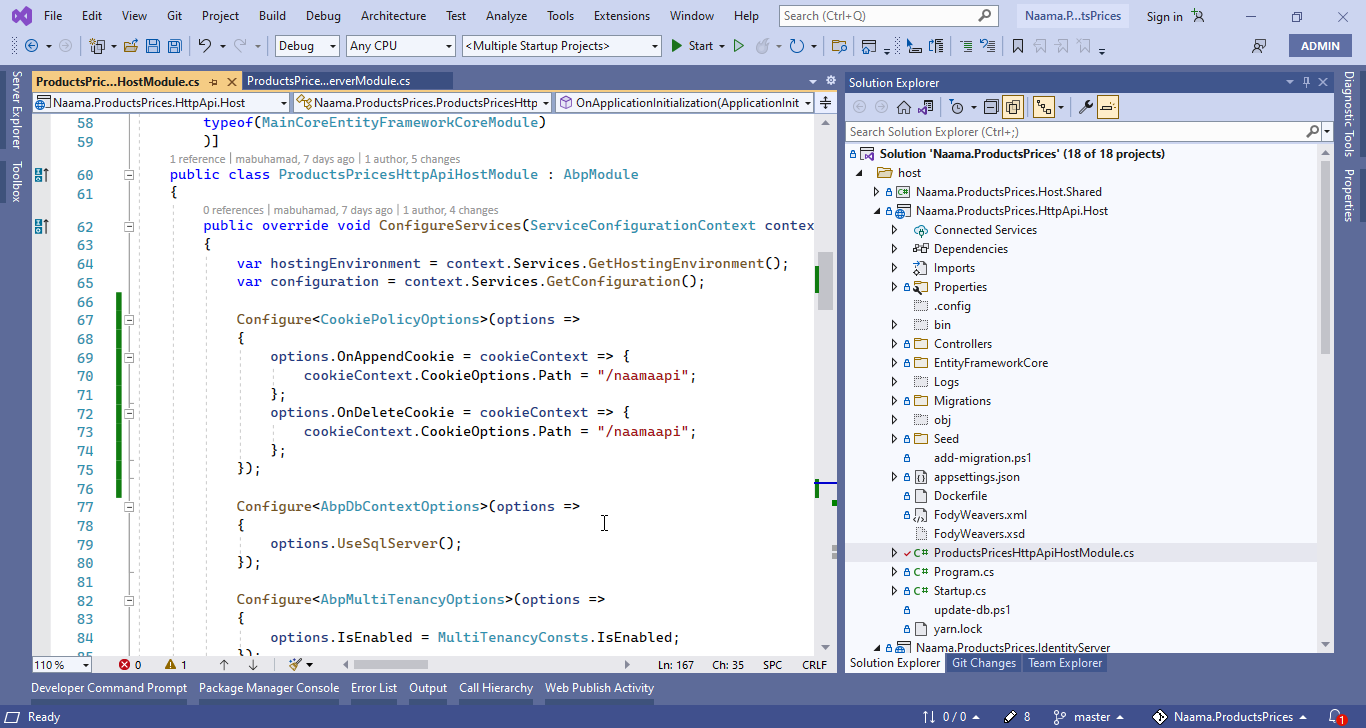
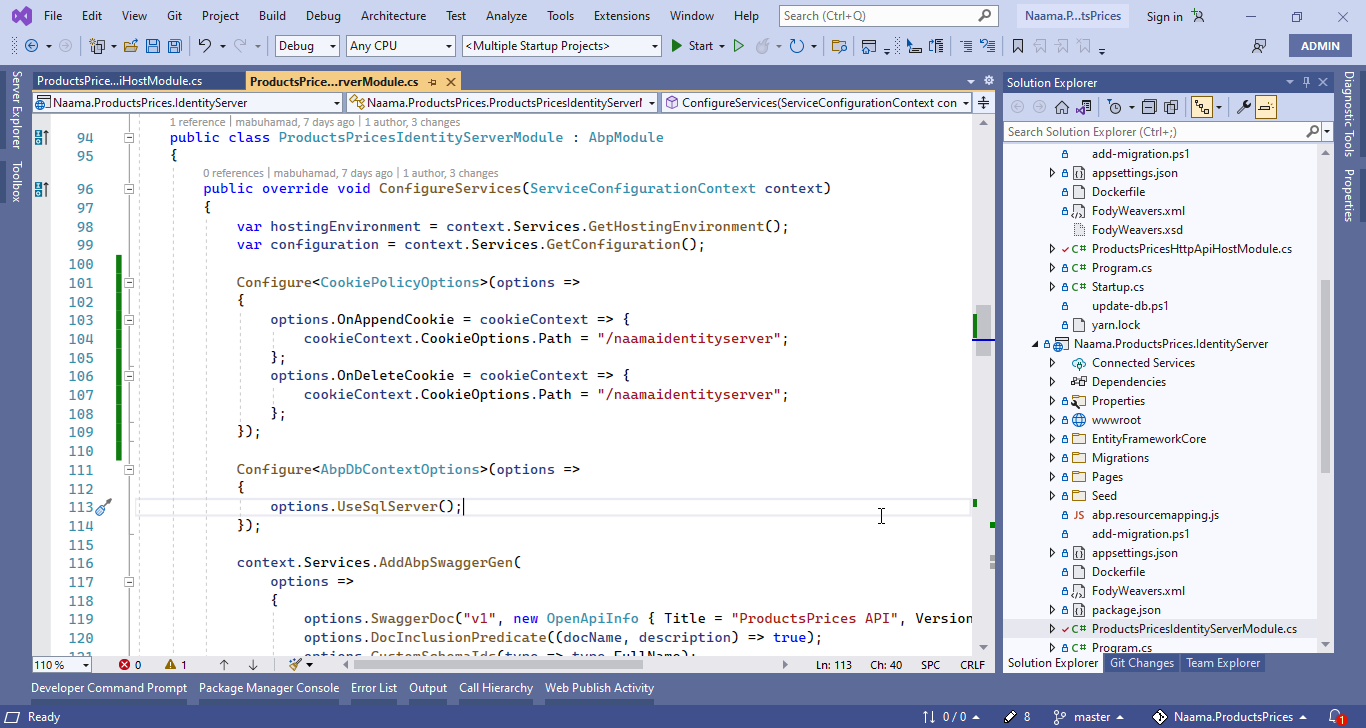
the first call angular
 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)
-
0
I try the above solution and the error anti-forgery cookie are fixed, but cookie path is case-sensitive the cookie is not sent by the browser if the case changes. Thereby, the user is not authenticated
https://stackoverflow.com/questions/59320702/case-sensitive-urls-has-to-be-exact-as-specified-in-sp-metadata?answertab=votes#tab-top
I Have other problem angular for first time, the angular appear as authenticated user, but actual not authenticated, and after click or any link to nagivate authenticated url, angular redirect on sso, and return to angular app after authenticated
Have you tried opening it in incognito mode?
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Have you tried opening it in incognito mode? incognito mode is working fine, but end-user don't open incognito mode.
if there is any way to change cookies name options.Cookie.Name = "API_AuthCookie";options.Cookie.Path = "/"; please provide me
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
incognito mode is working fine, but end-user don't open incognito mode.
You can clear the localhost or your domain cache and cookies.
options.Cookie.Name = "API_AuthCookie";options.Cookie.Path = "/";
https://docs.microsoft.com/en-us/aspnet/core/security/authentication/identity-configuration?view=aspnetcore-6.0#cookie-settings https://docs.microsoft.com/en-us/aspnet/core/security/anti-request-forgery?view=aspnetcore-6.0#configure-antiforgery-with-antiforgeryoptions https://docs.abp.io/en/abp/latest/CSRF-Anti-Forgery#configuration-customization
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
1
thanks
malimingfor support, I will try all the notes on a real server. many thanksMarkdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)