


Hello, I've separated applications in my project ,
Steps to reproduce the issue: 1-Create a user and login with his account 2-change from the administration area his status (deactivate or lock out this account ) ,but this user still can browse within his context and can do any request
How could I fix it to have instant response and stop this user immediately? Thanks in advance
Here is some information about my application
ABP Framework version: v5.1
UI type: MVC
DB provider: EF Core
5 Answer(s)
-
0
Technically speaking, if you would be using a tiered application or a SPA that uses tokens for authentication; you could delete the user tokens.
But in a non-tiered MVC application, you are basically trying to invalidate someone else's cookies. Even if you impersonate the user and sign out; it will be signed out from your browser, not his/her.
I don't think it is possible without XSS.
Or maybe I understand it wrong.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Hello , sorry for late response. I have created a new project using abp version 5.1 and create a small demo for this issue , https://jawda-my.sharepoint.com/:v:/g/personal/merna_jawda_net/EZrt105-FLpAhhg5rNKxW8gBgy0H1-oKd4RlVX9OfhImzQ?e=KFxQTK
so my problem here is very simple : I want to prevent the created user with username (merna2) from requesting any page(log him out) once the admin deactivate or delete the account. so is there anyway to apply it.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
There is a property
UserSecurityStampofIdentityUserandSecurityStampValidator.When the important properties of the user(username, email, password, etc) are changed, this value will change,
You can set
SecurityStampValidatorOptions.ValidationInterval Propertyto 3 second or other values.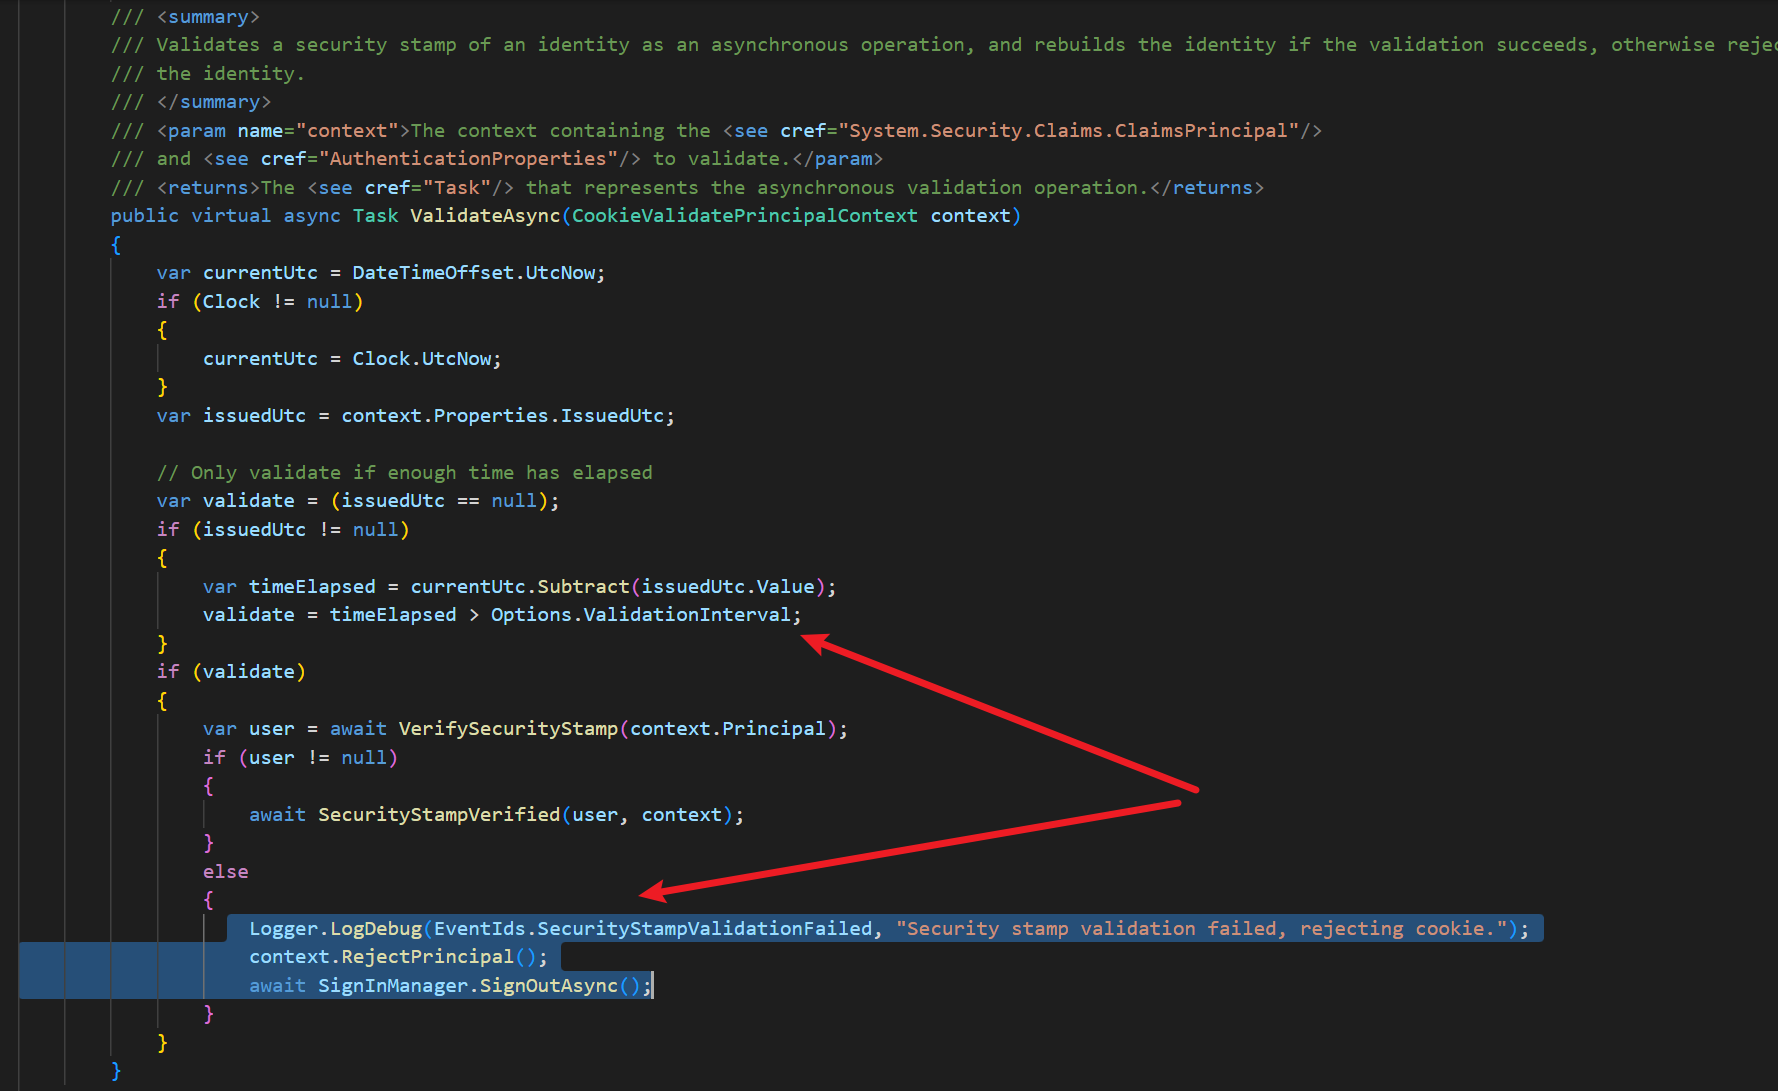 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)



