


- ABP Framework version: v8.3.2
- UI Type: Angular
- Database System: EF Core (SQL Server)
- Tiered (for MVC) or Auth Server Separated (for Angular): no
As I'm using dynamic claims, on the backend I can see that CurrentUser service is getting updated if I change the role of the current user.
on the frontend, if I call authService.refreshToken() the access token gets updated too.
but, this.config.getOne$('currentUser').subscribe((currentUser) => { } DOES NOT get reflected with the latest role for the current user.
how can I access the dynamic claim changes on the frontend for the currentuser
21 Answer(s)
-
0
Hi, I have the following method that I'm using to test the dynamic claims
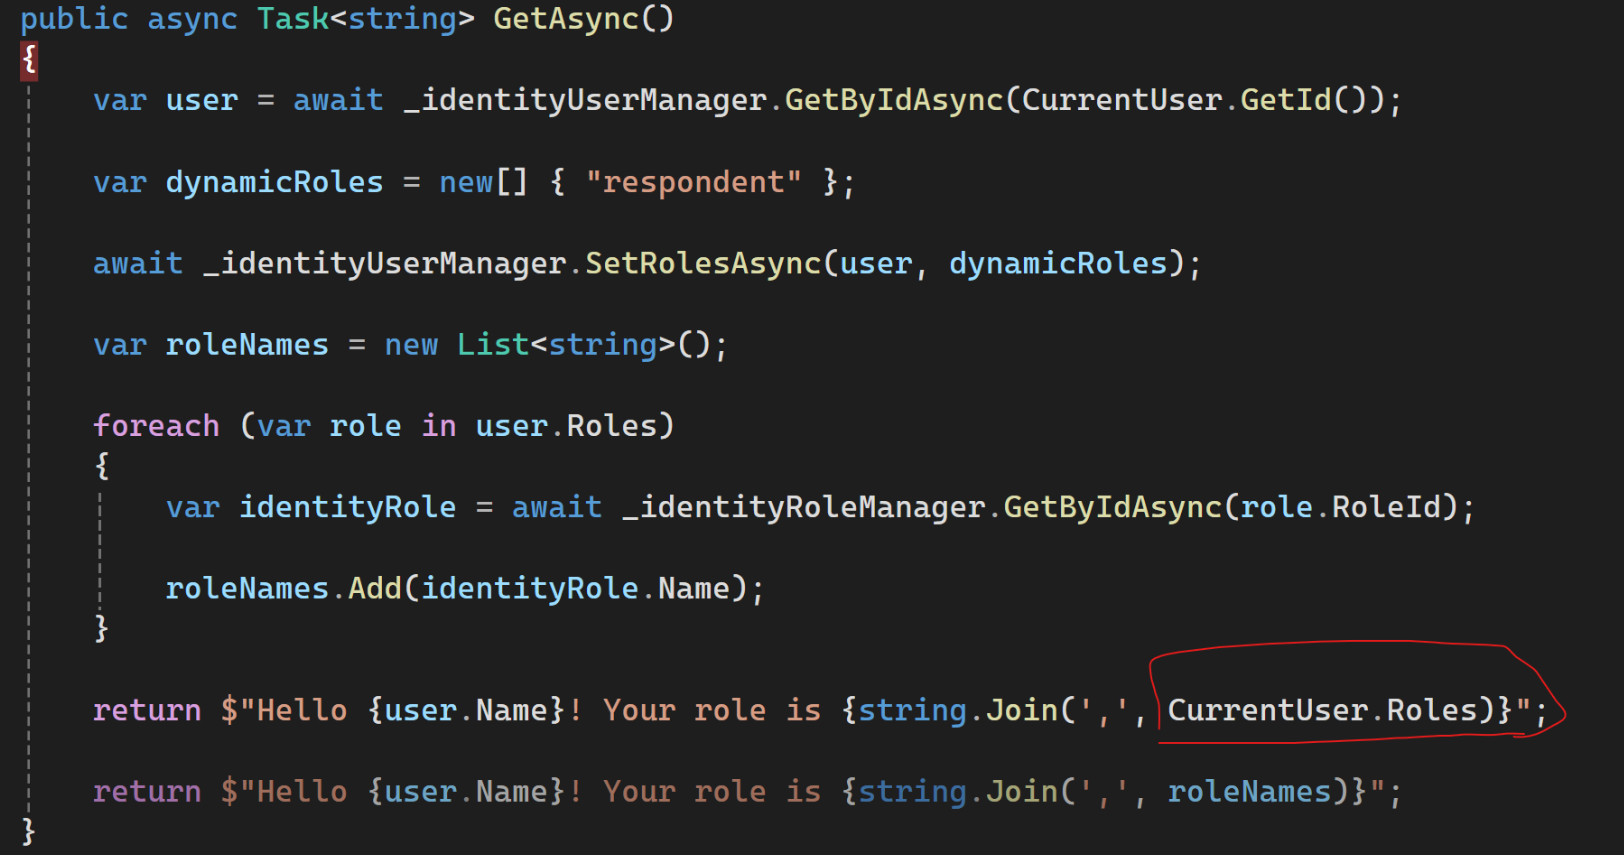
as you can see I'm changing the role of the current user on the backend.
if I return the first line with CurrentUser.Roles, it still shows old roles, (this means CurrentUser service is not updating with latest data)
but if I return the second line then it return the new roles
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
but if I return the second line then it return the new roles
Yes. This is the default behavior.
The
CurrentUservalues from HttContext.User.You can
Changing the Current Principalhttps://abp.io/docs/latest/framework/infrastructure/current-user#changing-the-current-principal
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
lets say If I don't want to change the Current Principal, but the other approach I'm taking to change the role of the user.
is it right approach or is there any better way to solve it.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi,
so far what I have understood is that. if I wanna change the role of the current user (dynamic claim) so I should stick with IdentityUserManager to change the role of the current user, but for other purpose I can use CurrentUser service to read some data about user.
because in my implementation, all I wanna do change the role of the current user based on some conditions.
am I correct ?
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
You should get the
user, user rolesfromUserManagerbased on theCurrentUser.Idvar user = await _identityUserManager.GetByIdAsync(CurrentUser.GetId());Then check the
user rolesto add your logic. For example, you could add or remove a role from theuser.if you want to return a string message. you can get it from
userentity instead ofCurrentUser.the
userentity has a higher priority than theCurrentUser.
In short, the
CurrentUseris used to get theuserentity.Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
thank you for explaining this,
from this, what I understood is that, I should always use _identityUserManager to change any dynamic claim for the current user.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Hi,
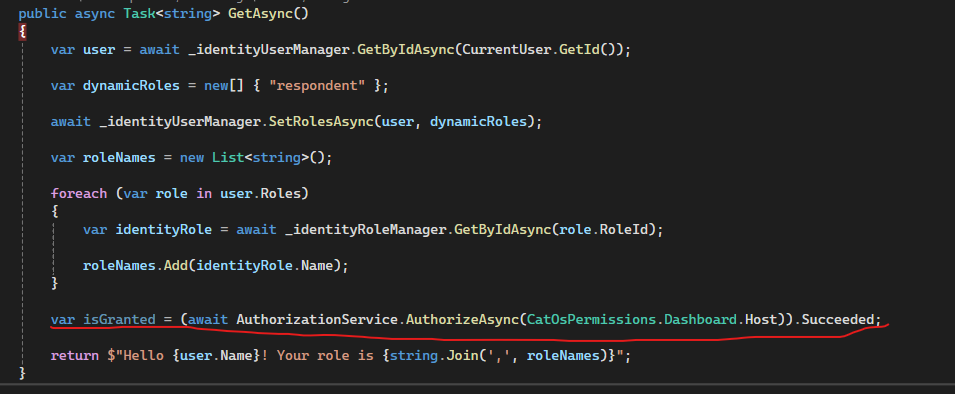
isGranted variable doesn't relfect the latest value when role is updated in this method before get to this line,
but in the next call, isGranted has the expected value and working fine.
so when role is changed, the associated permission of the role doesn't reflect in the same call.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
isGranted variable doesn't relfect the latest value when role is updated in this method before get to this line,
You can
Changing the Current Principaland then check the permission.https://abp.io/docs/latest/framework/infrastructure/current-user#changing-the-current-principal
The permission check will use the values from
CurrentUser.Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
is there any other way to check the permission without changing the current principal.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
I don't understand I'm changing the role with _IdentityUserManager for dynamic claims then I 'm changing current principal to check the permissions.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
You have changed the
userentity. but theCurrentUservalues fromHttpContext.UserThe
HttpContext.Uservalues come fromcookiesorjwt token. They are static in the current request and will update from theuserentity in the next HTTP request.That's why you have to change the
current principalMarkdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
based on the documentation you shared to change the current principal,
how can I create new Current principal with all the values of the existing principal and change only the role.
could you please give me code example based on the screenshot I shared before
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
Inject the
ICurrentPrincipalAccessorandIUserClaimsPrincipalFactory<IdentityUser>var identityUser = using (CurrentPrincipalAccessor.Change(await UserClaimsPrincipalFactory.CreateAsync(identityUser))) { }Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
just to understand, based on this screenshot
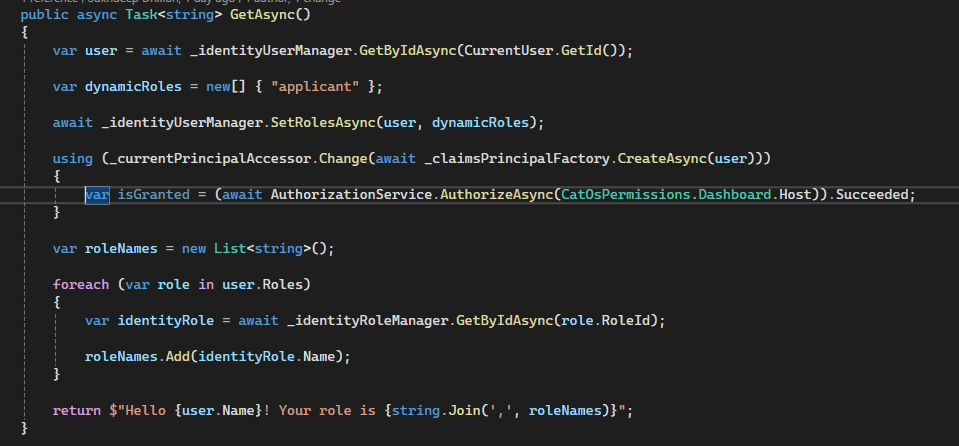
I'm doing the following:
- getting the IdentityUser from _identityUserManager
- Set new Role with _identityUserManager
- Creating new CurrentUser with _principalfactory by passing IdentityUser
- within the scope of _currentPrincipalAccessor, CurrentUser is changed (this is where I need to apply the logic)
- once the scope is completed, again the current user is back to whatever it was before
please correct me if I'm missing anything
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
thank you for helping me out.
I will keep this thread open and get back to you if I need further help.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)


