


- ABP Framework version: v8.2.1
- UI Type: Angular / MVC
- Database System: EF Core (MySQL)
- Tiered (for MVC) or Auth Server Separated (for Angular): Auth Server Separated (for Angular)
- Exception message and full stack trace:
- Steps to reproduce the issue:
- We are trying to store user info like which user has access to which all branches and each branch has what roles, ex: Branches : [{"Id":123, "Roles:['admin','user']},{"Id":113, "Roles:['subadmin','user']}] as object globally for filter purpose. Could you please suggest best way to integrate this in abp framework. storing this in access token looks incorrect as the information can have more arrays. We need to apply this filter with each db query like imultitenant filter. Filter is im clear how to implement.
20 Answer(s)
-
0
hi
We are trying to store user info like which user has access to which all branches and each branch has what roles,
Have you implemented this?
If you can get the
objectinfo you can easy to filter data based on it.https://abp.io/docs/latest/framework/infrastructure/data-filtering#defining-custom-filters https://abp.io/community/articles/switching-between-organization-units-i5tokpzt
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
We are trying to store user info like which user has access to which all branches and each branch has what roles,
Have you implemented this?
If you can get the
objectinfo you can easy to filter data based on it.https://abp.io/docs/latest/framework/infrastructure/data-filtering#defining-custom-filters https://abp.io/community/articles/switching-between-organization-units-i5tokpzt
Can i see all organization units data at once or it will be by organization unit only? Moreover i do no see organization units under newly created tenant.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
You can disable the filter to see all the data.
https://abp.io/docs/latest/framework/infrastructure/data-filtering#idatafilter-service-enable-disable-data-filters
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
You can disable the filter to see all the data.
https://abp.io/docs/latest/framework/infrastructure/data-filtering#idatafilter-service-enable-disable-data-filters
How can i maintain roles by organization units? moreover, I do not see organization unit for newly created tenant.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
You can add one or many members/roles to an organization unit
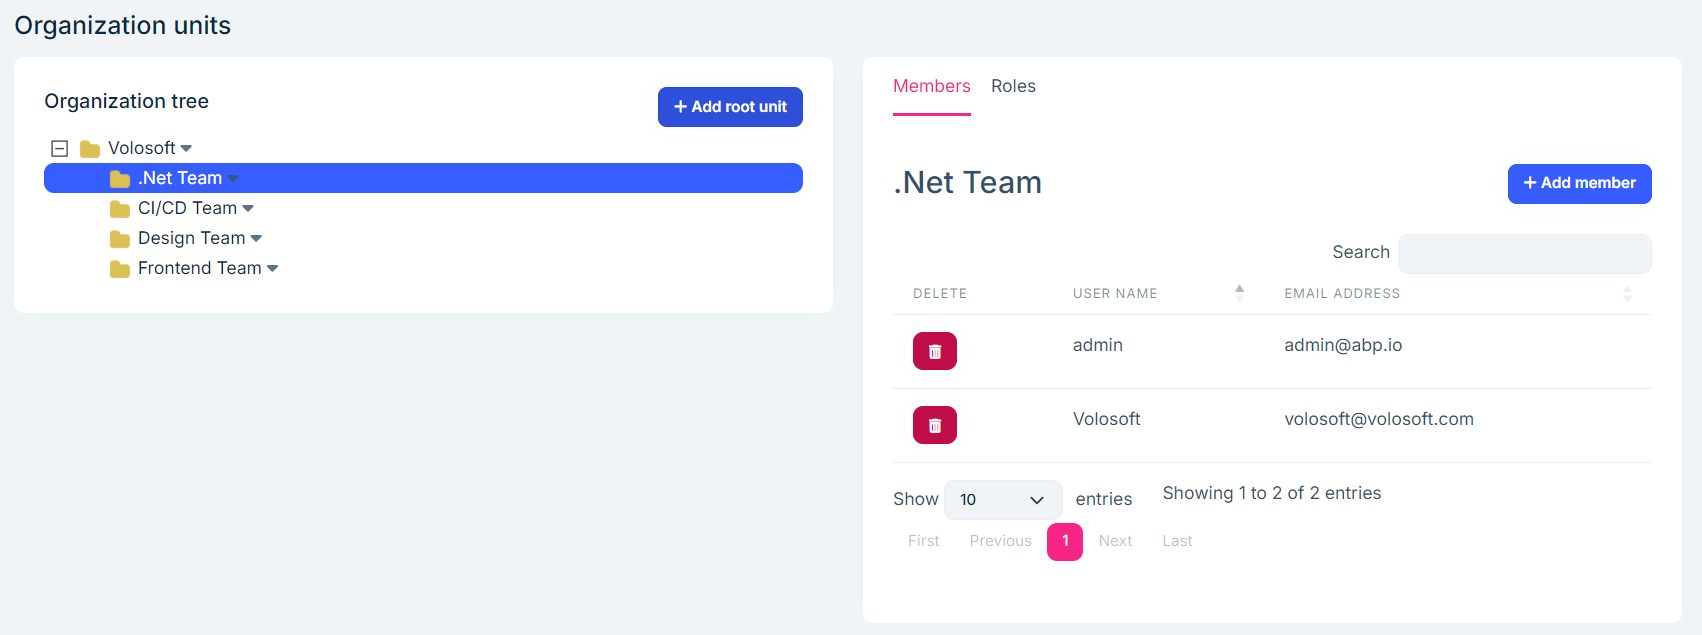
See https://abp.io/modules/Volo.Identity.Pro
I have a use case where i want to add roles by member for each organization unit and not maintain the role by organization unit. Moreover, if a member is belonging to branch USA and Turkey but USA branch has permission to view the book list but Turkey branch does not have permission to view the book list how does that scenario being handled here if i do not want to switch between the branch and display book list data at once if i disable the filter?
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
I have a use case where i want to add roles by member for each organization unit and not maintain the role by organization unit.
In this case, you can use the organization manager to add roles. which means adding code to do this. The UI doesn't have this feature
if a member is belonging to branch USA and Turkey but USA branch has permission to view the book list but Turkey branch does not have permission to view the book list how does that scenario being handled here if i do not want to switch between the branch and display book list data at once if i disable the filter?
You can check the permission first and get the branch that has permission. then switch to this branch in the code to query the data.
I get that. it becomes complicated in case i have 3 branch where in user have permission in 2 branches USA and turkey but not in the third branch let's say UK. Any suggestion to handle this?
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
- You can query three times and combine the results. get all branches of current user, switch and query.
- You can add your EF Core query instead of using datafilter.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
- You can query three times and combine the results. get all branches of current user, switch and query.
- You can add your EF Core query instead of using datafilter.
Can you suggest the best way to store the object similar to this : Branches : [{"Id":123, "Roles:['admin','user']},{"Id":113, "Roles:['subadmin','user']}]
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
You can create a new Entity/Table to store these
Branchesof a user.| Id | Roles | Foreign Key (userid) | | --- | ------------------- | -------------------- | | 1 | ['admin', 'user'] | 123123123 |
No i Was asking how to store it as cache so that we can use without db call.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
The claims are coming from jwt token. So jwt has to contain the claim.
so how the application configuration is maintained for user permissions? are those not stored as claims?
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)



