


Hello,
We are currently using an ABP framework project with ABP version 6.0, Angular UI, and have the Identity Server Separated currently in the project. According to this github issue, ABP is pivoting away from IdentityServer4 with options to either implement OpenIdDict or use an "External OAuth server (like Azure or Keycloack) instead of OpenIdDict or IDS", stated in the issue. We are looking to remove IdentityServer4 as the IDS and integrate Azure AD as our external OAuth server.
Are there guides, solutions, or examples on how previous ABP users have implemented an external OAuth server, specifically using Azure if possible?
Thanks
5 Answer(s)
-
0
hi
https://docs.abp.io/en/commercial/latest/migration-guides/openIddict-step-by-step https://docs.abp.io/en/commercial/latest/modules/identity/oauth-login https://docs.abp.io/en/commercial/latest/modules/account#social-external-logins
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Hello,
We integrated Azure AD to the ABP Angular application, allowing users to authentiate using Azure AD and the users are then added to the ABP Identity server.
We then added the Volo.Account module and noticed that when using the SignInManager, the ABP framework pulls in an access token from Azure AD and then exchanges it for an application token which is returned to Angular and stored. Is there a way for us to not exchange the application token and keep the access token from Azure AD to call others apis with the Azure AD access token?
Code below shows where the access token is acquired and exchanged in Volo.Abp.Account.Web.Pages.Account.Login.cshtml We print out the access token and it has the information we need, but we want that token stored in the frontend instead of the exchanged ABP token. Starting at line 191. https://github.com/abpframework/abp/blob/dev/modules/account/src/Volo.Abp.Account.Web/Pages/Account/Login.cshtml.cs
var loginInfo = await SignInManager.GetExternalLoginInfoAsync();
        if (loginInfo == null)
        {
            Logger.LogWarning("External login info is not available");
            return RedirectToPage("./Login");
        }

        var result = await SignInManager.ExternalLoginSignInAsync(
            loginInfo.LoginProvider,
            loginInfo.ProviderKey,
            isPersistent: false,
            bypassTwoFactor: true
        );
        Console.WriteLine("HELLO WORLD!");
        Console.WriteLine(loginInfo.AuthenticationTokens);
        foreach(var item in loginInfo.AuthenticationTokens)
        {
            Console.WriteLine(item);
            foreach (PropertyDescriptor descriptor in TypeDescriptor.GetProperties(item))
            {
                string name = descriptor.Name;
                object value = descriptor.GetValue(item);
                Console.WriteLine("{0}={1}", name, value);
            }
Thanks
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
the ABP framework pulls in an access token from Azure AD and then exchanges it for an application token which is returned to Angular and stored. Is there a way for us to not exchange the application token and keep the access token from Azure AD to call others apis with the Azure AD access token?
You can't do this, it's a designed process.
You can create a new API that returns Azure AD tokens.
//get origin azure ad tokens
httpContext.GetTokenAsync("access_token");
httpContext.GetTokenAsync("id_token");
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Hello,
Sounds good, thanks. For clarification, in the new API are you saying to make a new request to Azure to grab the tokens? Otherwise the tokens don't seem to exist in the HttpContext and need to be populated still.
Thanks.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
The azure tokens will be stored in the HttpContext after you set
SaveTokensto true, you can give it a try.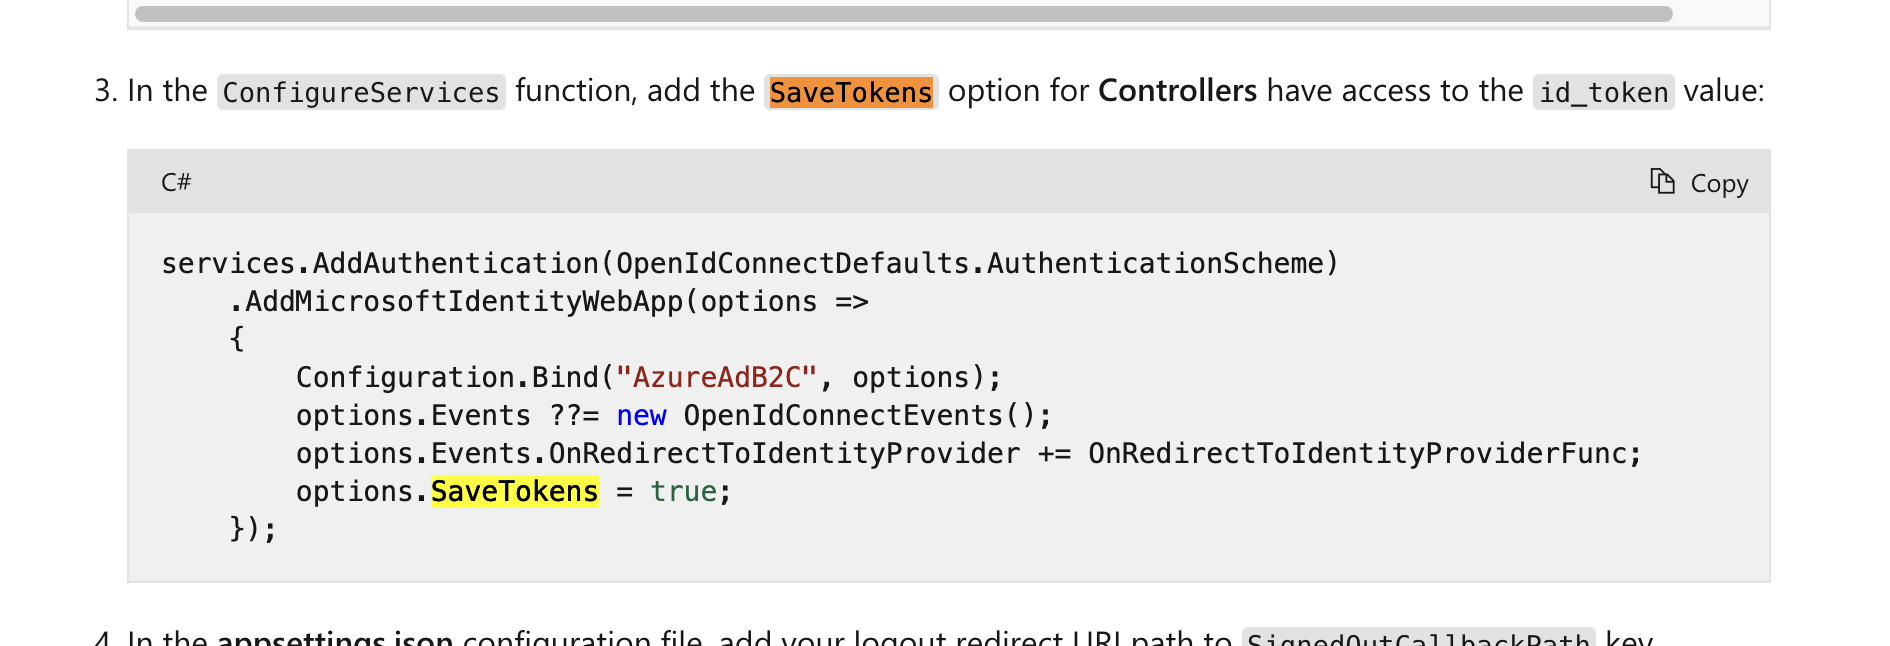
https://learn.microsoft.com/en-us/azure/active-directory-b2c/enable-authentication-web-application-options
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)


