I know that the cookie needs to be deleted, I actually deleted it but it seems to remain, anyway the problem is solved
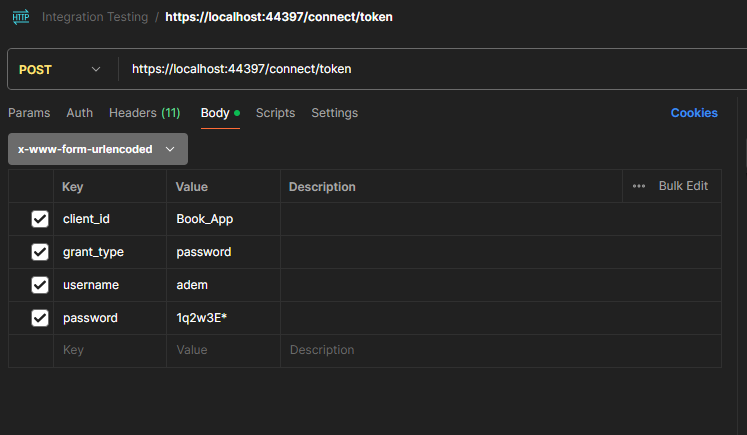
Accept: / Accept-Encoding: gzip, deflate, br Accept-Language: en Cache-Control: no-cache Connection: keep-alive Content-Length: 81 Content-Type: application/x-www-form-urlencoded Cookie: .AspNetCore.Culture=c%3Dtr%7Cuic%3Dtr; __tenant=39f7b3e6-b1a7-61af-ec9f-cc85613d2ec4 Host: localhost:44397 User-Agent: PostmanRuntime/7.40.0 Postman-Token: bb994fdb-b047-4a2f-b267-fe49fac1dbe8
HostModule:( I don't use Multitenancy)
        //if (MultiTenancyConsts.IsEnabled)
        //{
        //    app.UseMultiTenancy();
        //}
When I try to get a token from Postman, I get the error "tenant not found". But I don't use Multitenancy feature. (Cookies is cleaned)
Hi,
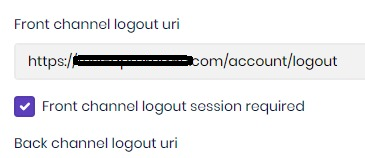
I found the solution; I set the 'Front Channel Logout URI' value to https://account.abc.com/account/logout, and my problem was resolved.
However, if I upgrade my abp project to v.6+, it seems that you don't have such a solution in your OpenID Connect configuration
Hi, We have two separate projects on the same codebase. The first project needs to work with local login, while the second one needs to use external provider. Therefore, we need two identity servers. Currently, when we log out from the Angular UI (authorization code flow), it logouts from our project, but not from the external provider.
hi, Do you have any other suggestions?
hi, If https://test-ffe-api.xxx.com has logged out, I tried to manually invoke the connect/endsession endpoint with the code below, but couldn't succeed. I think I need to call the connect/endSession endpoint with a similar code?
options.Events = new OpenIdConnectEvents // required for single sign out
                {
                    OnRedirectToIdentityProviderForSignOut = async (context) => { var client = new HttpClient(); await client.GetAsync($"{configuration["ExternalProvider:Authority"]}/connect/endsession?id_token_hint={await context.HttpContext.GetTokenAsync("id_token")}&post_logout_redirect_uri={configuration["Abp:SelfUrl"]}"); }
                };
Hi, It's a business (product owner) decision
Hi Maliming, steps:
I have an abp project consisting of the addresses https://online.abc.com (angular) and https://online-api.abc.com. Additionally, I have another abp project using https://account.abc.com as an external login. In other words, when a user wants to log in, they are redirected to https://account.abc.com and log in successfully. However, when they log out, the call to https://online-api.abc.com/connect/endsession is made for logout. Despite wanting to log out from https://account.abc.com as well (meaning, calling https://account.abc.com/connect/endsession), it doesn't log out. How can I achieve this?
online.abc.com HostModule : (Enable Local Login = false)
context.Services.AddAuthentication().AddAbpOpenIdConnect("oidc", options =>
            {
                options.Authority = configuration["ExternalProvider:Authority"];
                options.RequireHttpsMetadata = Convert.ToBoolean(configuration["ExternalProvider:RequireHttpsMetadata"]); ;
                options.ResponseType = OpenIdConnectResponseType.CodeIdToken;
                options.ClientId = configuration["ExternalProvider:ClientId"];
                options.ClientSecret = configuration["ExternalProvider:ClientSecret"];
                options.UsePkce = true;
                options.SaveTokens = true;
                options.GetClaimsFromUserInfoEndpoint = true;
                options.Scope.Add("role");
                options.Scope.Add("email");
                options.Scope.Add("phone");
                options.ClaimActions.MapJsonKey(ClaimTypes.NameIdentifier, "sub");
            });

Hi, I just realized that xyz.com comes to us with the following link:
https://account.abc.com/connect/endsession?post_logout_redirect_uri=https://xyz.com&client_id=Xyz_App
I customized the code as follows:
public async Task InvokeAsync(HttpContext context)
    {
        if (context.Request.Path.StartsWithSegments("/connect/endsession"))
        {
            var postLogoutRedirectUri = context.Request.Query["post_logout_redirect_uri"].ToString();
            var clientId = context.Request.Query["client_id"].ToString();

            var redirectUrl = $"/Account/LoggedOut?PostLogoutRedirectUri={postLogoutRedirectUri}&ClientName={clientId}";

            context.Response.Redirect(redirectUrl);
            return;
        }

        await _next(context);
    }
Thank you for your response.I have resolved my issue. However, I need to mention the following as well:
EDIT (2024-08-01):
The client application was not sending the id_token_hint during the invocation of /connect/endsession. Therefore, we removed the custom middleware. The system is now functioning in compliance with the standard