Hi Team,
We recently encountered an authentication issue in the Web UI due to an invalid X.509 encryption certificate configured in the Identity Service. The application logs reported the following error in identity service:
System.InvalidOperationException: When using X.509 encryption credentials, at least one of the registered certificates must be valid
The issue occurred because the Identity Service could not identify a valid registered certificate for the required encryption operation. We resolved it by creating a new Identity Service build image and redeploying it. To prevent similar issues in the future, we would like to explore proactive monitoring and alerting mechanisms. Could you please advise on the following?
Please share your recommendations on the best approach to implement these preventive measures.
Below is the code snippet for your reference.
AppContext.SetSwitch("Npgsql.EnableLegacyTimestampBehavior", true); if (!hostingEnvironment.IsDevelopment()) { PreConfigure<AbpOpenIddictAspNetCoreOptions>(options => { options.AddDevelopmentEncryptionAndSigningCertificate = false; });
            PreConfigure<OpenIddictServerBuilder>(builder =>
            {
                builder.AddSigningCertificate(GetSigningCertificate(hostingEnvironment, configuration));
                builder.AddEncryptionCertificate(GetSigningCertificate(hostingEnvironment, configuration));
private X509Certificate2 GetSigningCertificate(IWebHostEnvironment hostingEnv, IConfiguration configuration) { var fileName = "authserver.pfx"; var passPhrase = "XXXXXXXX-XXXX-XXXXX-XXXX-XXXXX8ED"; var file = Path.Combine(hostingEnv.ContentRootPath, fileName);
        if (!File.Exists(file))
        {
            throw new FileNotFoundException($"Signing Certificate couldn't found: {file}");
        }

        return new X509Certificate2(file, passPhrase);
    }
We have an old 3.1v Microservice Template, But version is upgraded 8.0. And we need to upgrade the 3.1v Microservice Template to the latest version. What is the best approach to upgrade: should we create a new template with the latest version and manually migrate the code?
Could you please provide your guidance on this?
For your reference pls find attached screen shot.

After adding the redirectUri and responseType parameters in my environment.ts file as part of the SSO OIDC integration, the SSO OIDC integration is working as expected. However, it is breaking the existing functionality.
If I comment out the redirectUri parameter, my Angular login page loads successfully. However, without commenting out the redirectUri parameter, how can I handle both scenarios: the normal user login page and the SSO OIDC login functionality?
const baseUrl = 'http://localhost:4200';
const oAuthConfig = {
  issuer: 'https://localhost:44350/',
  redirectUri: baseUrl,
  clientId: '',
  responseType: 'code',
  scope: 'offline_access ',
  requireHttps: true,
  showDebugInformation: true,
  requireHttps: true,
};
The "ClientType" column in the "OpenIddictApplications" table was initially set to "confidential" and after that you update value as "public", Then Angular application was able to successfully redirect.
However, I have notice after some time, this value automatically changed to "confidential". I have cross-checked the application but was unable to find where the value is being set.
Can you please suggest how I can fix this issue?

Tenant-Id and Tenant-Name Not Set in Header After Dashboard Redirect (SSO OIDC) #8132
https://abp.io/support/questions/8132/Tenant-Id-and-Tenant-Name-Not-Set-in-Header-After-Dashboard-Redirect-SSO-OIDC?CurrentPage=5
We have a requirement where, when a client clicks on our application logo (which is already configured within their application), they should be redirected directly to the IdP's login page instead of the ABP.IO login page. After authentication with the IdP, the user should be redirected to our dashboard.
Using below ABP.IO support ticket i am successfully able to run POC project. Note :- Tenant not set in POC project.
Error :- After integrating the same code into our existing project, we successfully authenticated with the IDP, added the user to the database, and were redirected to the dashboard. However, after a few seconds, the application automatically redirects to the logout page I have cross check log it's look like tenant not set that's why user not able to login.
For your refence please find below log
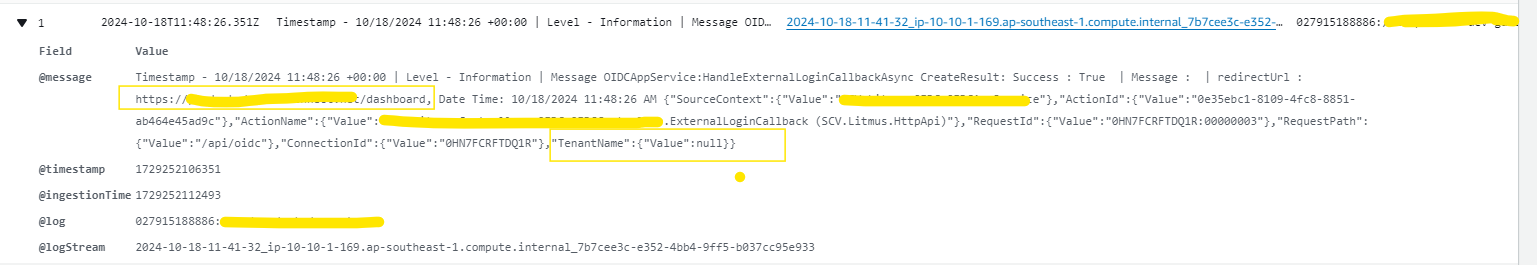
We need to set the tenant name and tenant ID headers for the dashboard redirect URL. How can we do this ?
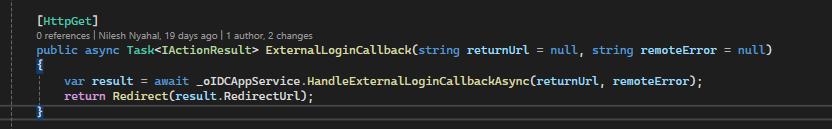
Subject :- SSO OIDC integration issue
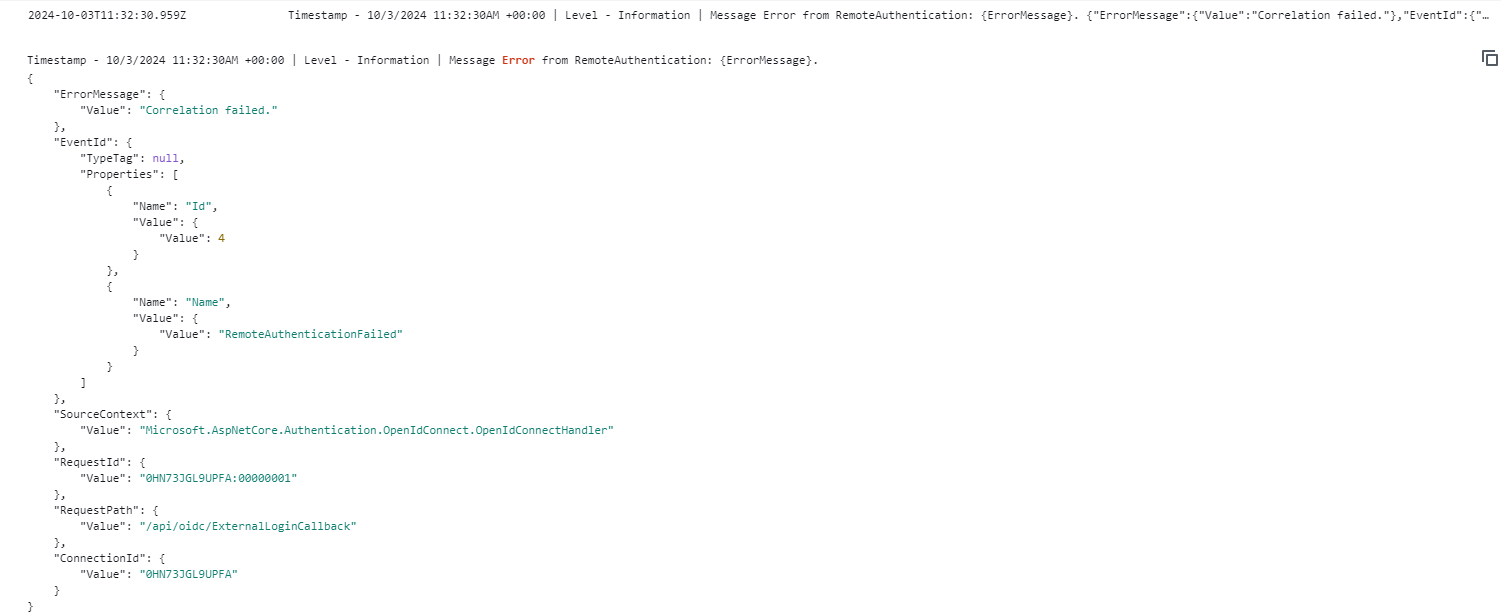
Exception details :- In our microservices architecture, we handle internal API calls using HTTP, while external applications access our APIs over HTTPS. However, when setting up the callback URL, it automatically picks up the internal domain with HTTP, leading to issues when using HTTPS.
To address this, I added the following code to modify the redirect URI:
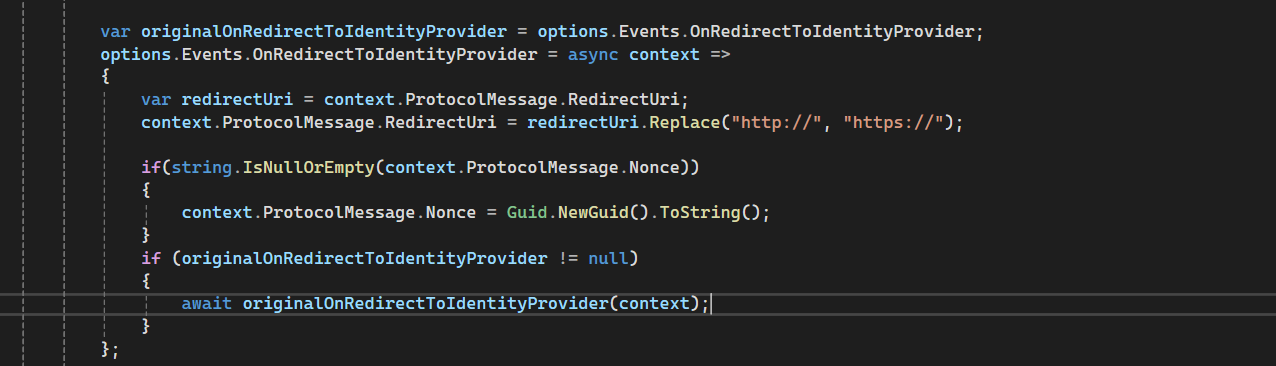 After implementing this change, I started facing the "Correlation failed" error in the remote authentication process. I’ve applied some additional fixes to resolve this issue.

I am currently facing an issue in my application, and I would greatly appreciate your assistance in resolving it.
public async Task<bool> CreateAsync(IdentityUserCreateDto input, Guid tenantId)
 {
 try
 {
 var newUserName = await GetUniqueUserNameAsync(input.Name.Trim(), input.Surname.Trim());
 var user = new IdentityUser(\_guidGenerator.Create(), newUserName.Trim(), input.Email, tenantId);

 var creationResult = await \_identityUserManager.CreateAsync(user, input.Password.Trim());
 creationResult.CheckErrors();

 await \_identityUserManager.SetEmailAsync(user, input.Email.Trim());
 await \_identityUserManager.SetPhoneNumberAsync(user, input.PhoneNumber.Trim());

 user.Name = input.Name.Trim();
 user.Surname = input.Surname.Trim();

 var claimsToAdd = new List\<Claim>
 {
 new Claim(ClaimTypes.Email, input.Email.Trim()),
 };
 await \_identityUserManager.AddClaimsAsync(user, claimsToAdd);
 await \_unitOfWorkManager.Current.SaveChangesAsync();

 await assignRoles(input, user);

 var userDetails = await \_identityUserManager.GetByIdAsync(user.Id);
 if (userDetails != null)
 {
 userDetails.SetProperty("Status", 1);
 userDetails.SetProperty("Language", "en");
 }
 await \_unitOfWorkManager.Current.SaveChangesAsync();
 }
 catch (Exception ex)
 {
 }
 }
<br>
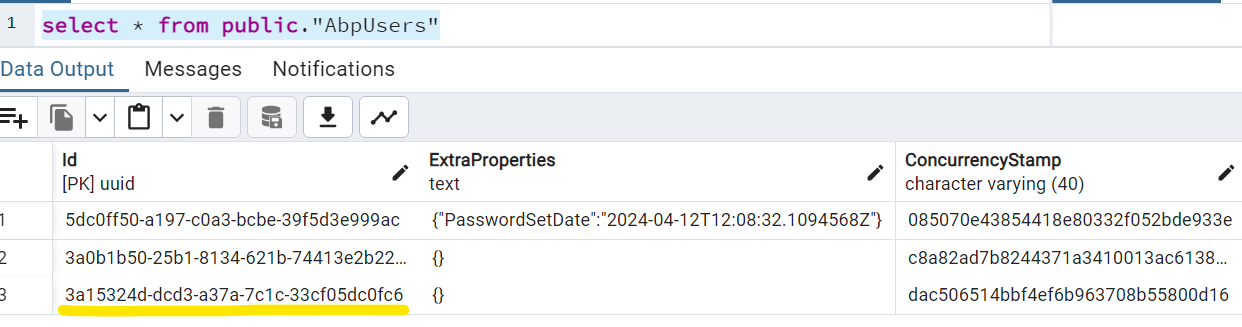
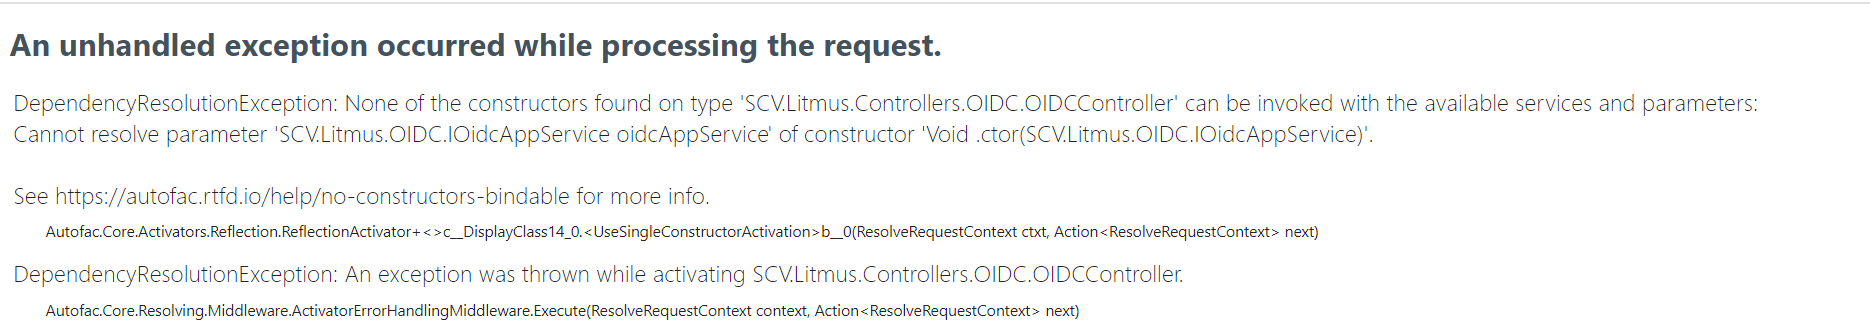
After successfully adding the user to the database, I encountered an error when executing the line var userDetails = await _identityUserManager.GetByIdAsync(user.Id);.
I have verified that the user was added to the database and that the user ID is present and correct.
Please find the attachment for your refence :-
Error :-
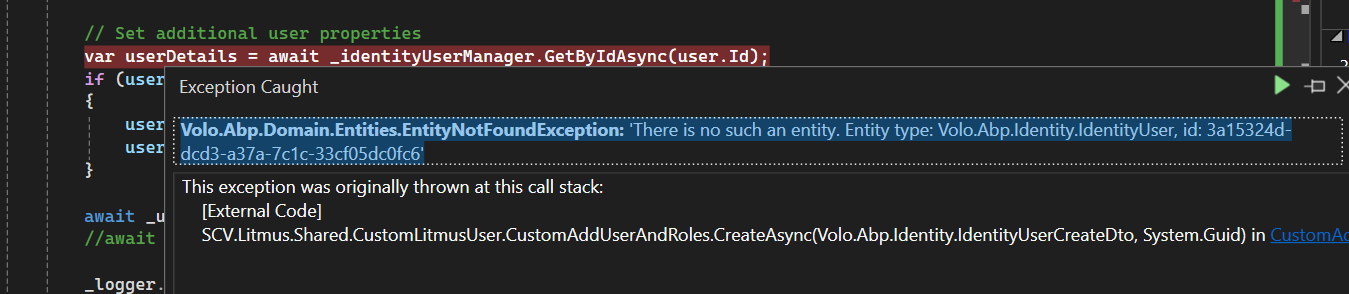
DB:-
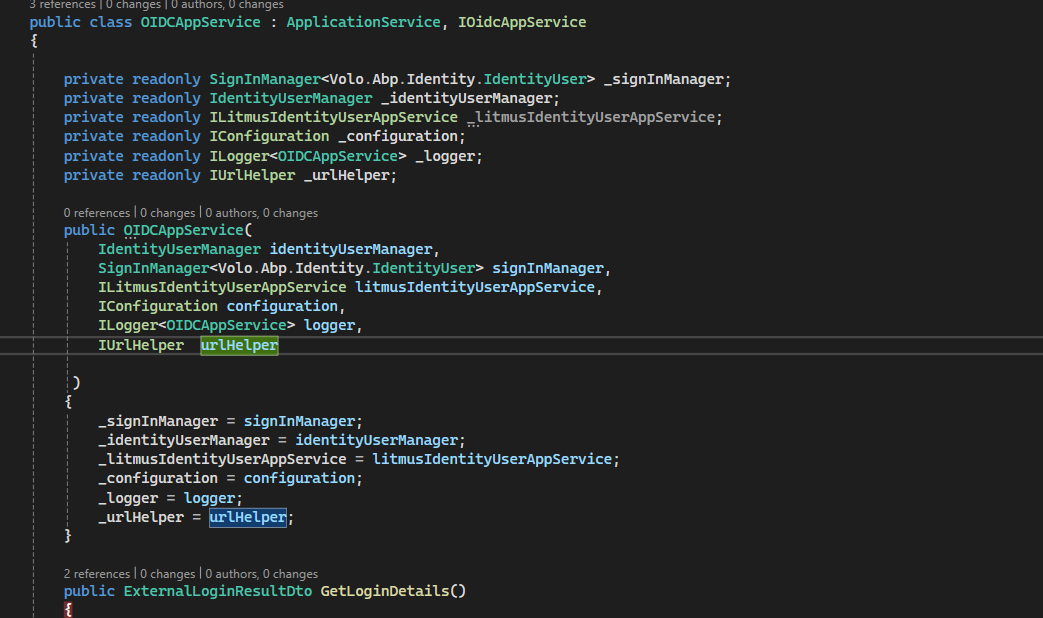
I need your assistance.
Objective: To bypass the ABP.IO login page and redirect users directly to the IdP’s login page, and after successful authentication, redirect them to application’s dashboard.
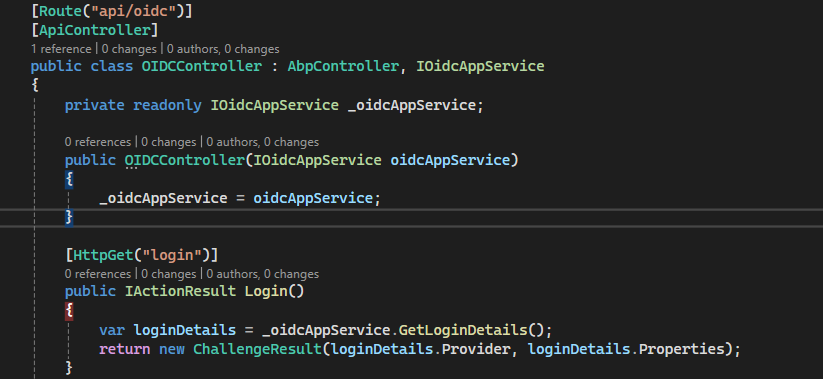
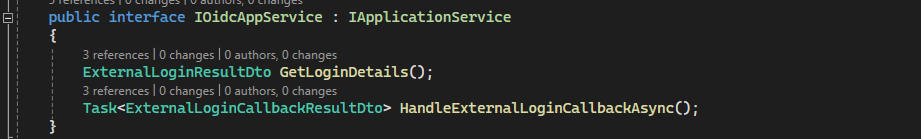
Description :- I have integrated OpenIdConnect with a third-party Identity Provider (IdP) in a new ABP.IO template project, and it is working as expected. However, we have a requirement where, when a client clicks on our application logo (which is already configured within their application), they should be redirected directly to the IdP's login page instead of the ABP.IO login page. After authentication with the IdP, the user should be redirected to our dashboard.
I need assistance how to handle routing and above scenario in abp.io template.
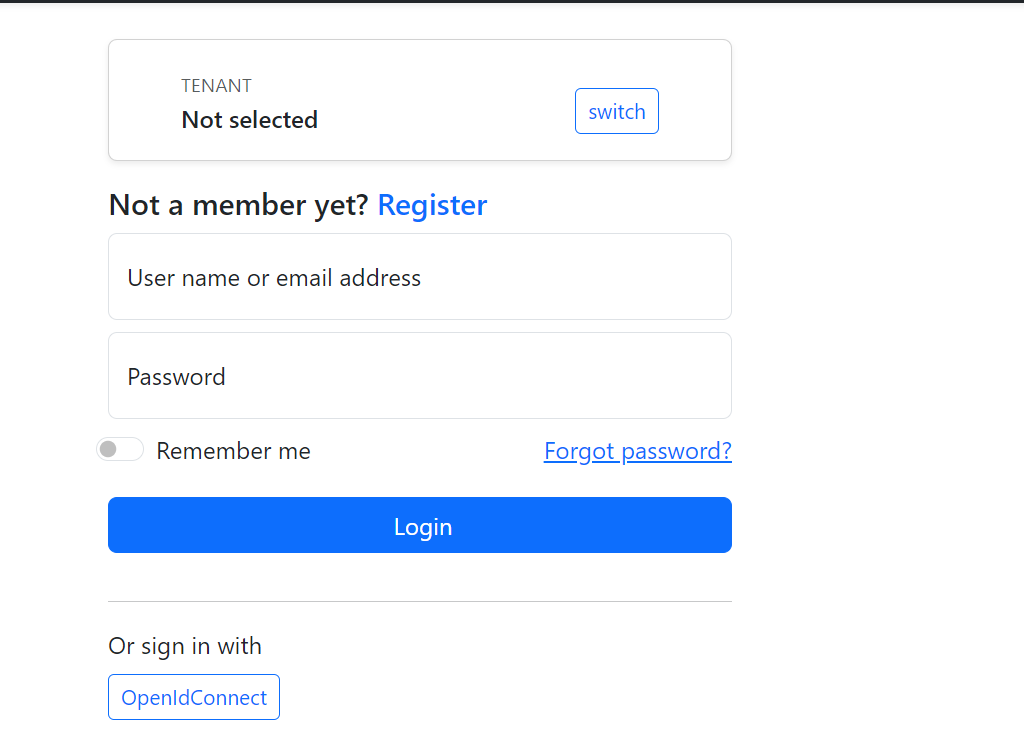
<br> I don't want to show below screen for OpenIdConnect login user.