


Hi, I've just got the issues like this like this https://abp.io/support/questions/7447/Authentication-valid-issuer-issue But the problem is not at this
nginx.ingress.kubernetes.io/whitelist-source-range
I have deploy my app to aks and configure the code of authserver like this
PreConfigure<OpenIddictServerBuilder>(serverBuilder =>
{
    serverBuilder.SetIssuer(new Uri(configuration["App:SelfUrl"]!));
    serverBuilder.SetAuthorizationEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/connect/authorize");
    serverBuilder.SetEndSessionEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/connect/logout");
    serverBuilder.SetDeviceAuthorizationEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/device");
    serverBuilder.SetUserInfoEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/connect/userinfo");
    serverBuilder.SetTokenEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/connect/token");
    serverBuilder.SetRevocationEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/connect/revocat");
    serverBuilder.SetIntrospectionEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/connect/introspect");
    serverBuilder.SetJsonWebKeySetEndpointUris($"{new Uri(configuration["App:SelfUrl"]!)}/.well-known/jwks");
});
and I also set forward header like
        context.Services.Configure<ForwardedHeadersOptions>(options =>
        {
            options.ForwardedHeaders =
                ForwardedHeaders.XForwardedFor | ForwardedHeaders.XForwardedProto;
        });
if (!env.IsDevelopment())
        if (!env.IsDevelopment())
            app.UseErrorPage();
            app.UseForwardedHeaders();
            app.UseHsts();
        }
My angular is deploy at link domain/admin and my authserver is deploy at domain/authserver. But when I access to /admin, it redirect to login page and when using the right account, I can login but it redirect back to /admin and then a loop redirect.
The log of authserver is
[16:53:34 INF] Request starting HTTP/1.1 GET http://domain.com/connect/authorize?response_type=code&client_id=Angular&state=M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2&redirect_uri=https%3A%2F%2Fdomain.com%2Fadmin&scope=openid%20profile%20email%20phone%20AccountService%20IdentityService%20AdministrationService%20SaasService&code_challenge=DVGK0fFWZJJqD3A0hzqNOQHOGkwBsMgbvYy0fqdQmq8&code_challenge_method=S256&nonce=M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2&culture=en&ui-culture=en - null null
[16:53:34 INF] The request URI matched a server endpoint: Authorization.
[16:53:34 INF] The authorization request was successfully extracted: {
"response_type": "code",
"client_id": "Angular",
"state": "M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2",
"redirect_uri": "https://domain.com/admin",
"scope": "openid profile email phone AccountService IdentityService AdministrationService SaasService",
"code_challenge": "DVGK0fFWZJJqD3A0hzqNOQHOGkwBsMgbvYy0fqdQmq8",
"code_challenge_method": "S256",
"nonce": "M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2",
"culture": "en",
"ui-culture": "en"
}.
[16:53:34 INF] The authorization request was successfully validated.
[16:53:34 INF] Executing endpoint 'Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
[16:53:34 INF] Route matched with {action = "Handle", controller = "Authorize", area = "", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.IActionResult] HandleAsync() on controller Volo.Abp.OpenIddict.Controllers.AuthorizeController (Volo.Abp.OpenIddict.AspNetCore).
[16:53:34 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
[16:53:34 ERR] OnAuthorizationAsync: Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)
[16:53:34 INF] Executing SignInResult with authentication scheme (OpenIddict.Server.AspNetCore) and the following principal: System.Security.Claims.ClaimsPrincipal.
[16:53:34 INF] The authorization response was successfully returned to 'https://domain.com/admin' using the query response mode: {
"code": "[redacted]",
"state": "M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2",
"iss": "https://domain.com/authserver",
"culture": "en",
"ui-culture": "en"
}.
[16:53:34 INF] Executed action Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore) in 453.3281ms
[16:53:34 INF] Executed endpoint 'Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
[16:53:34 INF] Request finished HTTP/1.1 GET https://domain.com/authserver/connect/authorize?response_type=code&client_id=Angular&state=M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2&redirect_uri=https%3A%2F%2Fdomain.com%2Fadmin&scope=openid%20profile%20email%20phone%20AccountService%20IdentityService%20AdministrationService%20SaasService&code_challenge=DVGK0fFWZJJqD3A0hzqNOQHOGkwBsMgbvYy0fqdQmq8&code_challenge_method=S256&nonce=M2dScEZzS2N1fjRTM3BXZEFGMEgybDZBSXJrdHRteHp0WnMwaU4wRWpvdzJ2&culture=en&ui-culture=en - 302 0 null 775.3449ms
[16:53:35 INF] Request starting HTTP/1.1 GET http://domain.com/.well-known/openid-configuration - null null
[16:53:35 INF] The request URI matched a server endpoint: Configuration.
[16:53:35 INF] The configuration request was successfully extracted: {}.
[16:53:35 INF] The configuration request was successfully validated.
[16:53:35 INF] The response was successfully returned as a JSON document: {
"issuer": "https://domain.com/authserver",
"authorization_endpoint": "https://domain.com/authserver/connect/authorize",
"token_endpoint": "https://domain.com/authserver/connect/token",
"introspection_endpoint": "https://domain.com/authserver/connect/introspect",
"end_session_endpoint": "https://domain.com/authserver/connect/logout",
"revocation_endpoint": "https://domain.com/authserver/connect/revocat",
"userinfo_endpoint": "https://domain.com/authserver/connect/userinfo",
"device_authorization_endpoint": "https://domain.com/authserver/device",
"jwks_uri": "https://domain.com/authserver/.well-known/jwks",
"grant_types_supported": [
"authorization_code",
"implicit",
"password",
"client_credentials",
"refresh_token",
"urn:ietf:params:oauth:grant-type:device_code",
"LinkLogin",
"Impersonation"
],
"response_types_supported": [
"code",
"code id_token",
"code id_token token",
"code token",
"id_token",
"id_token token",
"token",
"none"
],
"response_modes_supported": [
"query",
"form_post",
"fragment"
],
"scopes_supported": [
"openid",
"offline_access",
"email",
"profile",
"phone",
"roles",
"address",
"AccountService",
"IdentityService",
"AdministrationService",
"SaasService"
],
"claims_supported": [
"aud",
"exp",
"iat",
"iss",
"sub"
],
"id_token_signing_alg_values_supported": [
"RS256"
],
"code_challenge_methods_supported": [
"plain",
"S256"
],
"subject_types_supported": [
"public"
],
"prompt_values_supported": [
"consent",
"login",
"none",
"select_account"
],
"token_endpoint_auth_methods_supported": [
"client_secret_post",
"private_key_jwt",
"client_secret_basic"
],
"introspection_endpoint_auth_methods_supported": [
"client_secret_post",
"private_key_jwt",
"client_secret_basic"
],
"revocation_endpoint_auth_methods_supported": [
"client_secret_post",
"private_key_jwt",
"client_secret_basic"
],
"device_authorization_endpoint_auth_methods_supported": [
"client_secret_post",
"private_key_jwt",
"client_secret_basic"
],
"claims_parameter_supported": false,
"request_parameter_supported": false,
"request_uri_parameter_supported": false,
"tls_client_certificate_bound_access_tokens": false,
"authorization_response_iss_parameter_supported": true
}.
[16:53:35 INF] Request finished HTTP/1.1 GET https://domain.com/authserver/.well-known/openid-configuration - 200 2778 application/json;charset=UTF-8 16.5762ms
[16:53:35 INF] Request starting HTTP/1.1 GET http://domain.com/.well-known/jwks - null null
[16:53:35 INF] The request URI matched a server endpoint: JsonWebKeySet.
[16:53:35 INF] The JSON Web Key Set request was successfully extracted: {}.
[16:53:35 INF] The JSON Web Key Set request was successfully validated.
[16:53:35 INF] The response was successfully returned as a JSON document: {
"keys": [
{
"kid": "ABBE2D8F18E20CC5D05FF8EBD8932896F351364A",
"use": "sig",
"kty": "RSA",
"alg": "RS256",
"e": "AQAB",
"n": "xVi6Ofl-xz_DZPGOEssj69eJO4UZ5l5hhznwhZ-CaXoOYz-mW_svsLVI2x0D2JpKSII1KPAALnVQWxf0_LFr9hmSQX3CmnFO0yT6zmA-ZT7CQZlMIunkY9E_oKL4y-45zXBwMRH3BW54i9z3qI-tALaNp9UiCiAcfFbYzU3oW5lCZj05fSRf9q5gIHa6nu93Q10MilaxsBNsCFxwUcBIyK8X92wqedBwrzeEukkkyAz5qG1aD9U-3QIuCuQsNWa5a1qUAyxfM-Q8oUThWh6sk72T6xteL4ApxctqtjPEZ0VotjhVSbQVwtD_5i-DvpuiRQL461ilt35ZVDGw1QJooQ",
"x5t": "q74tjxjiDMXQX_jr2JMolvNRNko",
"x5c": [
"MIIDDTCCAfWgAwIBAgIJAMuAFCpOifXxMA0GCSqGSIb3DQEBCwUAMBQxEjAQBgNVBAMTCWxvY2FsaG9zdDAeFw0yNTA0MTIwMzU3MzVaFw0yNjA0MTIwMzU3MzVaMBQxEjAQBgNVBAMTCWxvY2FsaG9zdDCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAMVYujn5fsc/w2TxjhLLI+vXiTuFGeZeYYc58IWfgml6DmM/plv7L7C1SNsdA9iaSkiCNSjwAC51UFsX9Pyxa/YZkkF9wppxTtMk+s5gPmU+wkGZTCLp5GPRP6Ci+MvuOc1wcDER9wVueIvc96iPrQC2jafVIgogHHxW2M1N6FuZQmY9OX0kX/auYCB2up7vd0NdDIpWsbATbAhccFHASMivF/dsKnnQcK83hLpJJMgM+ahtWg/VPt0CLgrkLDVmuWtalAMsXzPkPKFE4VoerJO9k+sbXi+AKcXLarYzxGdFaLY4VUm0FcLQ/+Yvg76bokUC+OtYpbd+WVQxsNUCaKECAwEAAaNiMGAwDAYDVR0TAQH/BAIwADAOBgNVHQ8BAf8EBAMCBaAwFgYDVR0lAQH/BAwwCgYIKwYBBQUHAwEwFwYDVR0RAQH/BA0wC4IJbG9jYWxob3N0MA8GCisGAQQBgjdUAQEEAQIwDQYJKoZIhvcNAQELBQADggEBACnRy8UwkbLUqhHfmSUliiaNQqBNxyLTOhXe+V6cHBh+6B9B96v4/HKKT2T2RWzb7hJRPUY9CX/YfDt39lXwoSNpHYKTVZGRSyS8o8auXAV0TWYJbEL8/l/O1+dq04Qkb+vcs+cOq8UxOrgRtVbYolo4nw0chC+N+LCm3YMa2qMPLgVXusIaIhkUC7BV+06kinKoyEGJl5eivaf/xo4jjxMQiMCPAWQrBUdBdSvJeyOlAwItSm9N0e4WFVDtlnqGFgOhj1LVUq3k+D0s8GKWCNajbOznkuvZsH0GGQM9mGJOXg4dFoNaDNwWdQ8lqvJaV7spg4oCbdiliIkN+TB+Dns="
]
}
]
}.
[16:53:35 INF] Request finished HTTP/1.1 GET https://domain.com/authserver/.well-known/jwks - 200 1652 application/json;charset=UTF-8 3.0629ms
[16:53:36 INF] Request starting HTTP/1.1 POST http://domain.com/connect/token - application/x-www-form-urlencoded 246
[16:53:36 INF] CORS policy execution failed.
[16:53:36 INF] Request origin https://domain.com does not have permission to access the resource.
[16:53:36 INF] The request URI matched a server endpoint: Token.
[16:53:36 INF] The token request was successfully extracted: {
"grant_type": "authorization_code",
"code": "[redacted]",
"redirect_uri": "https://domain.com/admin",
"code_verifier": "Z2VkWTVvVE1MVTJWYzRBQ3daMMkR-b1RjTjY4",
"client_id": "Angular"
}.
[16:53:36 INF] The token request was successfully validated.
[16:53:36 INF] Executing endpoint 'Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
[16:53:36 INF] Route matched with {action = "Handle", controller = "Token", area = "", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.IActionResult] HandleAsync() on controller Volo.Abp.OpenIddict.Controllers.TokenController (Volo.Abp.OpenIddict.AspNetCore).
[16:53:36 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
[16:53:36 ERR] OnAuthorizationAsync: Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)
[16:53:36 INF] Executing SignInResult with authentication scheme (OpenIddict.Server.AspNetCore) and the following principal: System.Security.Claims.ClaimsPrincipal.
[16:53:36 INF] The token '3a194c8b-a935-2dc3-046f-aba1f5c013ee' was successfully marked as redeemed.
[16:53:36 INF] The response was successfully returned as a JSON document: {
"access_token": "[redacted]",
"token_type": "Bearer",
"expires_in": 2591999,
"scope": "openid profile email phone AccountService IdentityService AdministrationService SaasService ",
"id_token": "[redacted]"
}.
[16:53:36 INF] Executed action Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore) in 333.3868ms
[16:53:36 INF] Executed endpoint 'Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
[16:53:36 INF] Request finished HTTP/1.1 POST https://domain.com/authserver/connect/token - 200 3145 application/json;charset=UTF-8 680.5732ms
The log of administration services:
16:52:42 INF] Request starting HTTP/1.1 GET http://dbr-st-administration/api/abp/application-configuration?includeLocalizationResources=false - null null
[16

Microsoft.IdentityModel.Tokens.SecurityTokenInvalidIssuerException: IDX10204: Unable to validate issuer. validationParameters.ValidIssuer is null or whitespace AND validationParameters.ValidIssuers is null or empty.
at Microsoft.IdentityModel.Tokens.Validators.ValidateIssuerAsync(String issuer, SecurityToken securityToken, TokenValidationParameters validationParameters, BaseConfiguration configuration)
at Microsoft.IdentityModel.Tokens.Validators.ValidateIssuer(String issuer, SecurityToken securityToken, TokenValidationParameters validationParameters, BaseConfiguration configuration)
at Microsoft.IdentityModel.Tokens.InternalValidators.ValidateAfterSignatureFailed(SecurityToken securityToken, Nullable`1 notBefore, Nullable`1 expires, IEnumerable`1 audiences, TokenValidationParameters validationParameters, BaseConfiguration configuration)
at Microsoft.IdentityModel.JsonWebTokens.JsonWebTokenHandler.ValidateSignature(JsonWebToken jwtToken, TokenValidationParameters validationParameters, BaseConfiguration configuration)
at Microsoft.IdentityModel.JsonWebTokens.JsonWebTokenHandler.ValidateSignatureAndIssuerSecurityKey(JsonWebToken jsonWebToken, TokenValidationParameters validationParameters, BaseConfiguration configuration)
at Microsoft.IdentityModel.JsonWebTokens.JsonWebTokenHandler.ValidateJWSAsync(JsonWebToken jsonWebToken, TokenValidationParameters validationParameters, BaseConfiguration configuration)
[16:53:04 INF] Bearer was not authenticated. Failure message: IDX10204: Unable to validate issuer. validationParameters.ValidIssuer is null or whitespace AND validationParameters.ValidIssuers is null or empty.
[16:53:04 INF] Executing endpoint 'Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationController.GetAsync (Volo.Abp.AspNetCore.Mvc)'
[16:53:04 INF] Route matched with {area = "abp", action = "Get", controller = "AbpApplicationConfiguration", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.ApplicationConfigurationDto] GetAsync(Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.ApplicationConfigurationRequestOptions) on controller Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationController (Volo.Abp.AspNetCore.Mvc).
[16:53:04 WRN] The cookie 'XSRF-TOKEN' has set 'SameSite=None' and must also set 'Secure'.
[16:53:05 INF] Executing ObjectResult, writing value of type 'Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.ApplicationConfigurationDto'.
2 Answer(s)
-
0
Hi, first of all, thanks for sharing all the details. It seems the
AuthServerissues a token correctly with:"iss": "https://domain.com/authserver"But, the consuming service (
AdministrationService) throws:SecurityTokenInvalidIssuerException: IDX10204: Unable to validate issuer.This probably happens because the token validation parameters in your consuming services do not include "https://domain.com/authserver" as a valid issuer.
So, to fix this problem, in your AdministrationService, make sure your JWT Bearer configuration includes the issuer:
        context.Services.AddAuthentication(JwtBearerDefaults.AuthenticationScheme)
            .AddAbpJwtBearer(options =>
            {
                options.Authority = configuration["AuthServer:Authority"];
                options.MetadataAddress = configuration["AuthServer:MetaAddress"]!.EnsureEndsWith('/') + ".well-known/openid-configuration";
                options.RequireHttpsMetadata = configuration.GetValue<bool>(configuration["AuthServer:RequireHttpsMetadata"]);
                options.Audience = configuration["AuthServer:Audience"];

                //issuer configuration
                options.TokenValidationParameters = new TokenValidationParameters
                {
                    ValidateIssuer = true, //or set it as false, if you don't want to validate the issuer
                    ValidIssuer = "https://domain.com/authserver", // Match exactly
                    // Or use ValidIssuers = new[] { "https://domain.com/authserver" }
                };
            });
Note: Make sure this is consistent across all services that consume the tokens. (not just for administration service)
Also, please ensure you are calling
app.UseForwardedHeaders();before the routing, authentication and authorization middlewares!Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hi
Can you confirm if your
administration servicescan communicate with yourauthserver.eg: can
administration servicesrequestdomain.com/.well-known/openid-configurationsuccessfullyYou can enable the
identitymodellogs in youradministration servicesapp.IdentityModelEventSource.ShowPII = true; IdentityModelEventSource.Logger.LogLevel = EventLevel.Verbose; var wilsonTextLogger = new TextWriterEventListener("Logs/identitymodel.txt"); wilsonTextLogger.EnableEvents(IdentityModelEventSource.Logger, EventLevel.Verbose);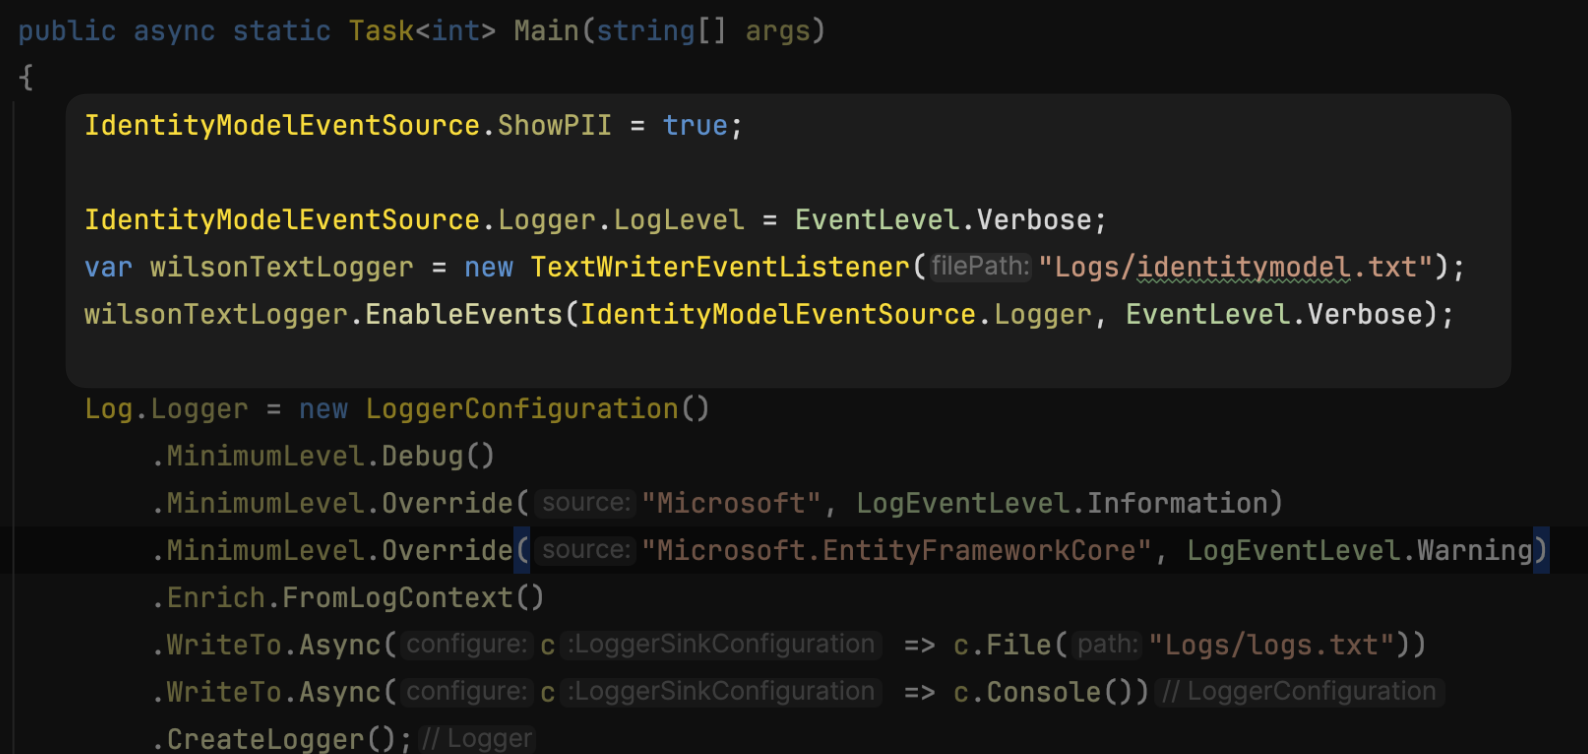 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)



