hi
Antiforgery token validation failed. The provided antiforgery token was meant for a different claims-based user than the current user.
Yes, this is because you have logged in to another tab.
I think in the given situation I could just redirect a user (already authenticated in the first tab) to the initial (home) page in the second tab, if such situation takes place instead of trying to log him in again. I just need the hint where I should place the corresponding check, please.
We have added a new js to refresh the page if authentication changes. You can add this js file to your 8.1.3 version.
https://github.com/abpframework/abp/pull/19569
https://github.com/abpframework/abp/pull/21167
Thanks, I will update it.
Hi
Please make your repos private and invite github.com/maliming
Thanks
hi
Can you share the logs.txt?
liming.ma@volosoft.com
: )
I have confirmed. You can't use layer-template. We will fix this in the next Studio version.
hi
There isn't much information in the logs. Can your website be changed so that I can access it? That way I can reproduce the problem online.
hi
the angular can use the access_token to get application configuration
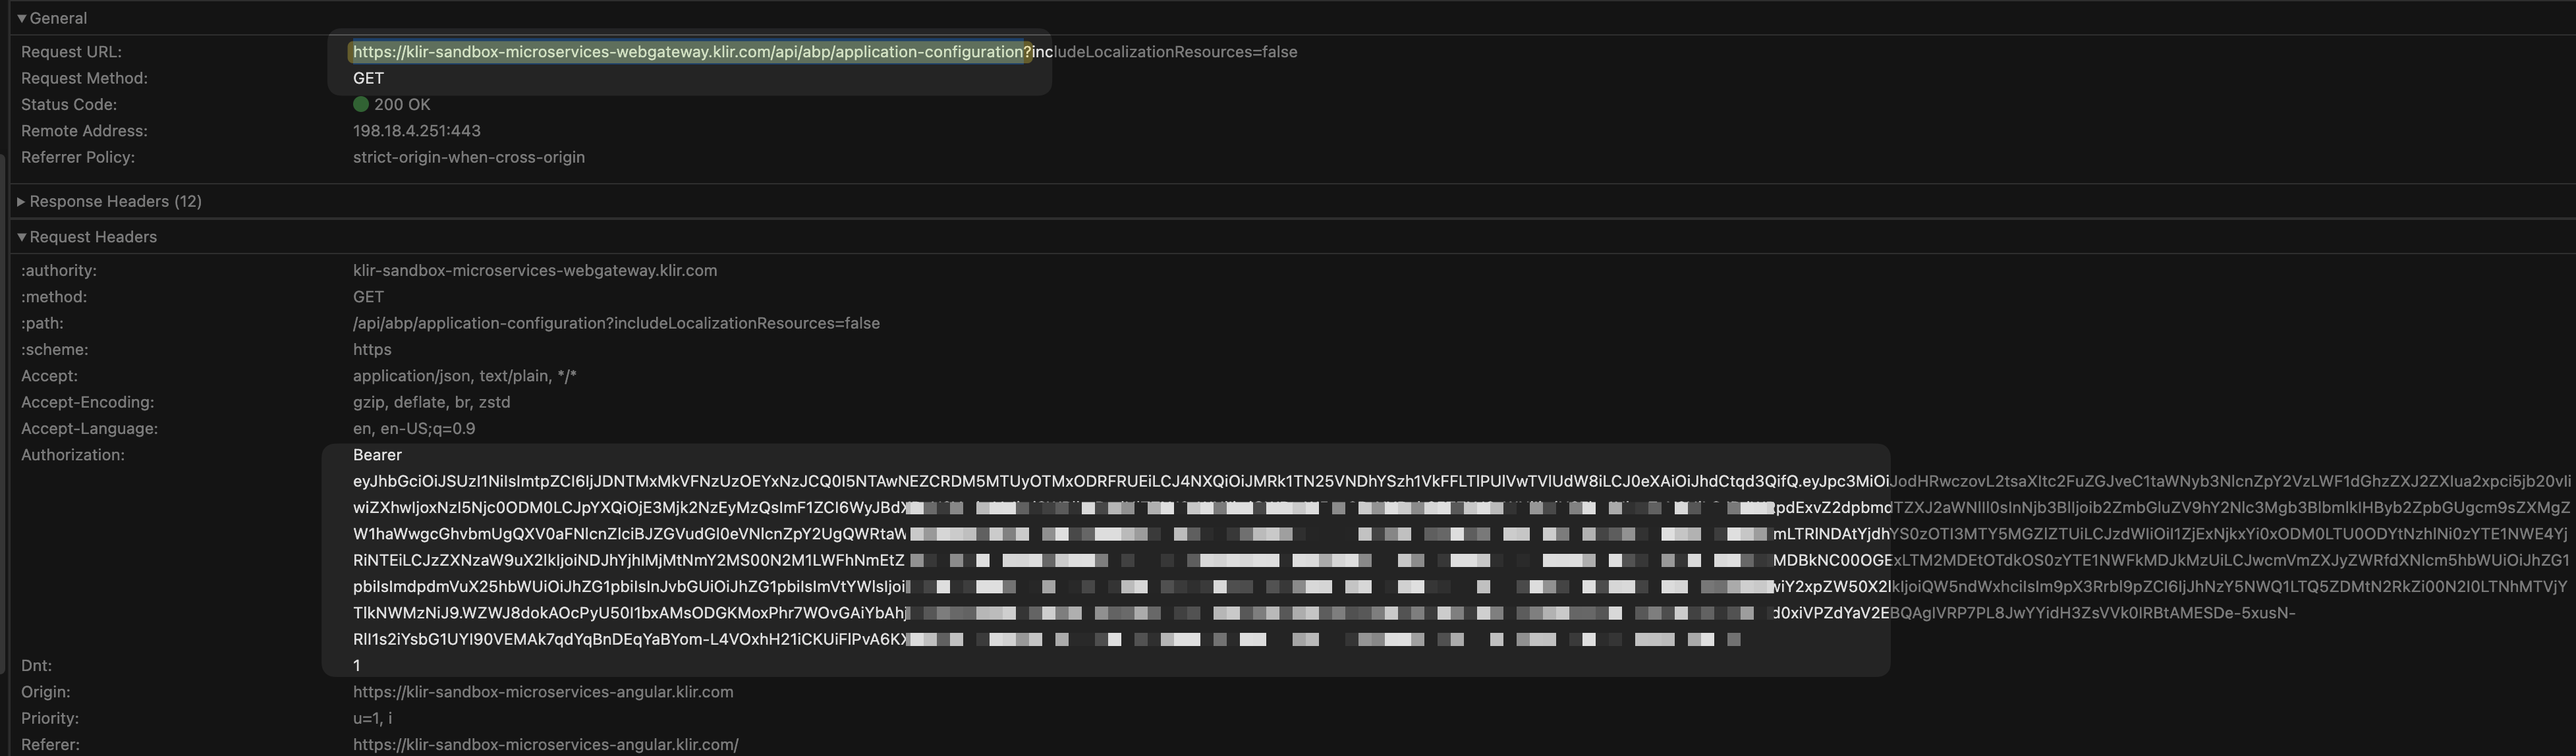
Can you share the logs for https://klir-sandbox-microservices-webgateway.klir.com/api/abp/application-configuration?
The logs you have shared don't include it.
Thanks
hi
In this case, you will get error 400 because of the "reused token" issue. This is what I am trying to avoid.
2024-10-23 11:09:42.807 +03:00 [INF] Antiforgery token validation failed. The antiforgery cookie token and request token do not match.
Microsoft.AspNetCore.Antiforgery.AntiforgeryValidationException: The antiforgery cookie token and request token do not match.
   at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateTokens(HttpContext httpContext, AntiforgeryTokenSet antiforgeryTokenSet)
   at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext)
   at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context)
2024-10-23 11:09:42.809 +03:00 [INF] Authorization failed for the request at filter 'Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.AutoValidateAntiforgeryTokenAuthorizationFilter'.
2024-10-23 11:09:42.813 +03:00 [INF] Executing StatusCodeResult, setting HTTP status code 400
This is the AntiforgeryToken error.
When you log in in tab-a, your cookies will be refreshed, and the old antiforgery token is still saved in tab-b HTML from.
see https://learn.microsoft.com/en-us/aspnet/core/security/anti-request-forgery?view=aspnetcore-8.0#multiple-browser-tabs-and-the-synchronizer-token-pattern




