hi
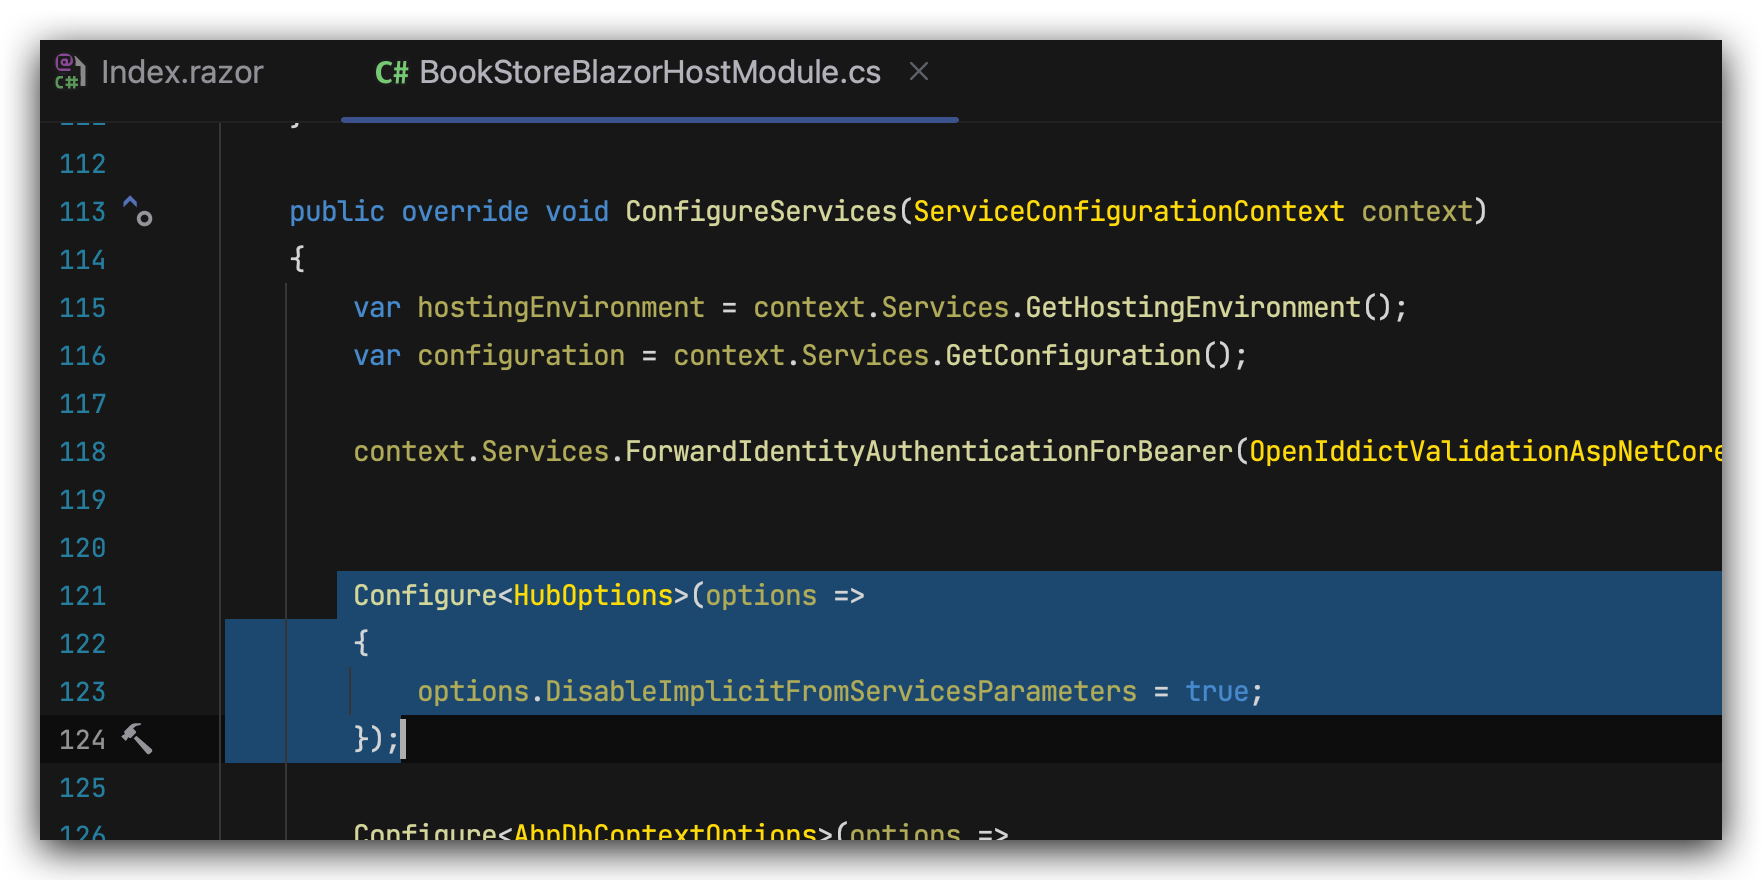
Configure<HubOptions>(options =>
{
    options.DisableImplicitFromServicesParameters = true;
});
https://github.com/dotnet/aspnetcore/issues/38842#issuecomment-1342540950
hi
https for all urls required. Also for urls received by discovery
Please share the logs of authserver.
hi
You can add a middleware after the authentication.
app.Use(async (context, next) =>
{
    // Do work that can write to the Response.
    await next.Invoke();
    // Do logging or other work that doesn't write to the Response.
});
https://learn.microsoft.com/en-us/aspnet/core/fundamentals/middleware/?view=aspnetcore-7.0
hi
You can check the current user's claims in the internal website. The client_id in the claims.
Thanks @john
You can try, if there is an error you can degrade your CLI and Suite to old version.
Source code also is broken.
hi
You can try this:
Alerts.Danger("unauthorized messages");
return Page();
hi
The LoginInput.UserNameOrEmailAddress. : )




