ok, I see. will work on it.
hi
The only thing that temporarily makes permissions work again is clearing cookies and flushing Redis cache.
After that, refreshing the page will work.
options.Events.OnValidatePrincipal
context.Services.AddAuthentication(options =>
{
    options.DefaultScheme = "Cookies";
    options.DefaultChallengeScheme = "oidc";
})
.AddCookie("Cookies", options =>
{
    options.ExpireTimeSpan = TimeSpan.FromDays(365);
    options.Events.OnValidatePrincipal = async principalContext =>
    {
        if (principalContext.Principal != null && principalContext.Principal.Identity != null && principalContext.Principal.Identity.IsAuthenticated)
        {
            var accessToken = principalContext.Properties.GetTokenValue("access_token");
            if (accessToken.IsNullOrWhiteSpace())
            {
                principalContext.RejectPrincipal();
                await principalContext.HttpContext.SignOutAsync("Cookies");
                return;
            }

            var httpClient = principalContext.HttpContext.RequestServices.GetRequiredService<IHttpClientFactory>().CreateClient();
            var response = await httpClient.IntrospectTokenAsync(new TokenIntrospectionRequest
            {
                Address = configuration["AuthServer:Authority"] + "/connect/introspect",
                ClientId = configuration["AuthServer:ClientId"],
                ClientSecret = configuration["AuthServer:ClientSecret"],
                Token = accessToken
            });

            if (!response.IsActive)
            {
                principalContext.RejectPrincipal();
                await principalContext.HttpContext.SignOutAsync("Cookies");
            }
        }
    };
})
.AddAbpOpenIdConnect("oidc", options =>
{
    options.Authority = configuration["AuthServer:Authority"];
    options.RequireHttpsMetadata = Convert.ToBoolean(configuration["AuthServer:RequireHttpsMetadata"]);;
    options.ResponseType = OpenIdConnectResponseType.CodeIdToken;

    options.ClientId = configuration["AuthServer:ClientId"];
    options.ClientSecret = configuration["AuthServer:ClientSecret"];

    options.SaveTokens = true;
    options.GetClaimsFromUserInfoEndpoint = true;

    options.Scope.Add("roles");
    options.Scope.Add("email");
    options.Scope.Add("phone");
    options.Scope.Add("BookStore");
});
we are using the blazorise library.
https://blazorise.com/docs/components/tab
hi
Can you share the implementation of this API?
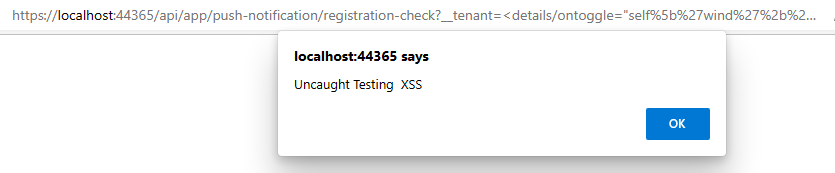
At the same time, angular should encode the response.
hi
I read MASA.Blazor document but didn't know its design ideas.
Maybe it can't be compatible with abp, I'm not sure.
I suggest you get help from MASA.Blazor
hi
Might be a false positive of Cloudflare.
https://support.abp.io/QA/Questions/4623
hi
What is your post content?
Please share the screenshot.
hi
I have limited experience with cookie management and am wondering if there are possible issues or workarounds to consider.
something like this https://gist.github.com/maliming/b1ea80d68982a5b7064d7df6bafa89f5
hi
Redis should be used as a high-performance cache, and it is not recommended to use it across the country.
You can change the redis server closest to you.
hi
Please share steps and code to reproduce this in the new template project.




