[maliming] said: Hi,
Quick context: in ABP 8.2.3, the
@abp/uppynpm wrapper declares"uppy": "^3.0.0", and npm resolves that to the latest 3.x — which is 3.27.3. The wrapper has no JS code of its own; it just copiesnode_modules/uppy/dist/*towwwroot/libs/uppy/viaabp.resourcemapping.js. So you can change the resolveduppyversion without touching ABP server-side (NuGet) packages.Two important signals before we pick a fix:
- Your report shows
uppy@3.27.3 (Transitive). In most SCA tools,(Transitive)means uppy is brought in through another package (here,@abp/uppy). The finding can either be in uppy's own code or in one of uppy's own sub-dependencies, and scanners often display the top-level package as the "vulnerable" one.- The public databases we can check do not flag
uppy@3.27.3itself:
- Snyk: https://security.snyk.io/package/npm/uppy/3.27.3 — "No direct vulnerabilities have been found for this package."
- GitHub Advisory Database / NVD: no advisory matching
uppy + CWE-843.This strongly suggests the actual vulnerable package is a sub-dependency of uppy, not uppy itself. To pinpoint it, please share:
- Output of
npm ls uppy(full chain, so we can confirm whether it comes through@abp/uppyor something else)- The exact advisory ID from your scanner (CVE / GHSA / SNYK-ID), and ideally the "vulnerable package" field — that one is the package you actually need to bump, not necessarily
uppyWhile you collect those, here are the upgrade paths in order of safety:
Option 1 — Bump only the
@abp/*npm packages to~8.3.x(recommended). Keep ABP NuGet at 8.2.3.@abp/uppy@~8.3.xdeclares"uppy": "^3.27.0", so you stay on the 3.x line and just get the latest 3.27 patch. This is the smallest change and may already pull a fresh enough sub-dependency to clear the finding.# In your client project, change @abp/* packages to ~8.3.x in package.json, then: rm -rf node_modules package-lock.json npm install npm ls uppyOption 2 — npm
overridesto pin the actual vulnerable package. Once you know which sub-dependency the scanner is flagging, override that one directly (not necessarilyuppy). Example shape:{ "overrides": { "<the-actual-vulnerable-package>": "<fixed-version>" } }If the scanner really is flagging
uppyitself, pin uppy to the latest 3.x patch and stay on the 3.x major.Don't blindly jump to
uppy@4.xor5.xvia overrides. Uppy 4.x went ESM-only and 5.x changed bundle/plugin internals further. ABP's MVC pages callUppy.Dashboard,Uppy.XHRUpload,uppy.use(), etc. via the global bundle, and although ABP itself moved to uppy 4 in v9.0 and uppy 5 in v10.0, that came with corresponding npm-pack updates and library-refresh runs (abp install-libs). Overriding the major across a wrong@abp/uppyversion risks runtime errors in upload UI (file-management, cms-kit-admin, identity user import, account profile picture, etc.).For reference, this is how ABP itself has moved uppy:
|
@abp/uppyversion |uppyrange | | --- | --- | | 8.0.x – 8.2.x |^3.0.0| | 8.3.x |^3.27.0| | 9.x |^4.4.1| | 10.x |^5.1.2|Also note: there is no ABP configuration switch that mitigates an npm-level vulnerability. It is purely a dependency-version question. If your client app does not actually use any Uppy-based upload UI at runtime, removing the package that pulls it in is also an option, but again
npm ls uppyis the first step to know what to remove.Thanks
Hi,
Thanks for the detailed explanation. The vulnerability flagged by our scanner is CVE-2025-70023, affecting uppy@3.27.3, which is currently resolved as a transitive dependency in our project. At the moment, the scanner indicates that no remediated (fixed) version is available yet. Based on this, I would like to clarify a few points:
Since there is no patched version available upstream, is there any recommended mitigation approach from ABP’s side (temporary or compensating control)? Would it be advisable to remove or replace @abp/uppy entirely if the functionality is not actively used, to eliminate the vulnerable dependency? Are there any safe workarounds (e.g., restricting features, usage patterns, or runtime configurations) that could reduce the risk exposure until an official fix is released? Lastly, does ABP have any planned update or advisory regarding this CVE for upcoming releases?
We understand this is an upstream issue, but any guidance on minimizing risk within the current ABP 8.2.3 setup would be very helpful. Thanks in advance for your support.
[maliming] said: Hi,
The CWE-693 vulnerability (GHSA-5wr9-m6jw-xx44) in Scriban is about
TemplateContextcaching type member accessors byTypeonly. It can be exploited when aTemplateContextinstance is reused across renders and theMemberFilterorMemberRenameris tightened between renders — previously cached accessors may still be exposed.
However, ABP's Scriban usage does not trigger this vulnerability:
- ABP creates a new
TemplateContextinstance for every render call — it never reusesTemplateContextacross renders.
- ABP does not configure
MemberFilterorMemberRenameronTemplateContextat all.
Since the vulnerability requires reusing a
TemplateContextwith dynamically tightened member access restrictions, and ABP doesn't do that, the actual risk is very low.
That said, if you want to eliminate the warning entirely, you can override the Scriban version to 7.0.0 in your project file. We tested this with ABP 8.2.3 on .NET 8 and it works without any issues:
This will resolve all Scriban-related security warnings.
Alternatively, if you prefer to keep the original version, you can suppress specific advisories:
Thanks
Hi,
I tried adding
<ItemGroup> <PackageReference Include="Scriban" Version="7.0.0" /> </ItemGroup> but getting below execption:
2026-04-13 14:15:10.552 +08:00 [ERR] Could not load type 'Scriban.Parsing.ParserOptions' from assembly 'Volo.Abp.TextTemplating.Scriban, Version=8.2.3.0, Culture=neutral, PublicKeyToken=null' due to value type mismatch.
System.TypeLoadException: Could not load type 'Scriban.Parsing.ParserOptions' from assembly 'Volo.Abp.TextTemplating.Scriban, Version=8.2.3.0, Culture=neutral, PublicKeyToken=null' due to value type mismatch.
at Volo.Abp.TextTemplating.Scriban.ScribanTemplateRenderingEngine.RenderTemplateContentWithScribanAsync(TemplateDefinition templateDefinition, String templateContent, Dictionary2 globalContext, Object model) at System.Runtime.CompilerServices.AsyncMethodBuilderCore.Start[TStateMachine](TStateMachine& stateMachine) at Volo.Abp.TextTemplating.Scriban.ScribanTemplateRenderingEngine.RenderTemplateContentWithScribanAsync(TemplateDefinition templateDefinition, String templateContent, Dictionary2 globalContext, Object model)
at Volo.Abp.TextTemplating.Scriban.ScribanTemplateRenderingEngine.RenderSingleTemplateAsync(TemplateDefinition templateDefinition, Dictionary2 globalContext, Object model) at Volo.Abp.TextTemplating.Scriban.ScribanTemplateRenderingEngine.RenderInternalAsync(String templateName, Dictionary2 globalContext, Object model)
at Volo.Abp.TextTemplating.Scriban.ScribanTemplateRenderingEngine.RenderAsync(String templateName, Object model, String cultureName, Dictionary2 globalContext) at Volo.Abp.TextTemplating.AbpTemplateRenderer.RenderAsync(String templateName, Object model, String cultureName, Dictionary2 globalContext)
at eFC.Common.ReportGenerator.SetHeaderTemplate(String FCNo, Encounter encounter, String mrn, Patient patient, String Specialty, String surgicalProcedure, String basedOn, String pGender, String residentialStatus, String specilaty, String headerText, String headerBody, String institutionCode, String campusCode, String encounterNoForheader, String fcmodecode) in C:\DIM\OctRelease\eFC\src\src\eFC.Application\Common\ReportGenerator.cs:line 814
at eFC.Common.ReportGenerator.GenerateETBSDetailedAsync(BillDetailDto bill, Int64 FCId, String priceMode, Boolean IsDetailed, Nullable1 columnId, String username, Boolean calcEstimatedMSVHPay) in C:\DIM\OctRelease\eFC\src\src\eFC.Application\Common\ReportGenerator.cs:line 203 at eFC.BT.BTAppService.DownloadPdfAsync(DownloadPdfDto input) in C:\DIM\OctRelease\eFC\src\src\eFC.Application\BT\BTAppService.cs:line 780 at lambda_method4575(Closure, Object) at Microsoft.AspNetCore.Mvc.Infrastructure.ActionMethodExecutor.AwaitableObjectResultExecutor.Execute(ActionContext actionContext, IActionResultTypeMapper mapper, ObjectMethodExecutor executor, Object controller, Object[] arguments) at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeActionMethodAsync>g__Awaited|12_0(ControllerActionInvoker invoker, ValueTask1 actionResultValueTask)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeNextActionFilterAsync>g__Awaited|10_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Rethrow(ActionExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeInnerFilterAsync>g__Awaited|13_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextExceptionFilterAsync>g__Awaited|26_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
2026-04-13 14:27:07.103 +08:00 [ERR] An error occurred using a transaction.
2026-04-13 14:27:08.505 +08:00 [ERR] ---------- RemoteServiceErrorInfo ----------
{
"code": null,
"message": "An internal error occurred during your request!",
"details": null,
"data": {},
"validationErrors": null
}
[maliming] said: hi
You can enable the Debug log first and then reproduce the error and share logs
Set
.MinimumLevel.Debug()everywhere.var loggerConfiguration = new LoggerConfiguration() .MinimumLevel.Debug() .MinimumLevel.Override("Microsoft.EntityFrameworkCore", LogEventLevel.Warning) .Enrich.FromLogContext() .WriteTo.Async(c => c.File("Logs/logs.txt"))Thanks
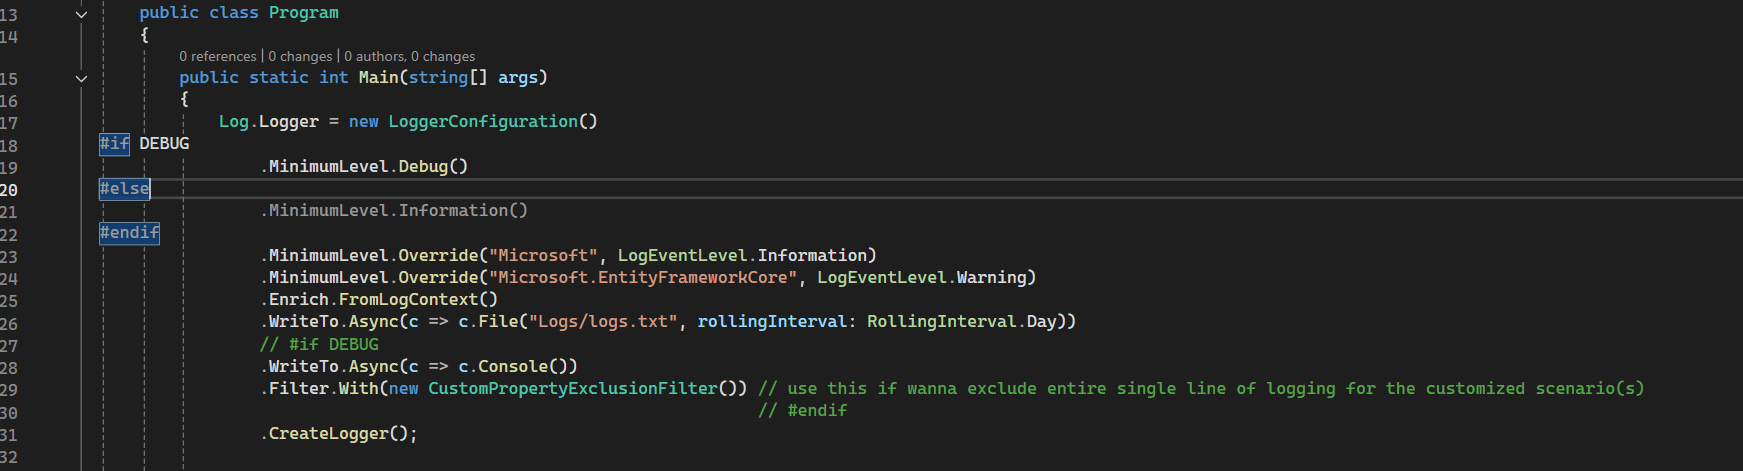
this is already there in my application, let me know if I need to add or remove anything else?
[maliming] said: hi
Can you share the full logs.txt file?
I will check the context logs.
liming.ma@volosoft.com
Thanks.
I copied the above text from logs file only.
[maliming] said: hi
We have recently increased permission for admin user but after adding the permission user started getting error
This error typically occurs only when there are too many claims (roles).
Can you share full debug logs?
https://abp.io/support/questions/8622/How-to-enable-Debug-logs-for-troubleshoot-problems
Thanks. 2026-01-29 10:41:53.140 +08:00 [ERR] SessionId is null. It's not possible to revoke the session during sign out.
sharing the log below, let me know if it works:
2026-01-29 14:30:52.586 +08:00 [ERR] SessionId is null. It's not possible to revoke the session during sign out.
2026-01-29 15:34:47.990 +08:00 [ERR] An unhandled exception has occurred while executing the request. Volo.Abp.UserFriendlyException: Cannot proceed because user is not allowed! at eFC.Web.Pages.Account.LoginCustomModel.OnGetExternalLoginCallbackAsync(String remoteError) in /work/3/49/s/src/src/eFC.Web/Pages/Account/LoginCustomModel.cshtml.cs:line 136 at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.ExecutorFactory.GenericTaskHandlerMethod.Convert[T](Object taskAsObject) at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.ExecutorFactory.GenericTaskHandlerMethod.Execute(Object receiver, Object[] arguments) at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.InvokeHandlerMethodAsync() at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.InvokeNextPageFilterAsync() at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.Rethrow(PageHandlerExecutedContext context) at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted) at Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.InvokeInnerFilterAsync() at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextExceptionFilterAsync>g__Awaited|26_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ExceptionContextSealed context) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextResourceFilter>g__Awaited|25_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ResourceExecutedContextSealed context) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeFilterPipelineAsync>g__Awaited|20_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Logged|17_1(ResourceInvoker invoker) at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Logged|17_1(ResourceInvoker invoker) at Microsoft.AspNetCore.Routing.EndpointMiddleware.<Invoke>g__AwaitRequestTask|7_0(Endpoint endpoint, Task requestTask, ILogger logger) at Volo.Abp.AspNetCore.Serilog.AbpSerilogMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at Volo.Abp.AspNetCore.Auditing.AbpAuditingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Volo.Abp.AspNetCore.Auditing.AbpAuditingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at Swashbuckle.AspNetCore.SwaggerUI.SwaggerUIMiddleware.Invoke(HttpContext httpContext) at Swashbuckle.AspNetCore.Swagger.SwaggerMiddleware.Invoke(HttpContext httpContext, ISwaggerProvider swaggerProvider) at Microsoft.AspNetCore.Authorization.AuthorizationMiddleware.Invoke(HttpContext context) at Microsoft.AspNetCore.Builder.ApplicationBuilderAbpOpenIddictMiddlewareExtension.<>c__DisplayClass0_0.<<UseAbpOpenIddictValidation>b__0>d.MoveNext() --- End of stack trace from previous location --- at Volo.Abp.AspNetCore.Uow.AbpUnitOfWorkMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at Volo.Abp.AspNetCore.ExceptionHandling.AbpExceptionHandlingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Volo.Abp.AspNetCore.ExceptionHandling.AbpExceptionHandlingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at eFC.Web.eFCWebModule.<>c.<<OnApplicationInitialization>b__15_1>d.MoveNext() in /work/3/49/s/src/src/eFC.Web/eFCWebModule.cs:line 475 --- End of stack trace from previous location --- at Volo.Abp.AspNetCore.MultiTenancy.MultiTenancyMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at Microsoft.AspNetCore.Builder.ApplicationBuilderAbpJwtTokenMiddlewareExtension.<>c__DisplayClass0_0.<<UseJwtTokenMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at Microsoft.AspNetCore.Authentication.AuthenticationMiddleware.Invoke(HttpContext context) at eFC.Web.eFCWebModule.<>c.<<OnApplicationInitialization>b__15_0>d.MoveNext() in /work/3/49/s/src/src/eFC.Web/eFCWebModule.cs:line 448 --- End of stack trace from previous location --- at Volo.Abp.AspNetCore.Tracing.AbpCorrelationIdMiddleware.InvokeAsync(HttpContext context, RequestDelegate next) at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext() --- End of stack trace from previous location --- at Microsoft.AspNetCore.Diagnostics.ExceptionHandlerMiddlewareImpl.<Invoke>g__Awaited|10_0(ExceptionHandlerMiddlewareImpl middleware, HttpContext context, Task task)
2026-01-29 15:37:43.018 +08:00 [ERR] ---------- RemoteServiceErrorInfo ---------- { "code": null, "message": "The data you have submitted has already changed by another user/client. Please discard the changes you've done and try from the beginning.", "details": null, "data": null, "validationErrors": null }
2026-01-29 15:37:43.018 +08:00 [ERR] The database operation was expected to affect 1 row(s), but actually affected 0 row(s); data may have been modified or deleted since entities were loaded. See https://go.microsoft.com/fwlink/?LinkId=527962 for information on understanding and handling optimistic concurrency exceptions.
Volo.Abp.Data.AbpDbConcurrencyException: The database operation was expected to affect 1 row(s), but actually affected 0 row(s); data may have been modified or deleted since entities were loaded. See https://go.microsoft.com/fwlink/?LinkId=527962 for information on understanding and handling optimistic concurrency exceptions.
---> Microsoft.EntityFrameworkCore.DbUpdateConcurrencyException: The database operation was expected to affect 1 row(s), but actually affected 0 row(s); data may have been modified or deleted since entities were loaded. See https://go.microsoft.com/fwlink/?LinkId=527962 for information on understanding and handling optimistic concurrency exceptions.
at Microsoft.EntityFrameworkCore.Update.AffectedCountModificationCommandBatch.ThrowAggregateUpdateConcurrencyExceptionAsync(RelationalDataReader reader, Int32 commandIndex, Int32 expectedRowsAffected, Int32 rowsAffected, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.Update.AffectedCountModificationCommandBatch.ConsumeResultSetWithRowsAffectedOnlyAsync(Int32 commandIndex, RelationalDataReader reader, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.Update.AffectedCountModificationCommandBatch.ConsumeAsync(RelationalDataReader reader, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.Update.ReaderModificationCommandBatch.ExecuteAsync(IRelationalConnection connection, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.Update.ReaderModificationCommandBatch.ExecuteAsync(IRelationalConnection connection, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.SqlServer.Update.Internal.SqlServerModificationCommandBatch.ExecuteAsync(IRelationalConnection connection, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.Update.Internal.BatchExecutor.ExecuteAsync(IEnumerable1 commandBatches, IRelationalConnection connection, CancellationToken cancellationToken) at Microsoft.EntityFrameworkCore.Update.Internal.BatchExecutor.ExecuteAsync(IEnumerable1 commandBatches, IRelationalConnection connection, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.Update.Internal.BatchExecutor.ExecuteAsync(IEnumerable1 commandBatches, IRelationalConnection connection, CancellationToken cancellationToken) at Microsoft.EntityFrameworkCore.ChangeTracking.Internal.StateManager.SaveChangesAsync(IList1 entriesToSave, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.ChangeTracking.Internal.StateManager.SaveChangesAsync(StateManager stateManager, Boolean acceptAllChangesOnSuccess, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.SqlServer.Storage.Internal.SqlServerExecutionStrategy.ExecuteAsync[TState,TResult](TState state, Func4 operation, Func4 verifySucceeded, CancellationToken cancellationToken)
at Microsoft.EntityFrameworkCore.DbContext.SaveChangesAsync(Boolean acceptAllChangesOnSuccess, CancellationToken cancellationToken)
at Volo.Abp.EntityFrameworkCore.AbpDbContext1.SaveChangesAsync(Boolean acceptAllChangesOnSuccess, CancellationToken cancellationToken) --- End of inner exception stack trace --- at Volo.Abp.EntityFrameworkCore.AbpDbContext1.SaveChangesAsync(Boolean acceptAllChangesOnSuccess, CancellationToken cancellationToken)
at Volo.Abp.Uow.UnitOfWork.SaveChangesAsync(CancellationToken cancellationToken)
at Volo.Abp.AspNetCore.Mvc.Uow.AbpUowActionFilter.SaveChangesAsync(ActionExecutingContext context, IUnitOfWorkManager unitOfWorkManager)
at Volo.Abp.AspNetCore.Mvc.Uow.AbpUowActionFilter.SaveChangesAsync(ActionExecutingContext context, IUnitOfWorkManager unitOfWorkManager)
at Volo.Abp.AspNetCore.Mvc.Uow.AbpUowActionFilter.OnActionExecutionAsync(ActionExecutingContext context, ActionExecutionDelegate next)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeNextActionFilterAsync>g__Awaited|10_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Rethrow(ActionExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeInnerFilterAsync>g__Awaited|13_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextExceptionFilterAsync>g__Awaited|26_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ExceptionContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextResourceFilter>g__Awaited|25_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ResourceExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeFilterPipelineAsync>g__Awaited|20_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Logged|17_1(ResourceInvoker invoker)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Logged|17_1(ResourceInvoker invoker)
at Microsoft.AspNetCore.Routing.EndpointMiddleware.<Invoke>g__AwaitRequestTask|7_0(Endpoint endpoint, Task requestTask, ILogger logger)
at Volo.Abp.AspNetCore.Serilog.AbpSerilogMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.InterfaceMiddlewareBinder.<>c__DisplayClass2_0.<<CreateMiddleware>b__0>d.MoveNext()
--- End of stack trace from previous location ---
at Volo.Abp.AspNetCore.Auditing.AbpAuditingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
[maliming] said: hi
SessionId is null. It's not possible to revoke the session during sign out.
Have you enabled the dynamic claims?
https://abp.io/docs/latest/modules/identity/session-management
Thanks.
No, this error can come if it is not enabled ?
[maliming] said: hi
We have recently increased permission for admin user but after adding the permission user started getting error
Did you add too many roles/claims to this admin user?
Thanks.
No, roles and permissions are almost same.
[maliming] said: hi
How many roles does your current user have? ABP will add all role names to claims(cookies)
Thanks.
Hi, I have multiple institution and for each institution "Institution Admin" role is there, right now I see approx. 35+ roles are there just for 1 user and in total in role table 120 rows are there.
also, we want to keep abpidentity roles by default as it is required to get permission, roles etc.
[maliming] said: hi
Have you restarted the website after changing the Web Config file?
Is there any 400 error in the app logs?
Can you share the full URL?
Thanks.
yes, I restarted, there is no 400 in logs, it's failing as header size is big. Below is the URL.
https://efc.devhealthgrp.com.sg/UAT/eFCApp/api/app/user/user-organization?userName=healthgrp%5Csim0886h