hi
The anonymous request to https://fa-api.xxx.net.tr/api/app/viop-contracts/client-pack will also get 500 error.
Maybe it is unrelated to the access token. What are the error logs?
Thanks.
Problem solved. You have to run the autuServer and api.host websites at same time
https://us05web.zoom.us/j/86720672155?pwd=DPgvKTFXRsq67U94YKvaTuzSYRAUyR.1
hi
Can you join the zoom?
I want to check it remotely.
hi
I have shared project via email. You can test it.
Can you share again via https://wetransfer.com/
Thanks.
hi
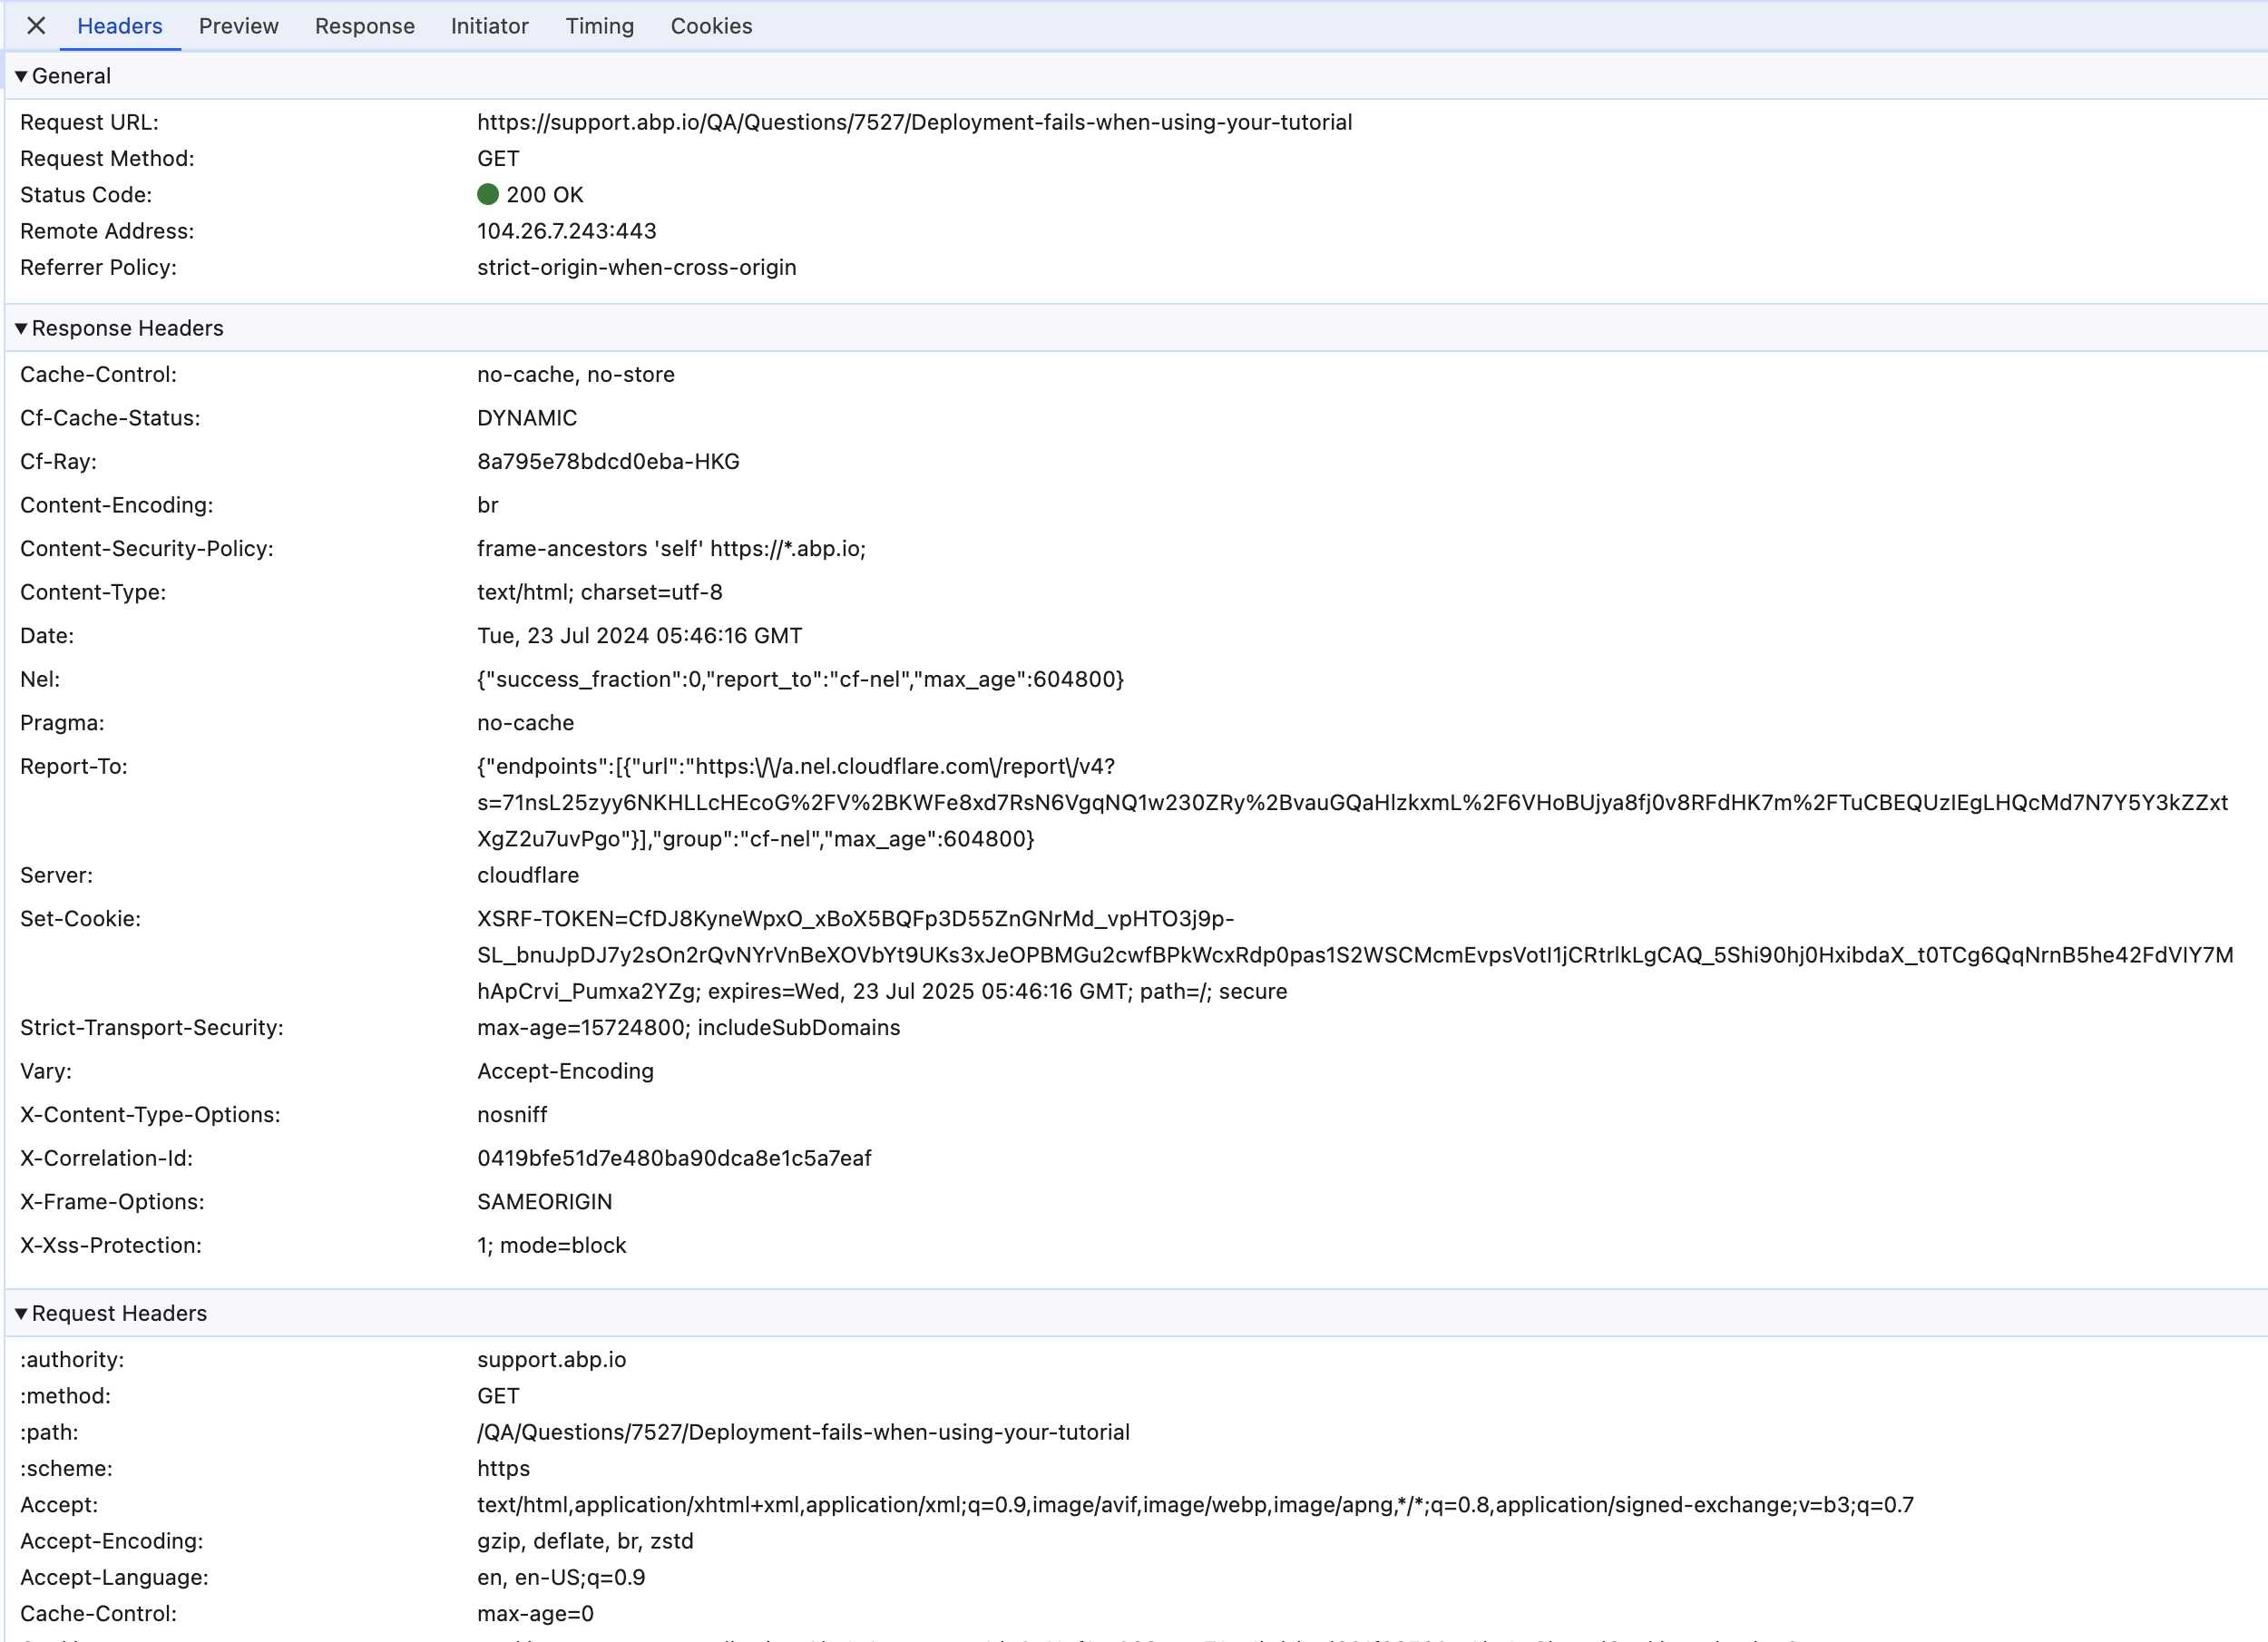
I mean the full request and response info include the headers.
And do you have an online angular URL so I can see the cors error?
Thanks.
By the way, you can try to override the IdentitySessionManager in your Aizanoi.AuthServer project.
using System;
using System.Threading.Tasks;
using Microsoft.Extensions.Logging;
using Volo.Abp.Caching;
using Volo.Abp.Identity.Settings;
using Volo.Abp.Settings;
using Volo.Abp.Uow;
using Volo.Abp.Users;

namespace Volo.Abp.Identity.Pro.DemoApp;

public class MyIdentitySessionManager : IdentitySessionManager
{
    protected IUnitOfWorkManager UnitOfWorkManager { get; }

    public MyIdentitySessionManager(
        IIdentitySessionRepository identitySessionRepository,
        ICurrentUser currentUser, IDistributedCache<IdentitySessionCacheItem> cache,
        ISettingProvider settingProvider,
        IdentityDynamicClaimsPrincipalContributorCache identityDynamicClaimsPrincipalContributorCache,
        IUnitOfWorkManager unitOfWorkManager)
        : base(identitySessionRepository, currentUser, cache, settingProvider, identityDynamicClaimsPrincipalContributorCache)
    {
        UnitOfWorkManager = unitOfWorkManager;
    }

    public async override Task<IdentitySession> CreateAsync(string sessionId, string device, string deviceInfo, Guid userId, Guid? tenantId, string clientId, string ipAddresses)
    {
        Check.NotNullOrWhiteSpace(sessionId, nameof(sessionId));
        Check.NotNullOrWhiteSpace(device, nameof(device));

        var session = await IdentitySessionRepository.FindAsync(sessionId);
        if (session == null)
        {
            using (var uow = UnitOfWorkManager.Begin(requiresNew: true))
            {
                Logger.LogInformation($"Creating identity session for session id: {sessionId}, device: {device}, user id: {userId}, tenant id: {tenantId}, client id: {clientId}");
                session = await IdentitySessionRepository.InsertAsync(new IdentitySession(
                    GuidGenerator.Create(),
                    sessionId,
                    device,
                    deviceInfo,
                    userId,
                    tenantId,
                    clientId,
                    ipAddresses,
                    Clock.Now
                ));

                await uow.SaveChangesAsync();
            }
        }

        var preventConcurrentLoginBehaviour = await IdentityProPreventConcurrentLoginBehaviourSettingHelper.Get(SettingProvider);
        switch (preventConcurrentLoginBehaviour)
        {
            case IdentityProPreventConcurrentLoginBehaviour.LogoutFromSameTypeDevices:
                await RevokeAllAsync(userId, device, session.Id);
                break;

            case IdentityProPreventConcurrentLoginBehaviour.LogoutFromAllDevices:
                await RevokeAllAsync(userId, session.Id);
                break;
        }

        return session;
    }
}
hi
I can log successfully on the https://fa.fintechxxx.net.tr/ website without any exception.
But the logs you shared show the following:
An error occurred using a transaction.
The request was aborted by the client.
Could not find a session
Does this happen every time?
hi
In blazor wasm module.
private static void ConfigureAuthentication(WebAssemblyHostBuilder builder)
{
    builder.Services.AddOidcAuthentication(options =>
    {
        builder.Configuration.Bind("AuthServer", options.ProviderOptions);
        options.UserOptions.NameClaim = OpenIddictConstants.Claims.Name;
        options.UserOptions.RoleClaim = OpenIddictConstants.Claims.Role;

        options.ProviderOptions.DefaultScopes.Add("MyProjectName");
        options.ProviderOptions.DefaultScopes.Add("roles");
        options.ProviderOptions.DefaultScopes.Add("email");
        options.ProviderOptions.DefaultScopes.Add("phone");
    });

    builder.Services.AddAuthorizationCore(options =>
    {
        options.AddPolicy("TenantPolicy", policy =>
        {
            policy.RequireAuthenticatedUser().RequireAssertion(handlerContext =>
            {
                var userId = handlerContext.User.FindUserId();
                Console.WriteLine($"****** UserId: {userId} ******");

                var tenantId = handlerContext.User.FindTenantId();
                Console.WriteLine($"****** TenantId: {tenantId} ******");
                return true; // false to skip
            });
        });
    });
}
Index.razor of blazor wasm project
@attribute [Authorize(policy: "TenantPolicy")]
Output:
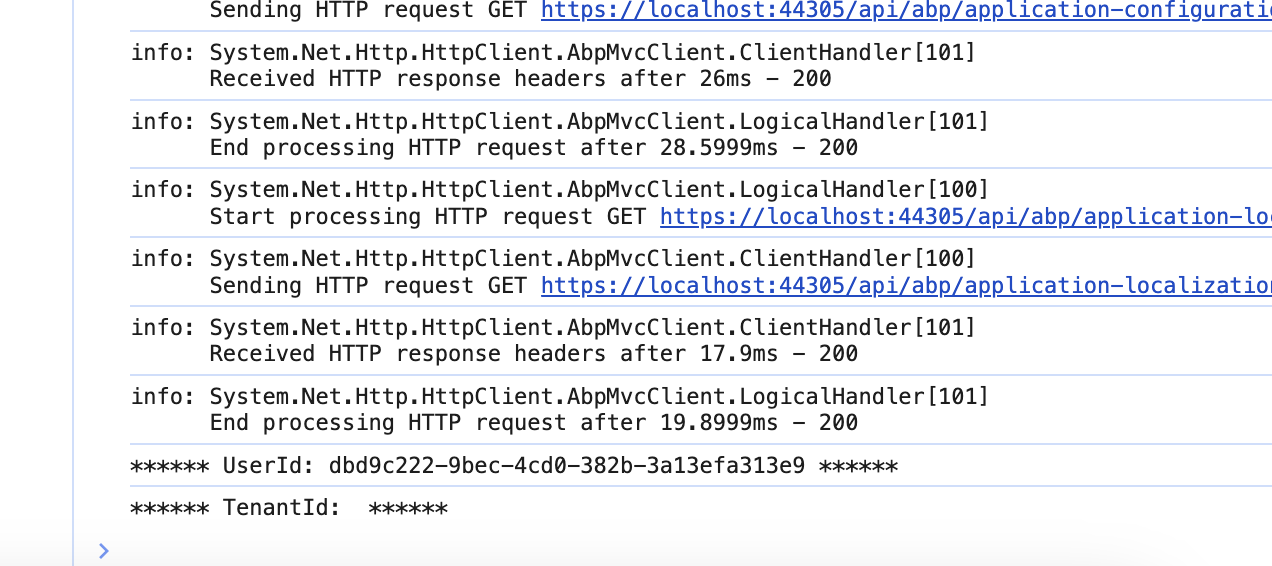
hi
The logs show that the cors check is successful.
Do you have an online angular URL so I can see the cors error?
Or please share the HTTP request and response of the https://localhost:44371/api/abp/application-configuration , you can view them in Chrome dev-tool.




