Hi maliming,
Thank you for the details you provided.
You can consider this ticket closed.
Best regards, Stefano
Hi maliming,
Thanks for your reply.
Yesterday I tried making the change AI-Bot suggested:
options.SaveTokens = false;
and the app worked again.
Regarding your question #1 (Roughly how many roles is this user assigned to?), the issue is that **all **the application users (about a hundred) were unable to log in.
Regarding your question #2, it's possible that users were assigned roles and/or permissions, but only through the application interface.
It should be noted that the code for managing roles, permissions, and claims does not vary from the standard ABP template on which the application is built.
In any case, at the moment and with that change the application is back to working for all users.
Best regards, Stefano
Hi,
Could it be that I need to enable Websockets in the Azure App?

Hi,
It looks like the request is not going through:

Stefano
Hi,
Unfortunately, I can't because the client environment is private and accessible with Okta authentication.
I can share sections of code with you or I can share the screen with you in a private call.
Stefano
Hi,
With this change, everything seems to work. Thanks for the support.
Stefano
Hi,
I sent you the files with WeTransfer.
I tried accessing the protected /Identity/Users page, which triggers a loop on the Okta login page.
Stefano
Hi,
no, no 502 error now. This is the log from login on wards:
2025-12-16 07:48:14.294 +00:00 [INF] Executing endpoint '/Account/Login'
2025-12-16 07:48:14.294 +00:00 [INF] Route matched with {page = "/Account/Login", area = "", action = "", controller = ""}. Executing page /Account/Login
2025-12-16 07:48:14.294 +00:00 [INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
2025-12-16 07:48:14.304 +00:00 [INF] Executing handler method Volo.Abp.Account.Public.Web.Pages.Account.LoginModel.OnPostExternalLogin - ModelState is "Invalid"
2025-12-16 07:48:14.937 +00:00 [INF] Executed handler method OnPostExternalLogin, returned result Microsoft.AspNetCore.Mvc.ChallengeResult.
2025-12-16 07:48:14.939 +00:00 [INF] Executing ChallengeResult with authentication schemes (["Okta"]).
2025-12-16 07:48:15.380 +00:00 [INF] AuthenticationScheme: Okta was challenged.
2025-12-16 07:48:15.382 +00:00 [INF] Executed page /Account/Login in 1087.6731ms
2025-12-16 07:48:15.382 +00:00 [INF] Executed endpoint '/Account/Login'
2025-12-16 07:48:15.823 +00:00 [INF] Request finished HTTP/1.1 POST https://webap-fbteammanagement-we1-int.azurewebsites.net/Account/Login?handler=ExternalLogin - 302 null null 1543.6053ms
2025-12-16 07:48:28.052 +00:00 [INF] Request starting HTTP/1.1 POST https://webap-fbteammanagement-we1-int.azurewebsites.net/signin-azuread-oidc - application/x-www-form-urlencoded 573
2025-12-16 07:48:28.298 +00:00 [INF] AuthenticationScheme: Identity.External signed in.
2025-12-16 07:48:28.299 +00:00 [INF] Request finished HTTP/1.1 POST https://webap-fbteammanagement-we1-int.azurewebsites.net/signin-azuread-oidc - 302 null null 247.0339ms
2025-12-16 07:48:28.385 +00:00 [INF] Request starting HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Account/Login?handler=ExternalLoginCallback - null null
2025-12-16 07:48:28.388 +00:00 [INF] Executing endpoint '/Account/Login'
2025-12-16 07:48:28.388 +00:00 [INF] Route matched with {page = "/Account/Login", area = "", action = "", controller = ""}. Executing page /Account/Login
2025-12-16 07:48:28.388 +00:00 [INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
2025-12-16 07:48:28.390 +00:00 [INF] Executing handler method Volo.Abp.Account.Public.Web.Pages.Account.LoginModel.OnGetExternalLoginCallbackAsync - ModelState is "Valid"
2025-12-16 07:48:29.253 +00:00 [INF] AuthenticationScheme: Identity.External signed out.
2025-12-16 07:48:29.881 +00:00 [INF] AuthenticationScheme: Identity.Application signed in.
2025-12-16 07:48:30.289 +00:00 [INF] Executed handler method OnGetExternalLoginCallbackAsync, returned result Microsoft.AspNetCore.Mvc.RedirectResult.
2025-12-16 07:48:30.339 +00:00 [INF] Executing RedirectResult, redirecting to /.
2025-12-16 07:48:30.340 +00:00 [INF] Executed page /Account/Login in 1951.7486ms
2025-12-16 07:48:30.340 +00:00 [INF] Executed endpoint '/Account/Login'
2025-12-16 07:48:30.345 +00:00 [INF] Request finished HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Account/Login?handler=ExternalLoginCallback - 302 null null 1960.6185ms
2025-12-16 07:48:30.443 +00:00 [INF] Request starting HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/ - null null
2025-12-16 07:48:30.446 +00:00 [INF] Executing endpoint '/Index'
2025-12-16 07:48:30.446 +00:00 [INF] Route matched with {page = "/Index", area = "", action = "", controller = ""}. Executing page /Index
2025-12-16 07:48:30.446 +00:00 [INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
2025-12-16 07:48:30.446 +00:00 [INF] Executing an implicit handler method - ModelState is "Valid"
2025-12-16 07:48:30.447 +00:00 [INF] Executed an implicit handler method, returned result Microsoft.AspNetCore.Mvc.RazorPages.PageResult.
2025-12-16 07:48:30.513 +00:00 [INF] Executed page /Index in 66.8962ms
2025-12-16 07:48:30.513 +00:00 [INF] Executed endpoint '/Index'
2025-12-16 07:48:30.516 +00:00 [INF] Request finished HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/ - 200 null text/html; charset=utf-8 73.4385ms
2025-12-16 07:48:31.011 +00:00 [INF] Request starting HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Abp/ApplicationConfigurationScript - null null
2025-12-16 07:48:31.015 +00:00 [INF] Executing endpoint 'Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationScriptController.Get (Volo.Abp.AspNetCore.Mvc)'
2025-12-16 07:48:31.015 +00:00 [INF] Route matched with {area = "Abp", action = "Get", controller = "AbpApplicationConfigurationScript", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.ActionResult] Get() on controller Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationScriptController (Volo.Abp.AspNetCore.Mvc).
2025-12-16 07:48:31.019 +00:00 [INF] Executing action method Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationScriptController.Get (Volo.Abp.AspNetCore.Mvc) - Validation state: "Valid"
2025-12-16 07:48:31.118 +00:00 [INF] Executed action method Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationScriptController.Get (Volo.Abp.AspNetCore.Mvc), returned result Microsoft.AspNetCore.Mvc.ContentResult in 98.7067ms.
2025-12-16 07:48:31.118 +00:00 [INF] Executing ContentResult with HTTP Response ContentType of application/javascript
2025-12-16 07:48:31.118 +00:00 [INF] Executed action Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationScriptController.Get (Volo.Abp.AspNetCore.Mvc) in 103.3587ms
2025-12-16 07:48:31.119 +00:00 [INF] Executed endpoint 'Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.AbpApplicationConfigurationScriptController.Get (Volo.Abp.AspNetCore.Mvc)'
2025-12-16 07:48:31.120 +00:00 [INF] Request finished HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Abp/ApplicationConfigurationScript - 200 4668 application/javascript 109.1082ms
2025-12-16 07:48:31.134 +00:00 [INF] Request starting HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Abp/ServiceProxyScript - null null
2025-12-16 07:48:31.137 +00:00 [INF] Executing endpoint 'Volo.Abp.AspNetCore.Mvc.ProxyScripting.AbpServiceProxyScriptController.GetAll (Volo.Abp.AspNetCore.Mvc)'
2025-12-16 07:48:31.137 +00:00 [INF] Route matched with {area = "Abp", action = "GetAll", controller = "AbpServiceProxyScript", page = ""}. Executing controller action with signature Microsoft.AspNetCore.Mvc.ActionResult GetAll(Volo.Abp.AspNetCore.Mvc.ProxyScripting.ServiceProxyGenerationModel) on controller Volo.Abp.AspNetCore.Mvc.ProxyScripting.AbpServiceProxyScriptController (Volo.Abp.AspNetCore.Mvc).
2025-12-16 07:48:31.139 +00:00 [INF] Executing action method Volo.Abp.AspNetCore.Mvc.ProxyScripting.AbpServiceProxyScriptController.GetAll (Volo.Abp.AspNetCore.Mvc) - Validation state: "Valid"
2025-12-16 07:48:31.149 +00:00 [INF] Executed action method Volo.Abp.AspNetCore.Mvc.ProxyScripting.AbpServiceProxyScriptController.GetAll (Volo.Abp.AspNetCore.Mvc), returned result Microsoft.AspNetCore.Mvc.ContentResult in 10.4597ms.
2025-12-16 07:48:31.149 +00:00 [INF] Executing ContentResult with HTTP Response ContentType of application/javascript
2025-12-16 07:48:31.150 +00:00 [INF] Executed action Volo.Abp.AspNetCore.Mvc.ProxyScripting.AbpServiceProxyScriptController.GetAll (Volo.Abp.AspNetCore.Mvc) in 12.5865ms
2025-12-16 07:48:31.150 +00:00 [INF] Executed endpoint 'Volo.Abp.AspNetCore.Mvc.ProxyScripting.AbpServiceProxyScriptController.GetAll (Volo.Abp.AspNetCore.Mvc)'
2025-12-16 07:48:31.151 +00:00 [INF] Request starting HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Abp/ApplicationLocalizationScript?cultureName=it - null null
2025-12-16 07:48:31.153 +00:00 [INF] Executing endpoint 'Volo.Abp.AspNetCore.Mvc.Localization.AbpApplicationLocalizationScriptController.GetAsync (Volo.Abp.AspNetCore.Mvc)'
2025-12-16 07:48:31.153 +00:00 [INF] Route matched with {area = "Abp", action = "Get", controller = "AbpApplicationLocalizationScript", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.ActionResult] GetAsync(Volo.Abp.AspNetCore.Mvc.ApplicationConfigurations.ApplicationLocalizationRequestDto) on controller Volo.Abp.AspNetCore.Mvc.Localization.AbpApplicationLocalizationScriptController (Volo.Abp.AspNetCore.Mvc).
2025-12-16 07:48:31.155 +00:00 [INF] Executing action method Volo.Abp.AspNetCore.Mvc.Localization.AbpApplicationLocalizationScriptController.GetAsync (Volo.Abp.AspNetCore.Mvc) - Validation state: "Valid"
2025-12-16 07:48:31.166 +00:00 [INF] Executed action method Volo.Abp.AspNetCore.Mvc.Localization.AbpApplicationLocalizationScriptController.GetAsync (Volo.Abp.AspNetCore.Mvc), returned result Microsoft.AspNetCore.Mvc.ContentResult in 11.1844ms.
2025-12-16 07:48:31.166 +00:00 [INF] Executing ContentResult with HTTP Response ContentType of application/javascript
2025-12-16 07:48:31.167 +00:00 [INF] Executed action Volo.Abp.AspNetCore.Mvc.Localization.AbpApplicationLocalizationScriptController.GetAsync (Volo.Abp.AspNetCore.Mvc) in 13.4191ms
2025-12-16 07:48:31.167 +00:00 [INF] Executed endpoint 'Volo.Abp.AspNetCore.Mvc.Localization.AbpApplicationLocalizationScriptController.GetAsync (Volo.Abp.AspNetCore.Mvc)'
2025-12-16 07:48:31.177 +00:00 [INF] Request finished HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Abp/ServiceProxyScript - 200 48073 application/javascript 43.2564ms
2025-12-16 07:48:31.178 +00:00 [INF] Request finished HTTP/1.1 GET https://webap-fbteammanagement-we1-int.azurewebsites.net/Abp/ApplicationLocalizationScript?cultureName=it - 200 125379 application/javascript 26.1949ms
Hi,
I checked all the settings and developed a test program to isolate the issue, which isn't an Azure environment problem. The following code is written with pure ASP.NET Core 9 and works perfectly (it uses Okta authentication):
using Microsoft.AspNetCore.Authentication;
using Microsoft.AspNetCore.Authentication.Cookies;
using Microsoft.AspNetCore.Authentication.OpenIdConnect;
using Microsoft.IdentityModel.Protocols.OpenIdConnect;
var builder = WebApplication.CreateBuilder(args);
builder.Services.AddControllersWithViews();
builder.Services.AddAuthentication(options =>
{
    options.DefaultScheme = CookieAuthenticationDefaults.AuthenticationScheme;
    options.DefaultChallengeScheme = "Okta";
})
.AddCookie(CookieAuthenticationDefaults.AuthenticationScheme)
.AddOpenIdConnect("Okta", options =>
{
    options.Authority = "https://myauthentication.okta.com/oauth2/default";
    options.ClientId = "MyClientId";
    options.ClientSecret = "MyClientSecret";
    options.CallbackPath = "/signin-azuread-oidc";
    options.ResponseType = OpenIdConnectResponseType.Code;
    options.MapInboundClaims = false;
    options.Scope.Add("email");
    options.Events = new OpenIdConnectEvents
    {
        OnRedirectToIdentityProvider = redirectContext =>
        {
            redirectContext.ProtocolMessage.RedirectUri = "https://int-fbteammgmt.lpl-cloud.com/signin-azuread-oidc";
            return Task.CompletedTask;
        }
    };
    options.AdditionalAuthorizationParameters["prompt"] = "login";
});
var app = builder.Build();
if (!app.Environment.IsDevelopment())
{
    app.UseExceptionHandler("/Home/Error");
    app.UseHsts();
}
app.UseStaticFiles();
app.UseRouting();
app.UseAuthentication();
app.UseAuthorization();
app.MapGet("/login", async (HttpContext ctx) =>
{
    await ctx.ChallengeAsync("Okta", new AuthenticationProperties
    {
        RedirectUri = "/Home/Secure"
    });
});
app.MapGet("/logout", async (HttpContext ctx) =>
{
    await ctx.SignOutAsync(CookieAuthenticationDefaults.AuthenticationScheme);
    ctx.Response.Redirect("/");
});
app.MapControllerRoute(
    name: "default",
    pattern: "{controller=Home}/{action=Index}/{id?}");
app.Run();
This is my page after logging in:
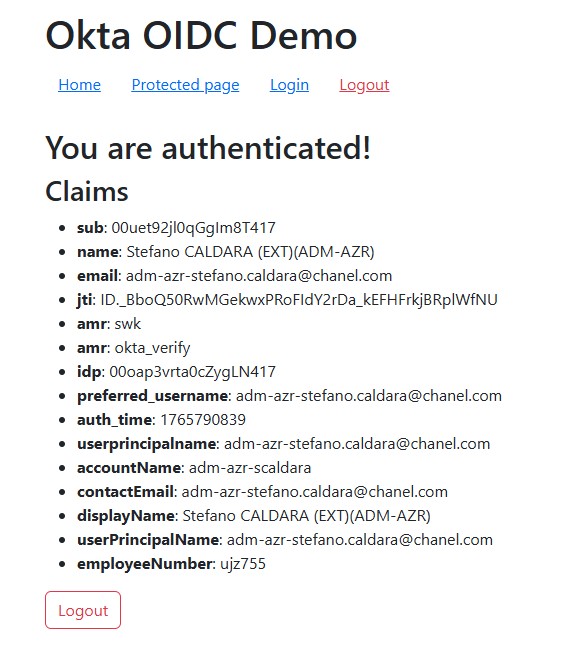 However, if I insert this code into the ConfigureExternalProviders method of a standard abp template created by abp studio:
private void ConfigureExternalProviders(ServiceConfigurationContext context)
{
    context.Services.AddAuthentication(options =>
    {
        options.DefaultScheme = CookieAuthenticationDefaults.AuthenticationScheme;
        options.DefaultChallengeScheme = "Okta";
        options.DefaultSignOutScheme = "Okta";
    })
    .AddCookie(CookieAuthenticationDefaults.AuthenticationScheme)
    .AddOpenIdConnect("Okta", options =>
    {
        options.Authority = "https://myauthentication.okta.com/oauth2/default";
        options.ClientId = "MyClientId";
        options.ClientSecret = "MyClientSecret";
        options.CallbackPath = "/signin-azuread-oidc";

        options.ResponseType = OpenIdConnectResponseType.Code;
        options.MapInboundClaims = false;
        options.Scope.Add("email");

        options.Events = new OpenIdConnectEvents
        {
            OnRedirectToIdentityProvider = redirectContext =>
            {
                redirectContext.ProtocolMessage.RedirectUri = "https://int-fbteammgmt.lpl-cloud.com/signin-azuread-oidc";
                return Task.CompletedTask;
            }
        };
    });
}
The result I get is that the login is successful, the application returns to the home page but the protected pages are not displayed, as if the user was not authenticated by abp:
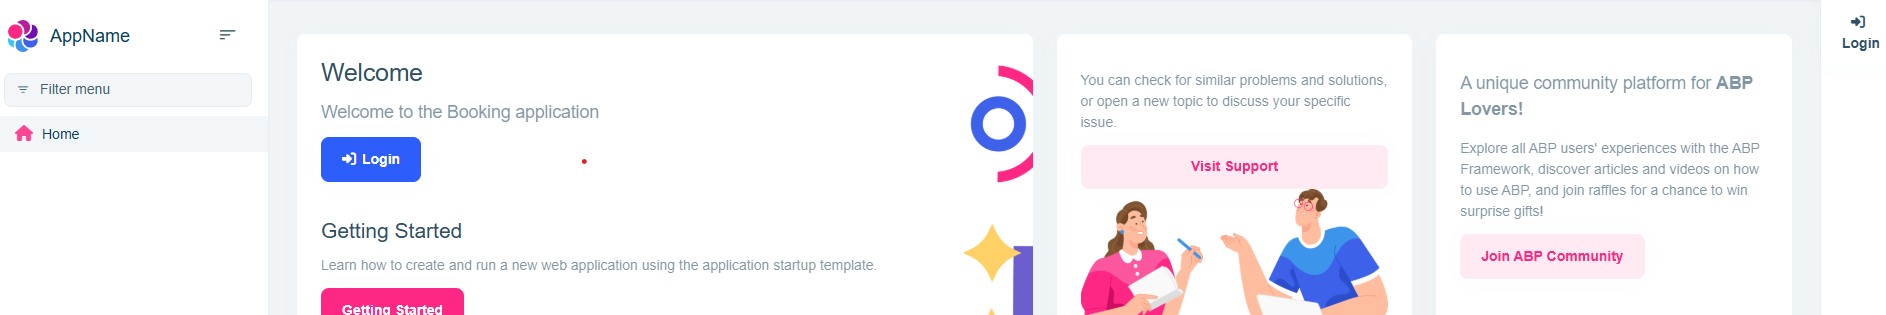
Please note that to ensure you are working in an identical environment, both applications are published to the same Azure Application. Please urgently provide me with the information needed to properly configure abp.
Stefano




