hi
We will give a solution soon. : )
hi
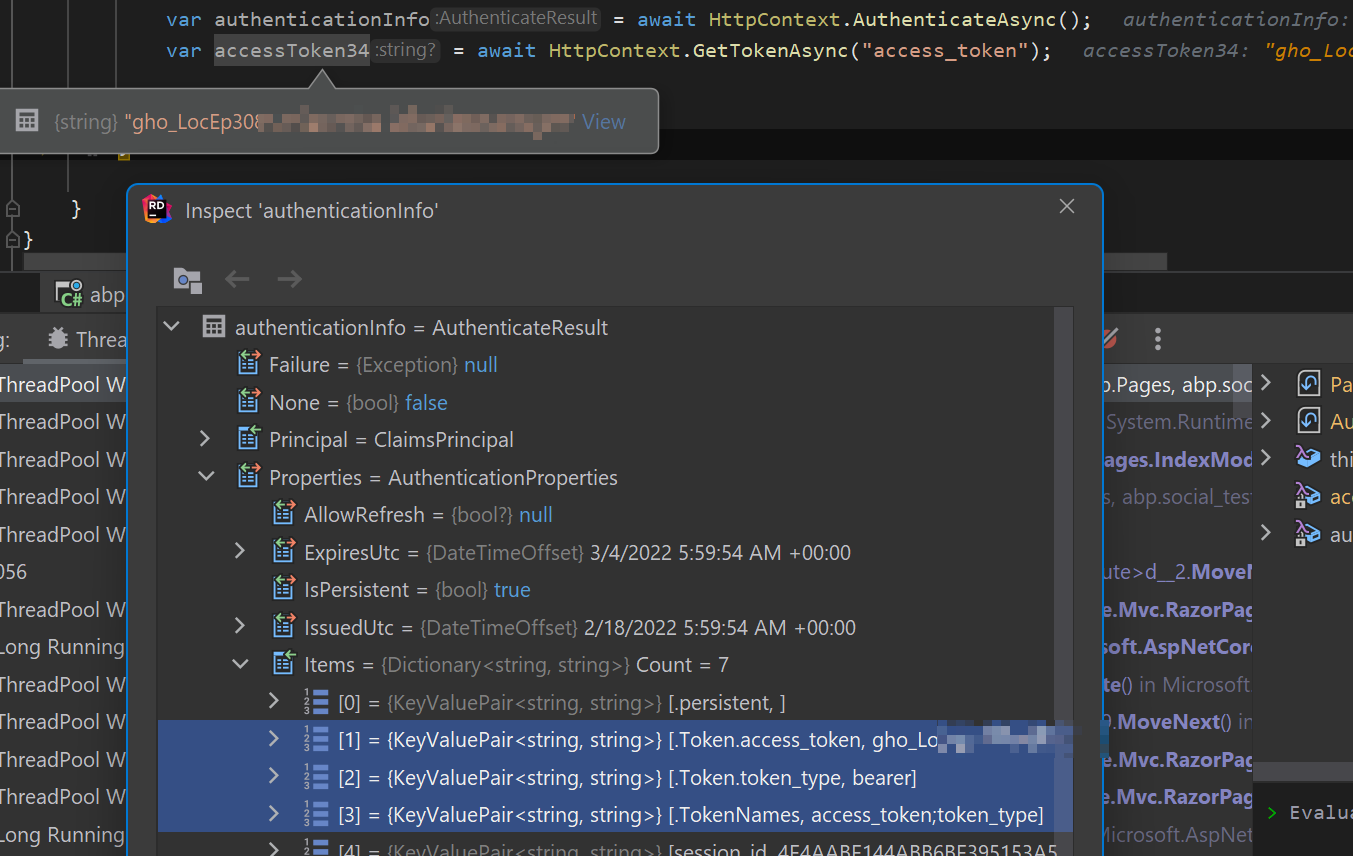
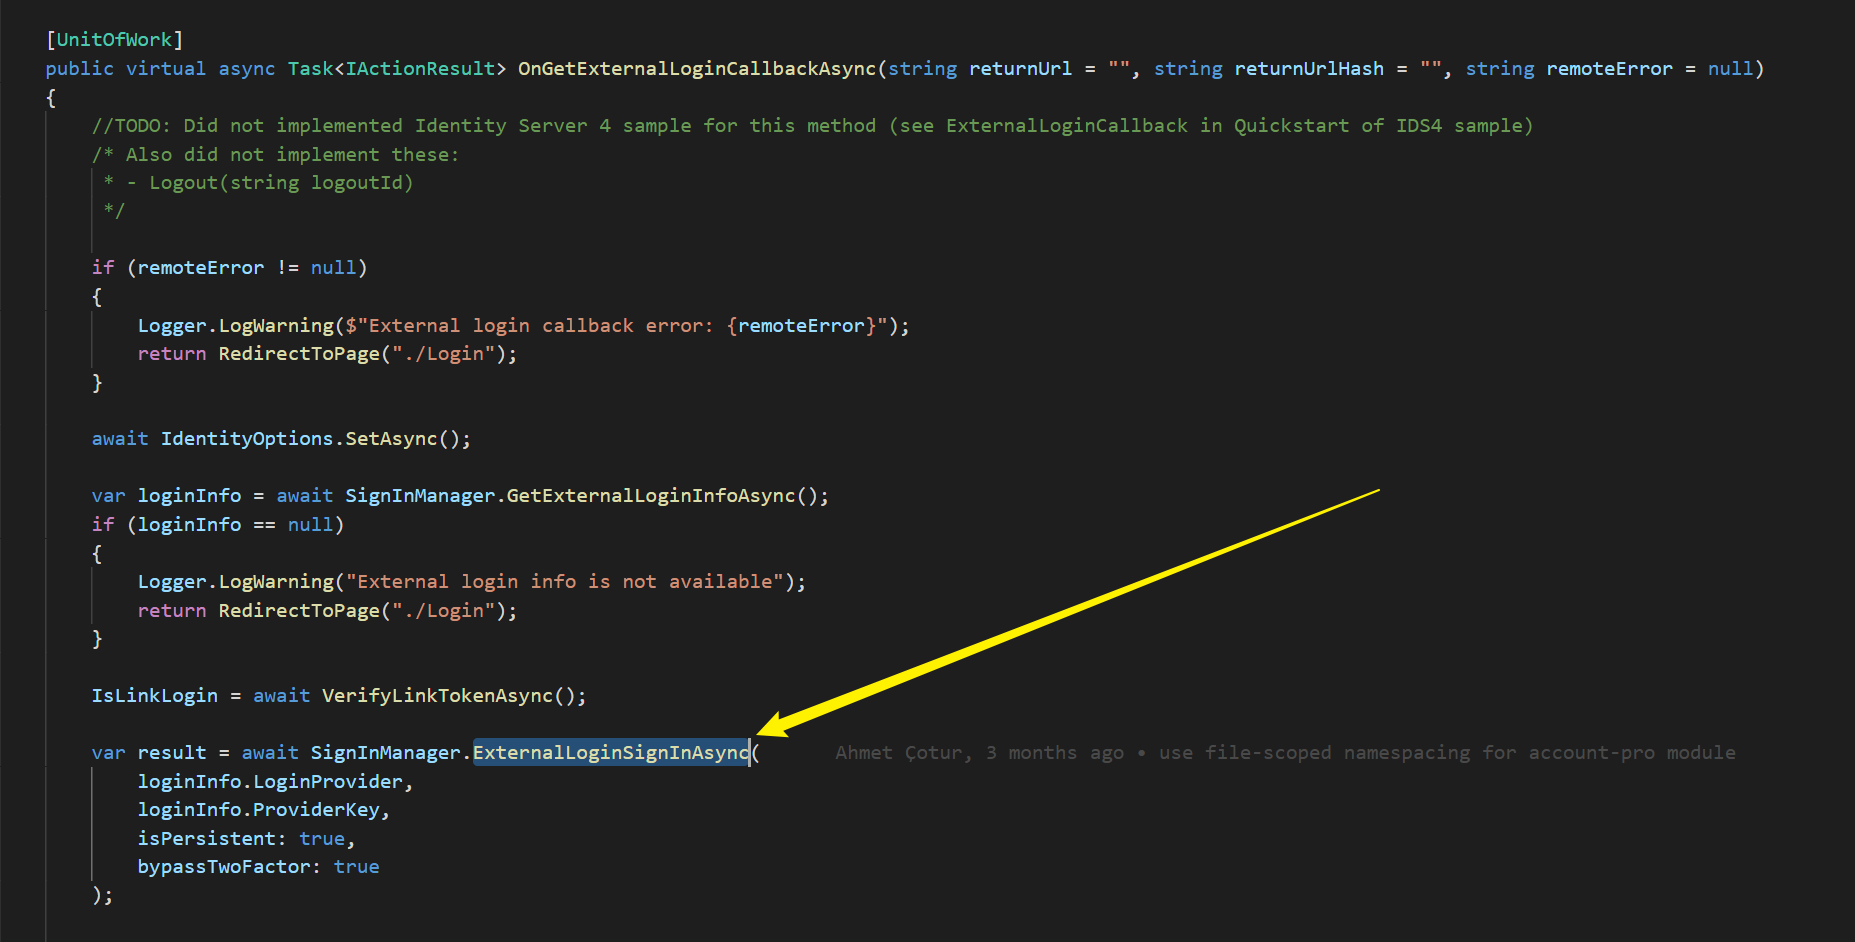
Here is a solution that copy tokens from IdentityConstants.ExternalScheme to IdentityConstants.ApplicationScheme
.AddGitHub(options =>
{
    options.ClientId = "bdcc3";
    options.ClientSecret = "32e3";

    options.SaveTokens = true;

    options.ClaimActions.Remove(ClaimTypes.Email);
    options.ClaimActions.MapJsonKey(AbpClaimTypes.Email, "email");
})


using System.Threading.Tasks;
using AspNet.Security.OAuth.GitHub;
using Microsoft.AspNetCore.Authentication;
using Microsoft.AspNetCore.Http;
using Microsoft.AspNetCore.Identity;
using Microsoft.Extensions.DependencyInjection;
using Microsoft.Extensions.Logging;
using Microsoft.Extensions.Options;
using Volo.Abp.DependencyInjection;
using IdentityUser = Volo.Abp.Identity.IdentityUser;

namespace abp.social_test.Web;

[Dependency(ServiceLifetime.Transient, ReplaceServices = true)]
[ExposeServices(typeof(SignInManager<IdentityUser>))]
public class MySignInManager : SignInManager<IdentityUser>
{
    public MySignInManager(Microsoft.AspNetCore.Identity.UserManager<IdentityUser> userManager,
        IHttpContextAccessor contextAccessor,
        Microsoft.AspNetCore.Identity.IUserClaimsPrincipalFactory<IdentityUser> claimsFactory,
        IOptions<IdentityOptions> optionsAccessor, ILogger<SignInManager<IdentityUser>> logger,
        IAuthenticationSchemeProvider schemes, IUserConfirmation<IdentityUser> confirmation) : base(userManager,
        contextAccessor, claimsFactory, optionsAccessor, logger, schemes, confirmation)
    {
    }

    public override async Task SignInAsync(IdentityUser user, AuthenticationProperties authenticationProperties,
        string authenticationMethod = null)
    {
        if (authenticationMethod == GitHubAuthenticationDefaults.AuthenticationScheme) // is github external login
        {
            var githubAuthenticateResult = await Context.AuthenticateAsync(IdentityConstants.ExternalScheme);
            if (githubAuthenticateResult.Succeeded)
            {
                if (githubAuthenticateResult.Properties != null)
                {
                    authenticationProperties.StoreTokens(githubAuthenticateResult.Properties.GetTokens());
                }
            }
        }

        await base.SignInAsync(user, authenticationProperties, authenticationMethod);
    }
}
hi
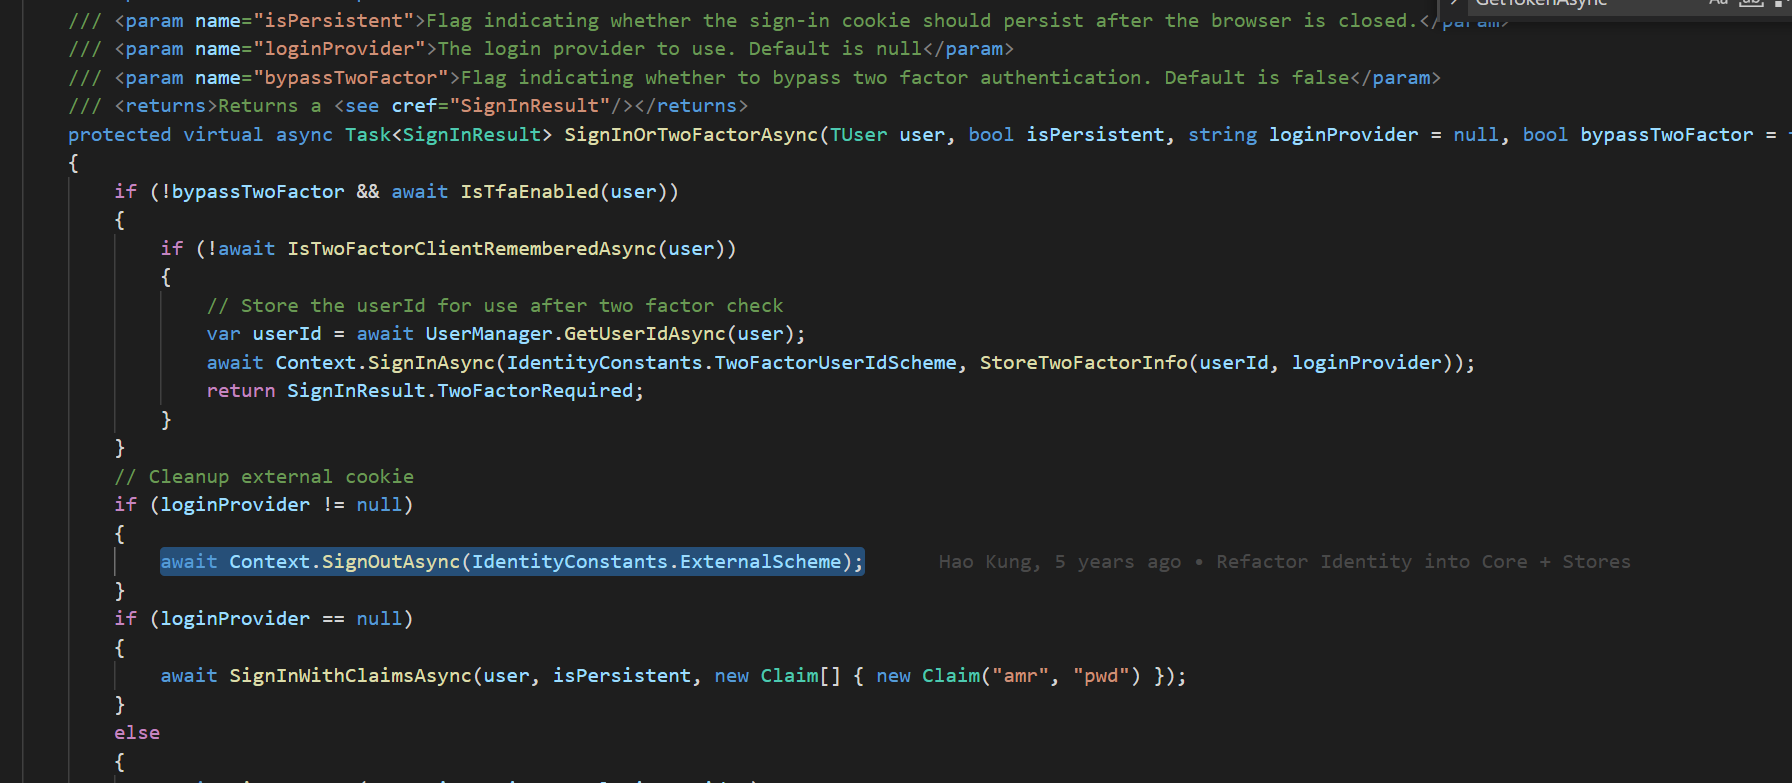
The ASP NET Core Identity cleans up the external cookie which includes the access_token etc.
This is Microsoft Design.
Now i have make changes in ABPSetting value like (manually set "enabled" as false)
The application use cache, You can't change settings manually, Please change it via the app, or clear the cache after changing DB.
You are right, We will review it.
Added to the internal work plan.
OK, We will further improve it in the future.
hi
You may need to wait for this PR released. https://github.com/abpframework/abp/pull/11551
OK, I will feedback to the SUITE team.
hi
I will check this. Thanks




