- Remove sensitive data from the payload if it is not required - Not sure if this is possible and application will work
- Instead of placing sensitive data in the payload, use an indirect object reference which is resolved on the server side - Not sure if this is possible and application will work
You can remove some claims from the Factory.
https://github.com/abpframework/abp/blob/dev/modules/identityserver/src/Volo.Abp.IdentityServer.Domain/Volo/Abp/IdentityServer/AspNetIdentity/AbpUserClaimsFactory.cs https://github.com/abpframework/abp/blob/dev/modules/identity/src/Volo.Abp.Identity.Domain/Volo/Abp/Identity/AbpUserClaimsPrincipalFactory.cs https://docs.abp.io/en/abp/latest/Authorization#claims-principal-factory
3.Encrypt the JWT payload using the JSON web encryption (JWE) scheme 4.Encrypt sensitive data within the JWT payload using a custom process.
I found some discuss about this.
https://github.com/DureSameen/IdentityServer4.JWE
i even tried return true alwas but no luck.
What's is results now?
https://samesite-sandbox.glitch.me/
Can you share your website url and user&password with me? liming.ma@volosoft.com
hi
I can't think of any possible reasons, we have followed Microsoft's documentation.
Can you try to use redis backplane in non-abp applications?
You should implement the IMultiTenant interface for your entities to make them multi-tenancy ready.
https://docs.abp.io/en/abp/latest/Multi-Tenancy
See https://github.com/abpframework/abp/pull/7509
The entity inherits IMultiTenant which means it is multi-tenant, and will try to get the connection string of the tenant.
hi
It is currently impossible. : )
is it correct behavior? When it needs to be triggered??
For instance, current tenant's company have bound licences, each of licence determines which UI pages ("modules") are accessible for current user.
You can create some permissions, Don't grant to users or user roles. Then your custom PermissionValueProvider will be triggered.
You can check the current tenant's company licences to return true or false, angular will show/hide the menu according to this value.
https://docs.abp.io/en/abp/latest/Authorization#advanced-topics
For 1 request it asks to resolve AbpPermissionManagement, AbpAuditLogging on the 2nd request it Asks to resolve only AbpAuditLogging for the same page request.
I think this is because the Permissions are cached. So we don't need read it from db for 2nd request.
So according the the code behaviour It should try to resolve connection string for ProductManagement and Intelligence. But it only tries to resolve ProductManagement.
It will only be triggered when Intelligence-related repositories are used and the _currentTenant.Id not be null.
Your entity also need IsMultiTenant
https://github.com/abpframework/abp/blob/c4e92a3431787b1a6727a615768a7a2906a9ba69/framework/src/Volo.Abp.EntityFrameworkCore/Volo/Abp/Domain/Repositories/EntityFrameworkCore/EfCoreRepository.cs#L52
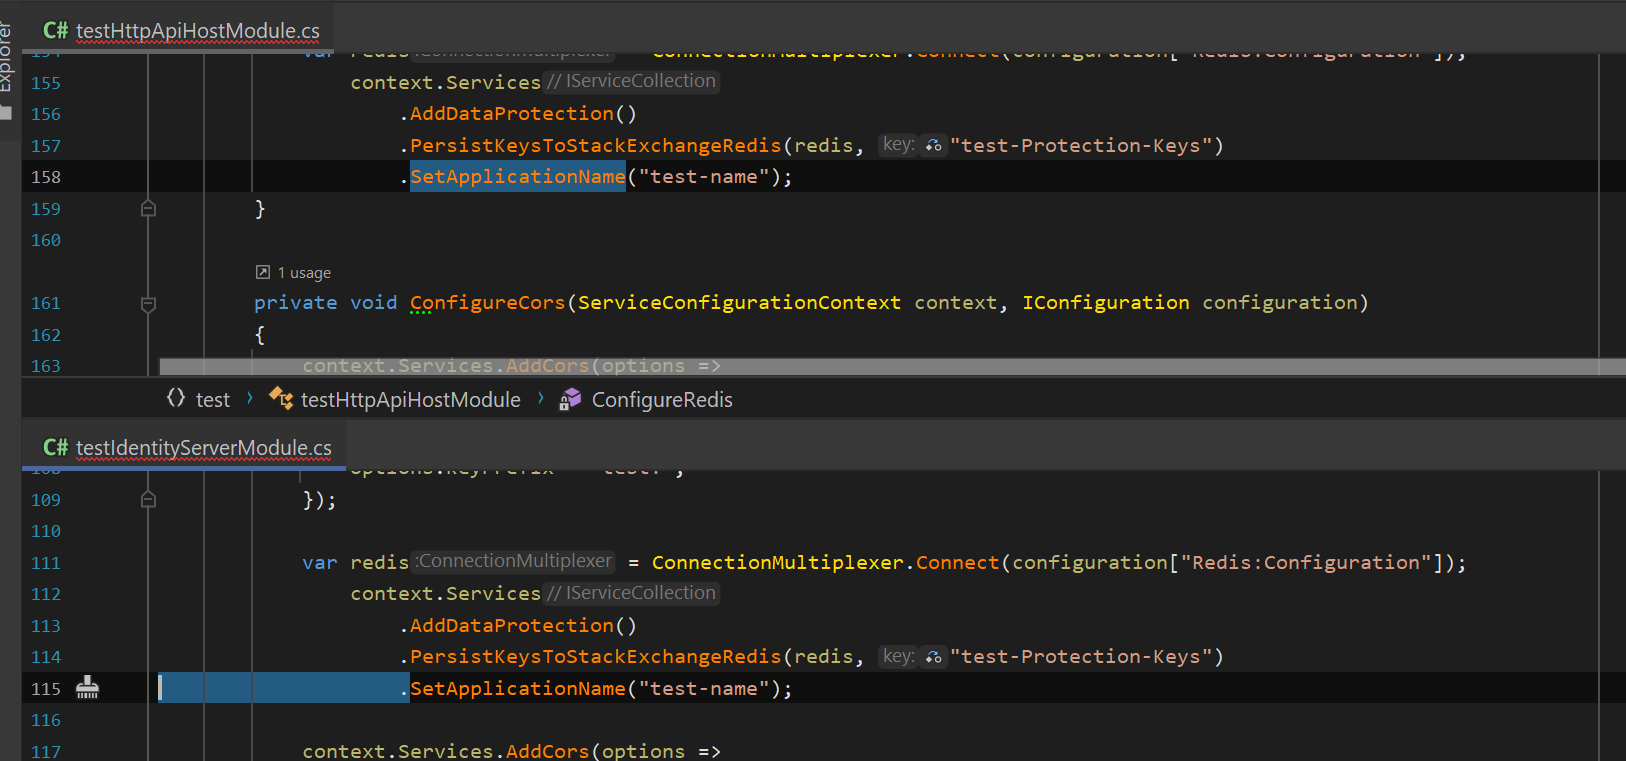
It works for me after SetApplicationName