hi
Can you share the module code and debug logs of Child Project (API Host)?
liming.ma@volosoft.com
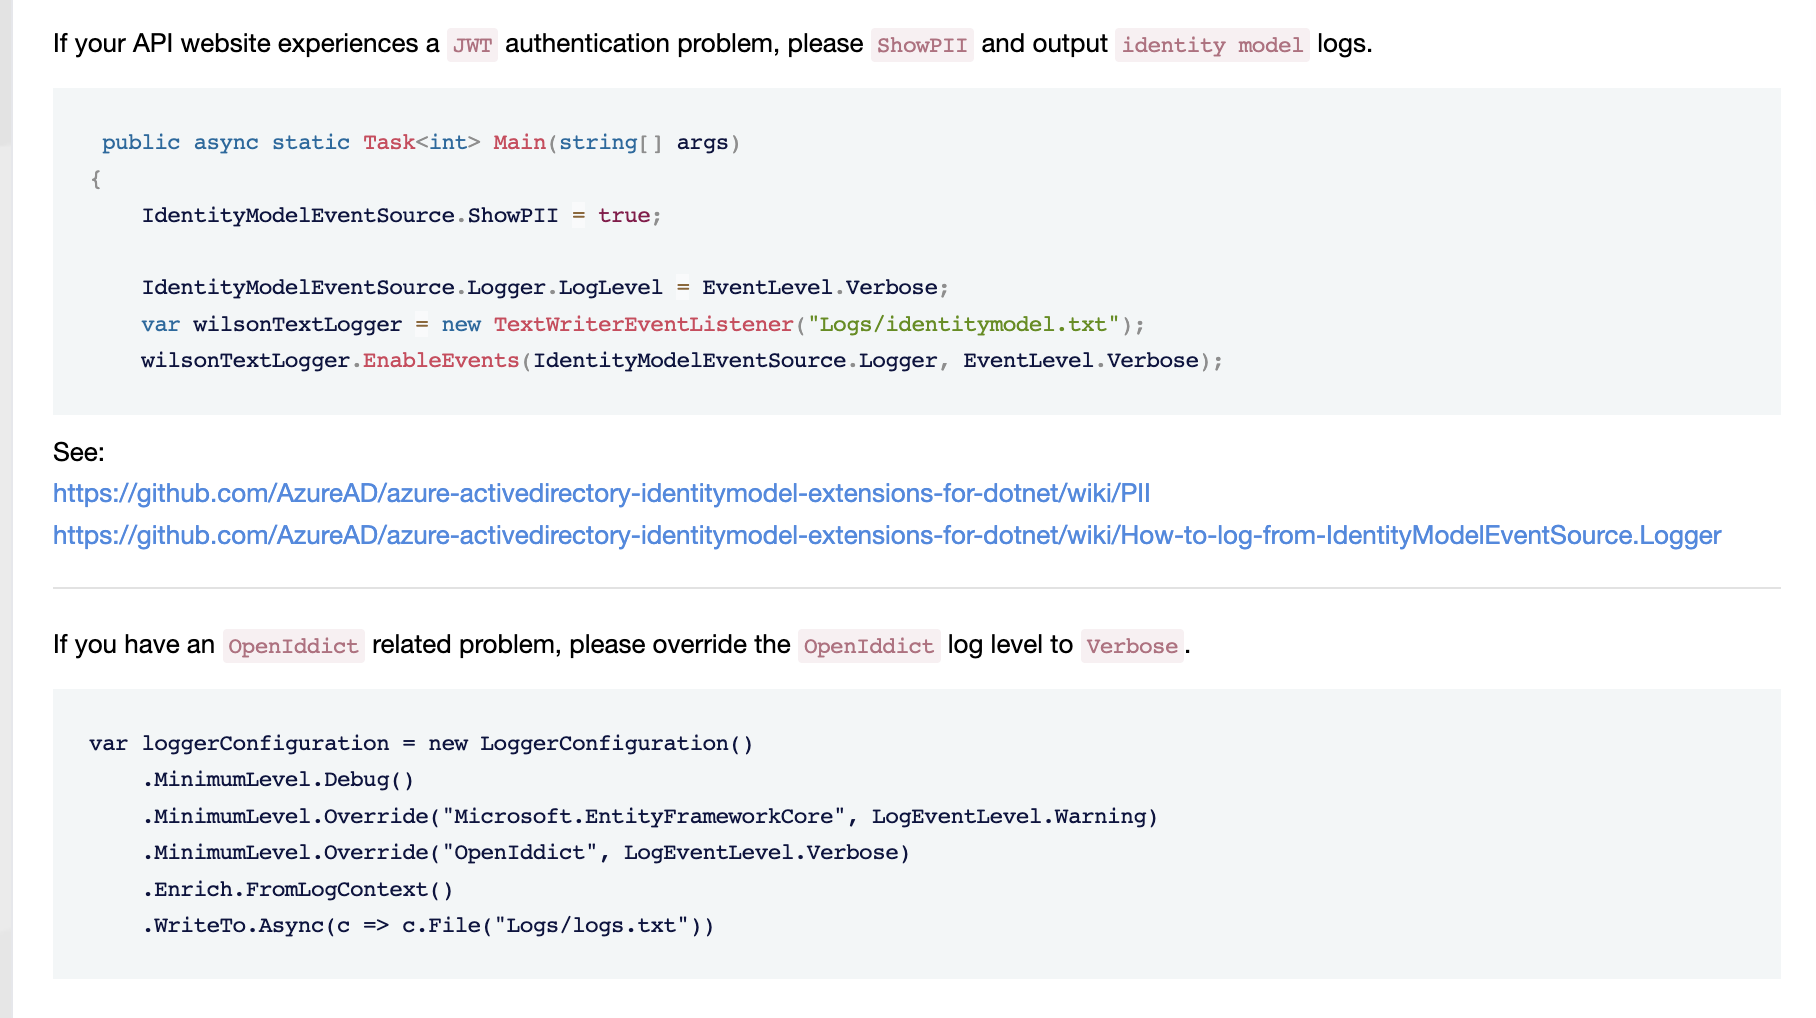
See https://abp.io/support/questions/8622/How-to-enable-Debug-logs-for-troubleshoot-problems
Thanks.
hi
The next 10.0 patch Suite will fix that.
Thanks.
hi
There is no user concept in the Client Credentials flow.
If you want to use a user, you can use the password flow.
Thanks.
hi
How can I reproduce it in a new template project with chat modules? Can you share some steps? Do you have any custom code?
Thanks.
hi
You can add these class/cshtml files to your AuthServer project.
See https://abp.io/docs/latest/framework/ui/mvc-razor-pages/customization-user-interface#overriding-a-razor-page-cshtml https://abp.io/docs/latest/framework/ui/mvc-razor-pages/customization-user-interface#example-1
hi
Yes, the authserver project
````csharp
[ExposeServices(typeof (OpenIddictSupportedLoginModel), typeof(LoginModel))]
public class MyLoginModel : OpenIddictSupportedLoginModel
{
    public override Task<IActionResult> OnPostAsync(string action)
    {
        var your_tenant_name = "my_tenant";// get it from post request.
        using(Current.Change(your_tenant_name))
        {
            return base.OnPostAsync(action);
        }
    }
}
hi
leptonx module source code and copy the aspnet-core/volo/src/Volo.Abp.AspNetCore.Mvc.UI.Theme.LeptonX/Themes/LeptonX/Layouts/Account/Default.cshtml to your project and hide the tenant selection component.account pro module source code and copy the abp/account/src/Volo.Abp.Account.Pro.Public.Web/Pages/Account/Login.cshtml to your project and add a new tenant name input.public virtual async Task<IActionResult> OnPostAsync(string action)(abp/account/src/Volo.Abp.Account.Pro.Public.Web/Pages/Account/Login.cshtml.cs) to change the current tenant.Thanks.
恩 你可以忽略这个csrf错误, 看看如何复现上述的菜单消息的问题. 当你测试的时候你可以在多个浏览器或者隐私标签中打开localhost来测试
The antiforgery token could not be decrypted.
大概率是你的应用程序没有持久化持DataProtection的加密 Key 每次启动都使用了一个新的key, 导致之前的cookies无法解密.
又或者有其他应用程序也使用了localhost 作为域名, 然后写入了新的cookie. 导致无法解密
详细的步骤是?
之后呢?
谢谢




