hi
Can you share a test app?
I will check it.
liming.ma@volosoft.com
Thanks
The auth website is just like Google
You should obtain a token from the core website.
hi
Even though the user is the same in core and auth, but they are actually different. So you can't use the core token to request auth, vice versa
They are different auth servers.
hi
Can you confirm your Administration service can communicate with the authserver website?
https://abp.io/community/articles/common-errors-in-jwt-bearer-authentication-4u3wrbs5#gsc.tab=0
Thanks
理论上没有问题, 你可以参考https://abp.io/community/articles/implementing-passwordless-authentication-with-asp.net-core-identity-c25l8koj 试试看
hi
You can change the check. eg OpenIddictServerEndpointType.Token
if (context.EndpointType != OpenIddictServerEndpointType.Authorization ||
    context.AuthorizationCodePrincipal == null)
{
    return;
}
你可以在authserver中这样做, 之后blazor server 或者 wasm要主动触发认证, 然后重定向到authserver中, 完成认证后再次重定向会应用中. 请参考https://abp.io/community/articles/implementing-passwordless-authentication-with-asp.net-core-identity-c25l8koj
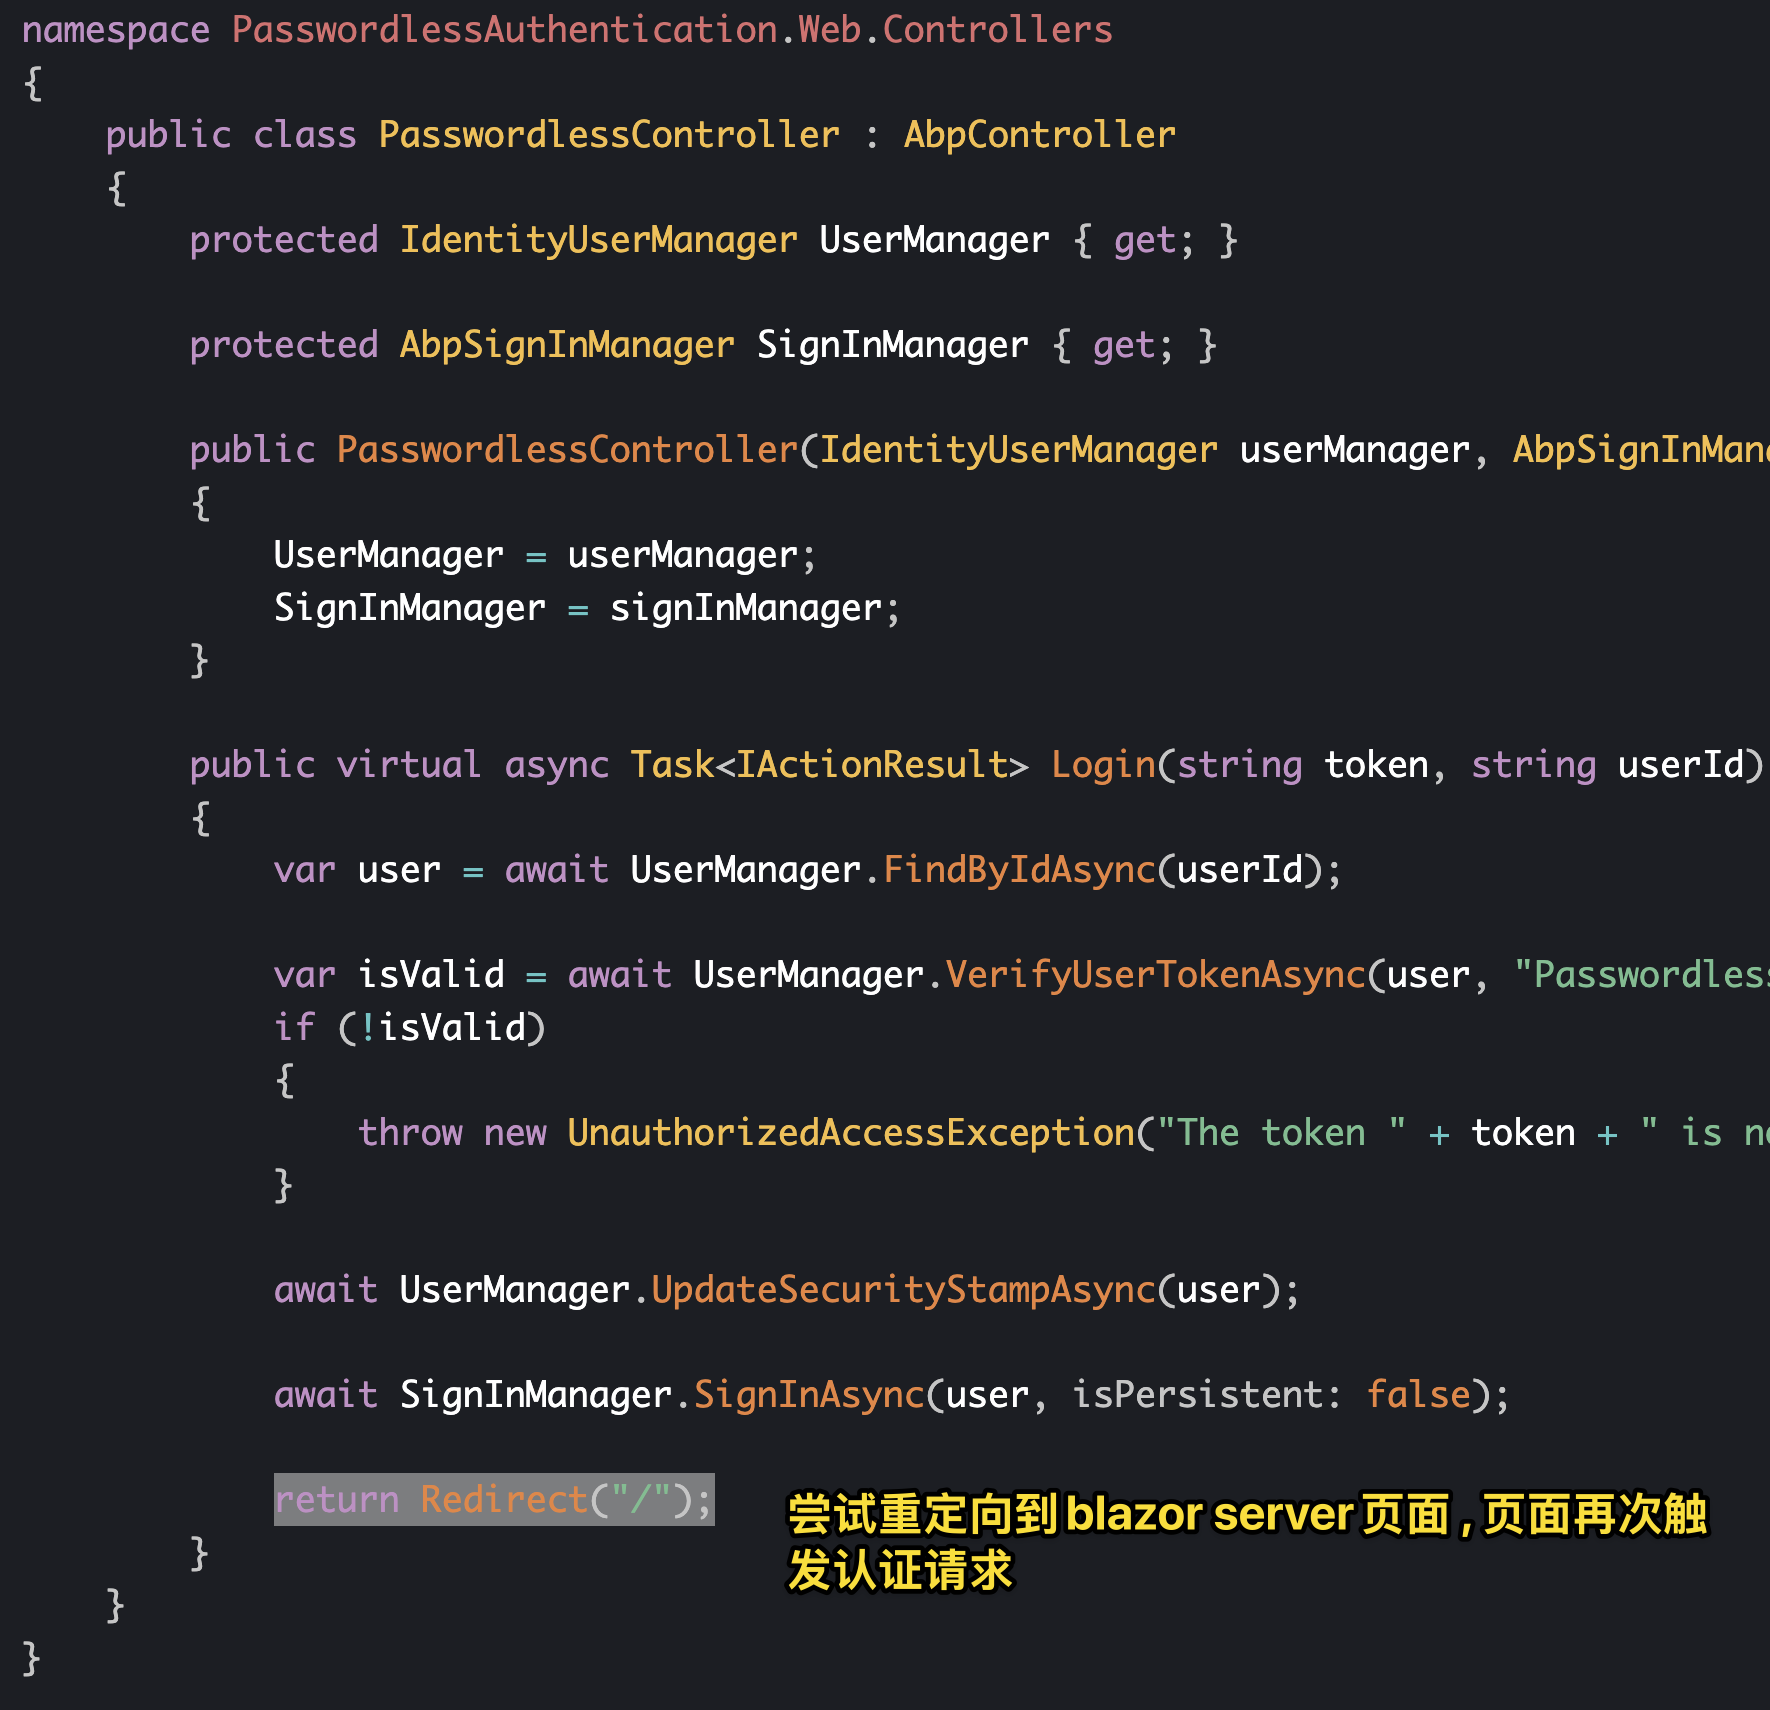
默认的项目模版就是这样工作的.
Blazor Server 或者 WASM 会使用code流通过AuthServer完成认证(获取access token/ id token).
你的最终需求是在authserver中完成登录吗?
谢谢




