Good news.
hi
Can you share a test project to reproduce this error?
liming.ma@volosoft.com Thanks
Please share a test project. You can upload it to https://wetransfer.com/ liming.ma@volosoft.com
hi
Do you mean run the Loda.Abp.Customers.AuthServer project?
This project doesn't reference the Volo.Abp.TextTemplateManagement.EntityFrameworkCore
so there will no TextTemplate tables in new migration file.
OpenIddict 中没有SessionId的概念, 你可以添加这样的claim到authserver和客户端中. 并检查它
Can you share the source code of your project? liming.ma@volosoft.com
hi
OpenIddict does not support Front-Channel Logout and Back-Channel Logout mechanisms.
If you only have two clients, system1 and system2, you can override the default LogoutController to return a view and add the logout URLs for both clients.
<!DOCTYPE html>
<html>
   <style>iframe{{display:none;width:0;height:0;}}</style>
   <body>
       <iframe src='https://localhost/signout-oidc'></iframe>
      <iframe src='https://localhost/signout-oidc'></iframe>
   </body>
</html>
https://github.com/abpframework/abp/blob/rel-7.2/modules/openiddict/src/Volo.Abp.OpenIddict.AspNetCore/Volo/Abp/OpenIddict/Controllers/LogoutController.cs#L12-L24
https://github.com/openiddict/openiddict-core/issues/312
You can maintain an array of client information, and add an iframe for each client to the logout view when logging out from the auth server.
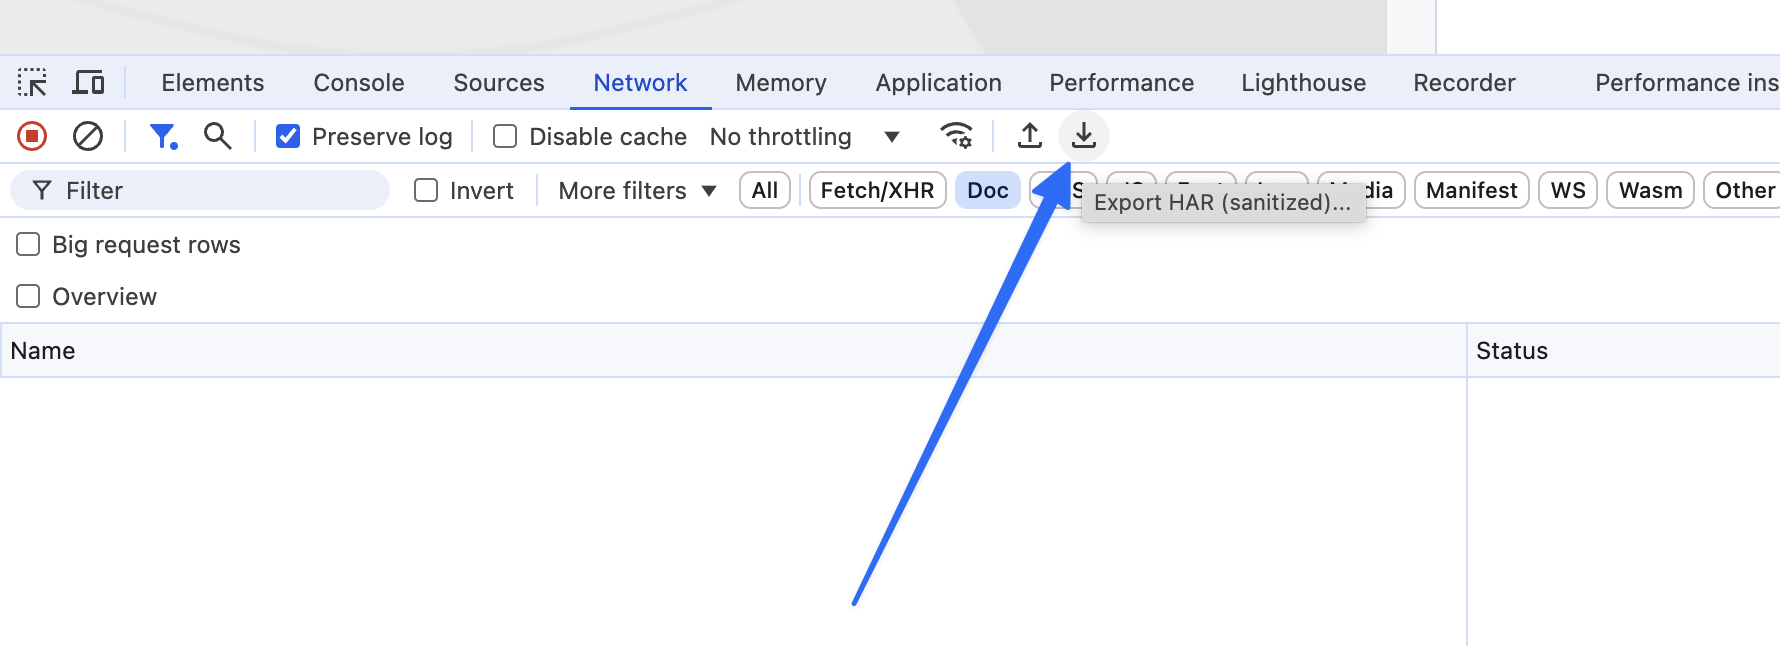
You can check&share all http requests during the logout process.
Use Chrome to record and export as a HAR file.
The HAR file will contain the request and response cookies.
liming.ma@volosoft.com
Thanks.