Great. : )
hi
ok.
Because the PermissionDataSeeder just inserts the data.
"AccountIntegrations.Create",
"AccountIntegrations.Edit",
"AccountIntegrations.Delete",
"BasketReturn.Create"
You can debug this code to see await PermissionGrantRepository.InsertManyAsync(permissions);
var accPermissions = new[]
{
    "AccountIntegrations.Create",
    "AccountIntegrations.Edit",
    "AccountIntegrations.Delete",
};

var names = accPermissions.ToArray();
var existsPermissionGrants = (await PermissionGrantRepository.GetListAsync(names, RolePermissionValueProvider.ProviderName, cashRoleName)).Select(x => x.Name).ToList();
var permissions = names.Except(existsPermissionGrants).Select(permissionName => new PermissionGrant(GuidGenerator.Create(), permissionName, RolePermissionValueProvider.ProviderName, cashRoleName, tenantId)).ToList();
if (!permissions.Any())
{
    return;
}
await PermissionGrantRepository.InsertManyAsync(permissions);
hi
Can you share a simple project to reproduce the problem?
I will download the code and debug it locally.
liming.ma@volosoft.com
Thanks.
hi
I have checked the video. Code seems to be no problem.
The PermissionDataSeeder will insert the records into the AbpPermissionGrant table. Can you check if the insert succeeds?
hi
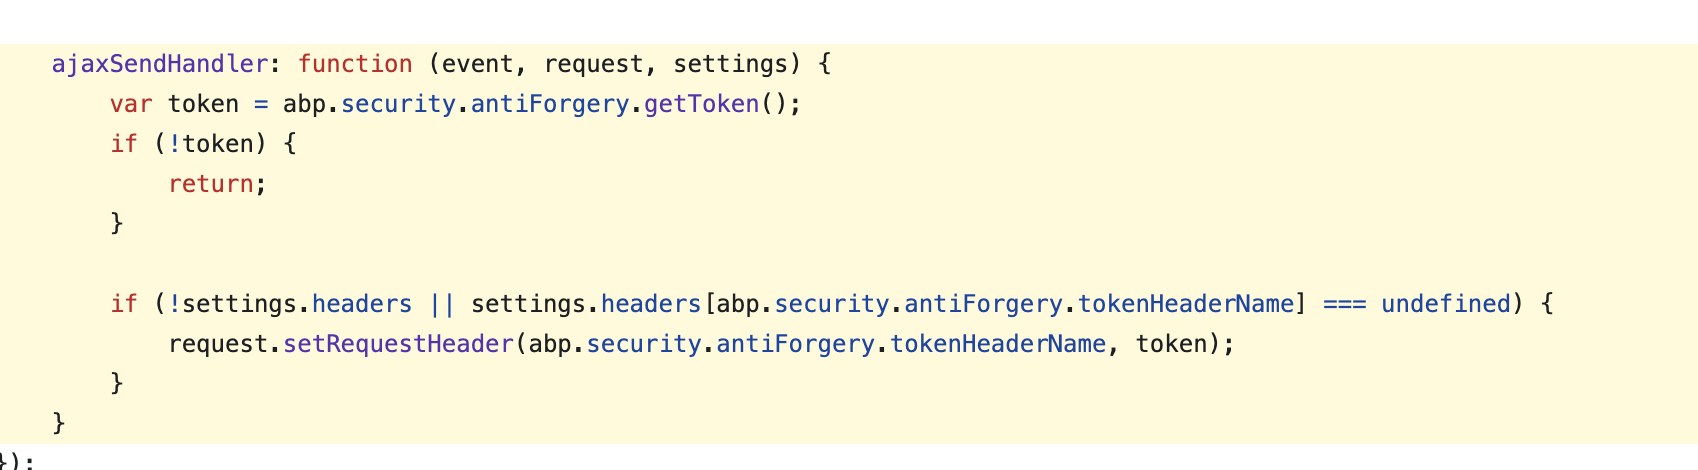
If the cookie contains this token, the request header must include it.
Also, recommended to use HTTPS instead of HTTP.
hi
POST /auth/api/account/profile-picture HTTP/1.1
RequestVerificationToken: abcdefg

Cookie: XSRF-TOKEN=abcdefg
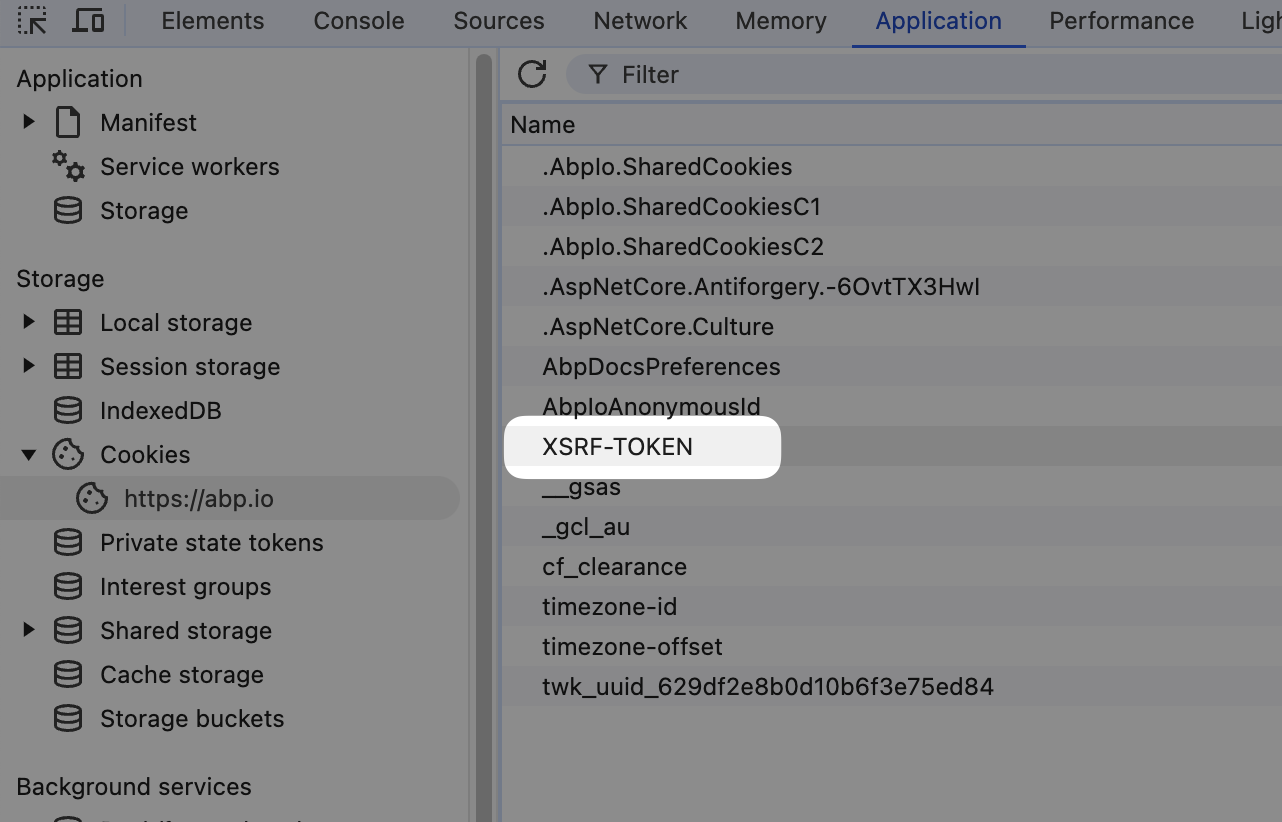
You can check your cookies. There should be an XSRF-TOKEN cookie.
The angular team has fixed a problem with XSRF
see https://github.com/abpframework/abp/pull/21595
hi yasin.hallak.89@gmail.com
Your ticket has been refunded.
Thanks.
hi
The required antiforgery request token was not provided in either form field "__RequestVerificationToken" or header value "RequestVerificationToken".
abp.ajax will set RequestVerificationToken to request header, it value read from cookies(XSRF-TOKEN).
https://github.com/abpframework/abp/blob/dev/npm/packs/jquery/src/abp.jquery.js#L254-L263
Is your api call has set this header?
Thanks.
hi LiSong
The services and repositories are registered to the dependency injection system by convention.

See https://abp.io/docs/latest/framework/fundamentals/dependency-injection#inherently-registered-types https://abp.io/docs/latest/framework/fundamentals/dependency-injection#dependency-interfaces
Thanks.
hi
Does context.TenantId have a value?
The PermissionDataSeeder will insert the records into the AbpPermissionGrant table.
Can you check if the insert succeeds?
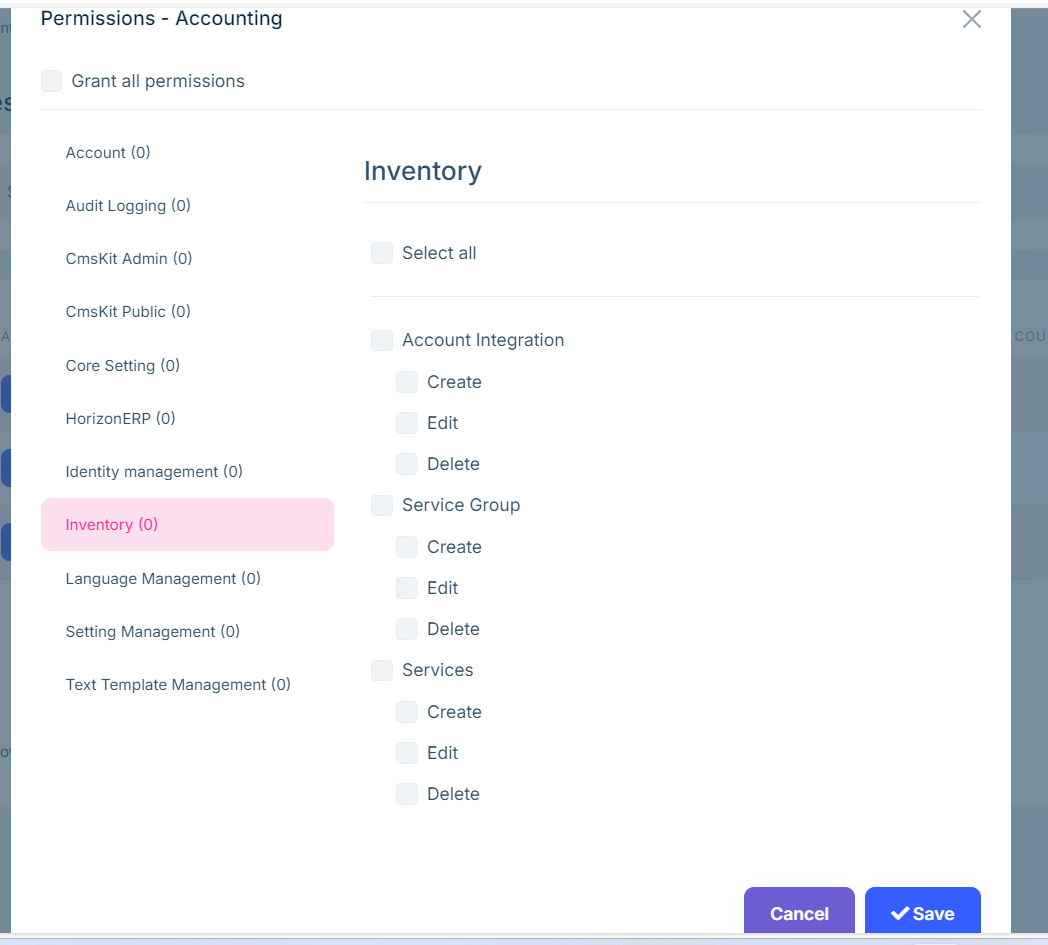
Is this UI page from a tenant admin user?
Thanks.




