


If you're creating a bug/problem report, please include the following:
- ABP Framework version: v5
- UI type:MVC
- DB provider: EF Core
- Tiered (MVC) or Identity Server Separated (Angular): MVC
- Exception message and stack trace:
- Steps to reproduce the issue:" i want to connect with the application API from the mobile flutter app (or even postman for testing), currently, i send the login credentials, and the API return success with cookie: as the following Login-Response status: 200 I/flutter (22205): Login-Response body: {"result":1,"description":"Success"} I/flutter (22205): Login-Response header: {x-powered-by: ASP.NET, cache-control: no-cache,no-store, set-cookie: idsrv.session=EDE9D7567F90AF7FAD2A31E496245202; path=/; secure; samesite=none,.AspNetCore.Identity.Application=CfDJ8GhZ26jUH4hCteGIT55Ww8Orv1wfkSbC_Axzu-DOG4eTj-O_ZRR6N91g21rYFQRCVTrOMN6rlKoMR4VAm8OQBXKxV0I2Hi0z-xKAptHF0dmPIHEexEVnkW3hNNcqQTZmQx33By6RigcnJkjFMLLshbYDiwyHbFdBe1OyNeJWZdEc9a5GR3Xdb5gc5n58E- ... etc
then i set the following: cookie = .AspNetCore.Identity.Application=CfDJ8GhZ26jUH4hCteGIT55Ww8Orv1wfkSbC_Axzu-DOG4eTj-O_ZRR6N91g21rYFQRCVTrOMN6rlKoMR4VAm8OQBXKxV0I2Hi0z-xKAptHF0dmPIHEexEVnkW3hNNcqQTZmQx33By6RigcnJkjFMLLshbYDiwyHbFdBe1OyNeJWZdEc9a5GR3Xdb5gc5n58E
then I make a call to get the data from the service and the data is returned back no issue: var header = { "Content-Type": "application/json", "Accept": "application/json", "Cookie": cookie }; now when i call the POST method using the same header with the required body data it keeps giving me Response status code: 302 if I take the JSON data (the body ) and post it using swagger it works i have read many articles inside support and abp.io but i got stuck i didn't understand it correctly
MY QUESTION IS:
i think i should use requestverificationtoken or token not cookie
please need clear steps on how I can reach a good solution, knowing that I created my ( MVC simple arch. not tired) application as a template without any change in the configuration from abp suite
also, I noted each time especially if fail in login it returns Html login page instead of JSON data , how i can return JSON not HTML if an error happened thanks in advance
3 Answer(s)
-
0
HI
AntiForgery always checks when a request contains authentication cookies (AspNetCore.Identity.Application)
https://docs.abp.io/en/abp/latest/CSRF-Anti-Forgery
how i can return JSON not HTML if an error happened
The default behavior of cookies authentication scheme:
Return HTML(301) when authentication failed, Return 401 when authentication failed if the current request is ajax.
https://github.com/dotnet/aspnetcore/blob/e755f6017c1be34d25c9381af87f50d1b31abe40/src/Security/Authentication/Cookies/src/CookieAuthenticationEvents.cs#L41-L45 https://github.com/abpframework/abp/pull/9940
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
hello ABP team, I wish I found comprehensive documentation about API and enough guide to follow best practice steps better than losing time just searching in Github and google :( anyhow i realize that i should do the following steps :
first use the following address baseUrl + "/connect/token" to get token first (don't use log in to return the cookie ) with the client request.bodyFields = { 'username': username, 'password': password, 'Client_Id': 'yourname_App', 'grant_type': 'password', 'client_secret': '1q2w3e*' }; this will return the token if it succeeded step2: send the token in heder with any request : var header = { 'Content-Type': 'application/json', 'Accept': 'application/json', 'Authorization': 'Bearer $token', }; it will return data and post data with no problems
**my question here ** if I want to receive login user details, which URL should I use? "/api/identity/users/by-username/" (user should has privilege to see users rights? ) if i use "/api/account/my-profile" it will return basic info but for example "Extra fields added to the identity not returned"
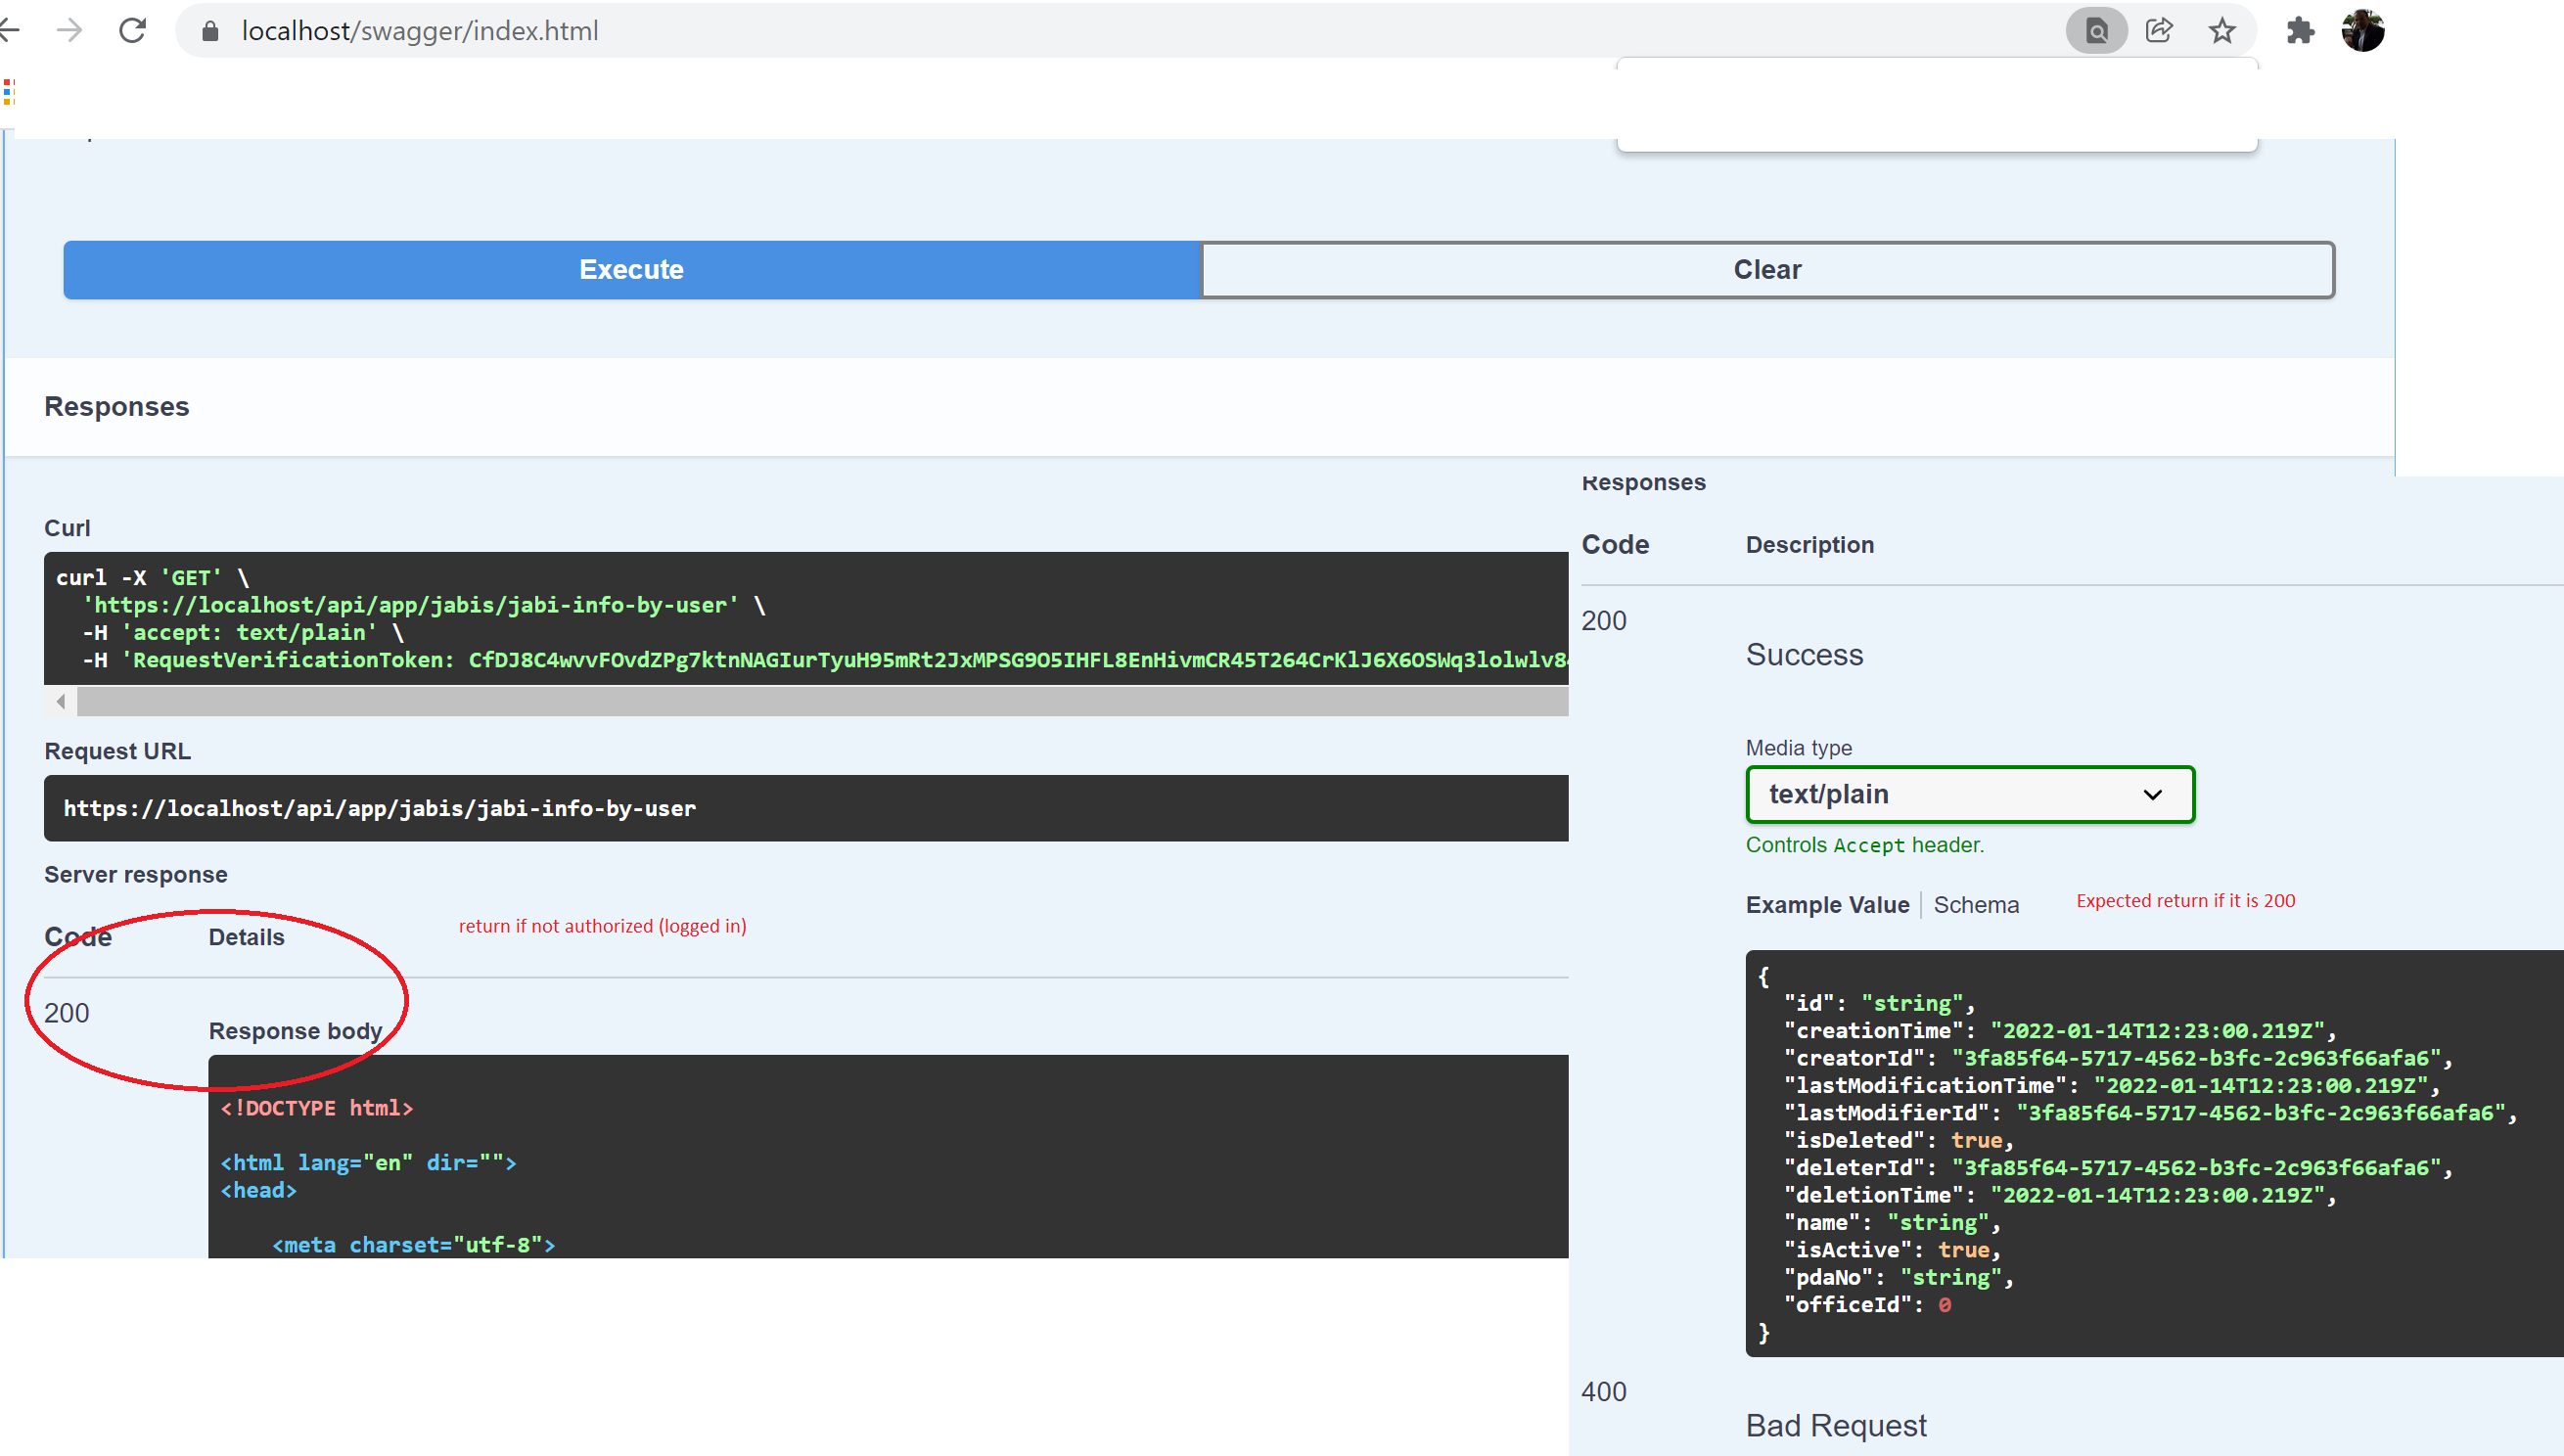
other question please: for some reason if the user, not login or he should re-login the response status returned 200 = OK !! with the login page, means it should return json data " not authorized" or how i can deal with login page HTML in json as an error?
 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)
-
0
if I want to receive login user details, which URL should I use?
You can create a custom API to do that.
for some reason if the user, not login or he should re-login the response status returned 200 = OK !! with the login page, means it should return json data " not authorized" or how i can deal with login page HTML in json as an error?
See
https://github.com/abpframework/abp/issues/5235 https://github.com/abpframework/abp/pull/9940 https://github.com/dotnet/aspnetcore/blob/9da42b9fab4c61fe46627ac0c6877905ec845d5a/src/Security/Authentication/Cookies/src/CookieAuthenticationEvents.cs#L63
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)


