


Hi Support Team,
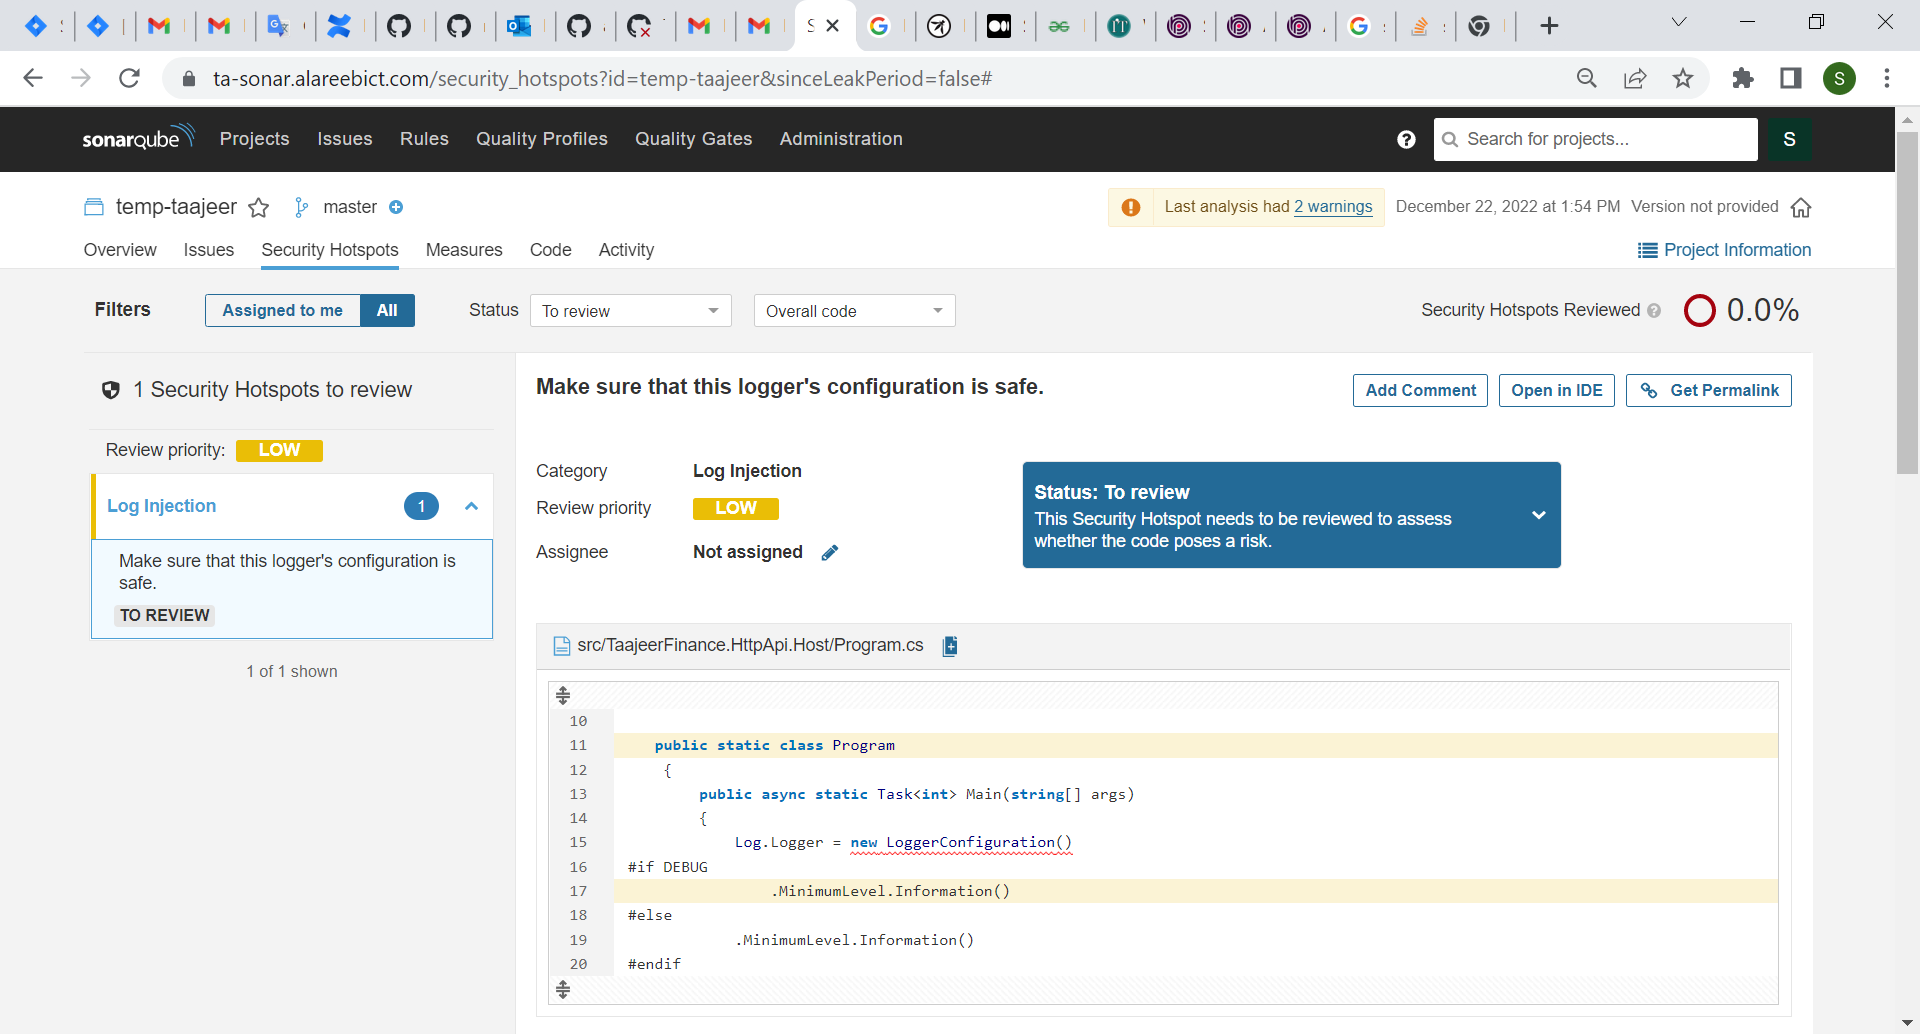
We have executed a security check via SonarQube but we received a security issue related to abp framework here are the details about this issue:
| Category | Log Injection | | -------------------- | ----------------------------------------------------------------- | | Review priority | LOW | | Details | Make sure that this logger's configuration is safe. |
Here are the links which might help you:
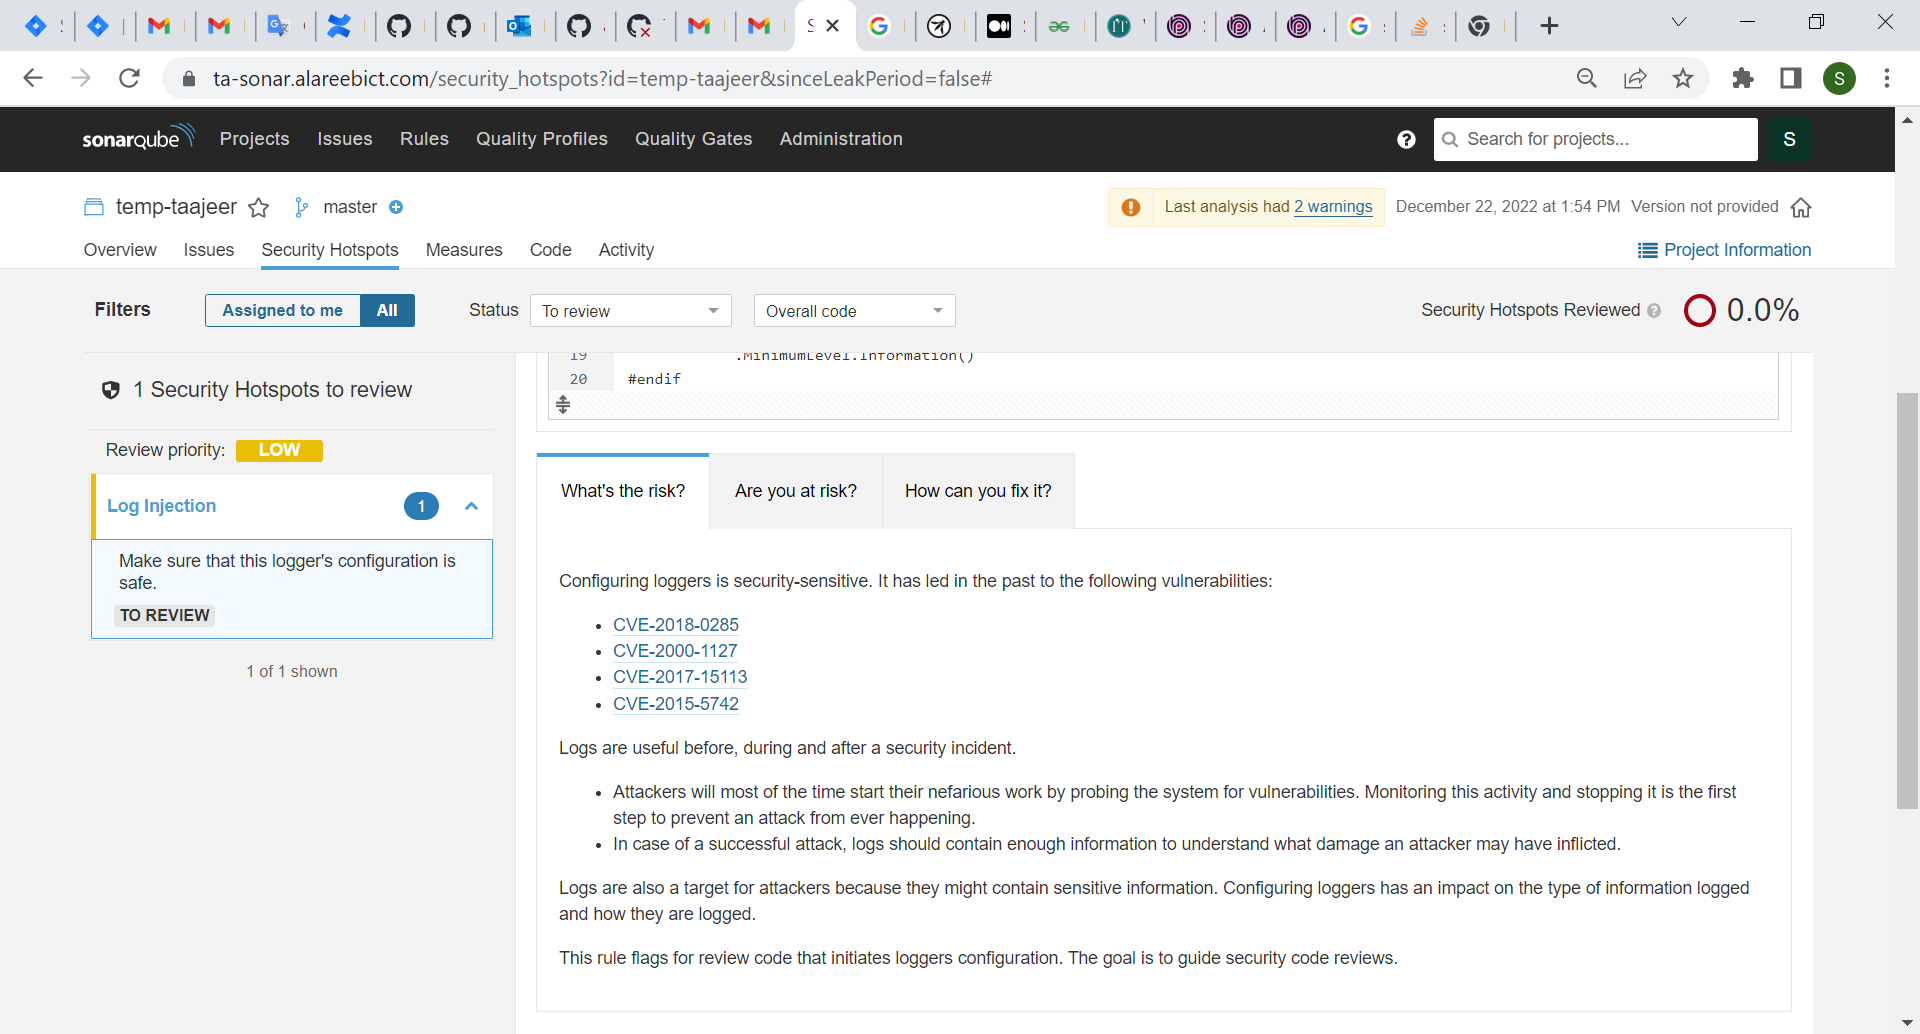
Configuring loggers is security-sensitive. It has led in the past to the following vulnerabilities:
CVE-2018-0285 CVE-2000-1127 CVE-2017-15113 CVE-2015-5742
How to fix see: OWASP Top 10 2017 Category A3 - Sensitive Data Exposure OWASP Top 10 2017 Category A10 - Insufficient Logging & Monitoring MITRE, CWE-532 - Information Exposure Through Log Files MITRE, CWE-117 - Improper Output Neutralization for Logs MITRE, CWE-778 - Insufficient Logging SANS Top 25 - Porous Defenses
- ABP Framework version: 6.0.1
- UI type: Angular
- DB provider: EF Core
- Tiered (MVC) or Identity Server Separated (Angular): no
- Exception message and stack trace: see the attached files
- Steps to reproduce the issue: Create a new project with abp framework then execute a security check with SonarQube.
Would you please give this issue a high priority we cannot proceed with abp framework without fixing this issue because we have a security audit from a third party?
3 Answer(s)
-
0
this is the default setup of the Logger. You can customize it according to your requirements. If your pen test tool raises it as a "low level security leak" you can change it in the
src/TaajeerFinance.HttpApi.Host/Program.csclass. Set it to.MinimumLevel.Fatal().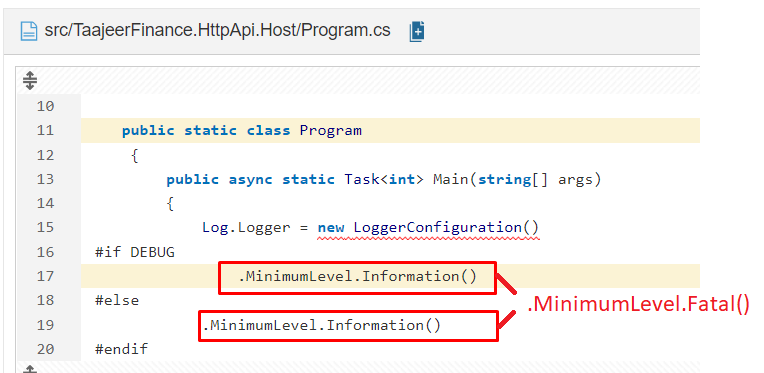
We cannot do it in the framework because it's not in the framework. It's in the application that you have generated.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)


