


- ABP Framework version: 7.4.2
- UI Type: Angular
- Database System: EF Core (PostgreSQL)
- Tiered (for MVC) or Auth Server Separated (for Angular): yes
- Exception message and full stack trace:
- Steps to reproduce the issue:
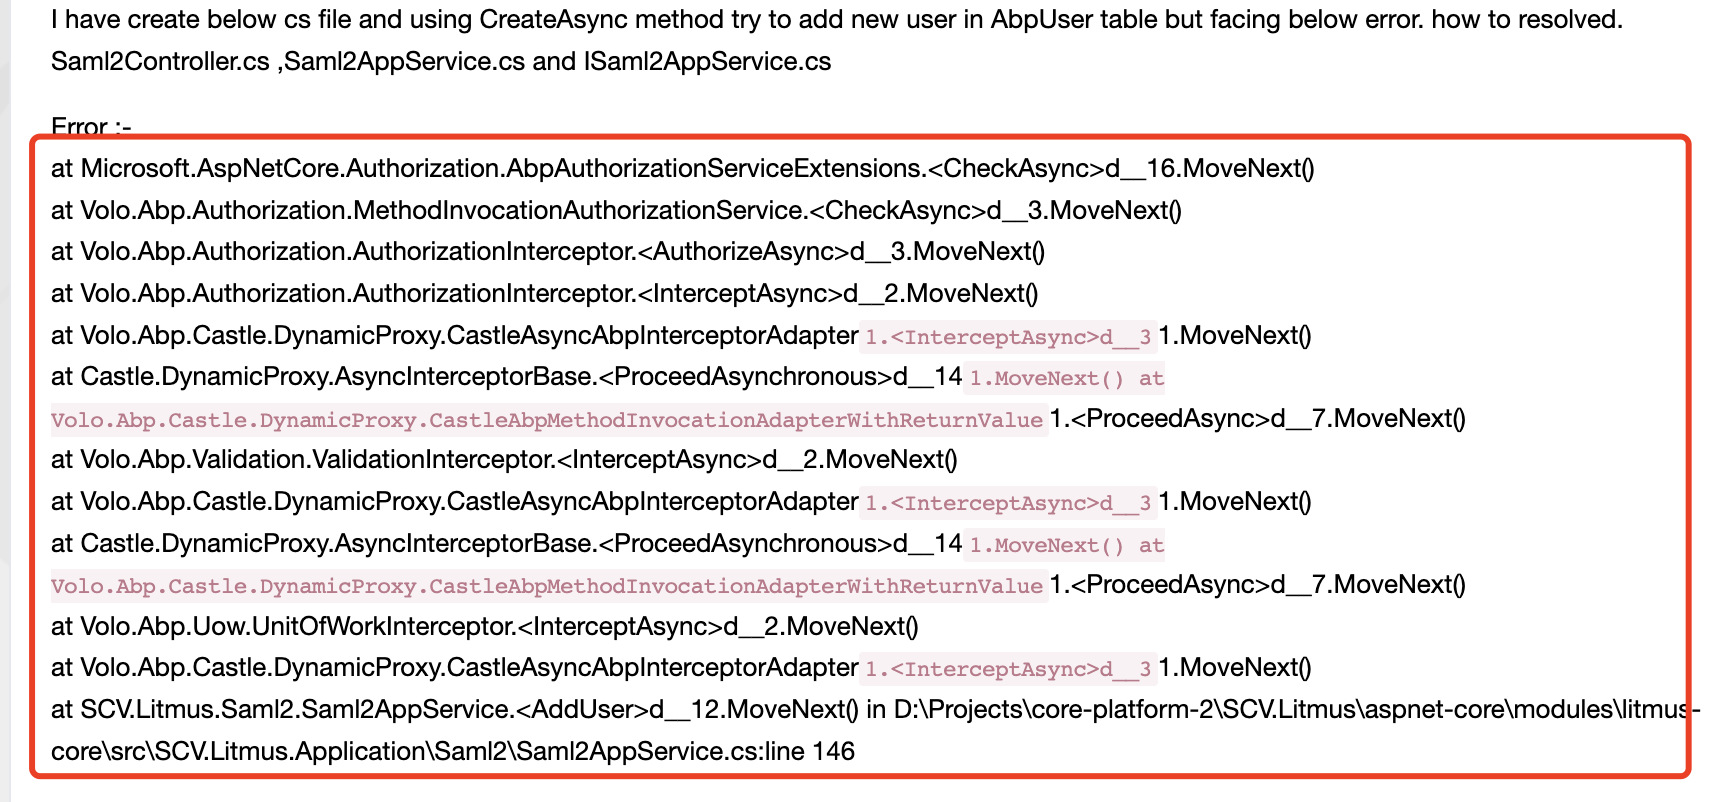
I have create below cs file and using CreateAsync method try to add new user in AbpUser table but facing below error. how to resolved. Saml2Controller.cs ,Saml2AppService.cs and ISaml2AppService.cs
Error :-
at Microsoft.AspNetCore.Authorization.AbpAuthorizationServiceExtensions.<CheckAsync>d__16.MoveNext()
at Volo.Abp.Authorization.MethodInvocationAuthorizationService.<CheckAsync>d__3.MoveNext()
at Volo.Abp.Authorization.AuthorizationInterceptor.<AuthorizeAsync>d__3.MoveNext()
at Volo.Abp.Authorization.AuthorizationInterceptor.<InterceptAsync>d__2.MoveNext()
at Volo.Abp.Castle.DynamicProxy.CastleAsyncAbpInterceptorAdapter1.<InterceptAsync>d__31.MoveNext()
at Castle.DynamicProxy.AsyncInterceptorBase.<ProceedAsynchronous>d__141.MoveNext() at Volo.Abp.Castle.DynamicProxy.CastleAbpMethodInvocationAdapterWithReturnValue1.<ProceedAsync>d__7.MoveNext()
at Volo.Abp.Validation.ValidationInterceptor.<InterceptAsync>d__2.MoveNext()
at Volo.Abp.Castle.DynamicProxy.CastleAsyncAbpInterceptorAdapter1.<InterceptAsync>d__31.MoveNext()
at Castle.DynamicProxy.AsyncInterceptorBase.<ProceedAsynchronous>d__141.MoveNext() at Volo.Abp.Castle.DynamicProxy.CastleAbpMethodInvocationAdapterWithReturnValue1.<ProceedAsync>d__7.MoveNext()
at Volo.Abp.Uow.UnitOfWorkInterceptor.<InterceptAsync>d__2.MoveNext()
at Volo.Abp.Castle.DynamicProxy.CastleAsyncAbpInterceptorAdapter1.<InterceptAsync>d__31.MoveNext()
at SCV.Litmus.Saml2.Saml2AppService.<AddUser>d__12.MoveNext() in D:\Projects\core-platform-2\SCV.Litmus\aspnet-core\modules\litmus-core\src\SCV.Litmus.Application\Saml2\Saml2AppService.cs:line 146
basically the users who are authenticated from external SSO are not our application users, only the similarity is the email address. After token validation, I have to check if the user exists in our system with the email id, if the user does not exist with that email create a user with a specific role and then set the current user. My question is how can I execute these user checks and creation logic immediately after user validate from IDP?
2 Answer(s)
-
0
any update ?
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
i didn't see any error message
basically the users who are authenticated from external SSO are not our application users, only the similarity is the email address. After token validation, I have to check if the user exists in our system with the email id, if the user does not exist with that email create a user with a specific role and then set the current user. My question is how can I execute these user checks and creation logic immediately after user validate from IDP?
see https://abp.io/support/questions/7390/Configure-Client-specific-external-providers-in-auth-server#answer-3a13601e-fb25-9aac-b3e8-a84ae3378128
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)


