0
Johannes created
- ABP Framework version: v3.3.0
- UI type: Angular
- DB provider: EF Core
We've implemented our own login controller for use by an external app.
The login endpoint uses the signinmanager:
protected SignInManager<Volo.Abp.Identity.IdentityUser> SignInManager { get; }
And logs in:
var signInResult = await SignInManager.PasswordSignInAsync(
                login.UserNameOrEmailAddress,
                login.Password,
                login.RememberMe,
                true
);
This works fine for users without 2-factor enabled.
When 2-factor is enabled, we get the expected 2-factor cookie back:
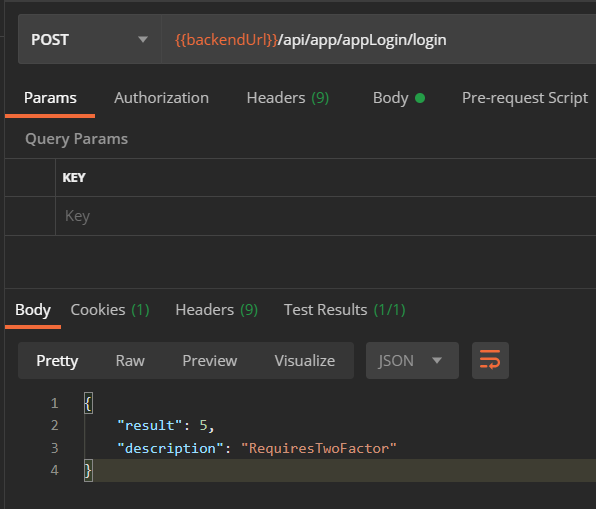
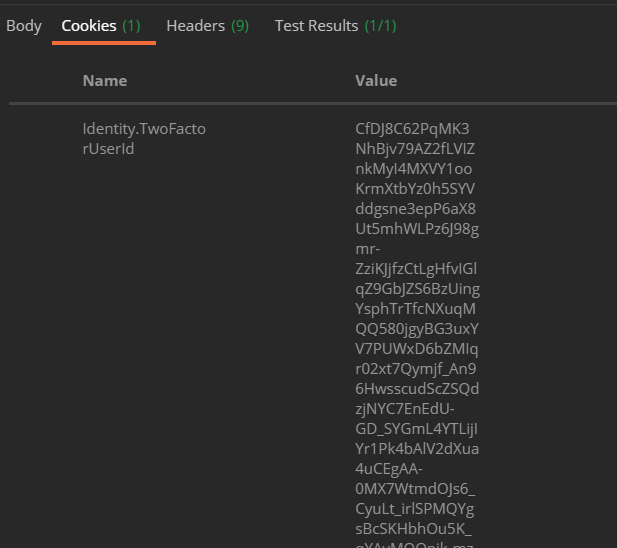
Which we then provide in the header when calling a SendSmsSecurityCode endpoint.
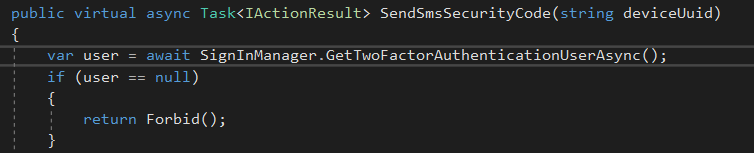
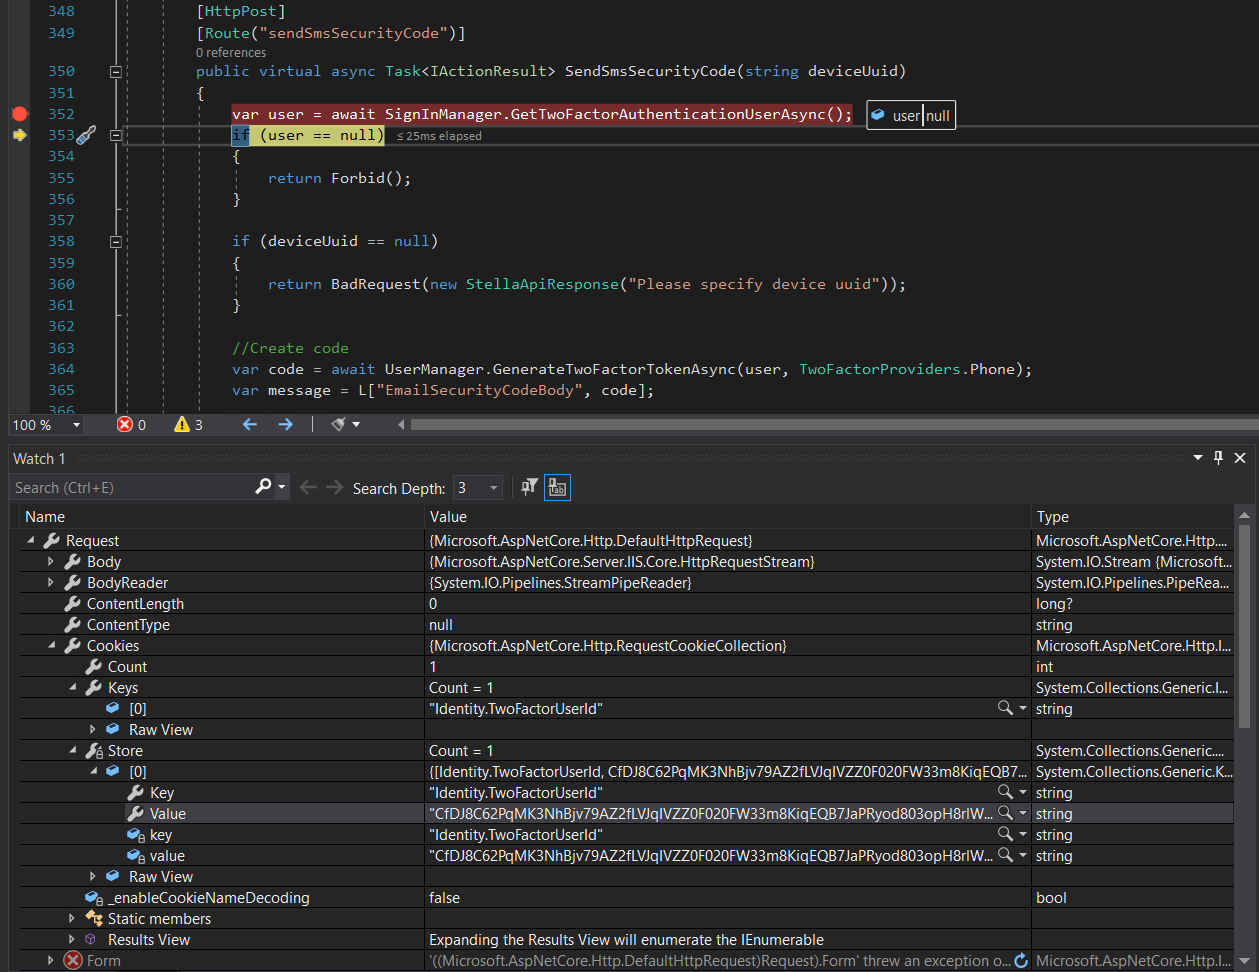
This it where we get confused: SignInManager.GetTwoFactorAuthenticationUserAsync() returns null. How can this happen? Are we doing something wrong?
Markdown supported.
Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)