
currently the CRUD page has xss issues, what's the best way to fix it? i.e. with html-encoded. etc..
We are trying to add a textbox on the register page, users can put a code in and we will use the code to pick a tenant for them, so instead of using https://localhost:44381/Account/register?__tenant=lego they will just use https://localhost:44381/Account/register and put a code 'lego' on the new textbox and then the code behind will select lego as the tenant how can we do that? thanks
I need to modify the Task<IActionResult> OnPostAsync(string action) function in Pages/Account/Login. Therefore, I created a new class and copied the code into a new subclass. The code is as follows:
Without making any changes, an error occurs when running the code. However, if I remove this function, it runs normally.
I have attached all the relevant code. I noticed that the value of the action parameter being passed is null, this should be root cause
using System;
using System.Collections.Generic;
using System.ComponentModel.DataAnnotations;
using System.Diagnostics;
using System.Linq;
using System.Security.Claims;
using System.Threading.Tasks;
using Microsoft.AspNetCore.Authentication;
using Microsoft.AspNetCore.Http.Extensions;
using Microsoft.AspNetCore.Identity;
using Microsoft.AspNetCore.Mvc;
using Microsoft.Extensions.Logging;
using Microsoft.Extensions.Options;
using Owl.reCAPTCHA;
using Volo.Abp;
using Volo.Abp.Account;
using Volo.Abp.Account.ExternalProviders;
using Volo.Abp.Account.Public.Web;
using Volo.Abp.Account.Public.Web.Pages.Account;
using Volo.Abp.Account.Public.Web.Security.Recaptcha;
using Volo.Abp.Account.Security.Recaptcha;
using Volo.Abp.Account.Settings;
using Volo.Abp.Auditing;
using Volo.Abp.Identity;
using Volo.Abp.Identity.AspNetCore;
using Volo.Abp.Identity.Settings;
using Volo.Abp.Reflection;
using Volo.Abp.Security.Claims;
using Volo.Abp.Settings;
using Volo.Abp.Uow;
using Volo.Abp.Users;
using Volo.Abp.Validation;
using IdentityUser = Volo.Abp.Identity.IdentityUser;

namespace Tapp.Web.Pages.Account;

[DisableAuditing]
public class TappLoginModel : LoginModel
{

    public TappLoginModel(
        IAuthenticationSchemeProvider schemeProvider,
        IOptions<AbpAccountOptions> accountOptions,
        IAbpRecaptchaValidatorFactory recaptchaValidatorFactory,
        IAccountExternalProviderAppService accountExternalProviderAppService,
        ICurrentPrincipalAccessor currentPrincipalAccessor,
        IOptions<IdentityOptions> identityOptions,
        IOptionsSnapshot<reCAPTCHAOptions> reCaptchaOptions) : base(
            schemeProvider,
            accountOptions,
            recaptchaValidatorFactory,
            accountExternalProviderAppService,
            currentPrincipalAccessor,
            identityOptions,
            reCaptchaOptions)
    {

    }


    [UnitOfWork] //TODO: Will be removed when we implement action filter
    public override async Task<IActionResult> OnPostAsync(string action)
    {
        string action2 = action;
        try
        {
            await ReCaptchaVerification();
        }
        catch (UserFriendlyException e)
        {
            if (e is ScoreBelowThresholdException)
            {
                var onScoreBelowThresholdResult = OnRecaptchaScoreBelowThreshold();
                if (onScoreBelowThresholdResult != null)
                {
                    return await onScoreBelowThresholdResult;
                }
            }

            Alerts.Danger(GetLocalizeExceptionMessage(e));
            return Page();
        }
        var validationResult = new AbpValidationResult();

        //AddErrors(validationResult, ModelState);

        if (ModelState.IsValid)
        {
            throw new AbpValidationException(
                "ModelState is not valid! See ValidationErrors for details.",
                validationResult.Errors
            );
        }

        foreach (var state in ModelState)
        {
            foreach (var error in state.Value.Errors)
            {
                validationResult.Errors.Add(new ValidationResult(error.ErrorMessage, new[] { state.Key }));
            }
        }

        if (validationResult.Errors.Any())
        {
            throw new AbpValidationException(
                "ModelState is not valid! See ValidationErrors for details.",
                validationResult.Errors
            );
        }
        //I commented it out for debugging purpose
        //ValidateModel();


@page
@using Microsoft.AspNetCore.Mvc.Localization
@using Microsoft.Extensions.Options
@using Owl.reCAPTCHA
@using Volo.Abp.Account.Localization
@using Volo.Abp.Account.Public.Web.Pages.Account;
@using Volo.Abp.Account.Public.Web.Security.Recaptcha
@using Volo.Abp.Account.Settings
@using Volo.Abp.Identity;
@using Volo.Abp.Settings
@model Tapp.Web.Pages.Account.TappLoginModel

@inject IHtmlLocalizer<AccountResource> L
@inject Volo.Abp.AspNetCore.Mvc.UI.Layout.IPageLayout PageLayout
@inject ISettingProvider SettingProvider
@{
    PageLayout.Content.Title = L["Login"].Value;
    var reCaptchaVersion = await SettingProvider.GetAsync<int>(AccountSettingNames.Captcha.Version);
    if (Model.UseCaptcha)
    {
        await Model.ReCaptchaOptions.SetAsync(reCaptchaVersion == 3 ? reCAPTCHAConsts.V3 : reCAPTCHAConsts.V2);
    }

}

@section scripts
    {
    <abp-script-bundle name="@typeof(LoginModel).FullName">
        <abp-script src="/Pages/Account/Login.js" />
    </abp-script-bundle>

    @if (Model.UseCaptcha)
    {
        if (reCaptchaVersion == 3)
        {
            <recaptcha-script-v3 />
            <recaptcha-script-v3-js action="login" execute="false" />
        }
        else
        {
            <recaptcha-script-v2 />
        }
    }
}

@if (Model.IsLinkLogin)
{
    <abp-alert alert-type="Warning">
        @L["LinkAccountWarning", Url.PageLink()]
    </abp-alert>
}

@if (Model.BackToExternalLogins)
{
    <div class="d-grid gap-2">
        <a class="mb-3 btn btn-primary btn-block" href="@Url.Page("./ExternalLogins")">@L["Back"]</a>
    </div>
}
<div class="account-module-form">

    @if (Model.IsSelfRegistrationEnabled)
    {
        <h5 class="mb-2">@L["NotAMemberYet"] <a class="text-decoration-none" href="@Url.Page("./Register", new {returnUrl = Model.ReturnUrl, returnUrlHash = Model.ReturnUrlHash})">@L["Register"]</a></h5>
    }

    @if (Model.EnableLocalLogin)
    {
        <form method="post" id="loginForm">
            @if (Model.UseCaptcha)
            {
                <input class="mb-3" data-captcha="true" type="hidden" name="@RecaptchaValidatorBase.RecaptchaResponseKey" id="@RecaptchaValidatorBase.RecaptchaResponseKey"/>
            }
            <div>
                <div class="form-floating mb-2">
                    <input asp-for="LoginInput.UserNameOrEmailAddress" type="text" class="form-control" placeholder="name@example.com">
                    @Html.LabelFor(m => m.LoginInput.UserNameOrEmailAddress)
                    <span asp-validation-for="LoginInput.UserNameOrEmailAddress"/>
                </div>

                <div class="form-floating mb-2">
                    <input asp-for="LoginInput.Password" id="password-input" type="password" class="form-control" placeholder="Password">
                    @Html.LabelFor(m => m.LoginInput.Password)
                    <i id="PasswordVisibilityButton" class="bi bi-eye-slash show-pass-icon" data-bs-toggle="tooltip" data-bs-placement="top" data-bs-html="true" aria-label="@L["ShowPassword"]" data-bs-original-title="@L["ShowPassword"]"></i>
                    <i id="capslockicon" class="bi bi-capslock caps-lock-icon" style="display: none;" data-bs-toggle="tooltip" data-bs-placement="top" data-bs-html="true" aria-label="<i class='bi bi-exclamation-circle'></i> @L["CapsLockOn"]!" data-bs-original-title="<i class='bi bi-exclamation-circle'></i> @L["CapsLockOn"]!"></i>
                    <span asp-validation-for="LoginInput.Password"/>
                </div>
            </div>
            <abp-row>
                <abp-column>
                    <div class="form-switch ps-2">
                        <abp-input asp-for="LoginInput.RememberMe" class="mb-4"/>
                    </div>
                </abp-column>
                <abp-column class="text-end">
                    <a href="@Url.Page("./ForgotPassword", new {returnUrl = Model.ReturnUrl, returnUrlHash = Model.ReturnUrlHash})">@L["ForgotPassword"]</a>
                </abp-column>
            </abp-row>

            @if (reCaptchaVersion == 2)
            {
                <script>
                    recaptchaCallback = function (token) {
                        $('form button[type=submit]').removeAttr("disabled");
                        $('#@RecaptchaValidatorBase.RecaptchaResponseKey').val(token)
                    };
                </script>
                <div class="mb-3">
                    <recaptcha-div-v2 callback="recaptchaCallback"/>
                </div>
            }

            <div class="d-grid gap-2">
                <abp-button button-type="Primary" type="submit" class="mb-3" name="Action" value="Login" disabled="true">
                    <i class="bi bi-box-arrow-in-right me-1"></i>
                    @L["Login"]
                </abp-button>
            </div>

            @if (Model.ShowCancelButton)
            {
                <div class="d-grid gap-2">
                    <abp-button button-type="Secondary" type="submit" formnovalidate="formnovalidate" class="mb-3" name="Action" value="Cancel">@L["Cancel"]</abp-button>
                </div>
            }
        </form>
    }

    @if (Model.VisibleExternalProviders.Any())
    {
        if(Model.EnableLocalLogin)
        {
            <hr/>
            @L["OrSignInWith"]
            <br/>
        }
        else
        {
            @L["SignInWithOneOfTheFollowingProviders"]
        }

        <form asp-page="./Login" asp-page-handler="ExternalLogin"
              asp-route-returnUrl="@Model.ReturnUrl"
              asp-route-returnUrlHash="@Model.ReturnUrlHash"
              asp-route-linkTenantId="@Model.LinkTenantId"
              asp-route-linkUserId="@Model.LinkUserId"
              asp-route-linkToken="@Model.LinkToken"
              method="post">
            @foreach (var provider in Model.VisibleExternalProviders)
            {
                <button type="submit"
                        class="mt-2 me-2 btn btn-outline-primary btn-sm"
                        name="provider"
                        value="@provider.AuthenticationScheme"
                        data-busy-text="@L["ProcessingWithThreeDot"]">
                    @if (provider.Icon != null)
                    {
                        <i class="@provider.Icon"></i>
                    }
                    <span>@provider.DisplayName</span>
                </button>
            }
        </form>
    }
</div>
An unhandled exception occurred while processing the request.
AbpValidationException: ModelState is not valid! See ValidationErrors for details.
Tapp.Web.Pages.Account.TappLoginModel.OnPostAsync(string action) in Login.cshtml.cs, line 105

Stack Query Cookies Headers Routing
AbpValidationException: ModelState is not valid! See ValidationErrors for details.
Tapp.Web.Pages.Account.TappLoginModel.OnPostAsync(string action) in Login.cshtml.cs
+
            throw new AbpValidationException(
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.ExecutorFactory+GenericTaskHandlerMethod.Convert<T>(object taskAsObject)
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.ExecutorFactory+GenericTaskHandlerMethod.Execute(object receiver, object[] arguments)
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.InvokeHandlerMethodAsync()
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.InvokeNextPageFilterAsync()
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.Rethrow(PageHandlerExecutedContext context)
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.Next(ref State next, ref Scope scope, ref object state, ref bool isCompleted)
Microsoft.AspNetCore.Mvc.RazorPages.Infrastructure.PageActionInvoker.InvokeInnerFilterAsync()
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextExceptionFilterAsync>g__Awaited|26_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, object state, bool isCompleted)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ExceptionContextSealed context)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(ref State next, ref Scope scope, ref object state, ref bool isCompleted)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextResourceFilter>g__Awaited|25_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, object state, bool isCompleted)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ResourceExecutedContextSealed context)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(ref State next, ref Scope scope, ref object state, ref bool isCompleted)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeFilterPipelineAsync>g__Awaited|20_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, object state, bool isCompleted)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Logged|17_1(ResourceInvoker invoker)
Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Logged|17_1(ResourceInvoker invoker)
Microsoft.AspNetCore.Routing.EndpointMiddleware.<Invoke>g__AwaitRequestTask|7_0(Endpoint endpoint, Task requestTask, ILogger logger)
Volo.Abp.AspNetCore.Serilog.AbpSerilogMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
Microsoft.AspNetCore.Builder.UseMiddlewareExtensions+InterfaceMiddlewareBinder+<>c__DisplayClass2_0+<<CreateMiddleware>b__0>d.MoveNext()
Volo.Abp.AspNetCore.Auditing.AbpAuditingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
Volo.Abp.AspNetCore.Auditing.AbpAuditingMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
Microsoft.AspNetCore.Builder.UseMiddlewareExtensions+InterfaceMiddlewareBinder+<>c__DisplayClass2_0+<<CreateMiddleware>b__0>d.MoveNext()
Swashbuckle.AspNetCore.SwaggerUI.SwaggerUIMiddleware.Invoke(HttpContext httpContext)
Swashbuckle.AspNetCore.Swagger.SwaggerMiddleware.Invoke(HttpContext httpContext, ISwaggerProvider swaggerProvider)
Microsoft.AspNetCore.Authorization.AuthorizationMiddleware.Invoke(HttpContext context)
Volo.Abp.AspNetCore.Security.Claims.AbpDynamicClaimsMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
Microsoft.AspNetCore.Builder.UseMiddlewareExtensions+InterfaceMiddlewareBinder+<>c__DisplayClass2_0+<<CreateMiddleware>b__0>d.MoveNext()
Volo.Abp.AspNetCore.Uow.AbpUnitOfWorkMiddleware.InvokeAsync(HttpContex
I have a running ABP website that does not support multi-tenancy. How should I add the multi-tenancy feature to this website?
We are building a multi-tenancy project and hope to enable the same account to switch between tenants, with the account having different roles in different tenants. How can this be achieved?
I have created a CRUD page, and I added a logic to check for the delete button:
        [Authorize(TappPermissions.TappOrganizations.Delete)]
        public override async Task DeleteAsync(Guid id)
        {
            var users = await _tappOrganizationUsersAppService.GetListAsync(new GetTappOrganizationUsersInput()
            {
                TappOrganization = id,
                MaxResultCount = 1
            });

            if (users.Items.Any())
                throw new Exception("This organization can't be deleted because it has users associated with it.");

            await _tappOrganizationRepository.DeleteAsync(id);
        }

and I am trying to show the exception message on this pop up window. how can I do that? thanks
I published the site recently and had my co-workers test, they found three strange bugs that I can't repeat:

this happened when saving a form
2.
 on register page, we didn't enable google recaptcha, again, I can't repeat this myself.
any suggestions to debug?
C:\Users\songh>abp suite [22:33:52 INF] You are running the second generation of the ABP CLI. If you're interested in the legacy CLI, see https://abp.io/new-cli Starting Suite v9.0.3 ... Opening http://localhost:3000 Press Ctrl+C to shut down. [22:34:11 ERR] ---------- RemoteServiceErrorInfo ---------- { "code": null, "message": "An internal error occurred during your request!", "details": null, "data": null, "validationErrors": null }
[22:34:11 ERR] Could not load file or assembly 'Volo.Abp.Core, Version=9.0.4.0, Culture=neutral, PublicKeyToken=null'. The system cannot find the file specified.
System.IO.FileNotFoundException: Could not load file or assembly 'Volo.Abp.Core, Version=9.0.4.0, Culture=neutral, PublicKeyToken=null'. The system cannot find the file specified.
File name: 'Volo.Abp.Core, Version=9.0.4.0, Culture=neutral, PublicKeyToken=null'
at System.Reflection.RuntimeAssembly.GetExportedTypes()
at Volo.Abp.Suite.Areas.AbpSuite.CrudPageGenerator.Commands.CrudPageGenerator.WOwavQr6MQ(Solution , EntityModel )
at Volo.Abp.Suite.Areas.AbpSuite.CrudPageGenerator.Commands.CrudPageGenerator.tAkaZc7Krj(Solution , EntityModel )
at Volo.Abp.Suite.Areas.AbpSuite.CrudPageGenerator.Commands.CrudPageGenerator.GenerateAsync(EntityModel entity, Solution solution, EntityModel masterEntity, List1 navigationConnections) at Volo.Abp.Suite.Controllers.CrudPageGeneratorController.SaveAndGenerateEntityAsync(Guid solutionId, EntityModel entity) at lambda_method2028(Closure, Object) at Microsoft.AspNetCore.Mvc.Infrastructure.ActionMethodExecutor.TaskOfActionResultExecutor.Execute(ActionContext actionContext, IActionResultTypeMapper mapper, ObjectMethodExecutor executor, Object controller, Object[] arguments) at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeActionMethodAsync>g__Awaited|12_0(ControllerActionInvoker invoker, ValueTask1 actionResultValueTask)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeNextActionFilterAsync>g__Awaited|10_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Rethrow(ActionExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeInnerFilterAsync>g__Awaited|13_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextExceptionFilterAsync>g__Awaited|26_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
having a very strange bug when I tried to generate CRUD page after I upgraded to 9.0.4, my solution can be built successfully. I even downgraded the abp suite and my solution back to 9.0.3, the error is still here.
pls help
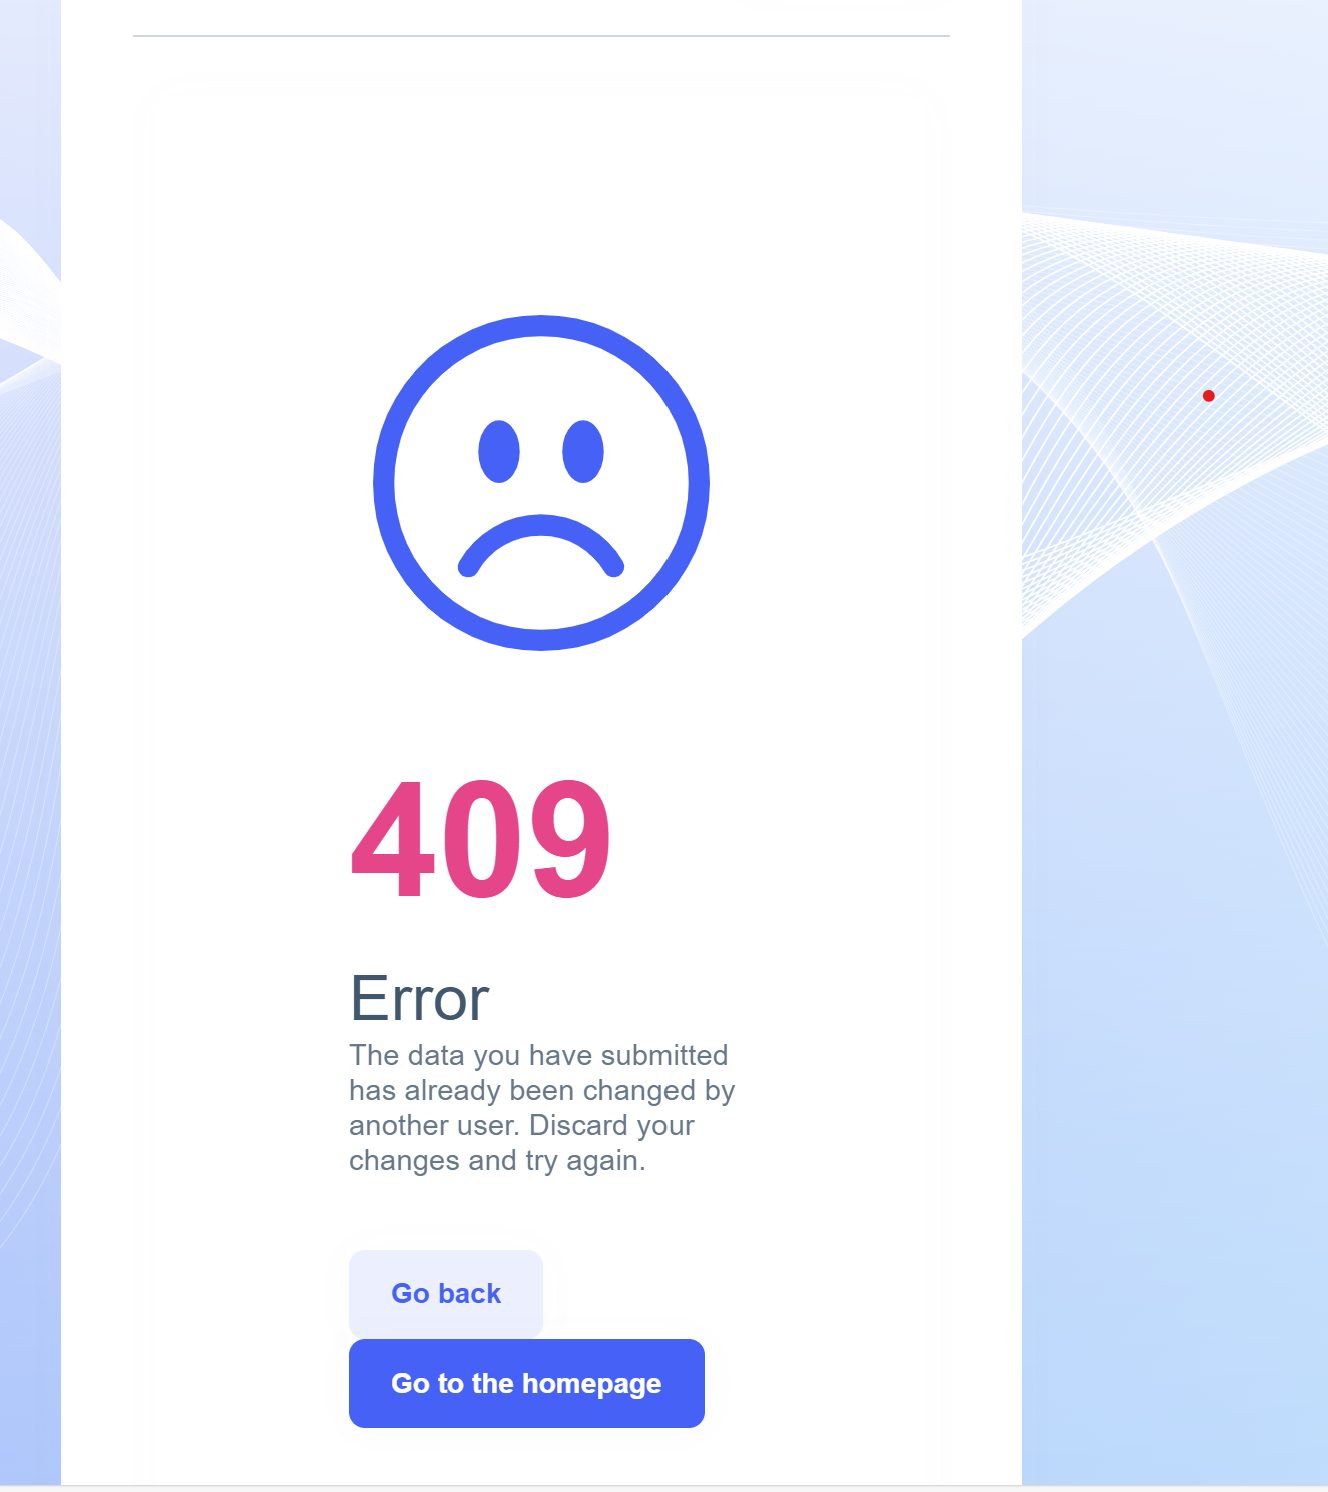
we want to use try catch to wrap this kind of exception, so that instead of showing a new page with the error, we want to just refresh the page and show a pop up so that it's easier for users to understand, can you give me some direction? I tried to use try catch, it doesn't catch the exception, but it still shows this 409 error, any suggestion?
or if what I said doesn't make sense, is there a way to get the orignial link(the destination where the go back button leads), and **automatically redirect ** users to the original link and showing a pop up alert saying("the data has een changed by another user... ") instead of letting them to choose go back or go to the homepage







