I wnt to disable Inboxes and outboxes behaviour for distributed bus
ABP Framework version: 9.1.1
Template: Microservice (with multi-tenancy)
When creating a new tenant in a microservice template, the admin user is sometimes created and sometimes not. The behavior is non-deterministic.
Root cause analysis:
In the Identity Service, there are ~7 registered IDistributedEventHandler<TenantCreatedEto> implementations — one from our custom IdentityServiceDatabaseMigrationEventHandler (which seeds the admin user) and 6 from ABP's built-in EF Core modules (SaasEntityFrameworkCoreModule, AbpPermissionManagementEntityFrameworkCoreModule, AbpFeatureManagementEntityFrameworkCoreModule, AbpSettingManagementEntityFrameworkCoreModule, AbpIdentityProEntityFrameworkCoreModule, AbpOpenIddictProEntityFrameworkCoreModule).
When a TenantCreatedEto event is received, all 7 handlers are dispatched nearly simultaneously (within milliseconds). Each handler calls MigrateDatabaseSchemaAsync(), which attempts to acquire a distributed lock via Redis. Only one handler can acquire the lock at a time — the remaining 6 time out and throw an exception.
In the custom handler's HandleEventAsync override, both MigrateDatabaseSchemaAsync() and the admin seeding (_dataSeeder.SeedAsync()) are wrapped in a single try/catch. If the distributed lock times out during migration, the entire block fails — including the admin user seeding. The exception is caught by HandleErrorTenantCreatedAsync which does not rethrow, so the inbox processor considers the event "processed" and does not retry.
Evidence from AbpEventInbox table:
Each tenant creation generates 7 inbox records with the same MessageId, all marked as Processed = true. Example for tenant "lbb":
Impact: In a shared-database scenario, the admin user is intermittently not created for new tenants, making the tenant unusable.
Expected behavior: The admin user should always be created regardless of distributed lock contention, since for shared-database tenants the schema migration is unnecessary (the schema already exists from the host migration).
create a new tenant don't create admin user
CAn I create an health check to verify the connection to rabbitmq
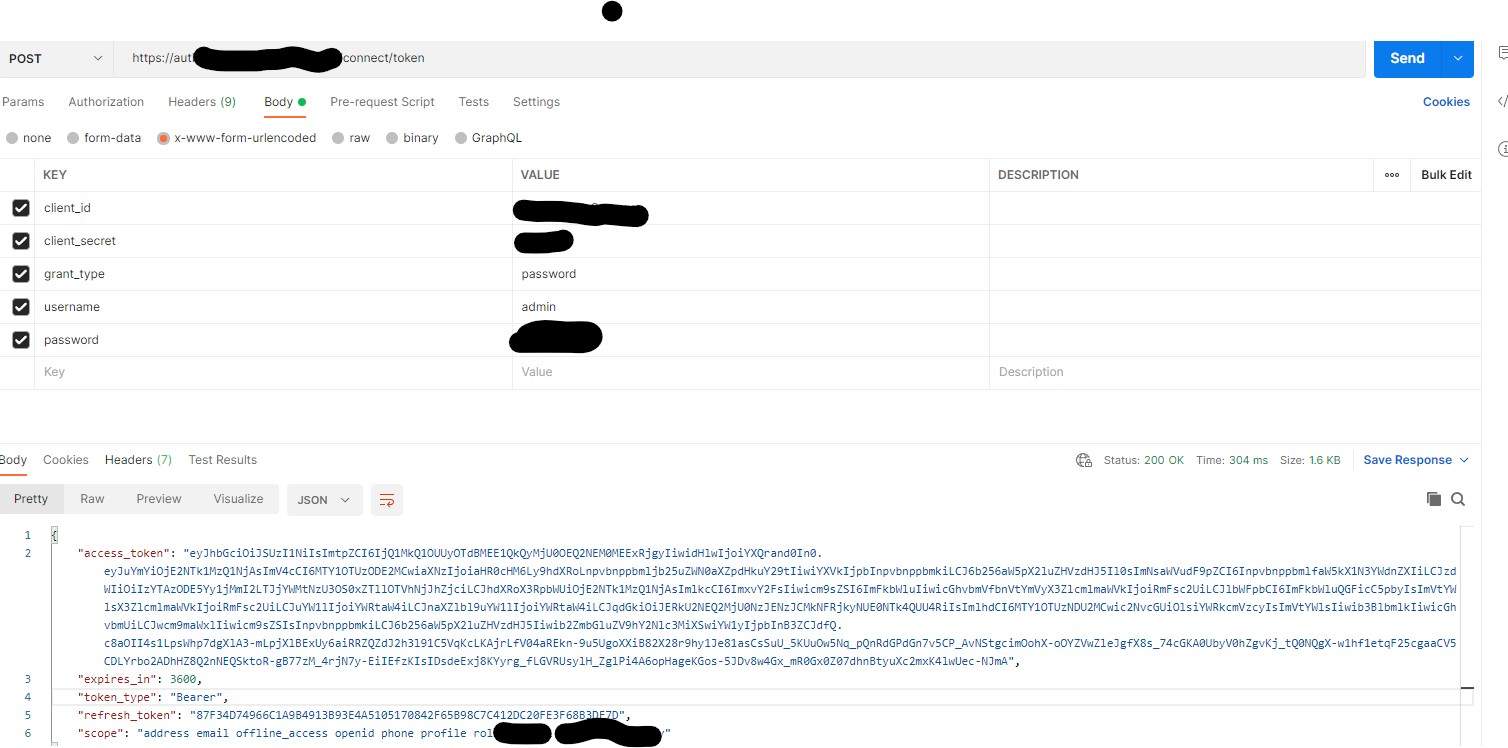
Hi, I need to access to my API form a third system using he bearer token auth method. I've created a new client, add the API scope, assign grant types password and authorization_code and create a shared secret. I'ma able to login to Identity and obtain a new access_token like that
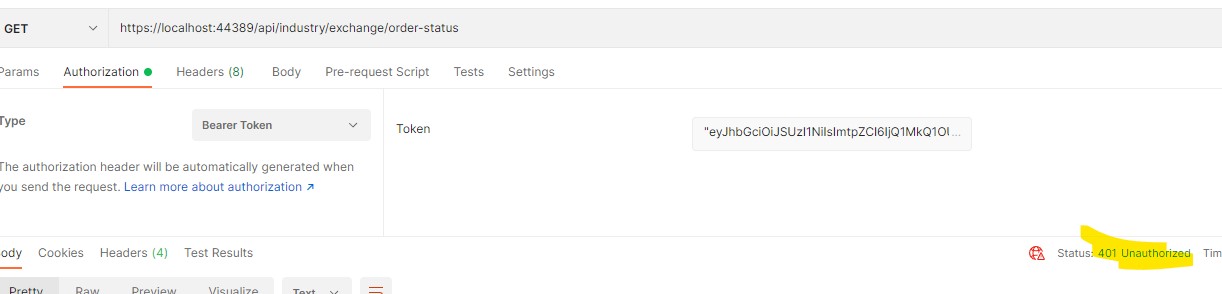
I try to make a new request to an Authorized controller and I get the error 401
the log of API:
[15:49:35 INF] Bearer was not authenticated. Failure message: No SecurityTokenValidator available for token.
[15:49:35 INF] Bearer was not authenticated. Failure message: No SecurityTokenValidator available for token.
[15:49:35 INF] Authorization failed. These requirements were not met:
DenyAnonymousAuthorizationRequirement: Requires an authenticated user.
[15:49:35 INF] AuthenticationScheme: Bearer was challenged.'
the log of Identity:
2022-08-03 15:49:20.681 +02:00 [INF] Try to use LDAP for external authentication
2022-08-03 15:49:20.684 +02:00 [WRN] Ldap login feature is not enabled!
2022-08-03 15:49:20.731 +02:00 [INF] Credentials validated for username: admin
2022-08-03 15:49:20.750 +02:00 [INF] {"Username":"admin","Provider":null,"ProviderUserId":null,"SubjectId":"3a03819c-c2b6-2cac-7579-1e9e95a62af7","DisplayName":null,"Endpoint":"Token","ClientId":"******_ind_Swagger","Category":"Authentication","Name":"User Login Success","EventType":"Success","Id":1000,"Message":null,"ActivityId":"800109bd-0001-d900-b63f-84710c7967bb","TimeStamp":"2022-08-03T13:49:20.0000000Z","ProcessId":20084,"LocalIpAddress":"","RemoteIpAddress":"","$type":"UserLoginSuccessEvent"}
2022-08-03 15:49:20.750 +02:00 [INF] Token request validation success, {"ClientId":"******_ind_Swagger","ClientName":"******_ind_Swagger","GrantType":"password","Scopes":"address email offline_access openid phone profile role ****** ******_industry","AuthorizationCode":"********","RefreshToken":"********","UserName":"admin","AuthenticationContextReferenceClasses":null,"Tenant":null,"IdP":null,"Raw":{"client_id":"******_ind_Swagger","client_secret":"***REDACTED***","grant_type":"password","username":"admin","password":"***REDACTED***"},"$type":"TokenRequestValidationLog"}
2022-08-03 15:49:20.767 +02:00 [INF] {"ClientId":"******_ind_Swagger","ClientName":"******_ind_Swagger","RedirectUri":null,"Endpoint":"Token","SubjectId":"3a03819c-c2b6-2cac-7579-1e9e95a62af7","Scopes":"address email offline_access openid phone profile role ****** ******_industry","GrantType":"password","Tokens":[{"TokenType":"refresh_token","TokenValue":"****DE7D","$type":"Token"},{"TokenType":"access_token","TokenValue":"****NJmA","$type":"Token"}],"Category":"Token","Name":"Token Issued Success","EventType":"Success","Id":2000,"Message":null,"ActivityId":"800109bd-0001-d900-b63f-84710c7967bb","TimeStamp":"2022-08-03T13:49:20.0000000Z","ProcessId":20084,"LocalIpAddress":":443","RemoteIpAddress":"","$type":"TokenIssuedSuccessEvent"}
2022-08-03 15:49:20.769 +02:00 [INF] Request finished HTTP/1.1 POST https://auth.************.com/connect/token application/x-www-form-urlencoded 108 - 200 - application/json;+charset=UTF-8 156.5627ms
2022-08-03 15:50:42.645 +02:00 [INF] Request starting HTTP/2 GET https://auth.************.com/connect/authorize?response_type=code&client_id=******_ind_Swagger&redirect_uri=https%3A%2F%2Flocalhost%3A44389%2Fswagger%2Foauth2-redirect.html&scope=******_industry&state=V2VkIEF1ZyAwMyAyMDIyIDE1OjUwOjQyIEdNVCswMjAwIChPcmEgbGVnYWxlIGRlbGzigJlFdXJvcGEgY2VudHJhbGUp - -
2022-08-03 15:50:42.730 +02:00 [INF] Invoking IdentityServer endpoint: IdentityServer4.Endpoints.AuthorizeEndpoint for /connect/authorize
2022-08-03 15:50:42.759 +02:00 [INF] {"ClientId":"******_ind_Swagger","ClientName":"******_ind_Swagger","RedirectUri":"https://localhost:44389/swagger/oauth2-redirect.html","Endpoint":"Authorize","SubjectId":"3a03819c-c2b6-2cac-7579-1e9e95a62af7","Scopes":"******_industry","GrantType":"authorization_code","Tokens":[{"TokenType":"code","TokenValue":"****21B5","$type":"Token"}],"Category":"Token","Name":"Token Issued Success","EventType":"Success","Id":2000,"Message":null,"ActivityId":"80003e65-0001-8800-b63f-84710c7967bb","TimeStamp":"2022-08-03T13:50:42.0000000Z","ProcessId":20084,"LocalIpAddress":":443","RemoteIpAddress":"","$type":"TokenIssuedSuccessEvent"}
2022-08-03 15:50:42.764 +02:00 [INF] Request finished HTTP/2 GET https://auth.************.com/connect/authorize?response_type=code&client_id=******_ind_Swagger&redirect_uri=https%3A%2F%2Flocalhost%3A44389%2Fswagger%2Foauth2-redirect.html&scope=******_industry&state=V2VkIEF1ZyAwMyAyMDIyIDE1OjUwOjQyIEdNVCswMjAwIChPcmEgbGVnYWxlIGRlbGzigJlFdXJvcGEgY2VudHJhbGUp - - - 302 - - 118.8755ms
2022-08-03 15:50:42.916 +02:00 [INF] Request starting HTTP/2 OPTIONS https://auth.************.com/connect/token - -
2022-08-03 15:50:42.916 +02:00 [INF] CORS policy execution successful.
Thanks




