Hi,
Sorry for being late. I will let the Angular team answer your question.
I have used [Authorize] in my controller class and method. When I try to execute the API with the invalid token, in the logs I see the error message that says invalid token or token no longer valid.
What's the Angular-side error message? It should prompt unauthorized
Hi,
Could you share the full steps to reproduce? i will check it.
Hi
Chat feature is disabled by default, you need to enable it https://abp.io/docs/latest/modules/chat#manage-chat-feature
Hi,
Could you share the * Steps to reproduce the issue:
Hi,
You can add your controller to HTTPApi.Host project
HI,
i could not reproduce the problem.
Since I don't have an azure subscription I use a local k8s environment
My steps
Create a new ms template
README.md under k8s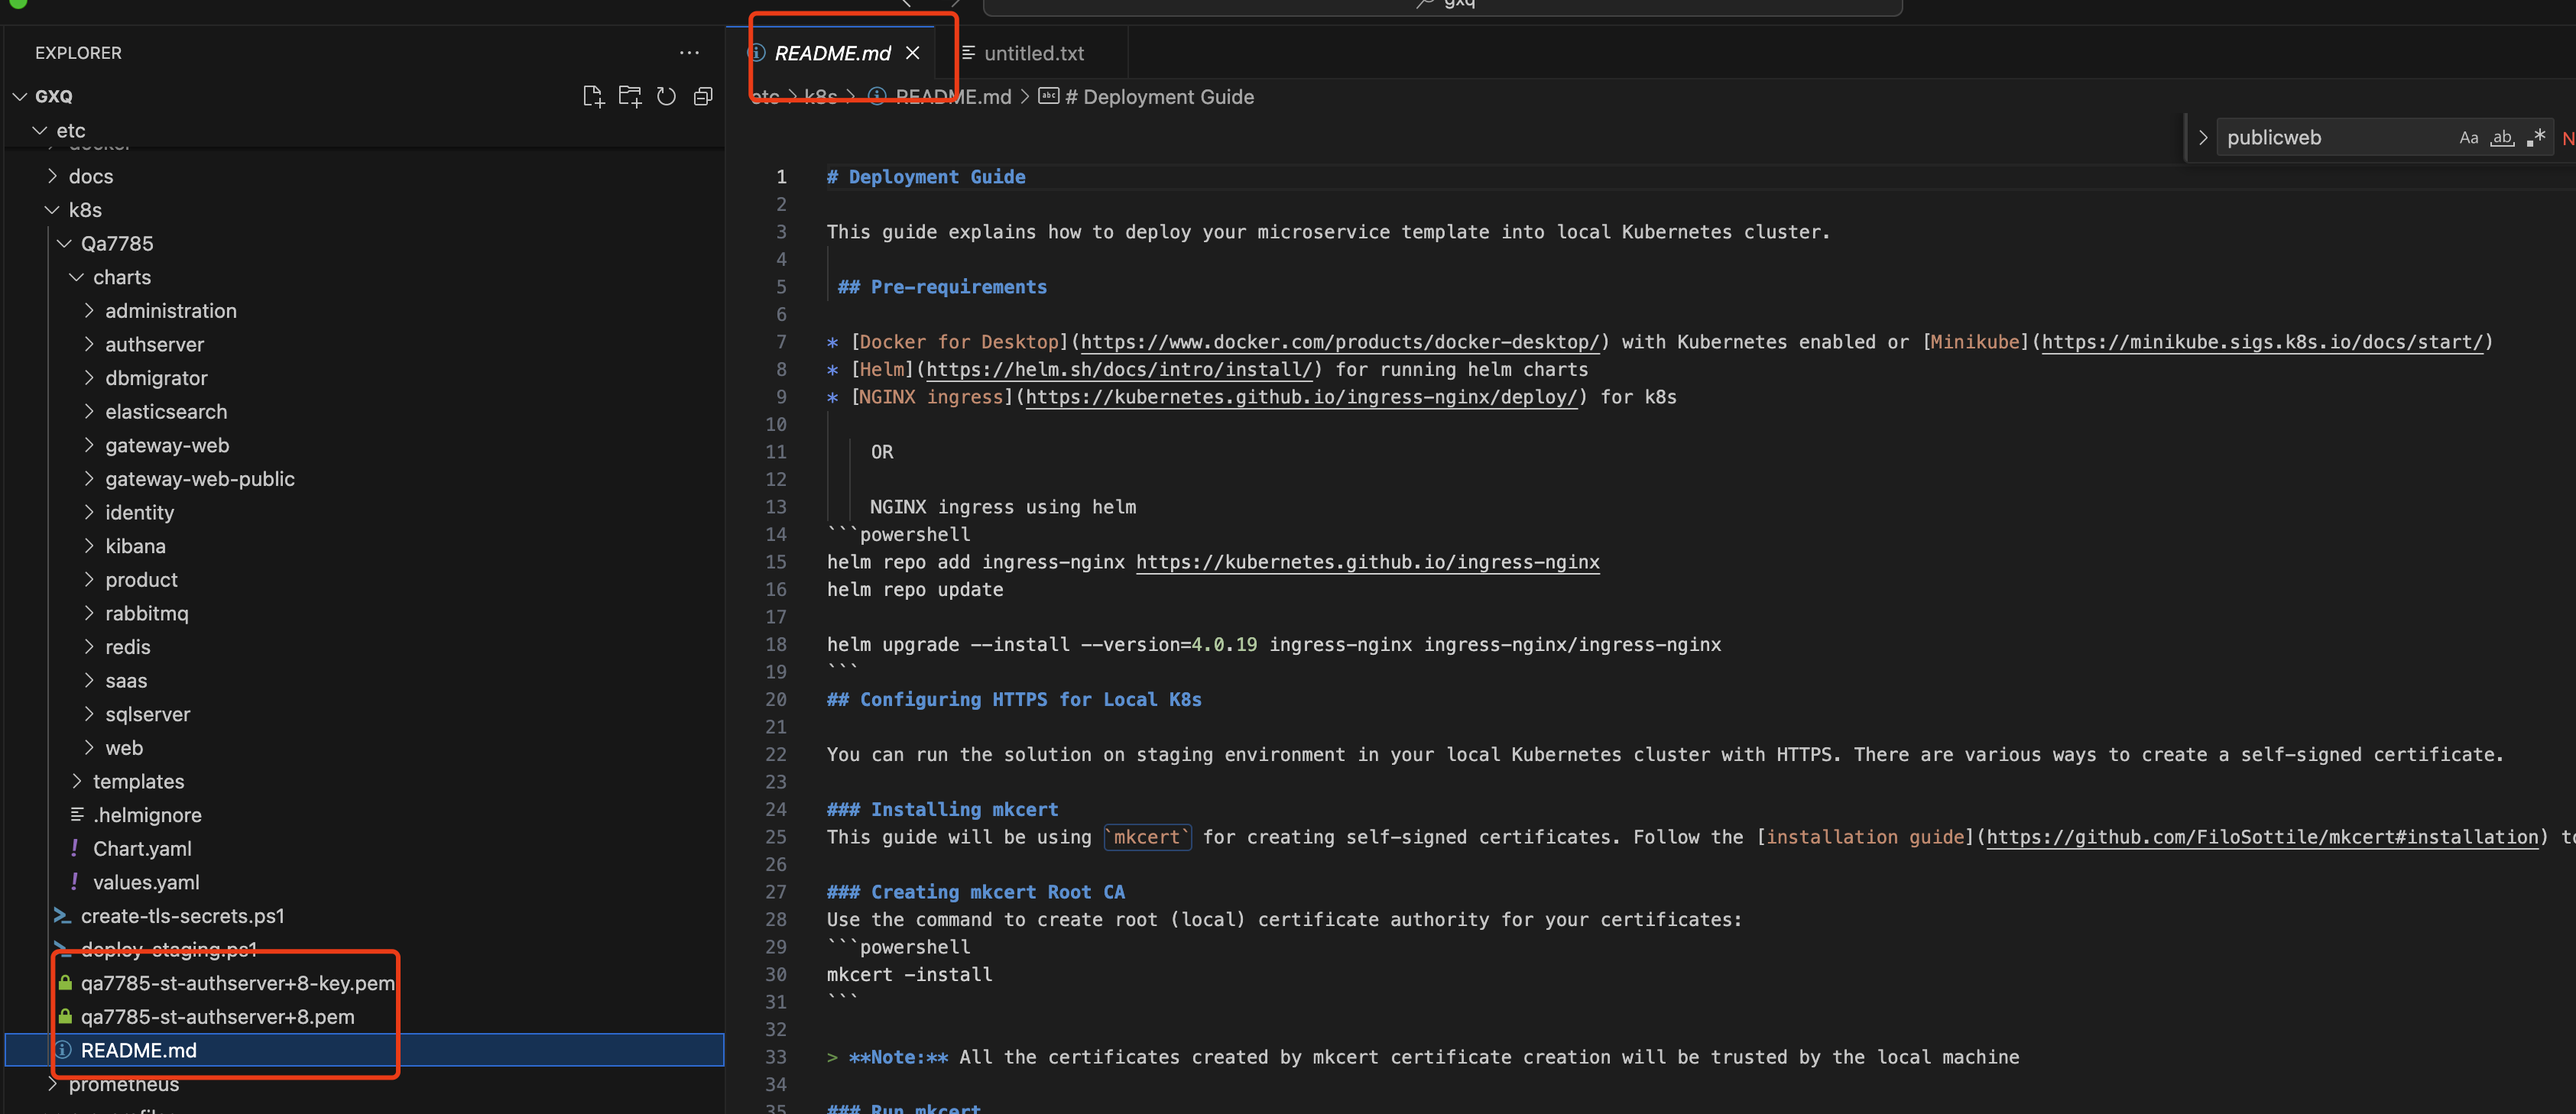
2024-09-12 17:09:45 [09:09:45 INF] Request starting HTTP/1.1 POST http://qa7785-st-authserver/Account/Login?ReturnUrl=%2Fconnect%2Fauthorize%3Fclient_id%3DWeb%26redirect_uri%3Dhttps%253A%252F%252Fqa7785-st-web%252Fsignin-oidc%26response_type%3Dcode%2520id_token%26scope%3Dopenid%2520profile%2520roles%2520email%2520phone%2520AccountService%2520IdentityService%2520AdministrationService%2520SaasService%2520ProductService%26response_mode%3Dform_post%26nonce%3D638617289811389097.MjhmZjk3MTYtN2EyOS00N2U1LWFiOGYtODhkNGMwODUxYmZjMjNiYzM1ZTQtNTM5Yi00MmY1LWFjYjUtZDM2NjZhZmRhYjM3%26state%3DCfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf%26x-client-SKU%3DID_NET6_0%26x-client-ver%3D6.15.1.0 application/x-www-form-urlencoded 291
2024-09-12 17:09:45 [09:09:45 INF] CORS policy execution failed.
2024-09-12 17:09:45 [09:09:45 INF] Request origin https://qa7785-st-authserver does not have permission to access the resource.
2024-09-12 17:09:45 [09:09:45 INF] Executing endpoint '/Account/Login'
2024-09-12 17:09:45 [09:09:45 INF] Route matched with {page = "/Account/Login", area = "", action = "", controller = ""}. Executing page /Account/Login
2024-09-12 17:09:45 [09:09:45 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
2024-09-12 17:09:45 [09:09:45 INF] Executing handler method Volo.Abp.Account.Public.Web.Pages.Account.LoginModel.OnPostAsync - ModelState is Valid
2024-09-12 17:09:45 [09:09:45 INF] Try to use LDAP for external authentication
2024-09-12 17:09:45 [09:09:45 WRN] Ldap login feature is not enabled!
2024-09-12 17:09:45 [09:09:45 INF] Try to use OAUTH for external authentication
2024-09-12 17:09:45 [09:09:45 WRN] OAuth login feature is not enabled!
2024-09-12 17:09:45 [09:09:45 INF] AuthenticationScheme: Identity.Application signed in.
2024-09-12 17:09:45 [09:09:45 INF] Executed handler method OnPostAsync, returned result Microsoft.AspNetCore.Mvc.RedirectResult.
2024-09-12 17:09:45 [09:09:45 INF] Executing RedirectResult, redirecting to /connect/authorize?client_id=Web&redirect_uri=https%3A%2F%2Fqa7785-st-web%2Fsignin-oidc&response_type=code%20id_token&scope=openid%20profile%20roles%20email%20phone%20AccountService%20IdentityService%20AdministrationService%20SaasService%20ProductService&response_mode=form_post&nonce=638617289811389097.MjhmZjk3MTYtN2EyOS00N2U1LWFiOGYtODhkNGMwODUxYmZjMjNiYzM1ZTQtNTM5Yi00MmY1LWFjYjUtZDM2NjZhZmRhYjM3&state=CfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf&x-client-SKU=ID_NET6_0&x-client-ver=6.15.1.0.
2024-09-12 17:09:45 [09:09:45 INF] Executed page /Account/Login in 226.1494ms
2024-09-12 17:09:45 [09:09:45 INF] Executed endpoint '/Account/Login'
2024-09-12 17:09:45 [09:09:45 INF] Request finished HTTP/1.1 POST http://qa7785-st-authserver/Account/Login?ReturnUrl=%2Fconnect%2Fauthorize%3Fclient_id%3DWeb%26redirect_uri%3Dhttps%253A%252F%252Fqa7785-st-web%252Fsignin-oidc%26response_type%3Dcode%2520id_token%26scope%3Dopenid%2520profile%2520roles%2520email%2520phone%2520AccountService%2520IdentityService%2520AdministrationService%2520SaasService%2520ProductService%26response_mode%3Dform_post%26nonce%3D638617289811389097.MjhmZjk3MTYtN2EyOS00N2U1LWFiOGYtODhkNGMwODUxYmZjMjNiYzM1ZTQtNTM5Yi00MmY1LWFjYjUtZDM2NjZhZmRhYjM3%26state%3DCfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf%26x-client-SKU%3DID_NET6_0%26x-client-ver%3D6.15.1.0 application/x-www-form-urlencoded 291 - 302 0 - 292.3347ms
2024-09-12 17:09:45 [09:09:45 INF] Request starting HTTP/1.1 GET http://qa7785-st-authserver/connect/authorize?client_id=Web&redirect_uri=https%3A%2F%2Fqa7785-st-web%2Fsignin-oidc&response_type=code%20id_token&scope=openid%20profile%20roles%20email%20phone%20AccountService%20IdentityService%20AdministrationService%20SaasService%20ProductService&response_mode=form_post&nonce=638617289811389097.MjhmZjk3MTYtN2EyOS00N2U1LWFiOGYtODhkNGMwODUxYmZjMjNiYzM1ZTQtNTM5Yi00MmY1LWFjYjUtZDM2NjZhZmRhYjM3&state=CfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf&x-client-SKU=ID_NET6_0&x-client-ver=6.15.1.0 - -
2024-09-12 17:09:45 [09:09:45 INF] The request URI matched a server endpoint: Authorization.
2024-09-12 17:09:45 [09:09:45 INF] The authorization request was successfully extracted: {
2024-09-12 17:09:45   "client_id": "Web",
2024-09-12 17:09:45   "redirect_uri": "https://qa7785-st-web/signin-oidc",
2024-09-12 17:09:45   "response_type": "code id_token",
2024-09-12 17:09:45   "scope": "openid profile roles email phone AccountService IdentityService AdministrationService SaasService ProductService",
2024-09-12 17:09:45   "response_mode": "form_post",
2024-09-12 17:09:45   "nonce": "638617289811389097.MjhmZjk3MTYtN2EyOS00N2U1LWFiOGYtODhkNGMwODUxYmZjMjNiYzM1ZTQtNTM5Yi00MmY1LWFjYjUtZDM2NjZhZmRhYjM3",
2024-09-12 17:09:45   "state": "CfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf",
2024-09-12 17:09:45   "x-client-SKU": "ID_NET6_0",
2024-09-12 17:09:45   "x-client-ver": "6.15.1.0"
2024-09-12 17:09:45 }.
2024-09-12 17:09:45 [09:09:45 INF] The authorization request was successfully validated.
2024-09-12 17:09:45 [09:09:45 INF] Executing endpoint 'Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
2024-09-12 17:09:45 [09:09:45 INF] Route matched with {action = "Handle", controller = "Authorize", area = "", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.IActionResult] HandleAsync() on controller Volo.Abp.OpenIddict.Controllers.AuthorizeController (Volo.Abp.OpenIddict.AspNetCore).
2024-09-12 17:09:45 [09:09:45 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
2024-09-12 17:09:45 [09:09:45 INF] Executing SignInResult with authentication scheme (OpenIddict.Server.AspNetCore) and the following principal: System.Security.Claims.ClaimsPrincipal.
2024-09-12 17:09:45 [09:09:45 INF] The authorization response was successfully returned to 'https://qa7785-st-web/signin-oidc' using the form post response mode: {
2024-09-12 17:09:45   "code": "[redacted]",
2024-09-12 17:09:45   "id_token": "[redacted]",
2024-09-12 17:09:45   "state": "CfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf",
2024-09-12 17:09:45   "iss": "http://qa7785-st-authserver/"
2024-09-12 17:09:45 }.
2024-09-12 17:09:45 [09:09:45 INF] Executed action Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore) in 161.4656ms
2024-09-12 17:09:45 [09:09:45 INF] Executed endpoint 'Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
2024-09-12 17:09:45 [09:09:45 INF] Request finished HTTP/1.1 GET http://qa7785-st-authserver/connect/authorize?client_id=Web&redirect_uri=https%3A%2F%2Fqa7785-st-web%2Fsignin-oidc&response_type=code%20id_token&scope=openid%20profile%20roles%20email%20phone%20AccountService%20IdentityService%20AdministrationService%20SaasService%20ProductService&response_mode=form_post&nonce=638617289811389097.MjhmZjk3MTYtN2EyOS00N2U1LWFiOGYtODhkNGMwODUxYmZjMjNiYzM1ZTQtNTM5Yi00MmY1LWFjYjUtZDM2NjZhZmRhYjM3&state=CfDJ8IEEMWWN7RFAlJWhi5LTjUOus_I6dy7aKa8OWYlv0_y0DM7cVFW90ndOAR2uSrJ53XAsZrXR0edhBqEcu5QJHz4_3somqIxc9Oo1AgC_IKKMr8TFvmzCm1_gDA-pw778cTth5lE0upTO8BakV9gbi8SbxJHOTHrlcxiYylDJK0X8OLqgRCZQYncU4ncZlvD_NupH4fvEe-2gvwE50KFQ5CtrnVPaxd1NfnffJid7twGQksEUKaxxj6nvfwtkouhm86MD6mARo_1O4Tq4PYA4DtzVPlfI4BAf-iPZ3sHbYYZf&x-client-SKU=ID_NET6_0&x-client-ver=6.15.1.0 - - - 200 1972 text/html;charset=UTF-8 184.2490ms
2024-09-12 17:09:45 [09:09:45 INF] Request starting HTTP/1.1 POST http://qa7785-st-authserver/connect/token application/x-www-form-urlencoded 171
2024-09-12 17:09:45 [09:09:45 INF] The request URI matched a server endpoint: Token.
2024-09-12 17:09:45 [09:09:45 INF] The token request was successfully extracted: {
2024-09-12 17:09:45   "client_id": "Web",
2024-09-12 17:09:45   "client_secret": "[redacted]",
2024-09-12 17:09:45   "code": "[redacted]",
2024-09-12 17:09:45   "grant_type": "authorization_code",
2024-09-12 17:09:45   "redirect_uri": "https://qa7785-st-web/signin-oidc"
2024-09-12 17:09:45 }.
2024-09-12 17:09:45 [09:09:45 INF] The token request was successfully validated.
2024-09-12 17:09:45 [09:09:45 INF] Executing endpoint 'Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
2024-09-12 17:09:45 [09:09:45 INF] Route matched with {action = "Handle", controller = "Token", area = "", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.IActionResult] HandleAsync() on controller Volo.Abp.OpenIddict.Controllers.TokenController (Volo.Abp.OpenIddict.AspNetCore).
2024-09-12 17:09:45 [09:09:45 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy
2024-09-12 17:09:45 [09:09:45 INF] Executing SignInResult with authentication scheme (OpenIddict.Server.AspNetCore) and the following principal: System.Security.Claims.ClaimsPrincipal.
2024-09-12 17:09:46 [09:09:46 INF] The token '5b15b949-96df-0dbb-9821-3a14f7abc213' was successfully marked as redeemed.
2024-09-12 17:09:46 [09:09:46 INF] The response was successfully returned as a JSON document: {
2024-09-12 17:09:46   "access_token": "[redacted]",
2024-09-12 17:09:46   "token_type": "Bearer",
2024-09-12 17:09:46   "expires_in": 3600,
2024-09-12 17:09:46   "scope": "openid profile roles email phone AccountService IdentityService AdministrationService SaasService ProductService",
2024-09-12 17:09:46   "id_token": "[redacted]"
2024-09-12 17:09:46 }.
2024-09-12 17:09:46 [09:09:46 INF] Executed action Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore) in 209.0545ms
2024-09-12 17:09:46 [09:09:46 INF] Executed endpoint 'Volo.Abp.OpenIddict.Controllers.TokenController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)'
2024-09-12 17:09:46 [09:09:46 INF] Request finished HTTP/1.1 POST http://qa7785-st-authserver/connect/token application/x-www-form-urlencoded 171 - 200 2779 application/json;charset=UTF-8 264.7367ms
What is the error message in logs now?
I will try deploy a ms template to the ASK cluster to reproduce the problem, could you share the full steps? thanks
Sorry I don't see any errors in the logs




