var testClientId = configurationSection["SBC_Mobile:ClientId"];
if (!testClientId.IsNullOrWhiteSpace())
{
    await CreateClientAsync(
        name: testClientId,
        scopes: commonScopes,
        grantTypes: new[] { "password", "client_credentials", "authorization_code"},
        secret: configurationSection["SBC_Mobile:ClientSecret"].Sha256(),
        requireClientSecret: true,
        redirectUri: "https://localhost:44317"
    );
}

private async Task<ApiResource> CreateApiResourceAsync(string name, IEnumerable<string> claims)
    {
        var apiResource = await _apiResourceRepository.FindByNameAsync(name);
        if (apiResource == null)
        {
            apiResource = await _apiResourceRepository.InsertAsync(
                new ApiResource(
                    _guidGenerator.Create(),
                    name,
                    name + " API"
                ),
                autoSave: true
            );
        }

        foreach (var claim in claims)
        {
            if (apiResource.FindClaim(claim) == null)
            {
                apiResource.AddUserClaim(claim);
            }
        }

        if (apiResource.FindSecret((name + "Secret").Sha256()) == null)
        {
            apiResource.AddSecret((name + "Secret").Sha256());
        }

        return await _apiResourceRepository.UpdateAsync(apiResource);
    }
Scope = "email openid profile offline_access role phone address SBC",
var response = await httpClient.Value.IntrospectTokenAsync(new TokenIntrospectionRequest
{
    Address = disco.IntrospectionEndpoint,
    ClientId = "SBC",
    ClientSecret = "SBCSecret",
    Token = token.Text,
});
var response = await httpClient.Value.RequestRefreshTokenAsync(new RefreshTokenRequest()
{
    Address = disco.TokenEndpoint,
    ClientId = clientId.Text,
    ClientSecret = secret.Text,
    RefreshToken = refreshToken.Text,
});
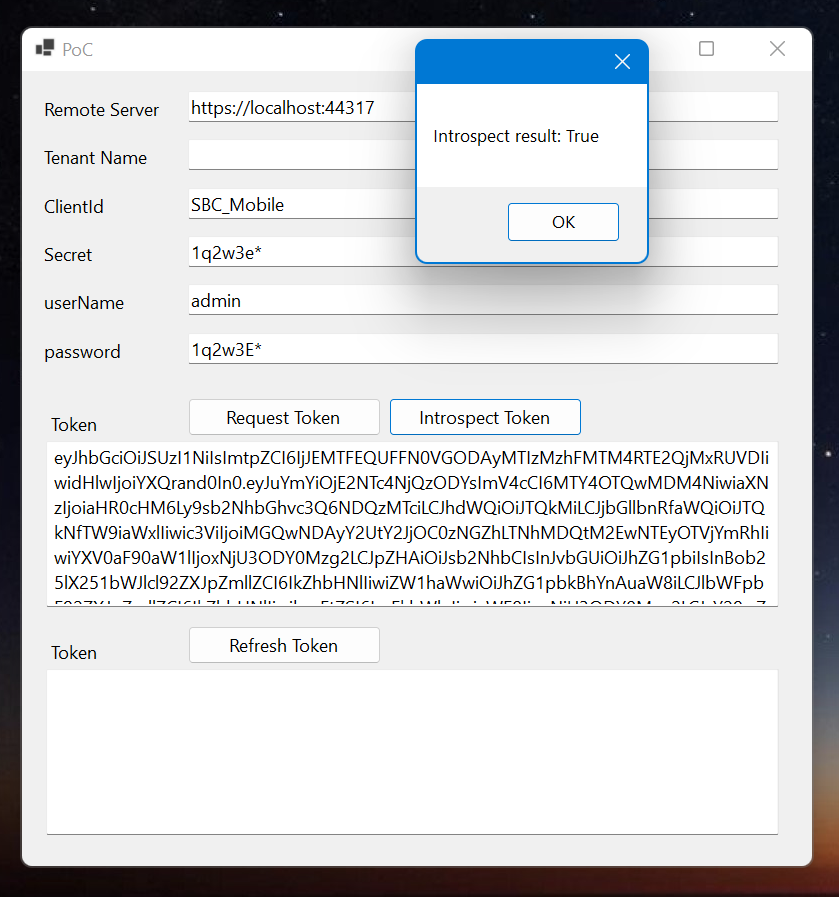
hi
The current design cannot remove these infrastructure modules.
How should we handle https://tenant1.api.getabp.net:44302/swagger/index.html for tenant1?
What do you mean?
Another thing that I found. If I update a Client (just edit, change some field, can save), it doesn't work anymore. It says that the secret is invalid. Looking at the database, table IdentityServerClientSecrets, I found that the column "Value" was modified and it has the same value as the previous record. Can you have a look at that as well?
Does this resolve the problem? https://support.abp.io/QA/Questions/3404#answer-5bd6d8f3-7f01-53fa-6050-3a05049ffeee
hi
ABP Framework version?
hi
Can you share a simple project to reproduce? liming.ma@volosoft.com
hi
---> System.Reflection.TargetInvocationException: Exception has been thrown by the target of an invocation. ---> System.MissingMethodException: Method not found: 'Void AutoMapper.IMemberConfigurationExpression
3.MapFrom(System.Linq.Expressions.Expression1<System.Func2<!0,!!0>>)'. at OtisEd.Alerts.AlertsApplicationAutoMapperProfile.<>c.<.ctor>b__0_3(IMemberConfigurationExpression3 opt)
Can you share a sample project? You can use the template project.
hi
How can I validate and refresh a token? Currently, I'm saving the date/time expiration in the session. If that is expired, I'm trying to call connect/introspect, but, no success. Same error as described on this item: https://github.com/abpframework/abp/issues/12394
Did you add a secret to the client?
https://github.com/abpframework/abp/issues/12394#issuecomment-1112961398
It is saying Grant is invalid. Besides, there is no refresh_token token in the Identity Server > Client form. I had to add a custom grant type.
What is your request? You can use the IdentityModel class library. https://identitymodel.readthedocs.io/
hi
OK, I think there will be no problem with your new computer




