hi
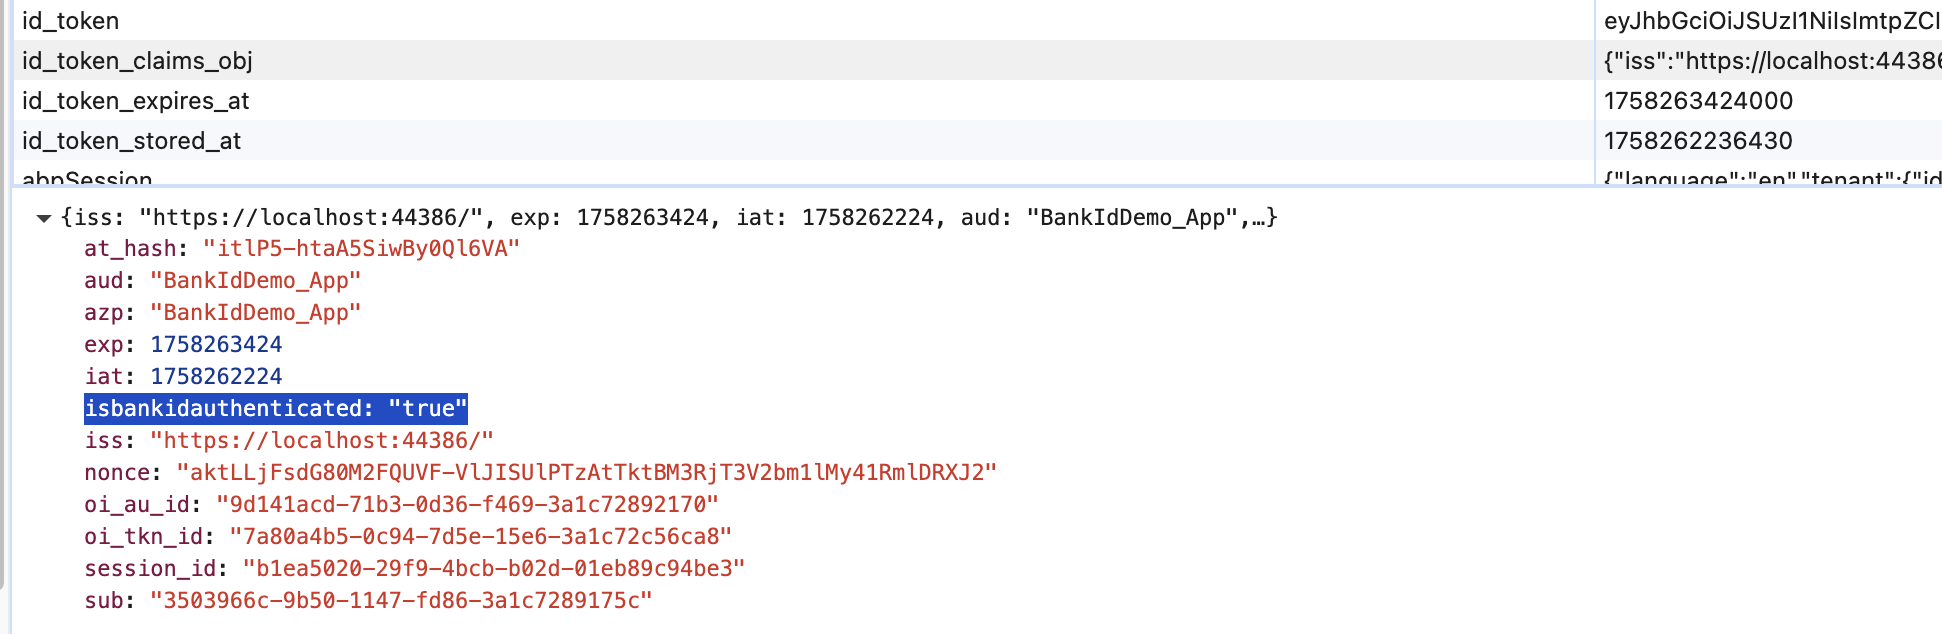
using System;
using System.Security.Claims;
using System.Threading.Tasks;
using Microsoft.AspNetCore;
using Microsoft.AspNetCore.Authentication;
using Microsoft.AspNetCore.Identity;
using OpenIddict.Abstractions;
using OpenIddict.Server;

namespace BankIdDemo;

public class BankIdOpenIddictServerHandler : IOpenIddictServerHandler<OpenIddictServerEvents.ProcessSignInContext>
{
    public static OpenIddictServerHandlerDescriptor Descriptor { get; }
        = OpenIddictServerHandlerDescriptor.CreateBuilder<OpenIddictServerEvents.ProcessSignInContext>()
            .UseSingletonHandler<BankIdOpenIddictServerHandler>()
            .SetOrder(100_000)
            .SetType(OpenIddictServerHandlerType.Custom)
            .Build();

    public async ValueTask HandleAsync(OpenIddictServerEvents.ProcessSignInContext context)
    {
        var httpContext = context.Transaction.GetHttpRequest()?.HttpContext;
        if (httpContext == null)
        {
            return;
        }

        if (context.EndpointType == OpenIddictServerEndpointType.Authorization && context.AuthorizationCodePrincipal != null)
        {
            var identity = await httpContext.AuthenticateAsync(IdentityConstants.ApplicationScheme);
            if (identity.Principal != null)
            {
                var bankIdClaim = identity.Principal.FindFirst("isbankidauthenticated");
                if (bankIdClaim != null)
                {
                    context.AuthorizationCodePrincipal?.AddClaim("isbankidauthenticated", bankIdClaim.Value);
                };
            };
        }

        if (context.EndpointType == OpenIddictServerEndpointType.Token)
        {
            if (context.AccessTokenPrincipal != null && context.IdentityTokenPrincipal != null)
            {
                var bankIdClaim = context.AccessTokenPrincipal .FindFirst("isbankidauthenticated");
                if (bankIdClaim != null)
                {
                    context.IdentityTokenPrincipal?.AddClaim("isbankidauthenticated", bankIdClaim.Value);
                }
            }
        }
    }
}
我的意思是: MVC, Blazor 还是 Angular?
hi
When I create a user on the XXXAuth side and access this user via XXXCore, the Sign Up option creates a user record in the local database, and the password field for this record is naturally left blank
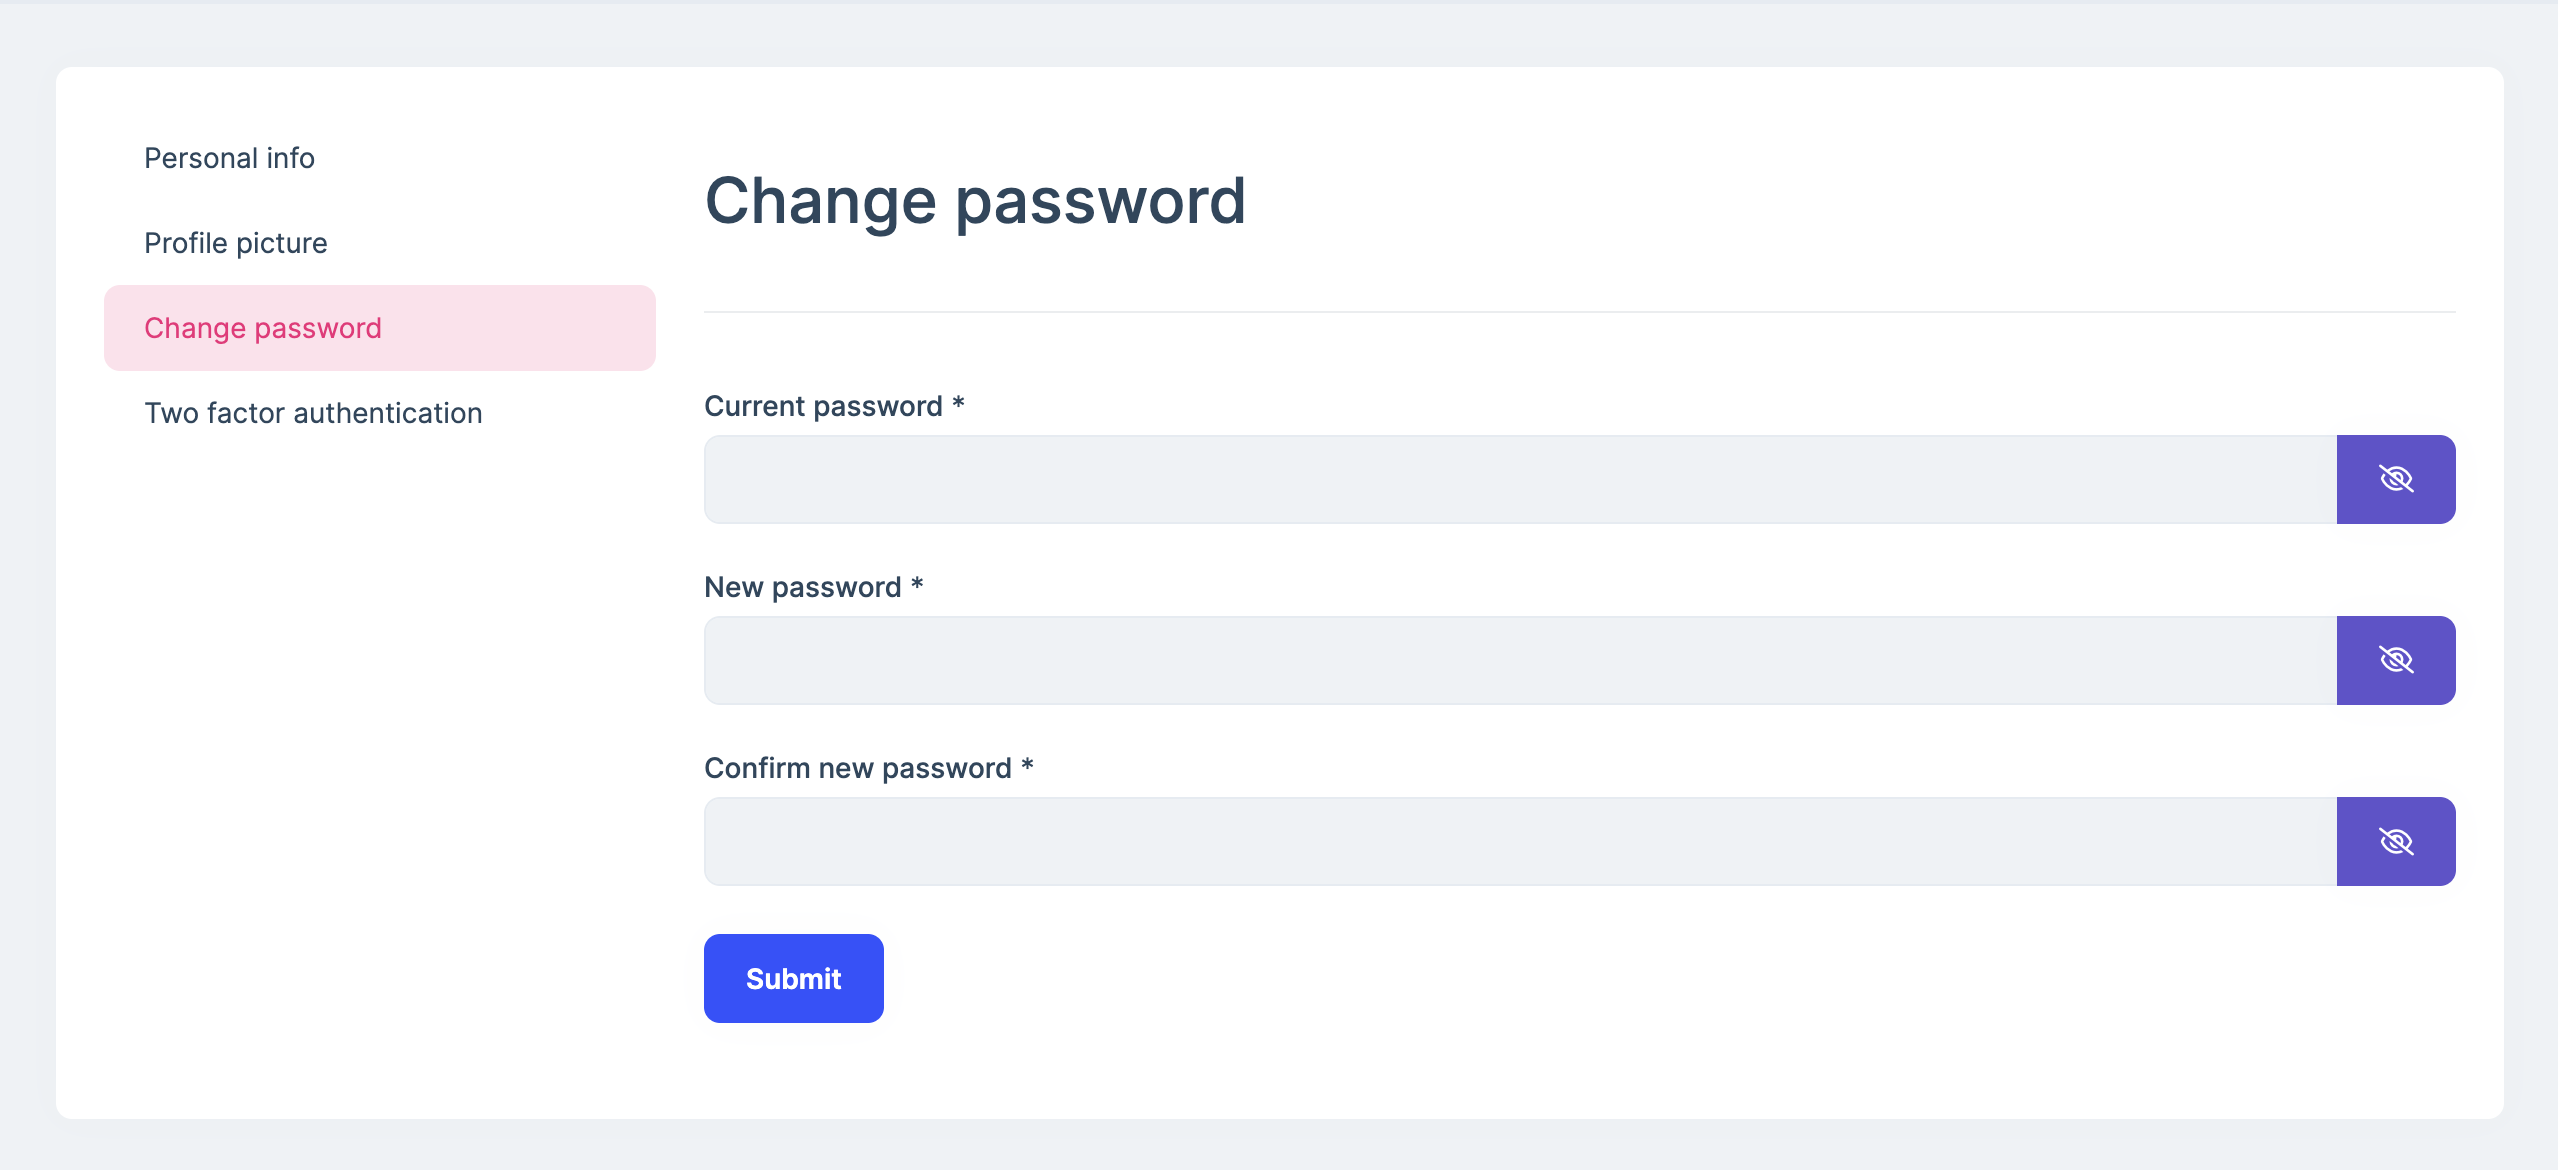
You can change your new user password in Core websites.
https://corewebsite/Account/Manage
Is there any endpoint, definition, or parameter for obtaining a token via the API?
You should use the connect/token endpoint, this is recommended.
The custom grant type also uses connect/token endpoint, and it will work.
https://abp.io/community/articles/how-to-add-a-custom-grant-type-in-openiddict.-6v0df94z#gsc.tab=0
Thanks.
Ok, Thanks.
Great : )
你的UI类型是?