hi
You need to change the log level of your website(https://pcassist-testing.premiumasp.net/).
Postman is just used to send HTTP requests (API/app/book).
We need the logs.txt of your website.
hi
Try to set Layout to null of your partial view.
@{
    Layout = null;
    PageLayout.Content.Title = L["Wizard Steps"].Value;
    PageLayout.Content.MenuItemName = HorizonERPMenus.MainWizard;
}
Set log level in your c# application.
Program.cs file.
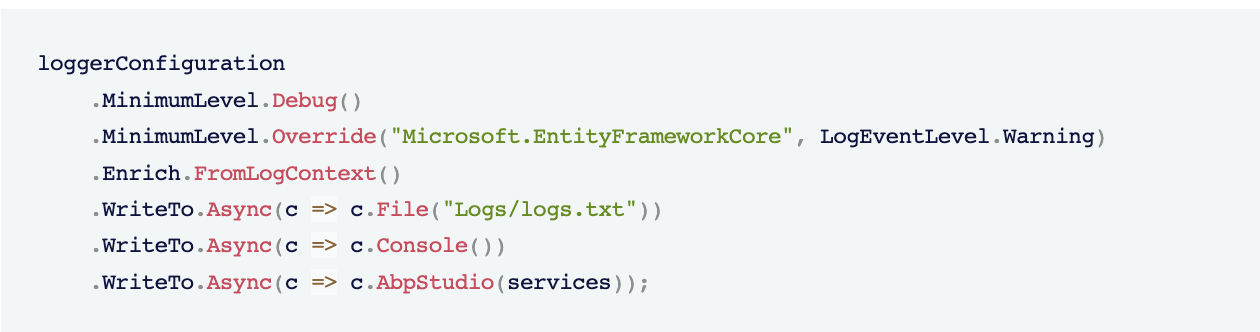
hi
api/app/book in your Postman with your access token..MinimumLevel.Debug()
loggerConfiguration
    .MinimumLevel.Debug()
    .MinimumLevel.Override("Microsoft.EntityFrameworkCore", LogEventLevel.Warning)
    .Enrich.FromLogContext()
    .WriteTo.Async(c => c.File("Logs/logs.txt"))
    .WriteTo.Async(c => c.Console())
    .WriteTo.Async(c => c.AbpStudio(services));
hi
Please share your project type.
Great : )
hi
Please share full debug logs of this request(made by postman).
https://pcassist-testing.premiumasp.net/api/app/book
liming.ma@volosoft.com
Thanks.
hi
see 3.2
Cors will check if the request header contains Origin etc..
Check the logic of CorsMiddleware
https://github.com/dotnet/aspnetcore/blob/release/9.0/src/Middleware/CORS/src/Infrastructure/CorsMiddleware.cs#L107-L110 https://github.com/dotnet/aspnetcore/blob/release/9.0/src/Middleware/CORS/src/Infrastructure/CorsMiddleware.cs#L112-L157 https://learn.microsoft.com/en-us/aspnet/core/security/cors?view=aspnetcore-9.0
3.1 You can call _cache.GetOrAddAsync.
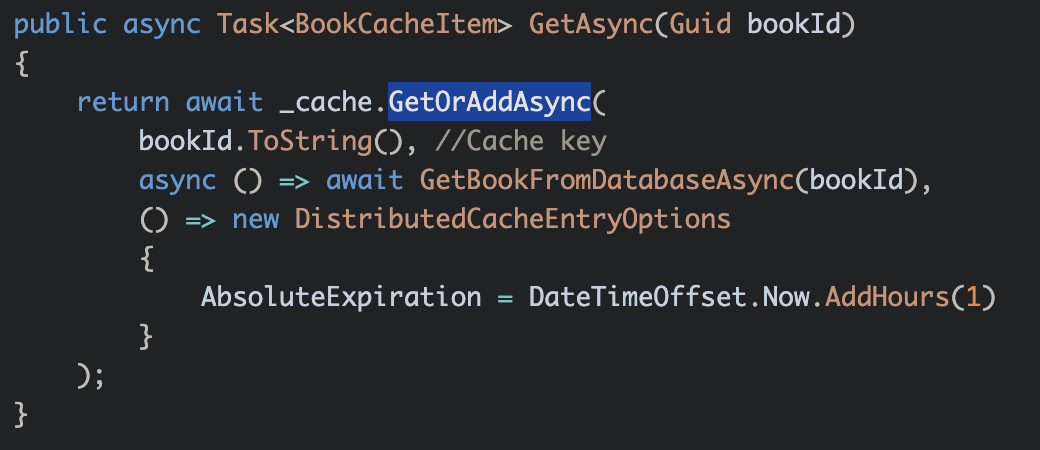
3.2 If there is no domains, you can return Task.FromResult<CorsPolicy?>(null);
https://github.com/dotnet/aspnetcore/blob/release/9.0/src/Middleware/CORS/src/Infrastructure/DefaultCorsPolicyProvider.cs#L12
hi
after checking server logs I found the below:
Please remove all Cookies from your HTTP request.
The anti-forgery will check if the current request contains the XSRF-TOKEN cookie.
https://abp.io/docs/latest/framework/infrastructure/csrf-anti-forgery
hi
You can configure the connection to specify DbContext.
For your case you need to change the connection string for IIdentityProDbContext(IIdentityDbContext)
https://abp.io/docs/latest/framework/fundamentals/connection-strings




