Apply rate limits directly to business operations with fine-grained policies, partition-aware rules, and enforcement models that fit real application workflows.
Available starting with ABP v10.3.


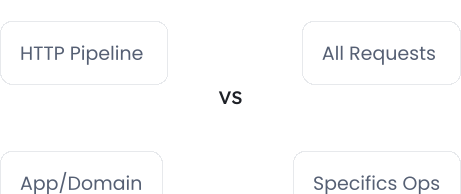
ASP.NET Core's built-in rate limiting works at the HTTP pipeline level, great for DDoS protection and API throttling, but too coarse for business rules like "max 3 SMS codes per hour per phone number" or "max 2 report generations per day per user."
The Operation Rate Limiting module works at the application and domain code level. Define policies for specific operations, partition counters by user, phone number, IP, tenant, or any custom key, and enforce limits exactly where your business logic runs.
Define a policy, check the limit, and let the module handle counter management, distributed locking, and error responses.
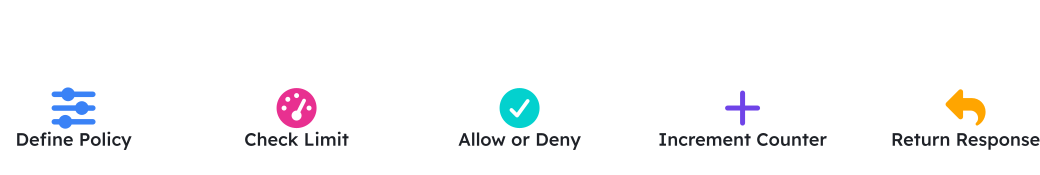
Use the declarative attribute for clean, convention-based enforcement, or inject the checker service for full programmatic control.
Apply the attribute to Application Service methods or MVC Controller actions. The rate limit is checked automatically before the method executes, with no manual code needed.
Mark a parameter with [RateLimitingParameter] or implement IHasOperationRateLimitingParameter on your DTO to control how the partition key is resolved.
Inject the checker service and call CheckAsync, IsAllowedAsync, GetStatusAsync, or ResetAsync for full control over rate limiting behavior.
CheckAsync throws AbpOperationRateLimitingException (HTTP 429) when limits are exceeded, automatically handled by ABP's exception pipeline.
Group rate limit counters by any dimension: users, tenants, IPs, phone numbers, emails, or your own custom keys.
Partition by parameter (phone number, API key, etc.), current user, current tenant, client IP address, email, or phone number. Each partition type creates independent counters so different keys never interfere with each other.
Register named resolvers for complex scenarios, combine device ID with user, resolve keys from extra properties, or query a database. Resolvers are async and stored by name for easy management and replacement in downstream modules.
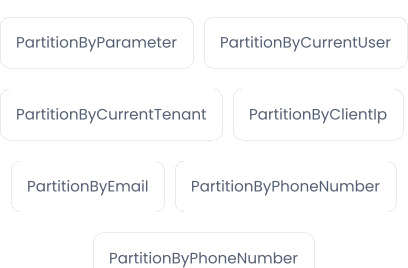
Define simple or complex rate limiting policies with multi-rule support, custom error codes, and full override capabilities.
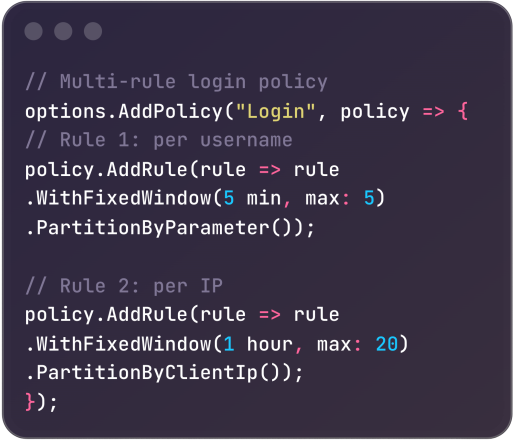
Use a simple fixed window for straightforward limits, or combine multiple rules with AND logic. A two-phase check ensures no counter is wasted when one rule blocks the request.
Replace an existing policy entirely with AddPolicy, or fine-tune it with ConfigurePolicy - add rules on top, change the error code, or clear and redefine.
Give rules a stable name so changing parameters like maxCount or duration won't reset existing counters. Essential when rules are managed from a database or UI.
Enterprise-grade rate limiting with multi-tenancy, distributed caching, extensibility, and seamless ABP integration.

Enable tenant-isolated counters per rule with WithMultiTenancy(). Each tenant gets independent rate limits, or share counters globally - your choice per policy.

Built on ABP's IDistributedCache for production-ready distributed counter storage. Distributed locking ensures thread-safe counter increments across multiple instances.

Replace the store, implement custom rate limiting algorithms (sliding window, token bucket), customize time formatters, or load policies from a database. Every component is designed for override.
From SMS verification to brute-force prevention, apply rate limits exactly where your application needs them.
Limit how often verification codes can be sent to the same phone number or email address. Prevent abuse without blocking legitimate users.
Restrict login attempts per username and per IP address with multi-rule policies. Stop brute-force attacks while keeping the experience smooth for real users.
Cap expensive operations like report generation, file exports, or AI API calls per user or per tenant. Protect your infrastructure from unintentional overload.
Use both together - ASP.NET Core middleware for broad API protection, and this module for targeted business operation limits.
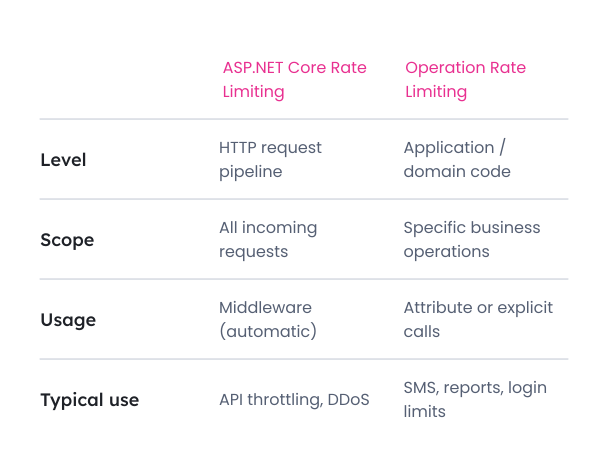
ASP.NET Core's built-in rate limiting operates at the HTTP request pipeline, ideal for DDoS protection and global API throttling. Operation Rate Limiting operates at the application layer, ideal for business logic constraints on specific operations.
Pre-installed with the Account (Pro) module and the latest ABP startup templates. No manual installation needed - just define your policies and start protecting your operations.
Built on ABP's distributed caching, dependency injection, and exception handling, and works out of the box with your existing ABP infrastructure.
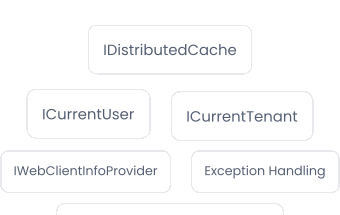
The module integrates with ABP's IDistributedCache for counter storage, ICurrentUser and ICurrentTenant for partition resolution, IWebClientInfoProvider for IP-based limits, and ABP's exception handling pipeline for automatic HTTP 429 responses.
It supports the ABP interceptor system for declarative attribute enforcement on Application Services and an ASP.NET Core action filter for MVC Controllers, all automatically registered.
Operation Rate Limiting works seamlessly with ABP's supported databases and UI stacks, so you can enforce policies without changing your architectural choices.

All starter templates offer multiple options for implementing your data access layer.


Dive into the documentation to see every feature in detail.