


- ABP Framework version: v7.0
- UI type: MVC
- DB provider: EF Core
- **Tiered (MVC) **: no
- Exception message and stack trace:
* [13:21:58 INF] Request starting HTTP/1.1 POST http://webapp.testprojects.in/signin-oidc application/x-www-form-urlencoded 1607
[13:21:58 ERR] Message contains error: 'invalid_request', error_description: 'The specified HTTP method is not valid.', error_uri: 'https://documentation.openiddict.com/errors/ID2084', status code '400'.
[13:21:58 ERR] Exception occurred while processing message.
Microsoft.IdentityModel.Protocols.OpenIdConnect.OpenIdConnectProtocolException: Message contains error: 'invalid_request', error_description: 'The specified HTTP method is not valid.', error_uri: 'https://documentation.openiddict.com/errors/ID2084'.
   at Microsoft.AspNetCore.Authentication.OpenIdConnect.OpenIdConnectHandler.RedeemAuthorizationCodeAsync(OpenIdConnectMessage tokenEndpointRequest)
   at Microsoft.AspNetCore.Authentication.OpenIdConnect.OpenIdConnectHandler.HandleRemoteAuthenticateAsync()
[13:21:58 INF] Error from RemoteAuthentication: Message contains error: 'invalid_request', error_description: 'The specified HTTP method is not valid.', error_uri: 'https://documentation.openiddict.com/errors/ID2084'..
[13:21:58 ERR] An unhandled exception has occurred while executing the request.
System.Exception: An error was encountered while handling the remote login.
 ---> Microsoft.IdentityModel.Protocols.OpenIdConnect.OpenIdConnectProtocolException: Message contains error: 'invalid_request', error_description: 'The specified HTTP method is not valid.', error_uri: 'https://documentation.openiddict.com/errors/ID2084'.
   at Microsoft.AspNetCore.Authentication.OpenIdConnect.OpenIdConnectHandler.RedeemAuthorizationCodeAsync(OpenIdConnectMessage tokenEndpointRequest)
   at Microsoft.AspNetCore.Authentication.OpenIdConnect.OpenIdConnectHandler.HandleRemoteAuthenticateAsync()
   --- End of inner exception stack trace ---
   at Microsoft.AspNetCore.Authentication.RemoteAuthenticationHandler`1.HandleRequestAsync()
   at Microsoft.AspNetCore.Authentication.AuthenticationMiddleware.Invoke(HttpContext context)
   at Volo.Abp.AspNetCore.Security.AbpSecurityHeadersMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
   at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.<>c__DisplayClass6_1.<<UseMiddlewareInterface>b__1>d.MoveNext()
--- End of stack trace from previous location ---
   at Volo.Abp.AspNetCore.Tracing.AbpCorrelationIdMiddleware.InvokeAsync(HttpContext context, RequestDelegate next)
   at Microsoft.AspNetCore.Builder.UseMiddlewareExtensions.<>c__DisplayClass6_1.<<UseMiddlewareInterface>b__1>d.MoveNext()
--- End of stack trace from previous location ---
   at Microsoft.AspNetCore.Diagnostics.ExceptionHandlerMiddlewareImpl.<Invoke>g__Awaited|8_0(ExceptionHandlerMiddlewareImpl middleware, HttpContext context, Task task)
[13:21:58 INF] Executing endpoint 'Volo.Abp.AspNetCore.Mvc.UI.Theme.Shared.Controllers.ErrorController.Index (Volo.Abp.AspNetCore.Mvc.UI.Theme.Shared)'
[13:21:58 INF] Route matched with {action = "Index", controller = "Error", area = "", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.IActionResult] Index(Int32) on controller Volo.Abp.AspNetCore.Mvc.UI.Theme.Shared.Controllers.ErrorController (Volo.Abp.AspNetCore.Mvc.UI.Theme.Shared).
- Steps to reproduce the issue:"
We have Latest copy of ABP IO commercial V7.0 using MVC and EFCore. Everything is working fine on Local without any change. We are trying to run this application on azure, and when we click on login it successfully redirect to the Auth Server then after passing credentials and clicked on Login we are getting above error. Same Issue is for Public Web site login.
We did required changes on azure as well. "RequireHttpsMetadata": "false", this value is et to false and "IsOnK8s": "true", set to true for Public Web project.
After login we are running into this issue.
Could you please help us to resolve this issue ASAP.
"AuthServer": { "Authority": "authserver url", "RequireHttpsMetadata": "true", "ClientId": "PublicWeb", "ClientSecret": "1q2w3e*", "IsOnK8s": "true", "MetaAddress": "authserver url" },
33 Answer(s)
-
0
[04:22:07 INF] AuthenticationScheme: Identity.Application signed in. [04:22:07 INF] Executed handler method OnPostAsync, returned result Microsoft.AspNetCore.Mvc.RedirectResult. [04:22:07 INF] Executing RedirectResult, redirecting to /connect/authorize?client_id=PublicWeb&redirect_uri=https%3A%2F%2Fpublicweb.mydomain.com%2Fsignin-oidc&response_type=code%20id_token&scope=openid%20profile%20roles%20email%20phone%20AccountService%20AdministrationService%20ProductService&response_mode=form_post&nonce=638103901167256421.MGMyYjFlMWYtM2RhZC00MzAyLTk5NWYtYzE0ZmQ2ZTdhOTU5ZWViYmI4N2QtZmI1OS00ZTc5LWE4ZTItMzVjMTZjZTE4MzZl&state=CfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg&x-client-SKU=ID_NETSTANDARD2_0&x-client-ver=6.15.1.0. [04:22:07 INF] Executed page /Account/Login in 334.7733ms [04:22:07 INF] Executed endpoint '/Account/Login' [04:22:07 INF] Request finished HTTP/1.1 POST http://authserver.mydomain.com/Account/Login?ReturnUrl=%2Fconnect%2Fauthorize%3Fclient_id%3DPublicWeb%26redirect_uri%3Dhttps%253A%252F%252Fpublicweb.mydomain.com%252Fsignin-oidc%26response_type%3Dcode%2520id_token%26scope%3Dopenid%2520profile%2520roles%2520email%2520phone%2520AccountService%2520AdministrationService%2520ProductService%26response_mode%3Dform_post%26nonce%3D638103901167256421.MGMyYjFlMWYtM2RhZC00MzAyLTk5NWYtYzE0ZmQ2ZTdhOTU5ZWViYmI4N2QtZmI1OS00ZTc5LWE4ZTItMzVjMTZjZTE4MzZl%26state%3DCfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg%26x-client-SKU%3DID_NETSTANDARD2_0%26x-client-ver%3D6.15.1.0 application/x-www-form-urlencoded 291 - 302 0 - 532.6852ms [04:22:07 INF] Request starting HTTP/1.1 GET http://authserver.mydomain.com/connect/authorize?client_id=PublicWeb&redirect_uri=https%3A%2F%2Fpublicweb.mydomain.com%2Fsignin-oidc&response_type=code%20id_token&scope=openid%20profile%20roles%20email%20phone%20AccountService%20AdministrationService%20ProductService&response_mode=form_post&nonce=638103901167256421.MGMyYjFlMWYtM2RhZC00MzAyLTk5NWYtYzE0ZmQ2ZTdhOTU5ZWViYmI4N2QtZmI1OS00ZTc5LWE4ZTItMzVjMTZjZTE4MzZl&state=CfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg&x-client-SKU=ID_NETSTANDARD2_0&x-client-ver=6.15.1.0 - - [04:22:07 INF] The request URI matched a server endpoint: Authorization. [04:22:07 INF] The authorization request was successfully extracted: { "client_id": "PublicWeb", "redirect_uri": "https://publicweb.mydomain.com/signin-oidc", "response_type": "code id_token", "scope": "openid profile roles email phone AccountService AdministrationService ProductService", "response_mode": "form_post", "nonce": "638103901167256421.MGMyYjFlMWYtM2RhZC00MzAyLTk5NWYtYzE0ZmQ2ZTdhOTU5ZWViYmI4N2QtZmI1OS00ZTc5LWE4ZTItMzVjMTZjZTE4MzZl", "state": "CfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg", "x-client-SKU": "ID_NETSTANDARD2_0", "x-client-ver": "6.15.1.0" }. [04:22:07 INF] The authorization request was successfully validated. [04:22:07 INF] Executing endpoint 'Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)' [04:22:07 INF] Route matched with {action = "Handle", controller = "Authorize", area = "", page = ""}. Executing controller action with signature System.Threading.Tasks.Task`1[Microsoft.AspNetCore.Mvc.IActionResult] HandleAsync() on controller Volo.Abp.OpenIddict.Controllers.AuthorizeController (Volo.Abp.OpenIddict.AspNetCore). [04:22:07 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy [04:22:08 INF] Executing SignInResult with authentication scheme (OpenIddict.Server.AspNetCore) and the following principal: System.Security.Claims.ClaimsPrincipal. [04:22:08 INF] The authorization response was successfully returned to 'https://publicweb.mydomain.com/signin-oidc' using the form post response mode: { "code": "[redacted]", "id_token": "[redacted]", "state": "CfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg", "iss": "https://authserver.mydomain.com/" }. [04:22:08 INF] Executed action Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore) in 84.4659ms [04:22:08 INF] Executed endpoint 'Volo.Abp.OpenIddict.Controllers.AuthorizeController.HandleAsync (Volo.Abp.OpenIddict.AspNetCore)' [04:22:08 INF] Request finished HTTP/1.1 GET http://authserver.mydomain.com/connect/authorize?client_id=PublicWeb&redirect_uri=https%3A%2F%2Fpublicweb.mydomain.com%2Fsignin-oidc&response_type=code%20id_token&scope=openid%20profile%20roles%20email%20phone%20AccountService%20AdministrationService%20ProductService&response_mode=form_post&nonce=638103901167256421.MGMyYjFlMWYtM2RhZC00MzAyLTk5NWYtYzE0ZmQ2ZTdhOTU5ZWViYmI4N2QtZmI1OS00ZTc5LWE4ZTItMzVjMTZjZTE4MzZl&state=CfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg&x-client-SKU=ID_NETSTANDARD2_0&x-client-ver=6.15.1.0 - - - 200 2052 text/html;charset=UTF-8 101.1029ms [04:22:08 INF] Request starting HTTP/1.1 GET http://authserver.mydomain.com/connect/token - - [04:22:08 INF] The request URI matched a server endpoint: Token. [04:22:08 INF] The request was rejected because an invalid HTTP method was specified: GET. [04:22:08 INF] The response was successfully returned as a JSON document: { "error": "invalid_request", "error_description": "The specified HTTP method is not valid.", "error_uri": "https://documentation.openiddict.com/errors/ID2084" }. [04:22:08 INF] Request finished HTTP/1.1 GET http://authserver.mydomain.com/connect/token - - - 400 167 application/json;charset=UTF-8 0.7235ms [04:22:08 INF] Request starting HTTP/1.1 GET http://authserver.mydomain.com/ - - [04:22:08 INF] Executing endpoint '/Index' [04:22:08 INF] Route matched with {page = "/Index", area = "", action = "", controller = ""}. Executing page /Index [04:22:08 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy [04:22:08 INF] Executing handler method testmvc.AuthServer.Pages.IndexModel.OnGet - ModelState is Valid [04:22:08 INF] Executed handler method OnGet, returned result Microsoft.AspNetCore.Mvc.RedirectResult. [04:22:08 INF] Executing RedirectResult, redirecting to /Account/Login. [04:22:08 INF] Executed page /Index in 0.7039ms [04:22:08 INF] Executed endpoint '/Index' [04:22:08 INF] Request finished HTTP/1.1 GET http://authserver.mydomain.com/ - - - 302 0 - 18.2350ms [04:22:09 INF] Request starting HTTP/1.1 GET http://authserver.mydomain.com/ - - [04:22:09 INF] Executing endpoint '/Index' [04:22:09 INF] Route matched with {page = "/Index", area = "", action = "", controller = ""}. Executing page /Index [04:22:09 INF] Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy [04:22:09 INF] Executing handler method testmvc.AuthServer.Pages.IndexModel.OnGet - ModelState is Valid [04:22:09 INF] Executed handler method OnGet, returned result Microsoft.AspNetCore.Mvc.RedirectResult. [04:22:09 INF] Executing RedirectResult, redirecting to /Account/Login. [04:22:09 INF] Executed page /Index in 0.5982ms [04:22:09 INF] Executed endpoint '/Index' [04:22:09 INF] Request finished HTTP/1.1 GET http://authserver.mydomain.com/ - - - 302 0 - 6.7258ms
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Is it possible that your AuthServer changed the request method?
Is there a Reverse Proxy Server?
[04:22:08 INF] Request starting HTTP/1.1 GET http://authserver.mydomain.com/connect/token - - [04:22:08 INF] The request URI matched a server endpoint: Token. [04:22:08 INF] The request was rejected because an invalid HTTP method was specified: GET. [04:22:08 INF] The response was successfully returned as a JSON document: { "error": "invalid_request", "error_description": "The specified HTTP method is not valid.", "error_uri": "https://documentation.openiddict.com/errors/ID2084" }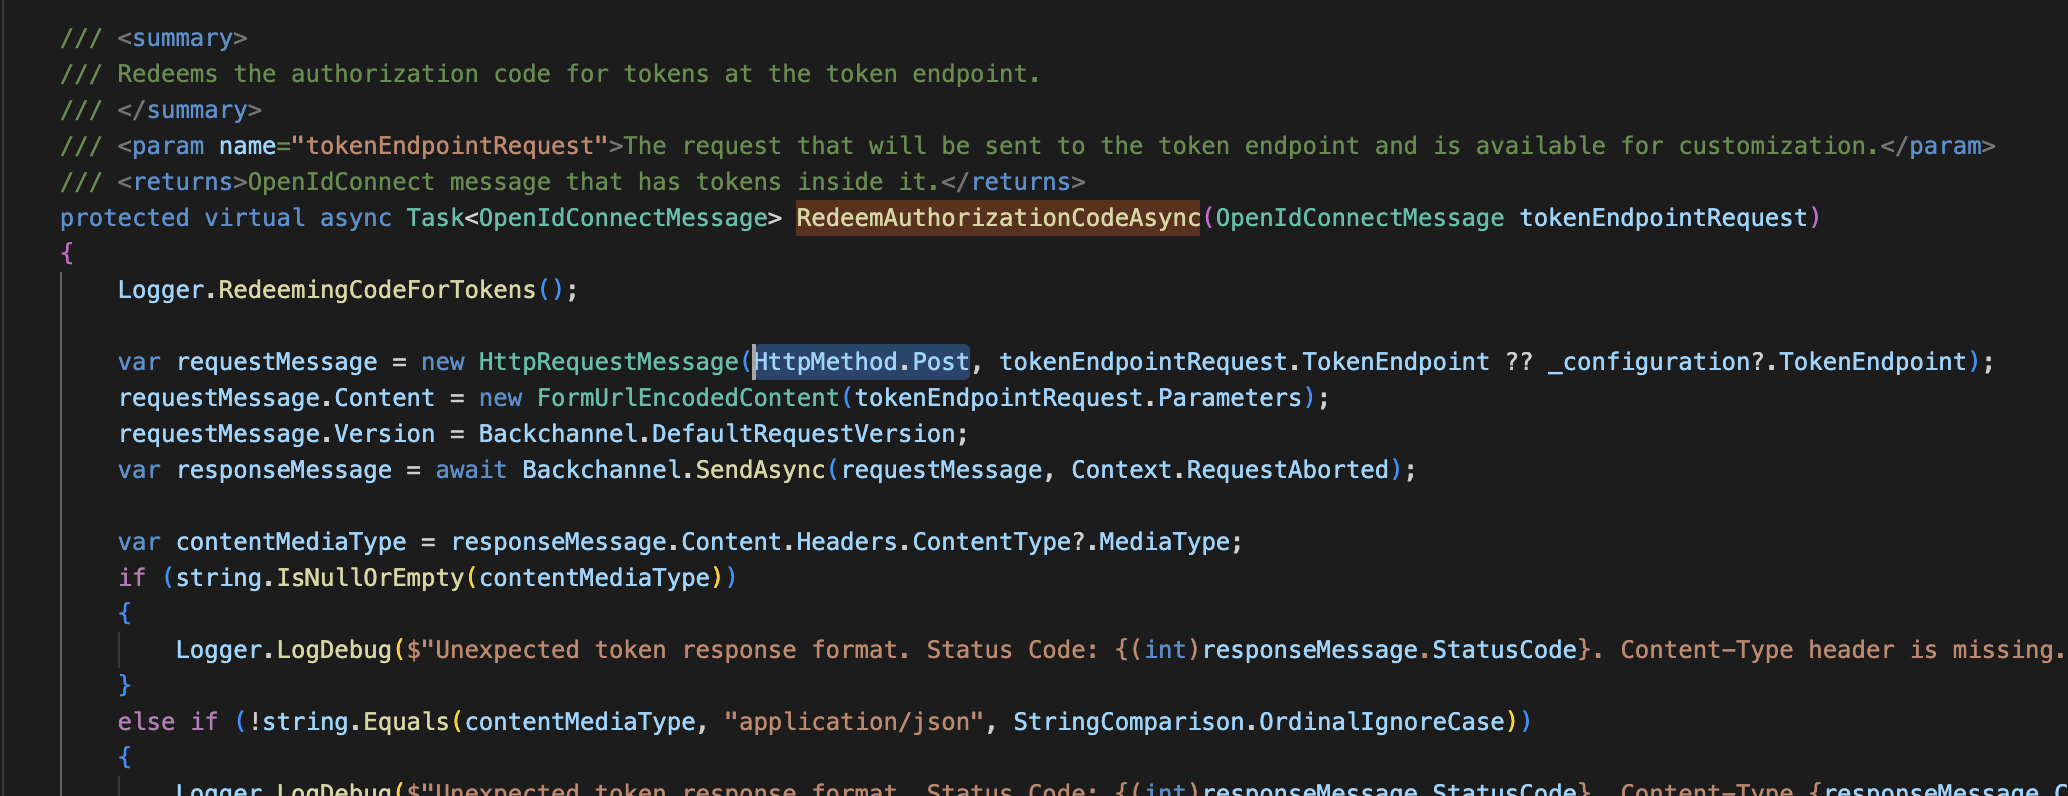 Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)
-
0
Hello,
[04:22:07 INF] Request finished HTTP/1.1 POST http://authserver.mydomain.com/Account/Login?ReturnUrl=%2Fconnect%2Fauthorize%3Fclient_id%3DPublicWeb%26redirect_uri%3Dhttps%253A%252F%252Fpublicweb.mydomain.com%252Fsignin-oidc%26response_type%3Dcode%2520id_token%26scope%3Dopenid%2520profile%2520roles%2520email%2520phone%2520AccountService%2520AdministrationService%2520ProductService%26response_mode%3Dform_post%26nonce%3D638103901167256421.MGMyYjFlMWYtM2RhZC00MzAyLTk5NWYtYzE0ZmQ2ZTdhOTU5ZWViYmI4N2QtZmI1OS00ZTc5LWE4ZTItMzVjMTZjZTE4MzZl%26state%3DCfDJ8JJyrua-ZltLqDoPZm_zeQfp0J1IFIuwBqACfHbom6IruK1Rv79GO333ahvIhrZ-SLtBwTL89u3GQwVsU-rMWqo9tTgXc_uUvjaqcCtdski-AKEmq8SVroq61km5yyA0Rxwg2HIEo33aKhPabt-lfLD3APbHOT-0MBynDfgkUKsIh3TklAQucKhwBYJUsYNaJURE2_eu4rgVuSJUOEBXlbcycaO3GskmtfKdzrl73AOMlxCzx_uY1sHfwb8tOoQs9Bvx54lD3MimJw9dMDyI5xABkoxnTTo6fbSCIEWzHWmqh-5P5ICQh4IQfcm_gWToYg%26x-client-SKU%3DID_NETSTANDARD2_0%26x-client-ver%3D6.15.1.0 application/x-www-form-urlencoded 291 - 302 0 - 532.6852msThis is your initial request and it seems to be redirected. It seems there is a reverse proxy redirecting this request. It can be related to cloudflare if you are using or something else.
And why do you set
"RequireHttpsMetadata": "true",on public-web application? What is your deployed/.well-known/openid-configurationendpoint?Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
By default,RequireHttpsMetadata is set to true in public web app. Now we set it to false, but still facing same error.
https://authserver.mydomain.com/.well-known/openid-configuration endpoint
{ "issuer": "https://authserver.mydomain.com/", "authorization_endpoint": "http://authserver.mydomain.com/connect/authorize", "token_endpoint": "http://authserver.mydomain.com/connect/token", "introspection_endpoint": "http://authserver.mydomain.com/connect/introspect", "end_session_endpoint": "http://authserver.mydomain.com/connect/logout", "revocation_endpoint": "http://authserver.mydomain.com/connect/revocat", "userinfo_endpoint": "http://authserver.mydomain.com/connect/userinfo", "device_authorization_endpoint": "http://authserver.mydomain.com/device", "jwks_uri": "http://authserver.mydomain.com/.well-known/jwks", "grant_types_supported": [ "authorization_code", "implicit", "password", "client_credentials", "refresh_token", "urn:ietf:params:oauth:grant-type:device_code", "LinkLogin", "Impersonation" ], "response_types_supported": [ "code", "code id_token", "code id_token token", "code token", "id_token", "id_token token", "token", "none" ], "response_modes_supported": [ "form_post", "fragment", "query" ], "scopes_supported": [ "openid", "offline_access", "email", "profile", "phone", "roles", "address" ], "claims_supported": [ "aud", "exp", "iat", "iss", "sub" ], "id_token_signing_alg_values_supported": [ "RS256" ], "code_challenge_methods_supported": [ "S256" ], "subject_types_supported": [ "public" ], "token_endpoint_auth_methods_supported": [ "client_secret_basic", "client_secret_post" ], "introspection_endpoint_auth_methods_supported": [ "client_secret_basic", "client_secret_post" ], "revocation_endpoint_auth_methods_supported": [ "client_secret_basic", "client_secret_post" ], "claims_parameter_supported": false, "request_parameter_supported": false, "request_uri_parameter_supported": false, "authorization_response_iss_parameter_supported": true }
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
You are using
kubernetes.io/ingress.class: azure/application-gateway. It seems like it is related to that. I have no idea aboutazure/application-gatewaybut I assume there is a guide, gui about configuring it since it seems like a gateway.Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post) -
0
Hello,
We tried deploying the app using nginx instead application gateway. But we are facing same issue as reported : "400 internal error occurred during your request !" Also images on the landing pages are broken.
Markdown supported.Copy, paste, or drag & drop images and files (max 100 MB per file, 100 MB total per post)



