hi
See the video: https://streamable.com/6uxolk
I can sign in by microsoft account and get username and email then register a new user.
If the role is set as default. The new user will have all of default roles.
Please share your test user with liming.ma@volosoft.com
no. I'm trying to log in by Microsoft account, Please create a new test user.
I will test your account with your app tomorrow
Thanks.
On your mobile device, approve request CBOC1
Please create a new test user.
Thanks.
Please share a test user of https://login.microsoftonline.com/
The code of ConfigureAuthentication
private void ConfigureAuthentication(ServiceConfigurationContext context, IConfiguration configuration)
{
    context.Services.AddAuthentication().AddOpenIdConnect(options =>
    {
        options.ClientId = configuration["Authentication:AzureAd:ClientId"];
        options.ClientSecret = configuration["Authentication:AzureAd:ClientSecret"];
        options.Authority = configuration["Authentication:AzureAd:Authority"];
        options.CallbackPath = configuration["Authentication:AzureAd:CallbackPath"];
        options.ResponseType = OpenIdConnectResponseType.Code;
        options.SaveTokens = true;
        //options.Scope.Clear();
        options.Scope.Add("openid");
        options.Scope.Add("profile");
        options.Scope.Add("email");
        //options.Scope.Add("offline_access");

        options.Events = new OpenIdConnectEvents
        {
            OnTokenValidated = async context =>
            {
                var claimsIdentity = (ClaimsIdentity) context.Principal.Identity;
                Console.WriteLine("User authenticated: " + claimsIdentity.Name);
            },
            OnRedirectToIdentityProvider = context =>
            {
                Console.WriteLine("Redirecting to Identity Provider...");
                return Task.CompletedTask;
            }
        };
    });

    // Add authentication using Azure AD
    //context.Services.AddAuthentication(options =>
    //{
    //    options.DefaultScheme = CookieAuthenticationDefaults.AuthenticationScheme;
    //    options.DefaultChallengeScheme = OpenIdConnectDefaults.AuthenticationScheme;
    //})
    //.AddOpenIdConnect(options =>
    //{
    //    options.ClientId = configuration["Authentication:AzureAd:ClientId"];
    //    options.ClientSecret = configuration["Authentication:AzureAd:ClientSecret"];
    //    options.Authority = configuration["Authentication:AzureAd:Authority"];
    //    options.CallbackPath = configuration["Authentication:AzureAd:CallbackPath"];
    //    options.ResponseType = OpenIdConnectResponseType.Code;
    //    options.SaveTokens = true;
    //    //options.Scope.Clear();
    //    options.Scope.Add("openid");
    //    options.Scope.Add("profile");
    //    options.Scope.Add("email");
    //    //options.Scope.Add("offline_access");

    //    options.Events = new OpenIdConnectEvents
    //    {
    //        OnTokenValidated = async context =>
    //        {
    //            var claimsIdentity = (ClaimsIdentity)context.Principal.Identity;
    //            Console.WriteLine("User authenticated: " + claimsIdentity.Name);
    //        },
    //        OnRedirectToIdentityProvider = context =>
    //        {
    //            Console.WriteLine("Redirecting to Identity Provider...");
    //            return Task.CompletedTask;
    //        }
    //    };
    //})
    //.AddCookie(CookieAuthenticationDefaults.AuthenticationScheme, options =>
    //{
    //    options.Cookie.HttpOnly = true;
    //    options.Cookie.SameSite = SameSiteMode.Strict;  // Adjust based on your requirements

    //    options.Events = new CookieAuthenticationEvents
    //    {
    //        OnSigningIn = context =>
    //        {
    //            Console.WriteLine("Signing in user...");
    //            return Task.CompletedTask;
    //        },
    //        OnSignedIn = context =>
    //        {
    //            Console.WriteLine("User signed in: " + context.Principal.Identity.Name);
    //            return Task.CompletedTask;
    //        },
    //        OnSigningOut = context =>
    //        {
    //            Console.WriteLine("Signing out user...");
    //            return Task.CompletedTask;
    //        }
    //    };
    //});

    context.Services.ForwardIdentityAuthenticationForBearer(OpenIddictValidationAspNetCoreDefaults.AuthenticationScheme);
    context.Services.Configure<AbpClaimsPrincipalFactoryOptions>(options =>
    {
        options.IsDynamicClaimsEnabled = true;
    });
}
Your project works for me.
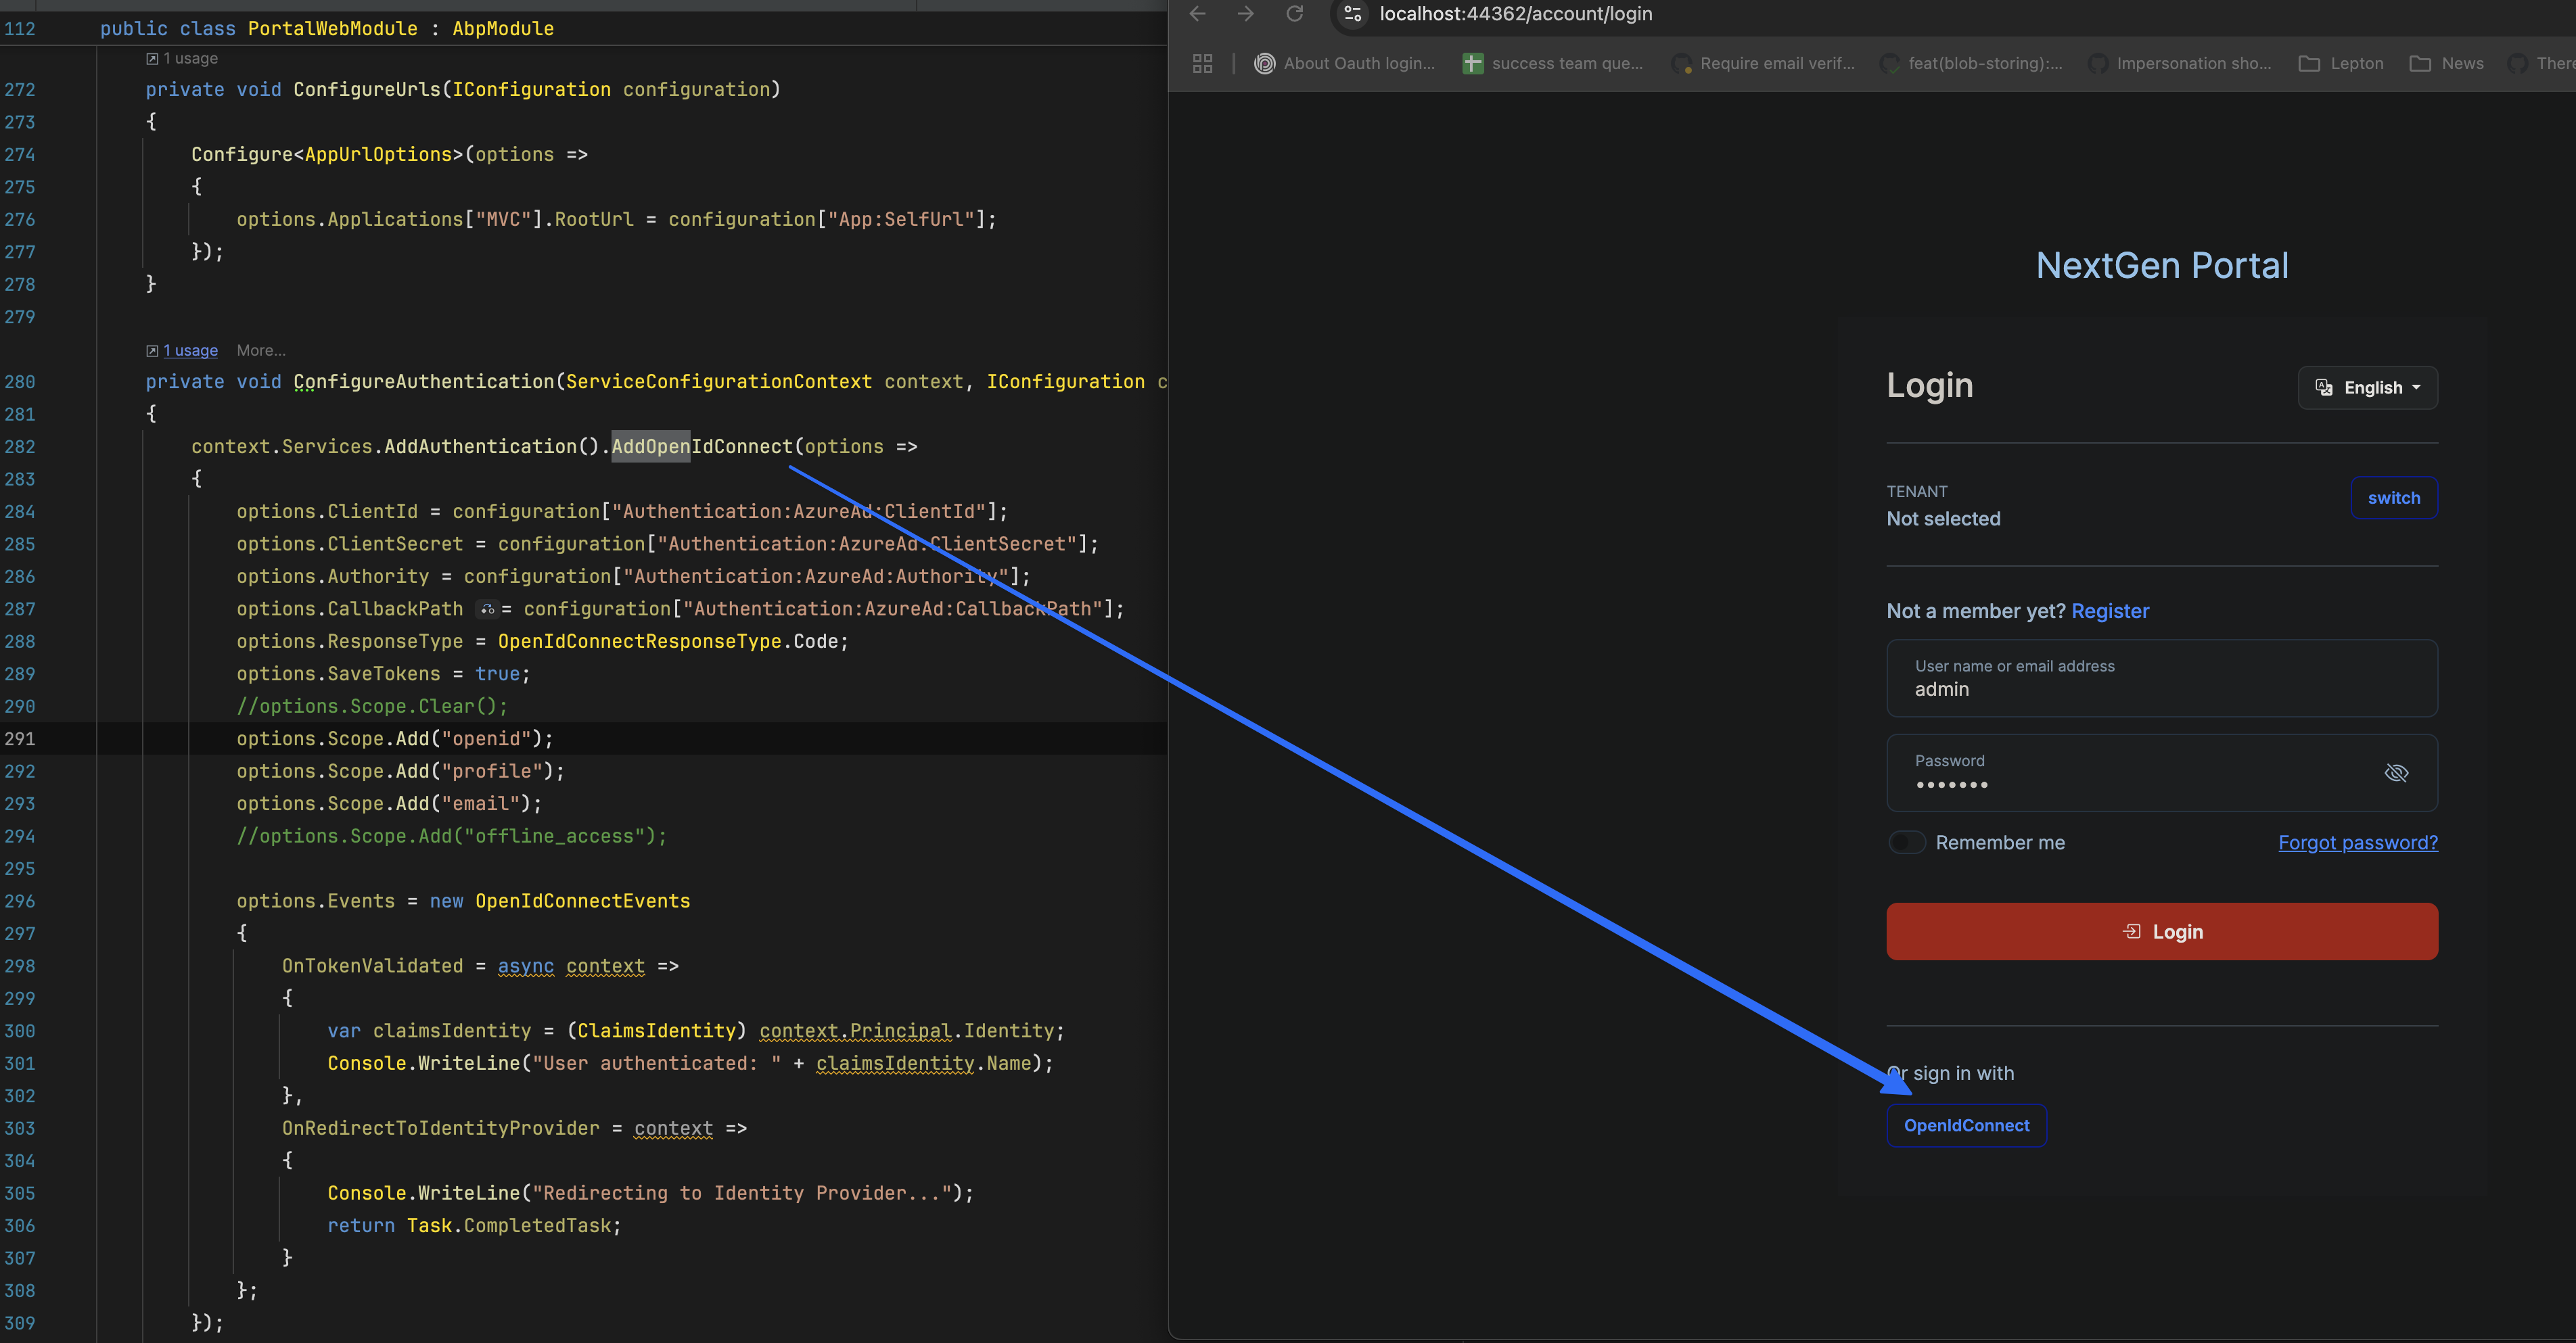
hi
You misunderstand the OAuth Resource Owner Password (ROP) External login Provider
See https://abp.io/docs/latest/modules/identity/oauth-login
If you want to see a login option on the Login/Register page, you can add your Okta as an external social login provider.
See https://abp.io/docs/latest/modules/account-pro#manage-external-logins
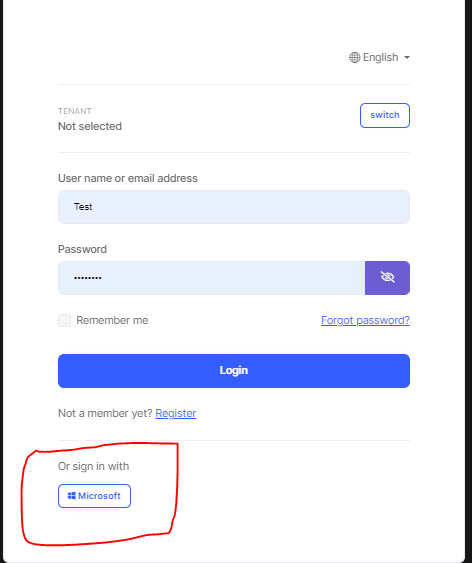
Ok, waiting for your project. Thanks
Thanks. If your project is complicated, you can test your code in a template project and share the template source code.




