hi
The authorization request was rejected because the application 'ReactG1' was not allowed to use the 'AccountService' scope.
Please check the scopes of the ReactG1
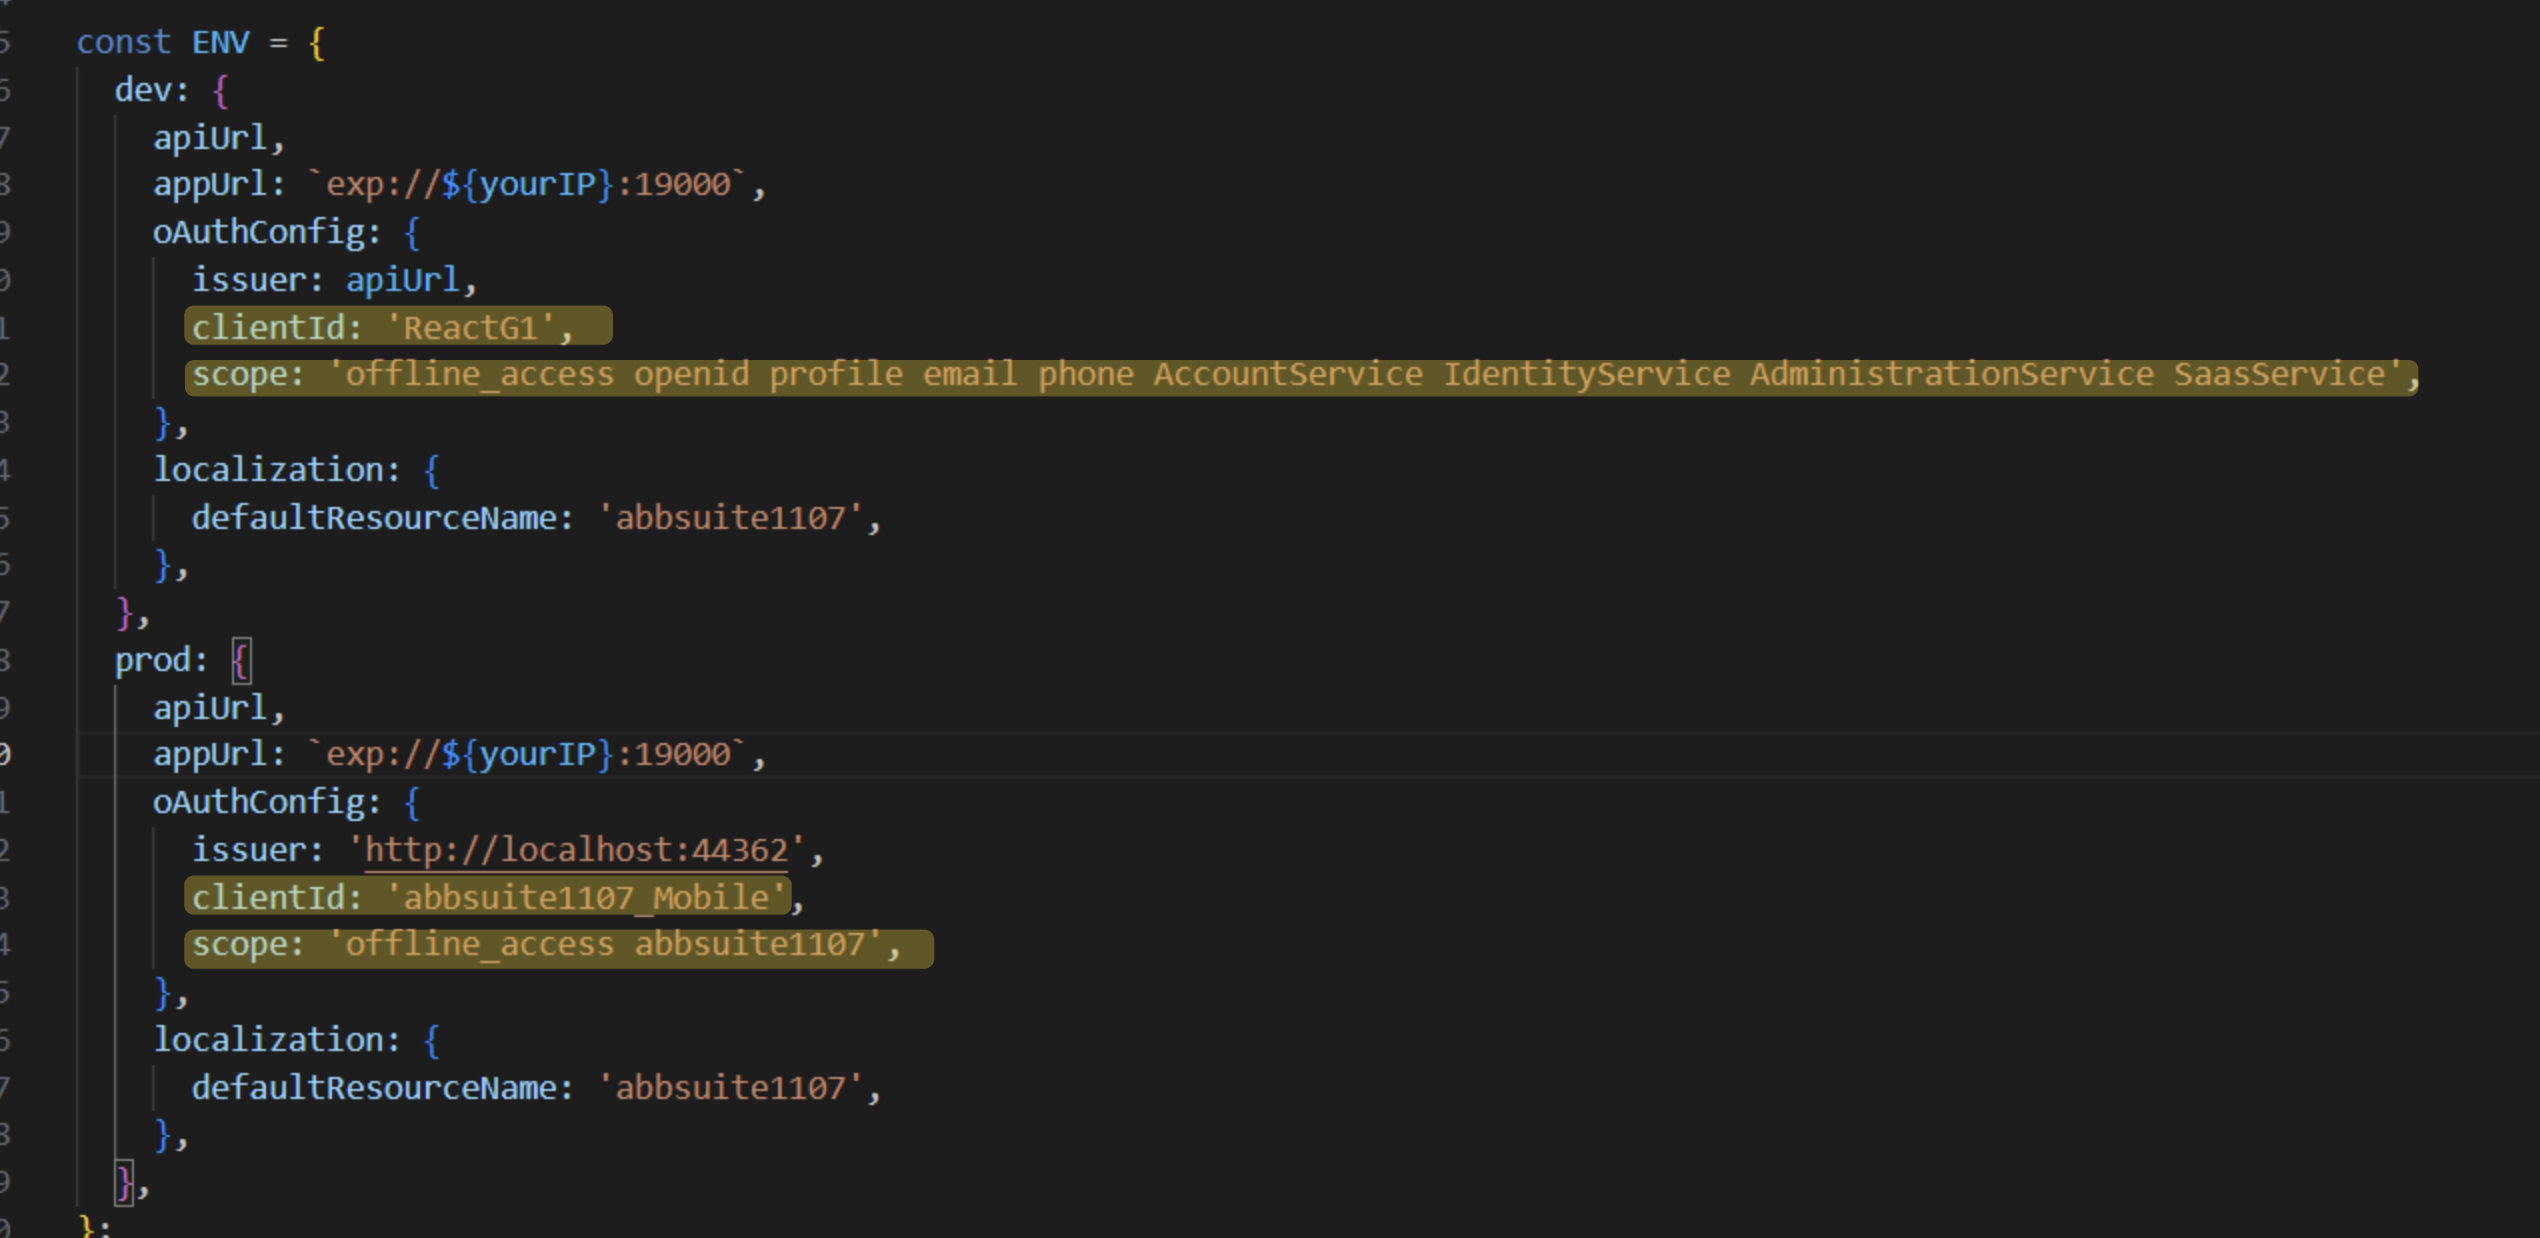
hi
System.ArgumentException: Cannot write DateTime with Kind=Local to PostgreSQL type 'timestamp with time zone', only UTC is supported. Note that it's not possible to mix DateTimes with different Kinds in an array, range, or multirange. (Parameter 'value')
Try to add this line to your ef core layer.
// https://www.npgsql.org/efcore/release-notes/6.0.html#opting-out-of-the-new-timestamp-mapping-logic
AppContext.SetSwitch("Npgsql.EnableLegacyTimestampBehavior", true);

hi
I will ask our angular team. Please wait a moment.
Thanks.
hi
I will investigate this. Thank you
The design of Openiddict and identity server are different, so this may not be possible.
Yes, there is no UI to configure the claims. You have to change it by code.
You can add an IAbpOpenIddictClaimsPrincipalHandler to see if your oauth2 request works.
If you get an error, please share the logs. I will check it.
Thanks.
hi
There are only Scope and Application that you need to pay attention to in OpenIddict.
https://github.com/abpframework/abp/blob/dev/templates/app/aspnet-core/src/MyCompanyName.MyProjectName.Domain/OpenIddict/OpenIddictDataSeedContributor.cs#L55-L56
For claims management, you can check https://docs.abp.io/en/abp/latest/Modules/OpenIddict#updating-claims-in-access_token-and-id_token
Add your claim types to id/access token from AbpOpenIddictClaimsPrincipalHandlerContext's Principal.
What are grantTypes of your client?
hi
Our angular team will reply asap.
sorry for that.
Good news. 👍
hi
Please set your log level to Debug and reproduce the problem then share the logs.txt to liming.ma@volosoft.com
Thanks.
public class Program
{
    public async static Task<int> Main(string[] args)
    {
        Log.Logger = new LoggerConfiguration()
            .MinimumLevel.Debug()
            .MinimumLevel.Override("Microsoft.EntityFrameworkCore", LogEventLevel.Warning)
            .Enrich.FromLogContext()
            .WriteTo.Async(c => c.File("Logs/logs.txt"))
            .WriteTo.Async(c => c.Console())
            .CreateLogger();
hi
How can I set the behavior for all the tenants as superadmin (admin without a tenant)
Get IdentityProSettingNames.Session.PreventConcurrentLogin definition and change the default value in your SettingDefinitionProvider
new SettingDefinition(IdentityProSettingNames.Session.PreventConcurrentLogin,
   IdentityProPreventConcurrentLoginBehaviour.Disabled.ToString(),
   L("DisplayName:Abp.Identity.PreventConcurrentLogin"),
   L("Description:Abp.Identity.PreventConcurrentLogin"),
   true)
make sure that tenant admins cannot change it in any case?
You can override the UpdateSessionAsync method of IdentitySettingsAppService to ensure that only the host admin can change it.




