hi
Please create a new 7.2 template project with npgsql
And global search for the EnableLegacyTimestampBehavior keyword.
hi
Please share your HTTP request info of angular.
hi
Please make sure you upgrade all Volo.Abp.xxx and Volo.xxx packages to 7.
hi
There was a new key created. so user was not authenticated.
Creating key {f5ac6d1c-79bb-4f8d-a633-ed8ec15f44e2} with creation date 2023-04-27 01:56:19Z, activation date 2023-04-27 01:56:19Z, and expiration date 2023-07-26 01:56:19Z.
No XML encryptor configured. Key {f5ac6d1c-79bb-4f8d-a633-ed8ec15f44e2} may be persisted to storage in unencrypted form.

Identity.Application was not authenticated. Failure message: Unprotect ticket failed
CORS policy execution failed.
Request origin https://localhost:44354 does not have permission to access the resource.
Can you share your project again? include the steps to reproduce. liming.ma@volosoft.com
hi
Are there any error logs on the backend app?
hi
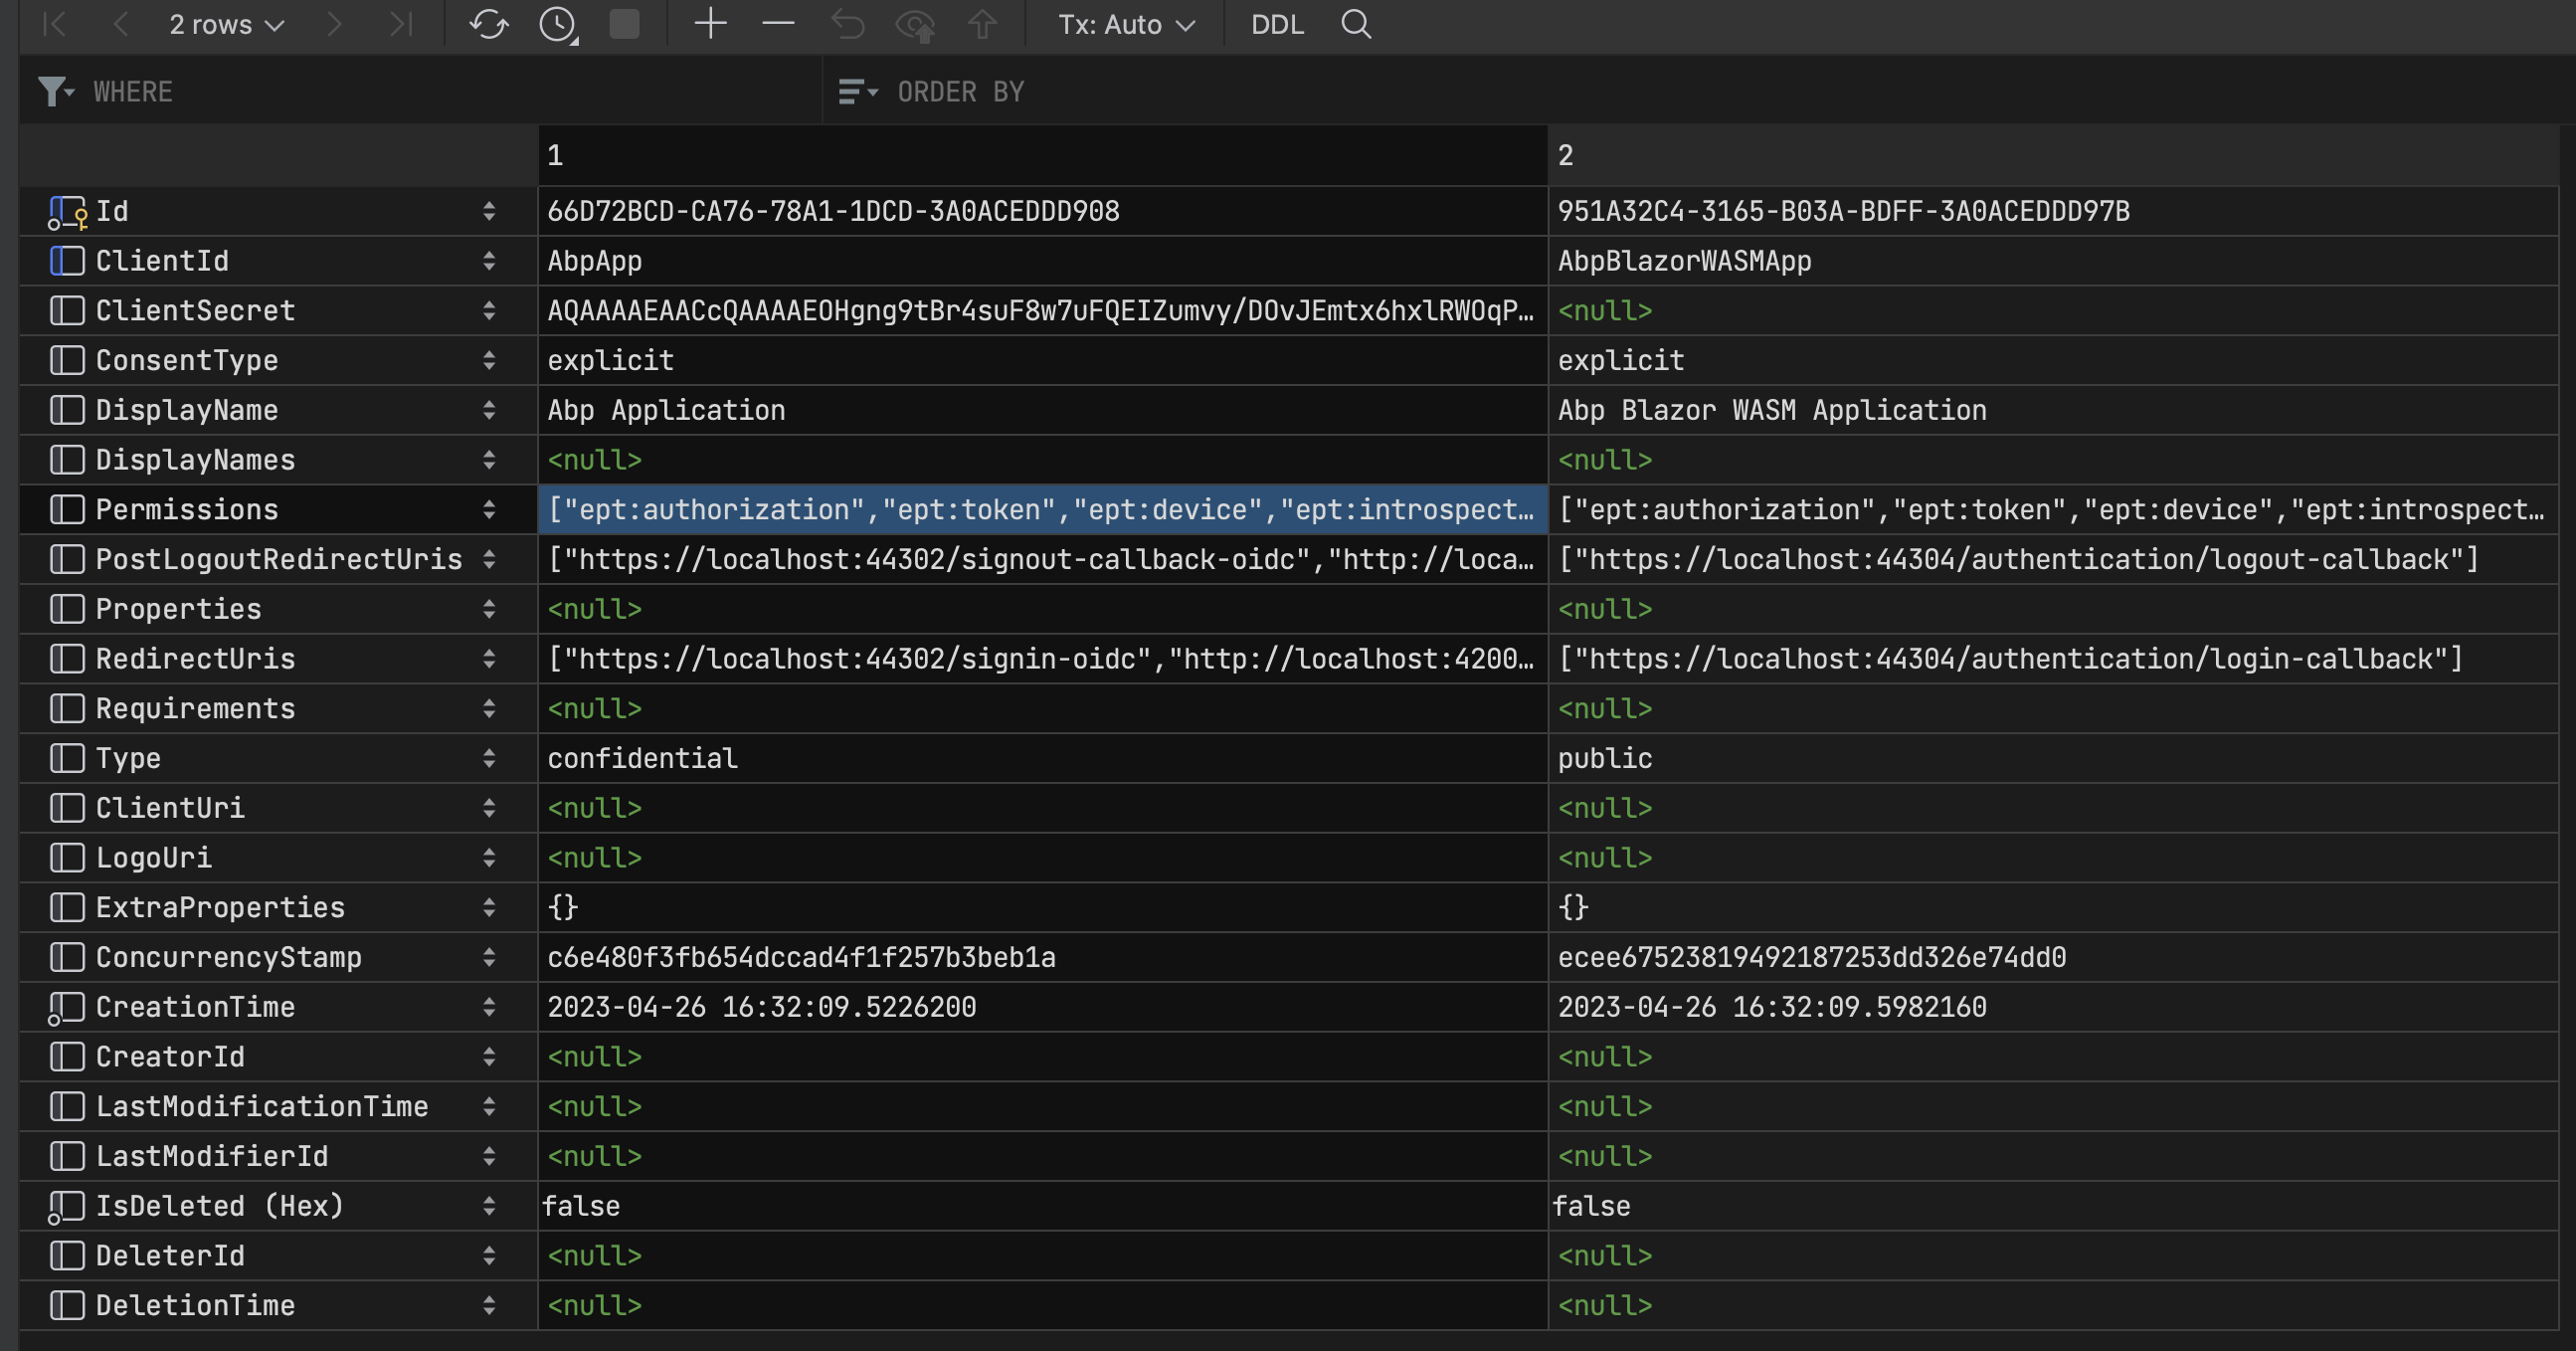
You can add "gt:Impersonation" to the Permissions of your application. We will support it in the next version.
["ept:authorization","ept:token","ept:device","ept:introspection","ept:revocation","ept:logout","gt:authorization_code","gt:implicit","gt:password","gt:refresh_token","gt:urn:ietf:params:oauth:grant-type:device_code","gt:client_credentials","gt:Impersonation","rst:code","rst:code id_token","rst:code id_token token","rst:code token","rst:id_token","rst:id_token token","rst:none","rst:token","scp:roles","scp:profile","scp:email","scp:address","scp:phone","scp:AbpAPI"]
[
  "ept:authorization",
  "ept:token",
  "ept:device",
  "ept:introspection",
  "ept:revocation",
  "ept:logout",
  "gt:authorization_code",
  "gt:implicit",
  "gt:password",
  "gt:refresh_token",
  "gt:urn:ietf:params:oauth:grant-type:device_code",
  "gt:client_credentials",
  "gt:Impersonation",
  "rst:code",
  "rst:code id_token",
  "rst:code id_token token",
  "rst:code token",
  "rst:id_token",
  "rst:id_token token",
  "rst:none",
  "rst:token",
  "scp:roles",
  "scp:profile",
  "scp:email",
  "scp:address",
  "scp:phone",
  "scp:AbpAPI"
]
"grant_type": "Impersonation",
"client_id": "DeployWeb22",
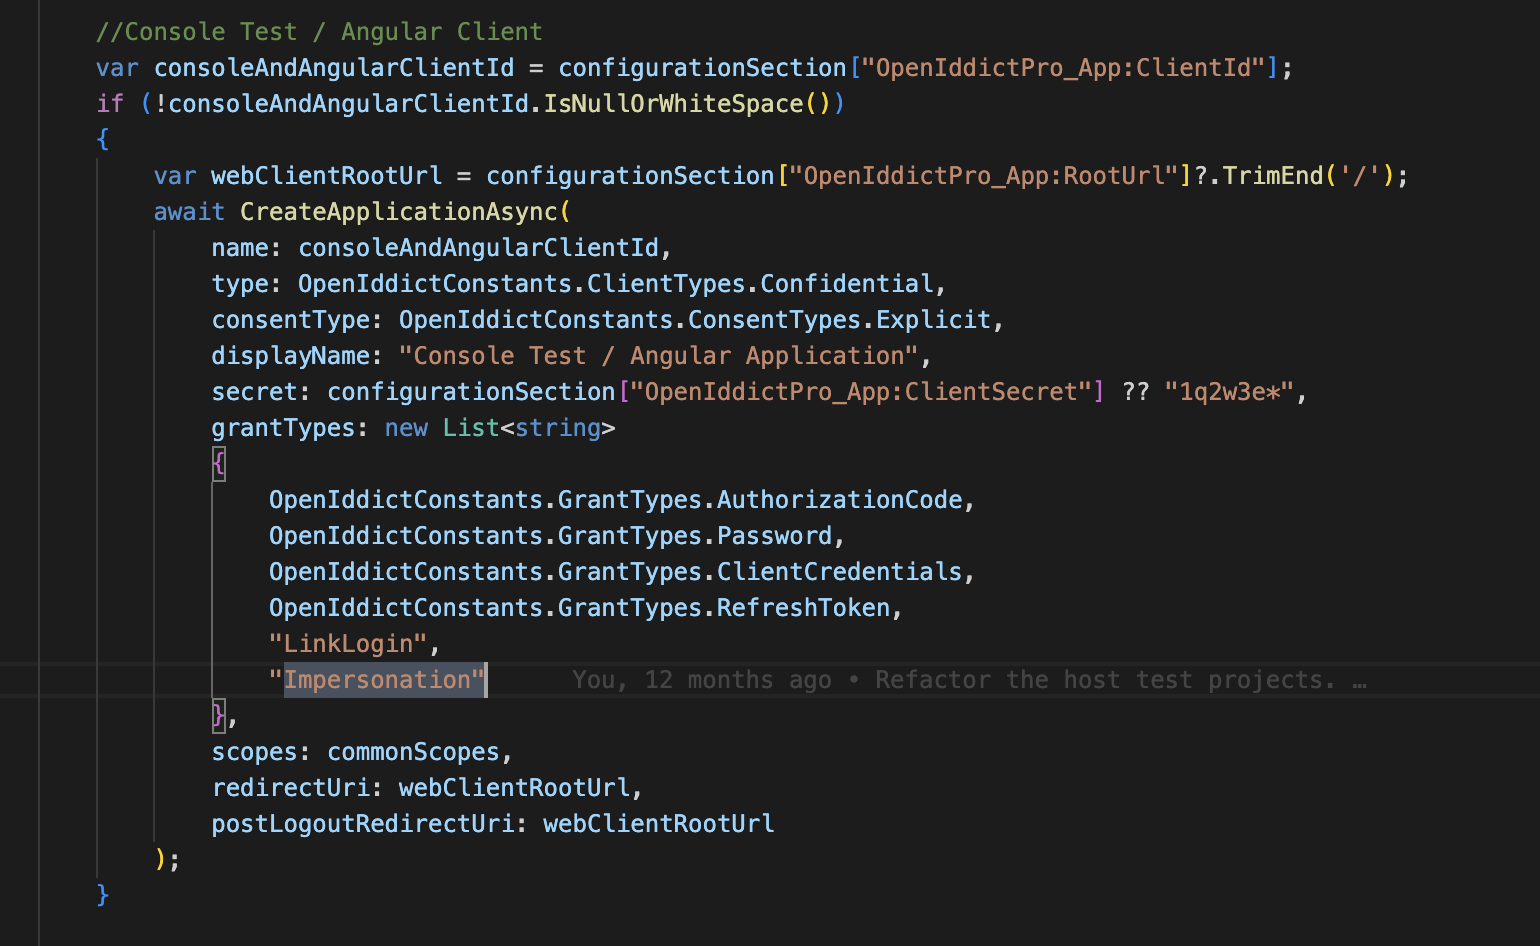
Please add Impersonation to granttypes of your angular application,
hi
Please check the consoleAndAngularClientRootUrl, There is no BookStore_App in your appsettings.

hi
You can create a new project.
Theappsettings.json of DbMigrator

You can also update the application on the web page.

hi
Client validation failed because 'http://localhost:4200' was not a valid redirect_uri for _3M_App.
The request URI matched a server endpoint: Authorization.
The authorization request was successfully extracted: {
  "response_type": "code",
  "client_id": "_3M_App",
  "state": "aGJOeWhrUXZqN3pXYTFrcVRYRWpydzRwcW02WkdhUlJSaVlOdThOUjRsbUMy",
  "redirect_uri": "http://localhost:4200",
  "scope": "offline_access openid profile email phone _3M",
  "code_challenge": "7dohmnVI2zU2qvJ6W0o2crV-UUr-EXRPil8l3_HJoYw",
  "code_challenge_method": "S256",
  "nonce": "aGJOeWhrUXZqN3pXYTFrcVRYRWpydzRwcW02WkdhUlJSaVlOdThOUjRsbUMy",
  "culture": "en",
  "ui-culture": "en"
}.
Client validation failed because 'http://localhost:4200' was not a valid redirect_uri for _3M_App.
The authorization request was rejected because the redirect_uri was invalid: 'http://localhost:4200'.




