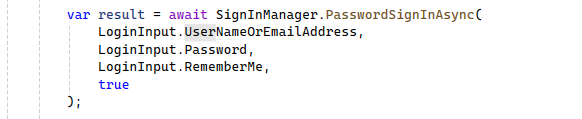
We are facing the issue during login process. when we have number of locations "AbpUserOrganizationUnits" (we have around 1500 Locations) and all of he locations is mapped to the users "AbpUserOrganizationUnits", The number of users are around 3000 this was working ok in our previous ABP 5 solution but after upgrading to Abp9 we found lot time it is taking top process the below code, around 3 minutes hence getting the timeout as well
In order top check this We have created a simple layered solution, and loaded with 2000 Locations. in this case we observed lo of time is taking at
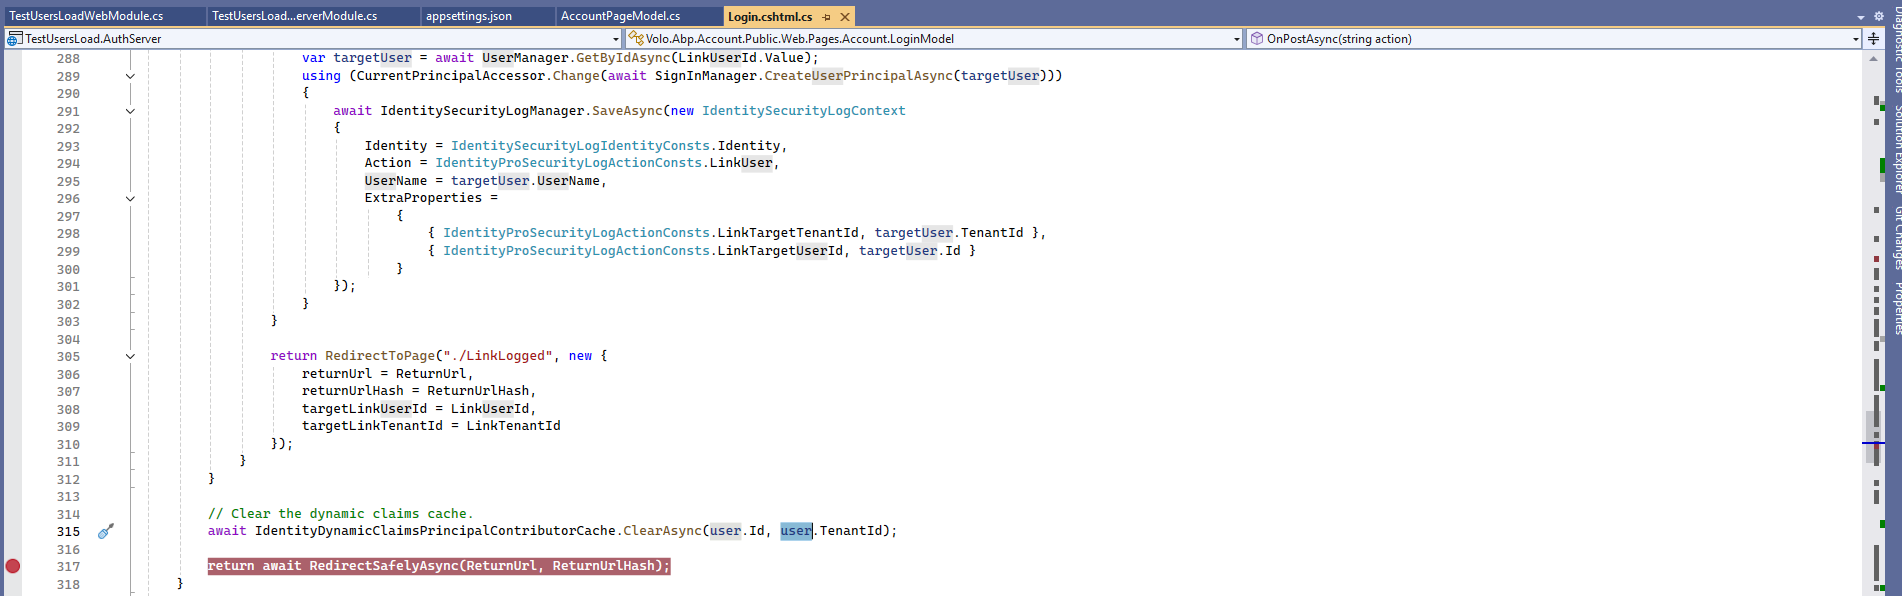
As per our analysis we are suspecting on claims. This is very critial and makor concern.
We did not find any ETOs for IdentityUserOrganizationUnit and IdentityUserRole to implement DistributedEventHandler.
We are using default ABP API for User creation and Edit. We are facing performance issue when we have hundreds of organization units. We've observed that LocalEventHandler is triggering for every organization unit assignment/removal in User create/edit. Is Default API using Batch Processing for organization unit assignment/removal or else need to inplement explicitly by overriding default API.
Any guidance or clarification on this would be greatly appreciated.
We are facing the perforamce issue on creation /modification of users when we have lots of locations and mappings.
These local event handlers are functioning as expected within the same application context.
As we transition to a distributed architecture using RabbitMQ, we are attempting to handle the same events through the distributed event bus, using: IDistributedEventHandler<EntityCreatedEventData<IdentityUserOrganizationUnit>> IDistributedEventHandler<EntityCreatedEventData<IdentityUserRole>>
However, we have encountered the following challenges: These events are not automatically published to the distributed event bus. Did not find any ETOs for the IdentityUserOrganizationUnit or IdentityUserRole entities. As a result, we are unable to subscribe to or handle these events using the distributed event.
In scenarios where a user is associated with hundreds of roles or organization units, this results in the UserManager making repeated changes per item — leading to hundreds of operations and drastically increasing the time required to complete the user creation/edit process.
Are there best practices within ABP for improving performance in such scenarios?
Any guidance or clarification on this would be greatly appreciated.
We have manually upgraded our solution from ABP.io 7 to ABP.io 9.
After the upgrade, the LeptonX CSS and JS bundles are loading, but not the latest ABP.io 9 bundles in development mode.
Could you please confirm if there are additional steps or configurations required to enable the latest LeptonX bundles in ABP.io 9?We have manually upgraded our solution from ABP.io 7 to ABP.io 9.
After the upgrade, the LeptonX CSS and JS bundles are loading, but not the latest ABP.io 9 bundles in development mode.
Could you please confirm if there are additional steps or configurations required to enable the latest LeptonX bundles in ABP.io 9?
Some how we are able to make the things working with Idenity4 server after upgrade to ABP 9 .
We made changes in Auth server module file
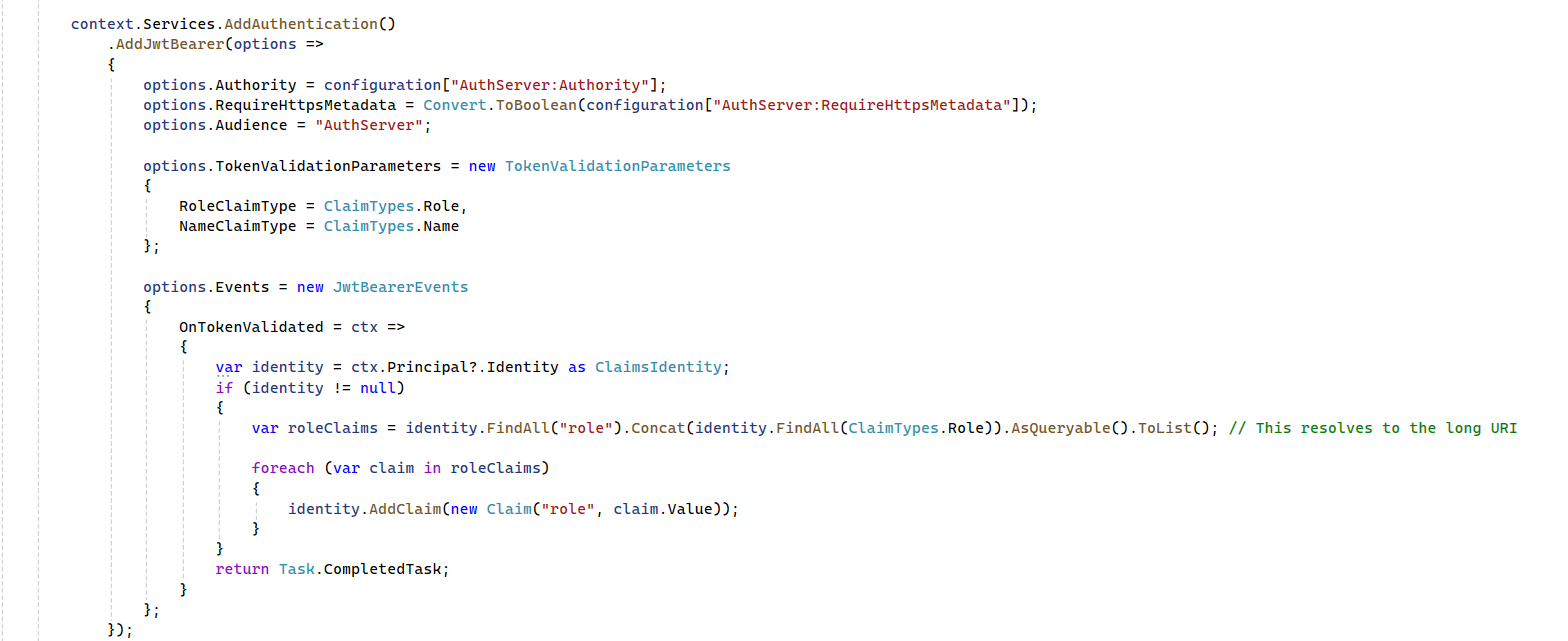
and in JwtBearerConfigurationHelper.cs we have added additional options

After the above changes Login worked perfectly and things are perfect till Auth Server ad Web,
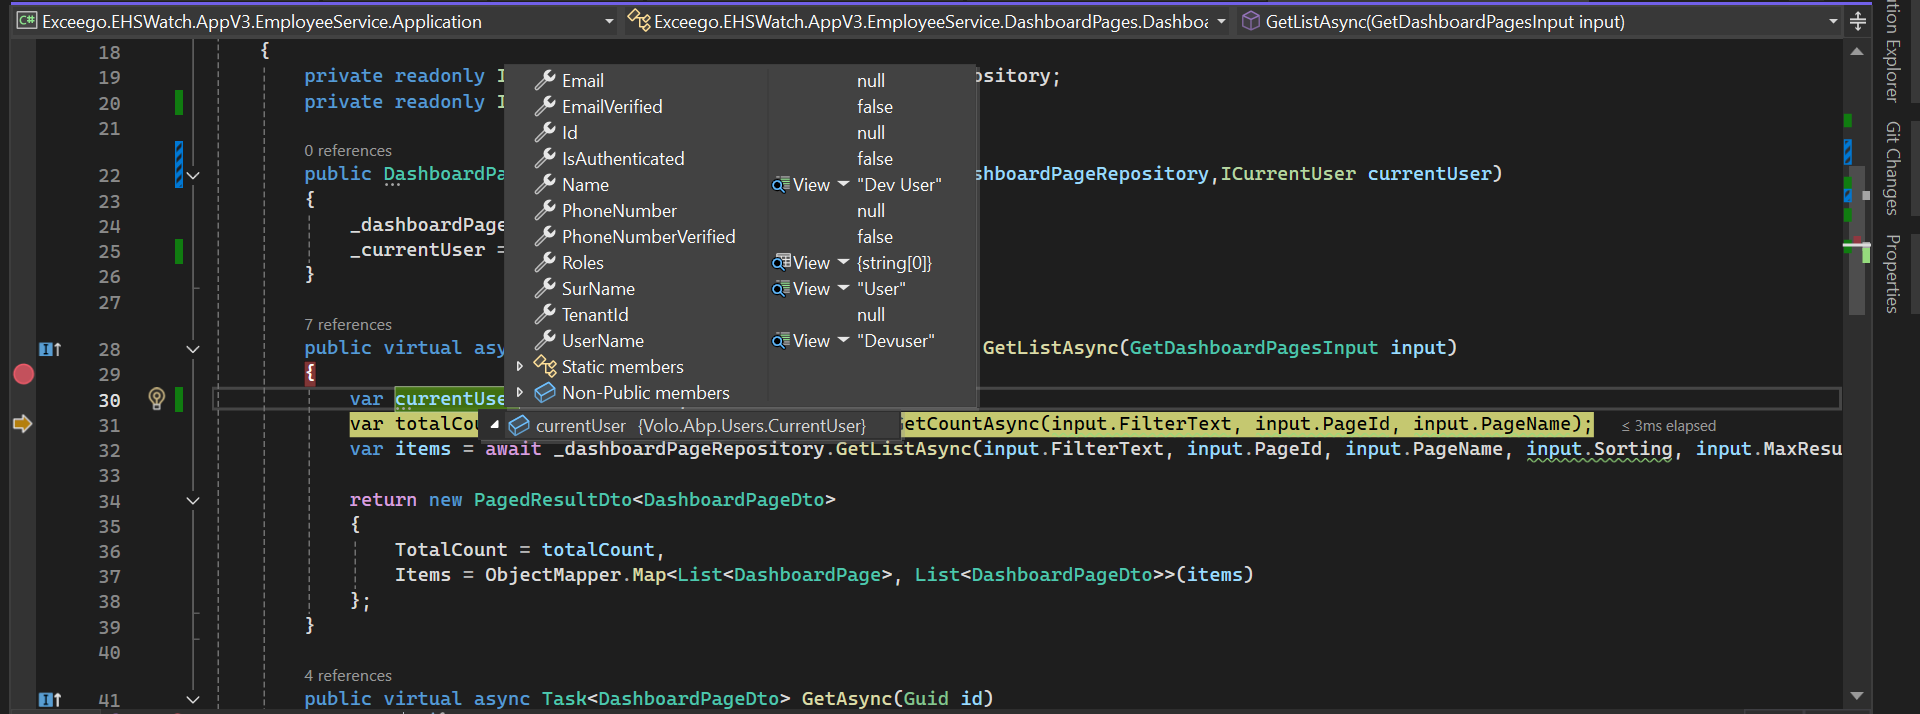
But we we are calling the API's from different services we observed that ICurrentUser object is coming but with null values for Id, Email etc, Also IsAuthenticated also coming as false so services are not respeoning as expected. Any idea what we might have missed?
We can find the Roles in Log, but when we inject CurrentUser in AppService, not able find the roles.
[liming.ma@volosoft.com] said: hi
The Microsoft logs level still not Debug
Please use the log configuration code below.
var loggerConfiguration = new LoggerConfiguration()
    .MinimumLevel.Debug()
    .MinimumLevel.Override("Microsoft.EntityFrameworkCore", LogEventLevel.Warning)
    .Enrich.FromLogContext()
    .WriteTo.Async(c => c.File("Logs/logs.txt"))
2025-06-30 19:52:16.805 +05:30 [INF] Request starting HTTP/1.1 GET http://localhost:44371/api/employee-service/dashboard-pages?PageId=HOMEDASHBOARD&SkipCount=0&MaxResultCount=20000&api-version=1.0 - null 0 2025-06-30 19:52:17.252 +05:30 [INF] Executing endpoint 'Exceego.EHSWatch.AppV3.EmployeeService.Controllers.DashboardPages.DashboardPageController.GetListAsync (Exceego.EHSWatch.AppV3.EmployeeService.HttpApi)' 2025-06-30 19:52:18.685 +05:30 [INF] Authorization failed. These requirements were not met: PermissionRequirement: EmployeeService.CustomReports 2025-06-30 19:52:19.936 +05:30 [INF] Request finished HTTP/1.1 GET https://localhost:44371/api/employee-service/dashboard-pages?PageId=HOMEDASHBOARD&SkipCount=0&MaxResultCount=20000&api-version=1.0 - 403 0 null 3131.5555msThese requirements were not met: PermissionRequirement: EmployeeService.CustomReports
Does your current user have
EmployeeService.CustomReportspermission?If the
403error only happened onExceego.EHSWatch.AppV3.EmployeeService.HttpApi.Host.website.Please enable the
Debuglog level and share again.Also output some info to the logs.
app.UseAuthentication();

app.Use(async (httpContext, next) =>
{
    var logger = httpContext.RequestServices.GetRequiredService<ILogger<EmployeeServiceHttpApiHostModule>>();
    var claims = httpContext.User.Claims.Select(x => new { x.Type, x.Value }).ToList();
    logger.LogError("HttpContext.User Claims:");
    logger.LogError(JsonSerializer.Serialize(claims));

    var currentUser = httpContext.RequestServices.GetRequiredService<ICurrentUser>().GetAllClaims().Select(x => new { x.Type, x.Value }).ToList();
    logger.LogError("Current User Claims:");
    logger.LogError(JsonSerializer.Serialize(currentUser));


    var userid = AbpClaimTypes.UserId;
    var username = AbpClaimTypes.UserName;
    var roleClaimType = AbpClaimTypes.Role;

    logger.LogError($"UserId Claim Type: {userid}");
    logger.LogError($"UserName Claim Type: {username}");
    logger.LogError($"Role Claim Type: {roleClaimType}");

    var authorizationHeader = httpContext.Request.Headers["Authorization"];
    logger.LogError(!string.IsNullOrEmpty(authorizationHeader)
        ? $"Authorization Header: {authorizationHeader}"
        : "Authorization Header is missing or empty.");

    await next(httpContext);
});
Thanks.
sent the logs to ur email, Thanks
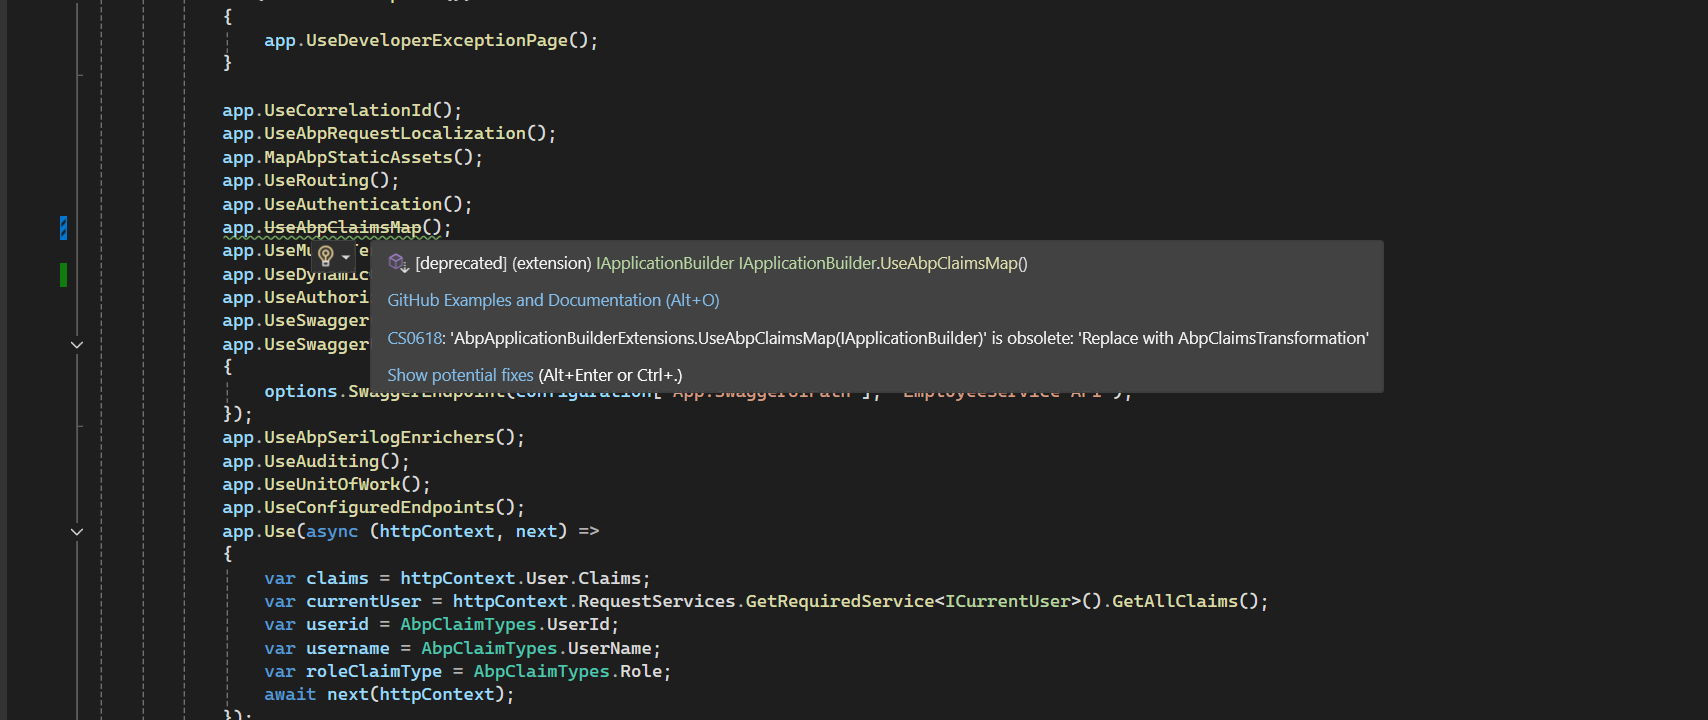
Are we missing anything to get Roles claims/CurrentUser in Employee Service?
Hi,
Sent you email.
[liming.ma@volosoft.com] said: hi
Add it to the project that has
forbidden errosAnd can you share the debug logs forforbidden erros?https://abp.io/support/questions/8622/How-to-enable-Debug-logs-for-troubleshoot-problems
Thanks.
Hi We have added the code in both web and one of the service still getting the autorization error, I have emails the log files to ur email id